

Earth Estries is an advanced persistent threat (APT) group that the post links to China. It conducts cyber-espionage against government institutions, critical infrastructure and research organizations. The post describes it as active through 2025, getting in through unpatched internet-facing servers and spear-phishing emails. Its aim is to gather political, military and research intelligence. The post rates it as a high risk.
Introduction
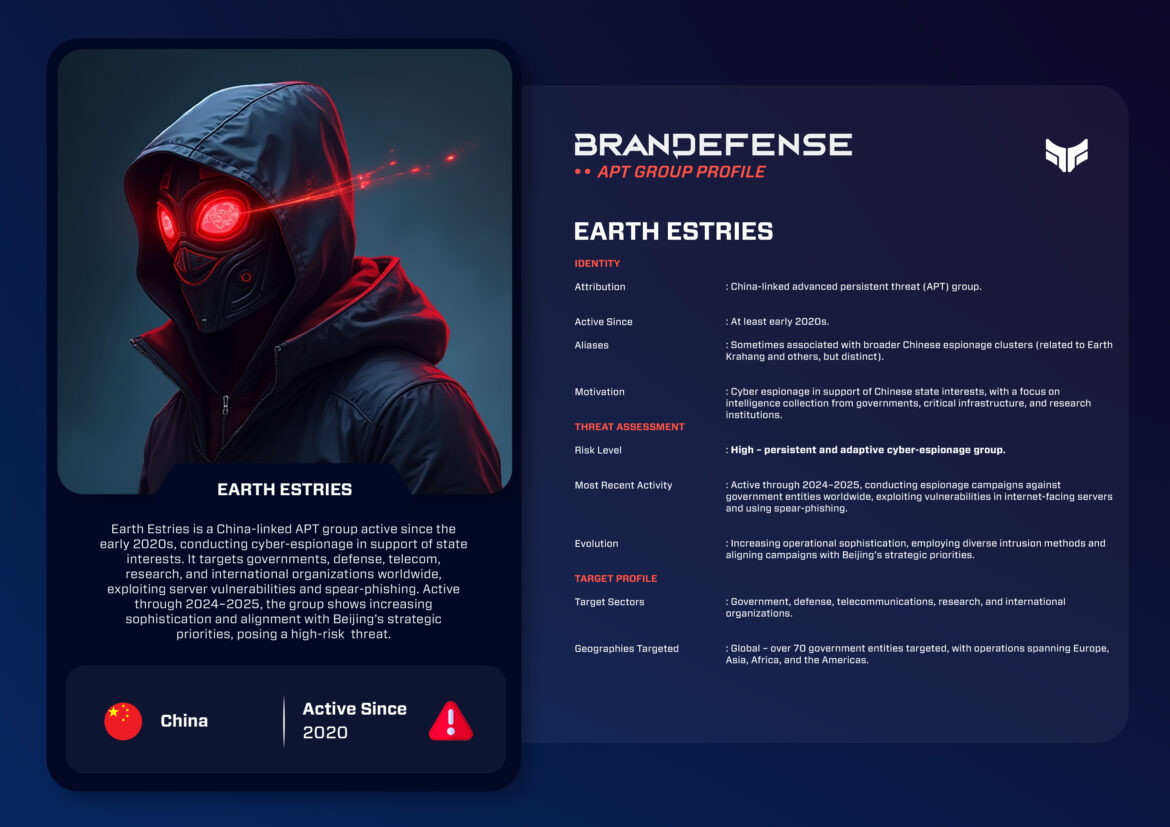
Earth Estries is a China-linked advanced persistent threat (APT) group that has recently reemerged on the international stage as a significant espionage actor in the 2020s. The group is best known for its global campaigns targeting government institutions, critical infrastructure, and research organizations, however by 2025 Earth Estries is becoming more relevant to international cybersecurity beyond just a threat level. The operational pattern of Earth Estries as an adversary aligns with Beijing’s geopolitical interest – and it is representative of more general state-sponsored cyber-espionage of China.
Who Is Earth Estries and What Motivates It?
Earth Estries has been attributed to Chinese state-aligned cyber-espionage activity, and the group’s motivation is attributed to gathering intelligence based on sensitive political, military, and research related information.
There are also indications that Earth Estries targets Western governments and institutions as part of the overall strategy of China to increase its geopolitical influence, maintain net technological advantages, and keep track of the policy and defense planning of its adversaries.
Aliases: While distinct, Earth Estries has been associated with overlapping toolsets and campaigns of other China-nexus groups such as Earth Krahang. A separate China-aligned group, PlushDaemon, is described by ESET as compromising network devices to hijack software updates.
- Type.
- China-linked advanced persistent threat (APT) group.
- Motive.
- Gathering political, military and research intelligence.
- Targets.
- Government institutions, critical infrastructure and research organizations.
- Related groups.
- Overlapping toolsets and campaigns with Earth Krahang.
- Activity.
- Active through 2025.
- Risk.
- Rated high risk.
TTPs (Tactics, Techniques & Procedures)
Earth Estries utilizes both advanced and opportunistic techniques to get into and hold out in their target’s networks.
- Initial accessUnpatched exposed servers or spear-phishing emails
- PersistenceWeb shells, scheduled tasks and compromised VPN credentials
- SpreadCredential dumping and lateral movement
- Command and controlHTTP/S channels and DNS tunneling to avoid detection
- ExfiltrationCovert data exfiltration channels
- Initial Access: Earth Estries leverages unpatched publicly exposed vulnerabilities in networked servers and sends spear-phishing emails with malicious attachments or links.
- Persistence: Persistence is varied but can primarily be achieved through web shells, scheduled tasks, and compromised VPN credentials.
- C2 (Command & Control): C2 is accomplished using custom attackers’ malware families that use HTTP/S-based channel and DNS tunneling to avoid detection.
- Malware & Tools: Deploys custom implants, loaders, and web shells designed for data collection and long-term espionage.
- Techniques: Living-off-the-land tactics, credential dumping, lateral movement, and covert data exfiltration channels.
Notable Operations
- 2021–2022: Initial spear-phishing campaigns against Asian government institutions.
- 2023: Extended reach to European and African targets, specifically telecom and government institutions.
- 2024: Coordinated espionage operations and campaigns against 70+ government entities across the globe, including ministries, embassies, and international organizations.
- 2025: Active campaigns exploiting server vulnerabilities and phishing campaigns targeting critical infrastructure and research institutions.
Recent Developments
As of 2025, Earth Estries appears to have maintained a level of sophistication in their campaigns. Revelations from security reports show the group continuing to leverage internet-facing vulnerabilities while incorporating obfuscation and better security practice around their operations. Moreover, the targeting has expanded from governments alone to include research institutions, NGOs, and other international organizations.
The broad global targeting suggests Earth Estries is a useful operator for Beijing to use as a strategic tool to collect intelligence surrounding not only government organizations in various regions, but also to minimize the technology gap and grow influence and power over their global competitors.
Conclusion
Earth Estries is characterized by high risk, state-sponsored espionage operational with global aspirations. While they may not always be the most technically advanced, their persistence, adaptability and socio-political alignment with Chinese geopolitical priorities position them as a serious threat.
How Can Organizations Defend Against Earth Estries?
- Act quickly to patch any internet facing applications to prevent exploitation.
- Enhance phishing awareness and training programs.
- Look for anomalous scheduled tasks, web shells and unauthorized VPN activity.
- Monitor for DNS tunneling and anomalous outbound traffic for early signs of C2 activity.
With Earth Estries’s continued operational expansion, defenders need to remain on high-alert. The group’s campaigns continue to demonstrate that Chinese cyber-espionage is persistent and adaptive, and in 2025 is growing a footprint across continents.
You can download and review the sheet for all the details!
