OldGremlin is a Russian-speaking, financially motivated criminal group, tracked since at least 2020, that mixes ransomware with slow, APT-style intrusions. It sends targeted phishing emails, spends weeks or months inside a network, steals data and then demands payment, a tactic known as double extortion. This post covers who OldGremlin is, how it attacks and what defenders can do.
Introduction
OldGremlin is one of the less well-known but more dangerous Russian-speaking criminal organizations to emerge in the last few years. The criminal organization’s activity has been tracked back to at least 2020. It has achieved a high level of operational discipline. In some quarters it is known for the long dwell time of its malware on compromised networks and systems. It is also known for a “strategic approach” to infiltrating corporate environments. OldGremlin’s attack methodology differs from most other ransomware groups. It is a low-volume, very high-impact group. It typically takes months to carry out its operational plans.
OldGremlin combines traditional advanced persistent threat (APT) tactics (reconnaissance stage, credential collection, lateral movement) with a refined method of extorting ransom payments. It uses these after infiltrating and gaining unauthorized access to corporate networks. This makes it a hybrid organization, straddling the line between large-scale cybercriminal operations and APTs (Advanced Persistent Threat).
While their motives are primarily financial, the level of sophistication and planning of OldGremlin’s operational plans place them on par with nation-state units. The maturity of OldGremlin’s operations continued to grow through 2024-2025. This shows in the detailed method it uses to create its phishing emails and in the effort it has put into its customized toolsets.
Who is OldGremlin and what motivates the group?
OldGremlin has a reputation as an organized cybercriminal group operating out of Russia. It uses complex operating methods and its own custom-built malware families.
OldGremlin is also indicative of the move towards APT-like practices by Russian eCrime syndicine.
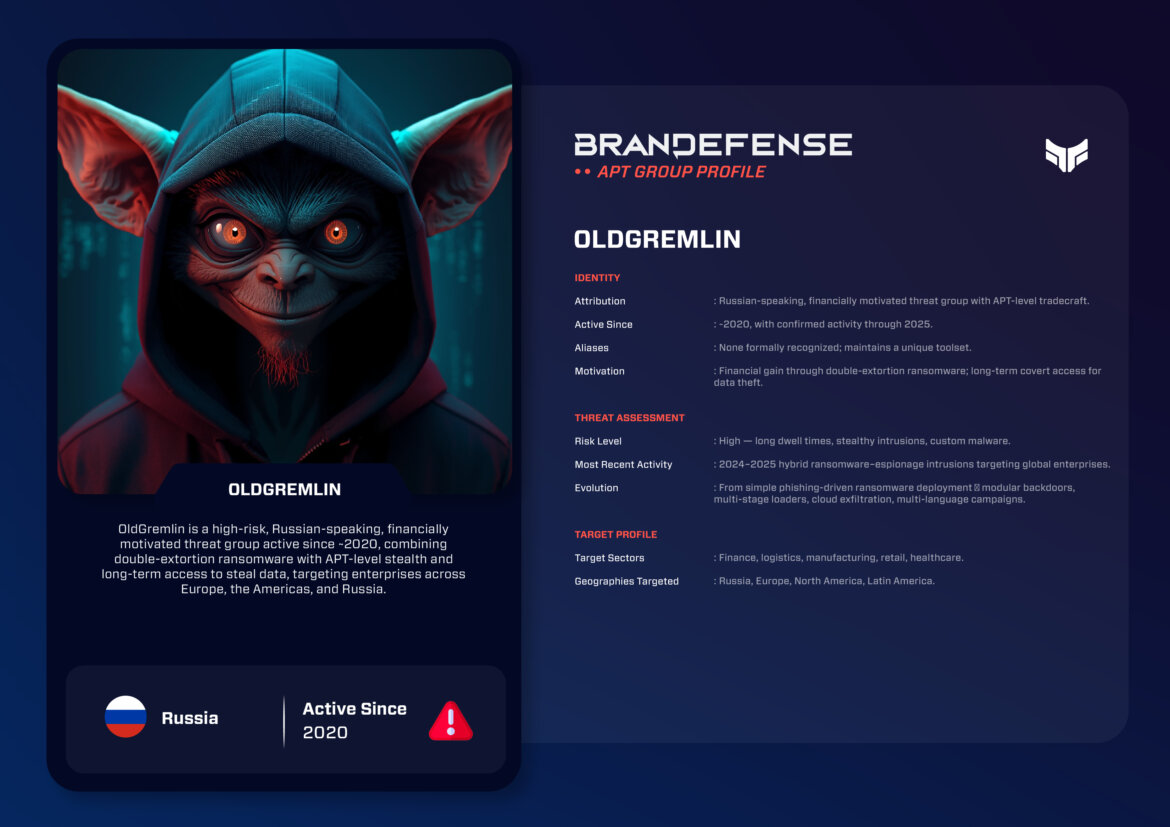
Attribution: Russian-speaking attributes, financially motivated, no confirmed links to government; however, practices similar in nature to nation-states.
Active Since: The first campaigns attributed to OldGremlin were identified in early 2020, and have continued through 2025.
Aliases: There are no aliases associated with OldGremlin; however, OldGremlin uses distinct signatures in their various campaign activities.
Motivation: The most significant motivation for OldGremlin is to obtain financial rewards through double-extortion ransomware.
Additionally, OldGremlin seeks to steal confidential information, maintain access to valuable long-term networks, and to sell such access to their on-going affiliate network.
OldGremlin’s operations rely on deep reconnaissance of potential victims before the encryption is activated. This lets the group use extortion for maximum damage.
- Attribution
- Russian-speaking, financially motivated, no confirmed links to government
- Active since
- Early 2020, continuing through 2025
- Aliases
- None associated with the group, per the post
- Motivation
- Financial gain through double-extortion ransomware
- Approach
- Low volume, high impact, deep reconnaissance before encryption
What tactics does OldGremlin use? (TTPs)
The different ways OldGremlin uses to hack are a lot more sophisticated than normal ransomware groups.
Initial Access
- Spear‑phishing emails in Russian, Spanish, or English that are targeted at specific people.t.
- Fake financial institutions and vendors in the supply chain, including local news media.
- Documents that contain malicious code that can be executed through the use of macros or trojanized attachments.
- Theft of VPN and Remote Desktop Protocol (RDP) credentials are also occasionally used to bypass perimeter defense measures.
Execution
- Installation of OldGremlin’s custom backdoor applications, called TinyNode, TinyShell, and custom implants, on compromised computers.
- The use of custom-built PowerShell frameworks to assist with automated reconnaissance on compromised environments.
- The payment of the ransom only occurs after the OldGremlin hackers have mapped out the entire targeted eCommerce business for several weeks.
Persistence
- Establishment of multiple redundant footholds using:
- Scheduled tasks
Registry run keys
Web shells
- Compromised VPN sessions
- Scheduled tasks
Command & Control (C2)
- Encrypted communications tunneled through:
- Cloud providers
Compromised corporate hosts
- Proxy networks
- Cloud providers
OldGremlin’s callback behavior is low volume and is intentionally intermittent.
Lateral Movement
- Abuse of legitimate administrative tools (LOLbins).
- Internal RDP pivoting.
- Credential harvesting with Mimikatz and custom tooling.
- Discovery of backup servers and domain controllers for maximum impact.
Data Exfiltration & Ransomware Deployment
- Selective exfiltration of high‑value business data.
- Deployment of tailored ransomware variants compiled per target.
- Double extortion: encryption + leak site publication threats.
- Initial accessTargeted spear-phishing emails, fake vendors, macro documentsTechnique T1566 (MITRE ATT&CK, opens in a new tab)
- ExecutionCustom backdoors and PowerShell frameworks for reconnaissance
- PersistenceScheduled tasks, registry run keys, web shells, VPN sessions
- Lateral movementAdmin tool abuse, RDP pivoting, Mimikatz, backup server discovery
- Exfiltration and ransomSelective data theft, tailored ransomware, leak site threats
What are OldGremlin’s notable operations (2020–2025)?
OldGremlin’s documented attacks are distinct in their low volume, targeted approach, and the tendency for long-term infiltration:
2020 – The first wave of attacks targeting medical and logistics companies in Russia
Phishing emails impersonating covid-19 alerts as delivery of malicious TinyNode backdoor with ransom amounts reaching hundreds of thousands of dollars.
2021 – A series of attacks against the manufacturing and retail sectors in Europe
Implementing new tools to preserve remote connection, for a multi-week distance prior to commencing encryption. Expanding into Spain, Poland and Germany.
2022–2023 – Shift to global targets
Targets expanded to North American businesses with expanding multi-language phishing kit capabilities; coordination between intruders and cash-out professionals.
2024 – Increasing adoption of supply‑chain impersonation
- More use of supply-chain impersonation, with fake invoices and shipping notices as deception techniques.
- More overlap with business email compromise tactics.
- Deeper reconnaissance phases that identify internal backup systems.
2025 – Continued hybrid APT–ransomware model
- A new build of the ransomware.
- More elaborate exfiltration methods that use a cloud storage proxy.
- Longer operational cycles that allow total domain ownership.
What has changed for OldGremlin in 2024 and 2025?
In 2024 and 2025 OldGremlin added to its capabilities by using:
- Multi-stage loader chains – these chains help reduce the chances of detection.
- Modular implants – these implants allow reconnaissance to be done via plugin(s).
- Cross-platform components – these components include Linux targeting scripts designed for backup servers.
- Encrypted SMB tunnels – these tunnels allow lateral movement within a network without detection.
In addition to the above capabilities, OldGremlin’s shift to human-operated ransomware has changed how they operate. The operators are now engaging in manual escalation of privileges and mapping systems. This hands-on approach lets them change tactics on the fly. They can get around any new defenses put in place during the attack.
The posts on OldGremlin’s leak site indicate more extortion and more psychological pressure on victims. This includes efforts to contact the victims’ partners, executives, and customers.
What is the strategic impact of OldGremlin?
The unique blend of APT-level stealth with monetization of cybercrime by OldGremlin creates a threat environment that is difficult for current security programs to manage. Key points of concern are:
- Serious consequences from the breaches, and long recovery times as they can fully compromise the victim’s domain;
- Because OldGremlin victimizes organizations across all sectors (finance, logistics, and manufacturing), the attacks have the potential to create a cross-sector risk.
- Increased operational costs incurred by defenders due to OldGremlin’s long dwell time (the time spent within a network undetected) requiring extensive forensic and remediation work
- Risk of data leakage due to selective exfiltration of only those items that create the greatest pressure on victims to pay.
OldGremlin’s method of operation resembles that of nation-state actors. This raises concerns that it may serve as a model for other cybercrime groups building their own long-term intrusion capabilities.
Conclusion
OldGremlin signifies the progressive development of financially motivated, APT-style groups. Rather than focusing purely on numbers, OldGremlin has focused on quality, being methodical, diligent and thorough in its approach to APT activity. As we approach the end of 2025, it is highly likely that tradecraft will keep growing more sophisticated. We expect loaders that are harder to identify, cloud-based data theft methods, and an even broader range of target geographies.
To limit the impact of OldGremlin, we recommend that organizations do four things. Increase monitoring of lateral movement. Reinforce behavioral analytics. Run ongoing training on phishing resistance. Limit permissions to access and use privileged accounts. OldGremlin keeps growing in sophistication. It also shows a possible future in which cybercriminals and ransomware gangs use the methods of intelligence services. This would make adversaries harder to identify, anticipate and stop.
You can download and review the sheet for all the details!