

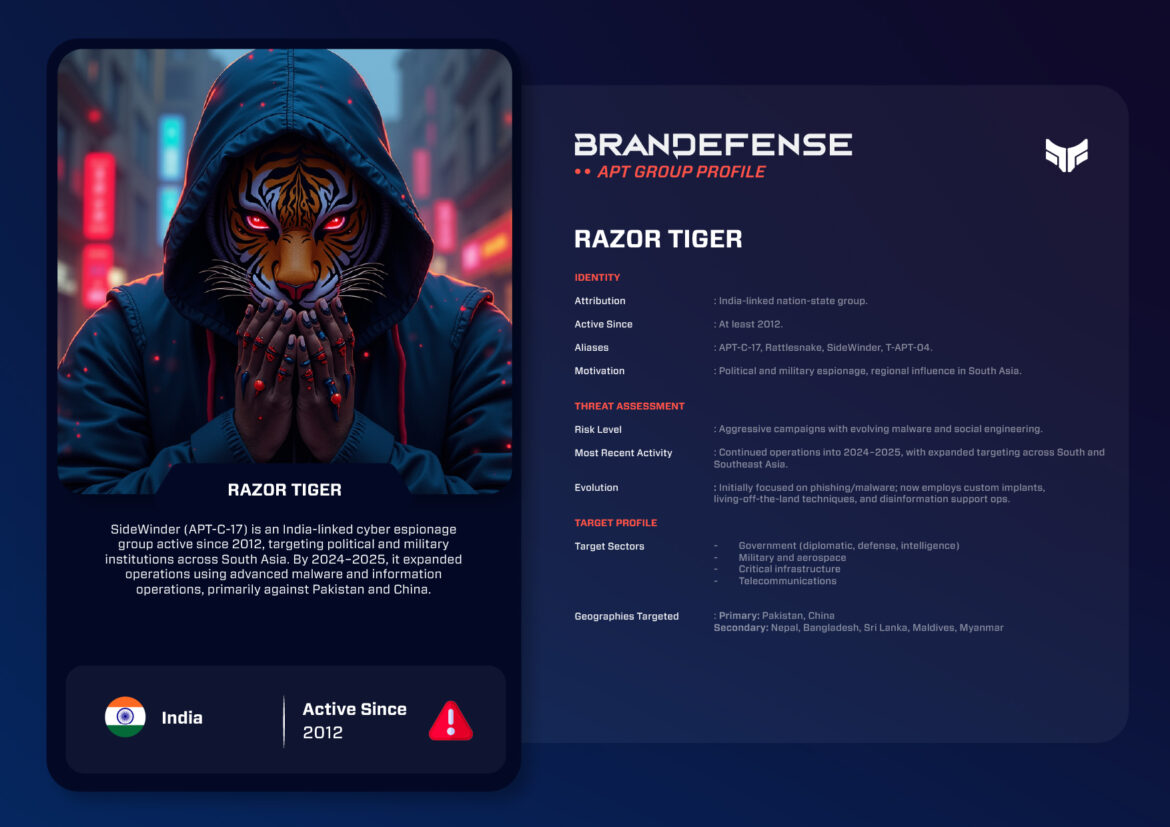
RAZOR TIGER, also known as SideWinder, is a cyber espionage group active since at least 2012. It is attributed by MITRE ATT&CK to a suspected Indian threat actor group. It targets government, military and business organizations in Asia, mainly Pakistan, China, Nepal and Afghanistan, and uses spear-phishing, DLL side-loading and registry persistence.
What is RAZOR TIGER?
RAZOR TIGER, also known as SideWinder (APT-C-17, Rattlesnake, T-APT-04), is an advanced persistent threat (APT) actor that has operated for many years since at least 2012. Public and industry reporting has typically assessed the actor as being connected to Indian state interests focused on cyber-espionage activity, specifically targets in South Asia and surrounding areas. The RAZOR TIGER actor has changed its tradecraft, expanded into new sectors like maritime and logistics, and updated its malware arsenal to evade defenders.
Who is RAZOR TIGER and what does it want?
- Aliases: SideWinder, APT-C-17, Rattlesnake, T-APT-04
- Attribution: India-connected nation state group (medium confidence)
- Active Since: ~2012
- Motivation: Political and military espionage, regional influence, and strategic intelligence collection
The group’s consistent focus on Pakistan, China, Nepal, Bangladesh, Sri Lanka, and other South Asian countries is consistent with geopolitical rivalries and regional security issues. The group’s motivation is squarely focused on gathering intelligence to effectively meet national defense and foreign policy objectives.
- Product.
- Microsoft Office 2007 SP3, 2010 SP2, 2013 SP1 and 2016.
- Published in NVD.
- November 15, 2017.
- CVSS v3.1 score.
- 7.8 (High).
- Effect.
- Lets an attacker run arbitrary code as the current user.
- Linked to the group.
- MITRE ATT&CK lists it among the flaws Sidewinder has used.
What tactics and techniques does RAZOR TIGER use? (TTPs)
RAZOR TIGER’s ability to shift and modify TTPs seems to be consistent with worldwide APT TTPs detailed in the 2024-2025 intel reports. To highlight some elements:
- Initial Access:
- Leverage of spear-phishing with malicious Office, RFT documents.
- Organization-branded decoys themed around government, military, or diplomatic issues.
- Exploitation of legacy vulnerabilities (CVE-2017-11882, etc.) and default login credentials.
- Persistence and Execution:
- Use of PowerShell-based loaders and malicious scripts.
- Side-loading of DLLs to avoid detection.
- Use of scheduled tasks and modifications to the registry to maintain long-term access and persistence.
- Command and Control (C2):
- Based on HTTPS beaconing through compromised infrastructure.
- Cloud services serve as a double-edged premise for domain fronting and data exfiltration.
- Malware and Tools:
- Custom espionage implants (one of which is a recent variant called “StealerBot”).
- Living-of-the-land binaries (LOLBins) such as WMI and CertUtil.
- Only used commodity penetration tools in tandem with various bespoke malware.
Notable Operations (Timeline)
2012–2016: Early phishing and credential theft operations, targeting South Asian government and defense organizations.
2017–2019: Expanded targeting of telecommunication networks, military networks, with a stronger emphasis on persistence (DLL side-loading techniques).
2020–2022: Utilization of cloud-hosted lures and expose enterprise services.
2023–2025: Extended targeting into maritime, logistical, and nuclear supporting areas; employed new implants with less detectable exfiltration channels.
Recent Trends (2024–2025)
Crime and threat intelligence from the past two years reflect how RAZOR TIGER has kept up with the changing global threat landscape:
Use of living-off-the-land techniques to limit reliance on signature-based detection of malware.
Use of a cloud resource for C2 to become much more commonplace, similar to how APT groups are increasingly adopting commercial platforms.
Increasing targeting of critical infrastructure, especially maritime and logistics, to support regional priorities.
Strategic Implications & Defensive Considerations
RAZOR TIGER continues to be one of the most active South Asian espionage actors, incorporating outdated exploit techniques with ongoing evolution of those tactics. Its continued activity raises several strategic concerns for governments, corporate and critical infrastructure:
- Regional Security: With its South Asian focus, RAZOR TIGER threatens the stability of already fragile diplomatic relations and the resilience of critical infrastructure.
- The focus on espionage rather than disruption: Unlike ransomware groups, RAZOR TIGER is focused on long-term access and stealthy intelligence collection, which increases the difficulty of detection.
- Adjusting to the global threat environment: RAZOR TIGER’s shift to cloud abuse and increased use of living-off-the-land techniques mirrors behavior, making distinctions between state actors and cybercriminal ecosystems less defined.
Defensive Recommendations:
- Strengthen email defenses; sandbox any potentially problematic attachments.
- Update your legacy Office exploits to address CVE-2017-11882, etc.
- Look for PowerShell execution, DLL side-loading, or unusual bahaviour from HTTPS beacon calls.
- Limit cloud service use to known-good domains and hyper- restrict access.
- Segment networks – particularly for defense, telecom, and maritime organizations.
Conclusion
RAZOR TIGER showcases the resilience and flexibility of a state-aligned APT. After more than a decade of transitioning from botched phishing attacks to sophisticated cloud-based espionage attacks, the resiliency of South Asian cyber-espionage eco-systems is demonstrated. For the defenders, at least the takeaway is clear; organizations must remain vigilant for the long-haul, untether themselves from the notion of layered defense, and share intelligence as quickly as this ecosystem of groups.
You can download and review the sheet for all the details!
