

SilverFox is a threat actor that, according to this post, mixes espionage with financially motivated attacks such as ransomware and data extortion. The post says it targeted government, telecom, finance and technology organizations in 2024 and 2025. Reported methods include exploiting Cleo file transfer software, phishing, the PlugX remote access tool, and stealing data before any encryption.
Introduction
SilverFox has quickly emerged in 2024 and 2025 as a competent and adaptable threat actor operating on the nexus of espionage and financially motivated operations. Its ability to take an opportunistic targeting approach while employing advanced intrusion techniques positions the group among threat actors that defenders cannot afford to ignore. Recent intelligence confirms SilverFox has moved away from opportunistic targeting with smaller breaches and instead focused on prolonged operations against organizations that represent enhanced operational value in the government, finance, and technology sectors.
Who Is SilverFox and What Motivates It?
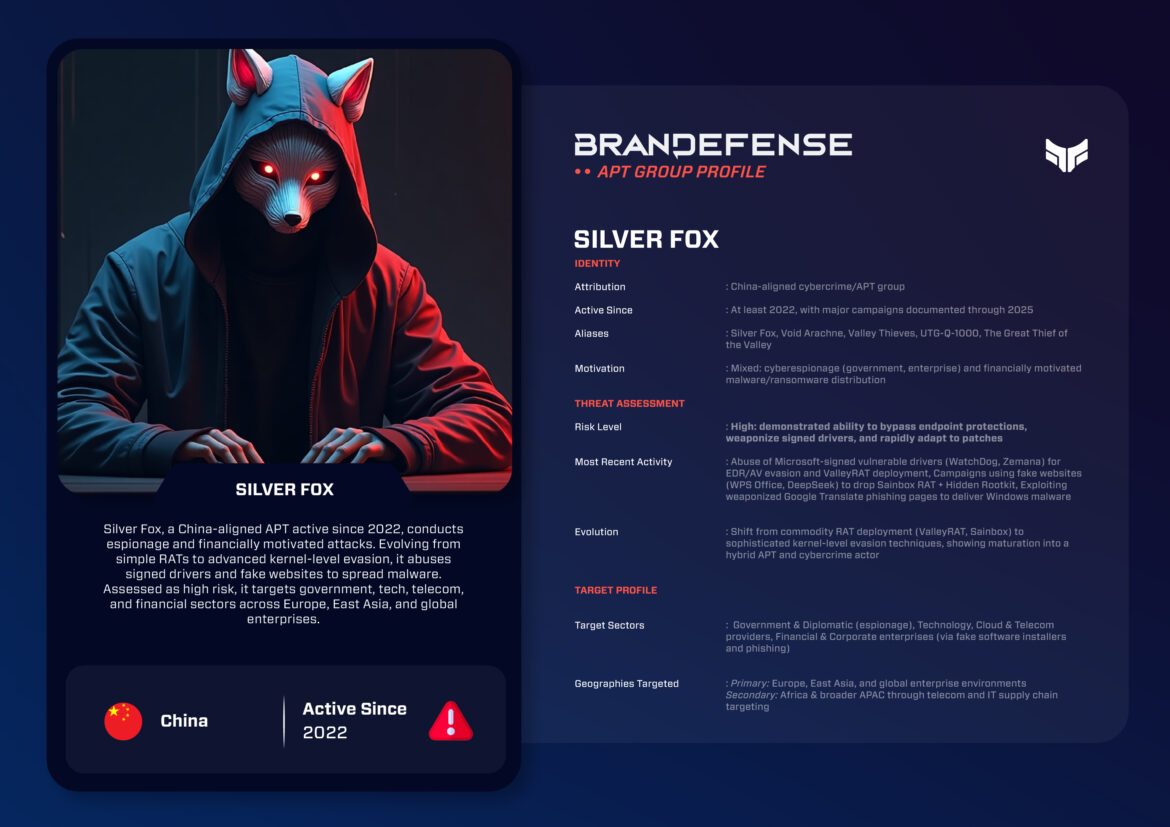
Attribution: SilverFox is assessed with moderate confidence to be state-aligned and there have been indications of a degree of coordination across Eastern Europe and Central Asia.
Active Since: There was public reporting on activity from as early as 2022, but there are indications the group has significantly increased its operational tempo since late 2023.
Aliases: While confirmed overlaps with other units are limited, their activity does sometimes overlap with the infrastructure established by Qilin affiliates.
Motivation: SilverFox uses a combination of strategic espionage targeting of government and telecommunications organizations, along with financially motivated operations such as ransomware and data extortion.
- Attribution.
- Assessed with moderate confidence to be state-aligned.
- Active since.
- Public reporting from as early as 2022, with a higher tempo since late 2023.
- Motivation.
- Espionage against government and telecom, plus ransomware and data extortion.
- Tools named.
- PlugX variants, credential stealers and custom loaders.
What Tactics, Techniques and Procedures Does SilverFox Use?
SilverFox utilized a hybrid operational style:
- Initial Access – SilverFox is reported to have exploited file transfer devices such as Cleo (this attribution comes from the source report and is not confirmed by CISA), and engaged in phishing campaigns that required an element of AI-generated lures.
- Persistence – SilverFox operated with Living-Off-The-Land tools, PowerShell, Windows Hello abuse, scheduled tasks, and cloud credential compromise.
- C2 and Infrastructure – SilverFox was observed primarily relying on TOR nodes and proxy botnets as its anonymization but occasionally used commercial VPNs as a backup.
- Malware and Tools – SilverFox was observed using PlugX variants, credential stealers, and custom loaders that were misrepresented as business software updates to retain access to their infrastructure.
Techniques:
Supply chain targeting of European software vendors.
Lateral movement through hybridized cloud and on-prem networks.
Data exfiltration occurred prior to encryption with ransomware only used selectively.
Notable Operations
- 2024 – Telecom Intrusions in Europe: SilverFox targeted telecom operators and conducted espionage based on a zero-day exploit of a VPN appliance.
- 2024 – Finance and Insurance in the Asia-Pacific: SilverFox breached a regional banking network and proceeded to exfiltrate sensitive data before ultimately monetizing it on the dark web.
- Q1 / 2025 – Supply Chain Campaign: reportedly targeted Cleo file transfer software vulnerabilities, using the same exploits as Clop, with customized data-theft techniques. This attribution is not confirmed by CISA.
- Q2 / 2025 – Government Entities in the MENA region: Operated in conjunction with credential harvesting campaigns against ministries in the Middle East region, in connection with the ongoing geopolitical situation.
The Cleo flaw CVE-2024-50623 has its own page.
- 2024Telecom intrusions in EuropeEspionage based on a zero-day exploit of a VPN appliance.
- 2024Finance and insurance in Asia-PacificA regional banking network was breached and data taken before being monetized on the dark web.
- Q1 2025Supply chain campaignCleo file transfer software flaws, reportedly using the same exploits as Clop (attribution not confirmed by CISA).
- Q2 2025Government entities in the MENA regionCredential harvesting against ministries in the Middle East.
Current Updates
SilverFox has demonstrated rapid evolution:
- Movement to cloud environments: Increased attention to SaaS compromises, and lateral movements in hybrid networks.
- Artificial intelligence adoption: Use of generative AI for phishing lures, voice cloning for vishing, and disinformation as part of larger influence campaigns.
- Operational partnerships: Possible links to Ransomware-as-a-Service partners like Qilin and RansomHub.
Conclusion
SilverFox is a powerful example of the merger of espionage and financial cybercrime in 2025. The dual-motives, targeting the supply chain, and rapid advances on use of AI as disruptive assets make them an unpredictable and dangerously active actor.
Defensive Takeaways:
- Prioritize patching edge devices, and file transfer systems
- Strengthen cloud identity management with MFA and conditional access
- Be mindful of phishing and vishing attempts that are intrusive by AI
- Heighten focus on supply chains risk management with vendors
SilverFox is continuing to emerge on the global threat landscape requiring co-ordinated international monitoring and cyber defense planning.
You can download and review the sheet for all the details!
