Wizard Spider is a Russia-based, financially motivated threat group. MITRE ATT&CK says it was first known for developing and distributing TrickBot malware since at least 2016. The group has run ransomware operations with Ryuk and Conti against major corporations and healthcare facilities. It is also tracked as FIN12, GOLD BLACKBURN and DEV-0193.
Introduction
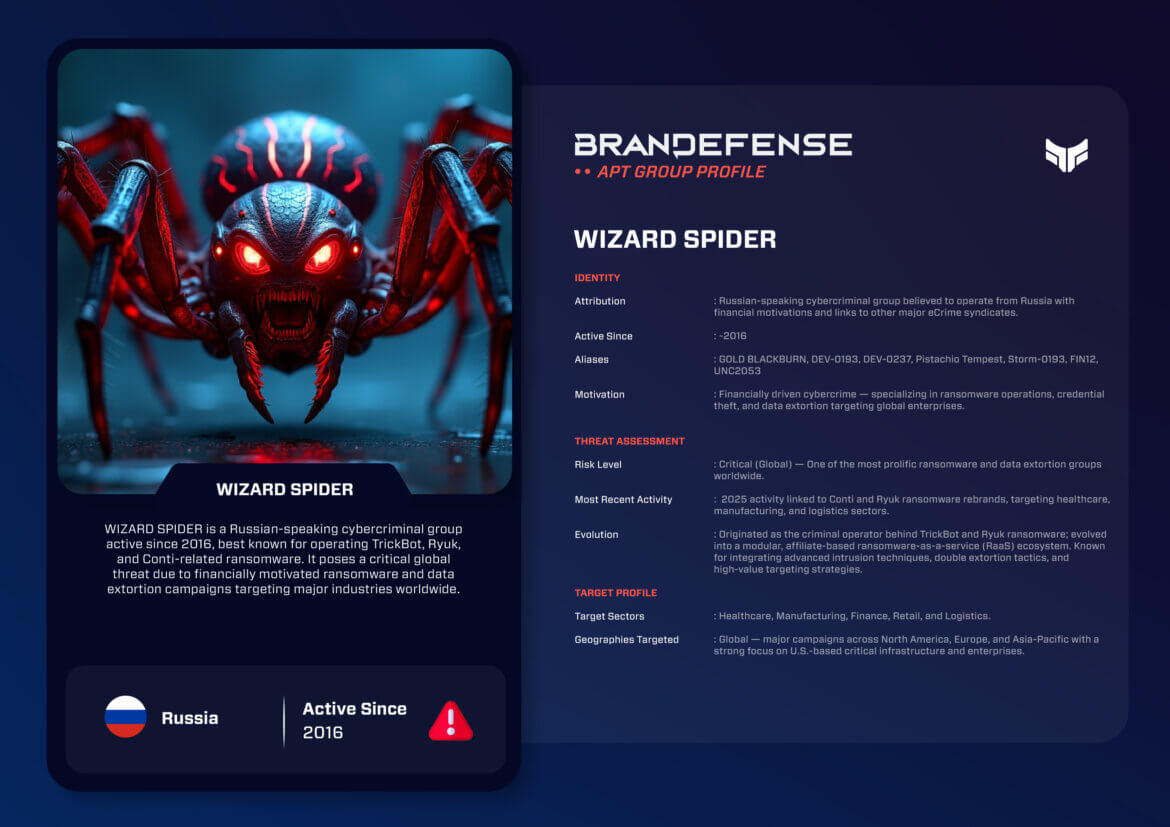
WIZARD SPIDER is one of the most active cybercriminal groups operating to date. It is also known by aliases including FIN12, GOLD BLACKBURN and DEV-0193. The group has been active since at least 2016.
It has become synonymous with large-scale ransomware attacks, credential theft and the industrialization of cyber extortion, among other criminal activity. WIZARD SPIDER grew out of TrickBot and Ryuk ransomware operations into a complex affiliate-based cybercrime network in the eCrime ecosystem. It added uneven layers linked to organized crime and possibly state tolerated cyber activity. It operates mainly from Russia and nearby CIS countries.
WIZARD SPIDER’s hallmark is its ability to adapt fast to law enforcement pressure. It changes its toolsets, infrastructure, and business plan. The group rolled out TrickBot as a banking Trojan. It later moved on to deploy Ryuk, Conti and now Black Basta ransomware.
In doing so, WIZARD SPIDER paved the way for modern ransomware as a service (RaaS). WIZARD SPIDER continues to pose serious financial and operational damage to companies across the global critical infrastructure.
- Also tracked as.
- FIN12, GOLD BLACKBURN, DEV-0193.
- Base.
- Russia and adjacent CIS countries.
- Motivation.
- Financial gain through ransomware and data leaks.
- Active since.
- At least 2016.
- Known tools.
- TrickBot, BazarLoader, Cobalt Strike, Ryuk, Conti, Black Basta.
Who Is Wizard Spider and What Motivates It?
The core motive of WIZARD SPIDER is money. Unlike most nation-state threat actors, it does not directly pursue espionage or geopolitical goals. Instead, it works in a permissive setting of Russian cybercriminal safe havens. There, prosecutions for attacks on foreign targets are rare at best.
Key motivations are:
1. Financial Gain: It focuses mainly on extorting its victims for financial gain through ransomware and data leaks.
2. Monetization of Access: It sells network access to affiliate actors and partners with other Ransomware as a Service (RaaS) groups to expand access.
3. Ecosystem Dominance: It establishes long-term, collaborative relationships with developers of loaders and infostealers, while also establishing initial access with other affiliates.
Profit is the ultimate principle this group operates under. Its structure and resilience suggest an organized, business-like hierarchy. This is on the same spectrum as multinational criminal enterprises.
Tactics, Techniques, and Procedures (TTPs)
WIZARD SPIDER has set up a solid, repeatable operating model. It uses a full attack chain, from exploitation to ransom negotiation. This lets it use several specialized subgroups and affiliates.
1. Initial Access
WIZARD SPIDER obtains initial access through phishing, malvertising, and exploiting services exposed on the Internet such as VPNs and RDP. It also works with infostealer malware operators like IcedID and QakBot to steal compromised credentials. In some cases, the victim is infected through TrickBot or BazarLoader. These establish persistence before a ransomware payload is deployed.
2. Persistence and Privilege Escalation
After compromising the victim, WIZARD SPIDER uses PowerShell, Cobalt Strike, and PsExec for lateral movement. Persistence capabilities are set up by creating domain accounts, changing registry entries, and creating scheduled tasks. WIZARD SPIDER is highly adaptable. It uses legitimate tools such as AnyDesk or Atera to gain and keep covert remote control over the victim’s environment.
3. Command and Control (C2)
The group uses encrypted HTTPS and TOR hidden services in C2 communications, layered behind a proxy. Infrastructure reuse is typical. However, domains and IPs are changed often to evade detection. In 2022, WIZARD SPIDER moved many of its operational capabilities to decentralized RaaS hosting and encrypted coordination via Telegram.
4. Malware and Toolset
WIZARD SPIDER deploys:
- TrickBot: Originally developed as a banking Trojan, its purpose changed to a modular loader.
- BazarLoader / BazarBackdoor: A loader and backdoor used to stealthily deploy Cobalt Strike and ransomware.
- Cobalt Strike: Used for reconnaissance and lateral movement. It is a key tool of WIZARD SPIDER.
- All versions of Ryuk, Conti, and Black Basta Ransomware: Successive generations of ransomware families that WIZARD SPIDER managed or influenced.
- AnchorDNS / AnchorMail: More advanced C2 frameworks used for persistence and stealthy operation.
The group continuously improves its toolset, setting up obfuscation, signed binaries, and living-off-the-land tactics to cut endpoint detection.
5. Data Exfiltration and Extortion
Before encrypting data, WIZARD SPIDER routinely exfiltrates sensitive data via Rclone, Mega, or scripts written for FTP for data transfer. After exfiltrating data, the group threatens to expose it on publicly accessible leak sites. One example is the Conti News blog.
Later examples are the recently rebranded portals of the Black Basta and Quantum operations. This “double extortion” method of operation, encrypting the victims’ data and threatening public exposure of said data to get the most from ransom payments.
- Initial accessPhishing, malvertising, exposed VPN and RDP services, or TrickBot and BazarLoader
- Lateral movementPowerShell, Cobalt Strike and PsExec
- PersistenceDomain accounts, registry entries, scheduled tasks, AnyDesk or Atera
- ExfiltrationData taken via Rclone, Mega or FTP scripts before encryption
- Double extortionData encrypted, then exposure threatened on leak sites

Notable Operations
Over the last decade, WIZARD SPIDER has been responsible for many ransomware attacks and has been involved in infrastructure disruptions. All of this has displayed impressive resiliency.
- 2018Ryuk campaignsLarge scale Ryuk attacks on U.S. hospitals and city governments.
- 2020Conti RaaS modelConti released under a RaaS agreement to recruit affiliates.
- 2021TrickBot and Emotet collaborationInfrastructure used to deploy Emotet and IcedID loaders.
- 2022Resilience after takedownMoved to BazarLoader and AnchorMail without disruption to operations.
- 2023Black Basta emergesAffiliates migrated to Black Basta after Conti shut down.
- 2025Healthcare and manufacturing attacksPhishing, supply chain vulnerabilities and misconfigured cloud services.
- 2018– Ryuk Campaigns: The group began large scale Ryuk ransomware attacks targeting U.S. hospitals and city governments. Ryuk became infamous for demanding multi million dollar ransoms, and ceased to be able to render even emergency services inoperable.
- 2020 – Conti RaaS Model: WIZARD SPIDER released Conti ransomware under a RaaS agreement. This allowed the group to recruit affiliates and increase its ransomware attacks. Conti led to hundreds of attacks in different countries, including the attack from the Irish Health Service Executive (HSE) in 2021.
- 2021– TrickBot and Emotet Collaboration: The group’s infrastructure was leveraged to deploy Emotet and IcedID loaders, bridging cooperation across attacks in the eCrime ecosystem.
- 2022 – Resilience Post-Takedown: One of the only ransomware groups using TrickBot was partially dismantled by law enforcement. WIZARD SPIDER simply redirected towards BazarLoader and AnchorMail, without any disruption to operations.
- 2023 – Emergence of Black Basta: After Conti shut down operations, affiliates of WIZARD SPIDER took a clear interest in moving future actions to Black Basta ransomware. They continued to target very high-value ransoms, as well as leaking data.
- 2025 – Healthcare and Manufacturing Attacks: The latest campaigns use phishing, supply chain vulnerabilities and other exploits of misconfigured cloud services. They target healthcare facilities, logistics companies and pharmaceutical companies.
How Has Wizard Spider Evolved and How Is It Structured?
The WIZARD SPIDER network is not a single cohesive entity. It is a loose consortium of financially motivated operators. This works through a series of specialized channels with modules that include:
- Access Brokers: Responsible for the first compromise through phishing or exploitation.
- Intrusion Operators: Conduct lateral movement, privilege escalation, and data exfiltration.
- Negotiation Units: Manages ransom communications, and other negotiations in chat, usually through anonymized chat portals.
- Developers: Maintain the codebases for ransomware and the backend.
The modular structure allows quick recovery when law enforcement steps in. When the Conti brand was exposed in 2022, the operators quickly repositioned themselves as Black Basta, Royal, and Quantum. They all kept similar playbooks.
WIZARD SPIDER’s collaborations with other cybercriminal groups, including TA505 (Clop), as well as EvilCorp, further extends its reach. These relationships allow for the shared resources, trading access, and overlapping targets of victims.
Strategic Impact and Defense
WIZARD SPIDER’s activity shows the industrialization of ransomware. This group has shown that organized cybercrime can run almost as efficiently as large corporations. It uses affiliates and black markets to grow the scale of its attacks.
Key Impacts:
- Economic Damage: Losses in the billions of dollars across the healthcare, logistics, and energy sectors.
- Operational Disruption: Ransomware encryption temporarily disables network operations and services in hospitals and city infrastructure.
- Cybercrime Ecosystem Expansion: The Ransomware as a Service (RaaS) model used by WIZARD SPIDER proliferated among actors, leading to today’s thriving ransomware ecosystem.
Defensive Recommendations:
- Multi-Layered Authentication: Multi-Factor Authentication (MFA) for VPN, RDP (Remote Desktop Protocol), and email accounts will limit credential-based compromises.
- Behavioral Monitoring: EDR (endpoint detection and response) and XDR (extended detection and response) tools could help detect PowerShell abuse, PsExec usage or anomalous file encryption.
- Network Segmentation: Reduce the privileges of all administrators and isolate critical systems.
- Incident Response Preparedness: Set up offline backups and a tested recovery plan for ransomware.
- Threat Intelligence Sharing: Engage across ISACs (Industry Share Analysis Center) in your sector to track new variants with shared Indicators of Compromise (IOCs).
Conclusion
WIZARD SPIDER continues to be a cornerstone of the global ransomware ecosystem. It has stayed strong through many highs and lows. Its mature structure and its work with other eCrime groups mean it lives on. This is true even after many of its members have been taken down and arrested.
The group keeps a steady presence in ransomware operations and keeps going. It also confuses defenders by rebranding its operations. This has been done from Ryuk to Conti and Black Basta. Even so, WIZARD SPIDER is still the face of ransomware to this day.
As we enter 2025, WIZARD SPIDER is perfectly positioned as a symbol of professionalized cybercrime. It is a shadow industry with hierarchies, specialization and a global reach. Combatting these groups takes more than installing technical defenses. It requires international cooperation, revoking and sanctioning their financial infrastructure, and stopping the economy behind the cybercriminal elements.intent and technical sophistication.
You can download and review the sheet for all the details!