

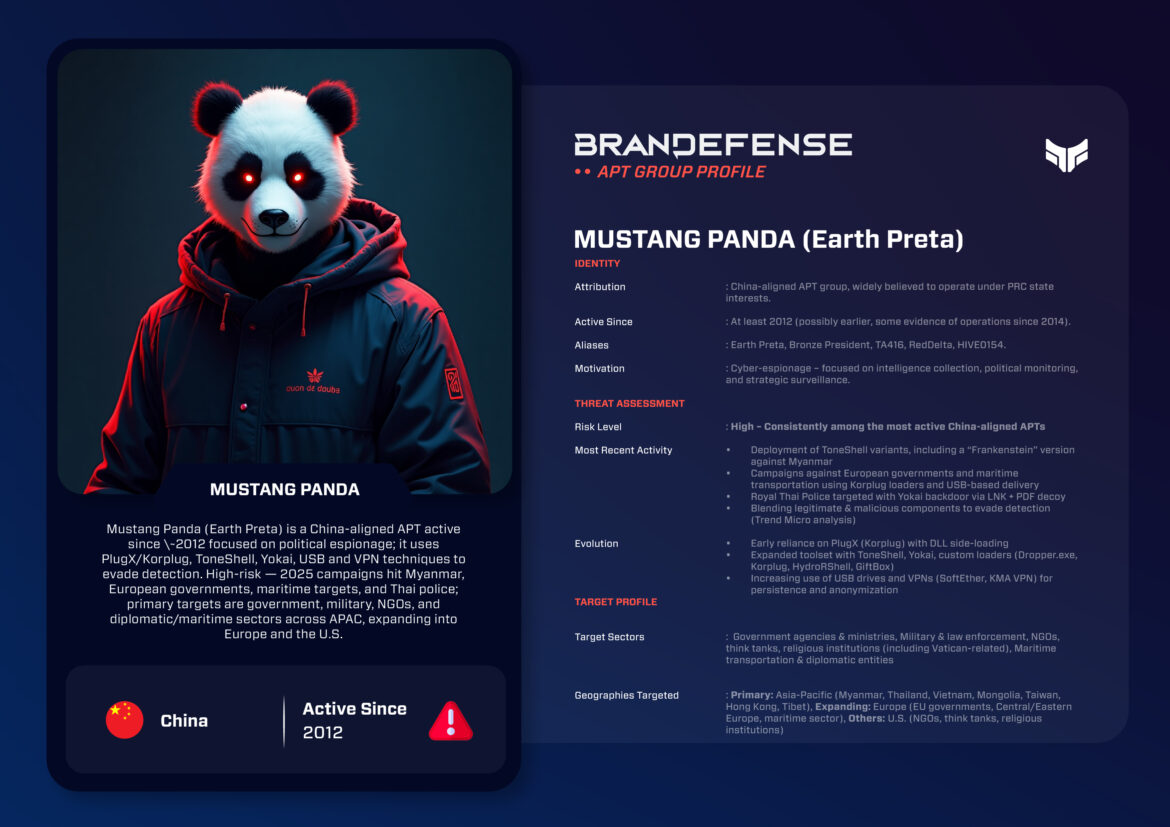
Mustang Panda is a cyber-espionage group that MITRE ATT&CK describes as China-based. It is also known as Earth Preta, Bronze President, TA416, RedDelta and HIVE0154.
It has been active since at least 2012. It targets government, military, law enforcement, NGO and diplomatic organizations in Asia, Europe and beyond. Its tools include spear-phishing, PlugX (Korplug), ToneShell and USB-based malware.
Introduction
Mustang Panda is also known as Earth Preta, Bronze President, TA416, RedDelta and HIVE0154. It is still one of the most active China-aligned APT groups in 2025.
It is a cyber-espionage group. It keeps changing its tools and methods. The goal is to stay inside key target organizations in Asia, Europe and beyond.
Its campaigns show how state-backed spying is changing. China-linked attackers keep their focus on collecting intelligence over the long term.
Identity and Motivation
- Attribution: Widely attributed to the People’s Republic of China (PRC).
- Operational since: At least 2012.
- Other names: Earth Preta, Bronze President, TA416, RedDelta, HIVE0154.
- Motive: Collecting political and military intelligence. Targets are government departments, the military, law enforcement, NGOs and diplomats.
Its goals clearly fit Beijing’s geopolitical and strategic interests. This is most true for three kinds of targets:
- Neighboring states.
- European partners.
- International bodies active in maritime security, policy and law enforcement.
- Attribution.
- Widely attributed to the People’s Republic of China (PRC).
- Operational since.
- At least 2012.
- Other names.
- Earth Preta, Bronze President, TA416, RedDelta, HIVE0154.
- Targets.
- Government, military, law enforcement, NGO and diplomatic organizations in Asia, Europe and beyond.
- Malware.
- Korplug/PlugX, ToneShell, Yokai, SoftEther VPN.
What Are Mustang Panda’s Tactics, Techniques and Procedures (TTPs)?
Mustang Panda keeps changing its methods. At the same time, it keeps some familiar tools and ways of delivery.
- Initial accessSpear-phishing, LNK files with PDF decoys, and USB-based malware
- ExecutionDroppers deploy Korplug/PlugX and newer backdoors like ToneShell
- PersistenceSoftEther VPN for extended access and DLL side-loading for stealthy execution
- C2 and exfiltrationXOR-obfuscated Korplug traffic and persistent C2 channels via VPN tunneling
- Initial Access: Spear-phishing with lures about current events. Harmful archives and shortcut (LNK) files paired with PDF decoys. Use of USB-based malware in Europe appears to be rising.
- Execution: Droppers that deploy known malware such as Korplug/PlugX. Newer custom backdoors such as ToneShell.
- Persistence: SoftEther VPN for long access to the victim’s network. DLL side-loading to run code quietly.
- Defense Evasion: Fake software, such as Google Chrome installers. They mix harmful and legitimate parts to avoid detection.
- C2 & Exfiltration: Korplug traffic hidden with XOR. Lasting C2 channels through VPN tunnels.
- Malware: Korplug/PlugX, ToneShell (including the recent “Frankenstein” variant), Yokai, SoftEther VPN.
Notable Operations
- 2025 (Myanmar): Deployed a “Frankenstein” variant of the ToneShell backdoor.
- 2025 (Thailand): Targeted the Royal Thai Police with a Yokai backdoor. It was delivered through an LNK file with a PDF decoy.
- 2025 (Europe): Kept up operations against European Union governments with maritime transport operations. It used USB-based loaders and Korplug.
- 2024-2025: Campaigns that mix legitimate apps with malware to slip past detection. One example is a legitimate installer used to drop a payload, as recorded by MITRE ATT&CK.
- Historical: Heavy use of PlugX/Korplug with DLL side-loading. Targets were NGOs, religious groups and governments across Asia and Europe.
Timeline of Operations
- 2012-2019: Campaigns built on PlugX against APAC governments and NGOs.
- 2020-2022: Wider targeting of EU diplomatic and religious groups.
- 2023: More USB-based attacks. Persistence through VPN tools.
- 2024: More use of ToneShell backdoors. More delivery that mixes harmless and harmful files.
- 2025: Active campaigns around the world. Malware keeps evolving (Frankenstein ToneShell, Yokai).
What Has Mustang Panda Done Recently?
From late 2024 and through 2025, Mustang Panda changed how it gets in. It used to rely on one way in. Now it adds USB media to its phishing-heavy operations.
- It kept rolling out new updates to ToneShell. This shows it keeps developing its tools in-house.
- It focused hard on finding targets in European government and maritime organizations. It also showed a greater focus on targets in Southeast Asia.
This APT group is clearly committed. Its spying runs in a lasting cycle. It lines up with Beijing’s foreign policy and national security goals.
Related groups
- In October 2026 Sophos named a separate China-based group, BRONZE SANDCASTLE. It also relies on DLL side-loading. Sophos says it could not reliably link the new group to Bronze President, one of the other names listed above for Mustang Panda.
- Other public reporting has tied a China-aligned group to Mustang Panda. ESET tracks it separately and sees no overlap in its telemetry. See how SlippyNunchucks used Sogou Input Method to deliver DarkVigil.
Conclusion
Mustang Panda shows how persistent and adaptable China-aligned APT groups can be. Its activity across APAC, Europe and North America shows steady change. It moved from operations built on PlugX to newer malware such as ToneShell and Yokai.
Its campaigns focus on diplomatic, government and law enforcement bodies. This shows the lasting strategic priorities of the Chinese state.
Takeaways for Defenders
- Limit the impact of DLL side-loading. Ban removable media and USB devices almost entirely.
- Keep improving email filtering and sandboxing. This helps against phishing with LNK files and archives.
- Watch for any SoftEther VPN installs on your systems. Also watch for C2 traffic patterns tied to Korplug/ToneShell.
Mustang Panda’s work in 2025 sums up one fact. China’s cyber-espionage machine is both persistent and adaptive. Defenders must expect its tools and methods to keep changing from one campaign to the next.
You can download and review the sheet for all the details!
Frequently Asked Questions
What is Mustang Panda?
Mustang Panda is a cyber espionage group that MITRE ATT&CK describes as China-based and active since at least 2012. It uses tailored phishing lures and decoy documents to deliver malware.
What other names does Mustang Panda use?
It is also tracked as Earth Preta, Bronze President, TA416, RedDelta and HIVE0154. MITRE ATT&CK lists these among its associated names, along with others such as Twill Typhoon and UNC6384.
Who does Mustang Panda target?
The post lists government departments, military, law enforcement, NGOs and diplomatic targets. MITRE ATT&CK adds think tanks, religious groups and research centers across the US, Europe and Asia.
How does Mustang Panda get into networks?
The post describes spear-phishing with current-affairs lures, malicious archives and LNK files with PDF decoys, plus growing use of USB-based malware. MITRE ATT&CK also records spearphishing and removable-media spread by PlugX.
What malware does Mustang Panda use?
It uses PlugX (also called Korplug) and newer backdoors such as ToneShell and Yokai. MITRE ATT&CK notes that PlugX uses DLL side-loading to evade antivirus and can copy itself to removable drives.
