
All Resources. Research, Reports And News.
Everything Brandefense publishes in one place: blog posts, threat research, reports, security news and whitepapers.
 Blog The Economic Dynamics of Data Trade in the Dark Web: Strategic Insights for SOC Analysts and Incident Response Leads The dark web has evolved into a complex cybercrime economy driven by data trade, pricing dynamics, and service-based crime models. Discover how dark web monitoring breaks…
 Malware Analysis Reports Donex Ransomware Technical Analysis What You Will Find In This Report? Learn Technical Method of Operation DetailsYou will find the technical details of the Donex ransomware, its functions, and details…
 Blog APT33/Peach Sandstorm: Threat Forecast and Analysis of a Cloud-Focused Adversary APT29, also known as Cozy Bear, is one of Russia’s most persistent cyber espionage groups. From SolarWinds to Microsoft, their operations highlight the sophistication of identity-based…
 APT Groups APT33 (Elfin / Refined Kitten): Iran’s Longstanding Cyber-Espionage Arm APT33, also known as Elfin or Refined Kitten, is Iran’s long-running cyber-espionage group targeting global defense, energy, and aerospace sectors with evolving tactics and tools.
 APT Groups Hazy Tiger: An Emerging Espionage Threat in South Asia Hazy Tiger is a South Asia-linked APT group active since 2013, targeting government, defense, and energy sectors through sophisticated espionage campaigns involving phishing, malware, and custom…
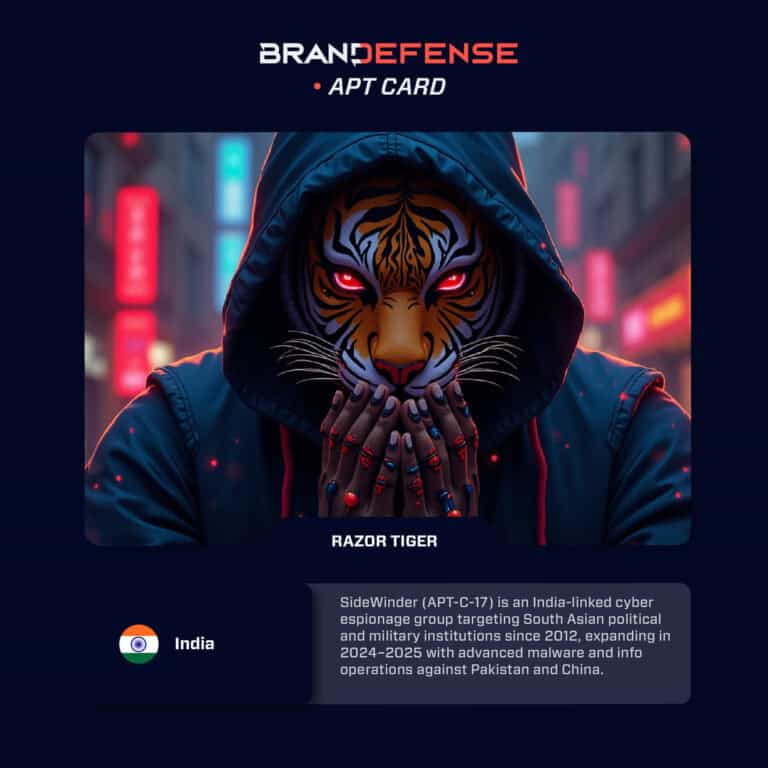 APT Groups RAZOR TIGER: The Persistent South Asian Espionage Threat Razor Tiger (APT-C-17), also known as SideWinder, is a long-standing India-linked APT group active since 2012. Its evolving espionage campaigns now target South Asian governments, defense,…
 APT Groups UNC4841 / SLIME57: China-Linked Espionage Threat Expanding Global Operations UNC4841, also known as SLIME57, is a China-linked APT group active since 2021, conducting cyber-espionage across government, defense, and tech sectors. Exploiting zero-day vulnerabilities and maintaining…
 APT Groups Ghostwriter: Hybrid Influence and Espionage Operations in Eastern Europe Ghostwriter, a Belarus/Russia-linked APT active since 2016, executes hybrid campaigns combining espionage, phishing, and disinformation against NATO and EU entities. Learn how these operations evolved into…
 APT Groups GhostEmperor: Advanced China-Linked Espionage Campaigns GhostEmperor is a China-linked APT active since 2019, leveraging stealthy rootkits like Demodex to conduct espionage across Asia, the Middle East, and Africa. Known for its…
All 98 pages
Our Research, By Email.
Questions About All Resources.
Last updated June 17, 2026-
Everything Brandefense publishes in one list: blog posts, threat intelligence research, reports, security news and whitepapers. Use the tabs to show one type only.
-
Type a word in the search box, pick a tab, or filter by year. Each item shows its type and date.
-
New items are added several times a month, newest first. Every item shows its date.
-
Some reports, such as the quarterly Ransomware Trends Report and the country reports, ask for a short form before the download opens. Blog posts, research and security news are read on the page.
-
Use the email box in the Our Research, By Email section on this page and tick the consent box. The Privacy Policy is linked there.
-
Brandefense is an AI-driven threat intelligence company. Its platform covers cyber threat intelligence, digital risk protection and external attack surface management. You can request a demo on your own domain from the Request A Demo page.
-
The counter above the list shows the current total, and each tab shows its own count. The list includes blog posts, Threat Intelligence Researches, reports, security news and whitepapers. The newest come first.
-
Yes. The year filter lists every year with publications. You can also filter by type, such as Blog, Reports or Whitepapers.
-
Reports are in-depth research, such as quarterly ransomware trends, malware analyses and country reports. Whitepapers are deeper reads that explain attack methods and how to defend against them. Both are listed here.
-
It sits under Threat Intelligence Researches. These are deep dives into live threats. Use the type filter to show only that group.
Research Is General. Your Exposure Is Not.
A demo of the platform, run on your own domain.