Darkweb alerts are notifications that tell a security team when its data shows up on underground sources. This data can be leaked credentials or ransomware victim postings. The post says Brandefense delivers them through a REST API. So alerts can flow into SIEM, SOAR, ticketing and chat tools. This lets teams act before stolen data is exploited.
Why Do Real-Time Darkweb Alerts Matter?
The darkweb has become an intricate ecosystem. Cybercriminals transfer stolen or hacked data there. They plug compromised victims into wallets. They also organize sophisticated and large-scale ransomware meetings.
For organizations of any size, it is not only a risk. It is present and increasing. Credential leaks, insider conversations, and organizational documentation and data show up on underground forums. This is often days, weeks, and sometimes months before exploitation is publicly visible and malicious activity occurs.
Traditional monitoring methods are often too slow to take action. An analyst may find a leak by manually searching for a mention. By then, adversaries have almost always already exploited the weakness.
Real time intelligence, delivered to organizations via APIs, has become central to success. APIs help security teams automate threat emerging and darkweb threat discovery. They put intelligence alerts directly into the security tools teams use. This lets teams respond before an attack occurs, and before damage is done.
Brandefense has built a platform for this reality. It offers endless amounts of API intelligence feeds. It also offers modules that can be integrated and preconfigured. These include a constant variety of historical, current and real-time darkweb intelligence.
It enhances security teams’ ability to see the darkweb and to aggregate activity. It also lets them take action at once.
Brandefense Integration Hub
Brandefense is much more than another threat intelligence feed. Instead, it offers an Integration Hub. This lets an organization connect its existing tools with darkweb intelligence.
Brandefense does not treat threat feeds as separate databases. Its intelligence is delivered at the place it’s consumed, where analysts are actually working.
The Integration Hub provides support for a broad range of platforms:
- SIEM solutions to enrich logs in real-time.
- SOAR platforms as part of an automated playbook.
- Ticketing and workflow solutions such as Jira to manage cases.
- Communication platforms such as Slack or Microsoft Teams for immediate alerting.
- Cloud monitoring such as AWS GuardDuty to monitor.
This breadth of integrations means an organization doesn’t have to recreate processes to consume threat intelligence. Instead, alerts are enriched and correlated in the same dashboards analysts use daily.
API-Driven Darkweb Intelligence
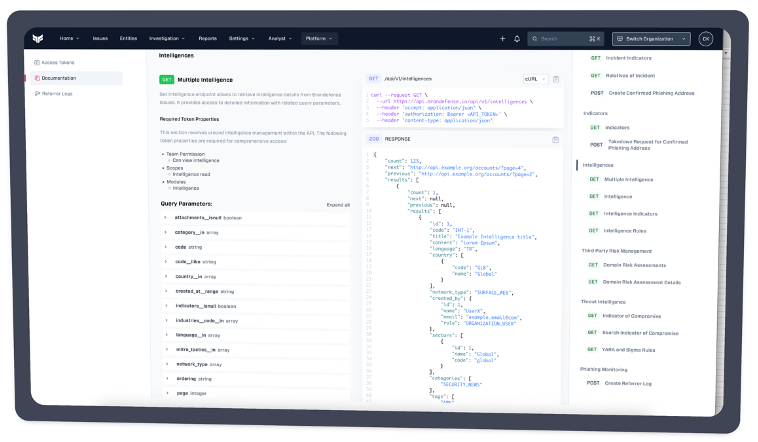
Attackers employ straightforward techniques to identify Shadow IT. One of the most common techniques is Certificate Transparency (CT) logs. All TLS certificates are logged in public CT logs. Attackers can run At the core of Brandefense is an API-first architecture.
The APIs were created to allow fast, structured, and filterable access to darkweb intelligence data. Developers, SOC engineers, MSSPs, etc. can embed intelligence into custom workflows.
The API adheres to REST principles. This makes it easy to integrate into whatever application you are working on.
Authentication is done using secure access tokens. Role-based permissions determine what different users/applications have access to.
The API itself includes some key features:
- Flexible query parameters: filter intelligence by category, country, industry, IOC type, or by time range.
- Structured JSON responses: provide machine-readable results that can be ingested into SIEM dashboards and used in automation pipelines.
- Real-time updates: data sourced from ransomware leaks sites, forums, Telegram channels or any other underground intelligence source.
What Are the Use Cases for Darkweb Alerts?
The combination of the Integration Hub and APIs opens several high-value use cases for enterprises, MSSPs, and government SOCs:
Credential Leak Monitoring
APIs may scan darkweb dumps in real-time. They look for any mention of usernames and passwords linked to an organization’s domains. When a dump is detected, alerts go directly to SIEMs or ticketing tools. This allows faster remediation.
Ransomware Leak Tracking
Ransomware actors are notorious for using leak sites. These sites publish victim data and act as a negotiating tactic to push companies to pay.
Brandefense’s APIs detect new postings in real-time. This allows faster investigation and legal action.
Phishing and Fraud Infrastructure
Brandefense monitors and detects domains, IPs, and hosting patterns advertised on underground marketplaces. This finds phishing infrastructures before they are weaponized.
Brandefense can also tie into preprocessing capabilities tagged to SOAR tools. Then it can automatically kick off domain takedown processes.
Third-Party and Vendor Risk
Not all threats exist within an organization’s realm. Threats can also exist outside of internal assets. They can sit with suppliers, contractors and partners.
Teams can filter intelligence by industry or company name. Then they can respond to issues outside their environment, yet across their entire supply chain.
Automating SOC Workflows
Brandefense integrations into Jira, Slack, and critical SIEM platforms mean alerts flow directly into existing workflows. This greatly reduces the manual work security teams do when they analyze darkweb chatter. Responding to incidents is faster and more efficient.
Conclusions: The Path to Proactive Defenses with Brandefense
Darkweb intelligence only matters when it arrives at the right location and at the right time. Brandefense APIs take the raw intelligence provided and turn it into actionable real-time alerts. These can be automated seamlessly throughout the security stack.
Brandefense helps organizations move past reactive monitoring and toward proactive defense. It does this by providing centrally managed integrations through the Brandefense portal and exposing flexible, secure APIs.
Teams no longer have to wait for a breach notification from a 3rd party monitoring service. They can identify leaked credentials, ransomware exposure, or malicious infrastructure as it occurs. Then they can take action before their organization suffers the consequences.
The future of cybersecurity will be driven by automation and integration. With solutions like Brandefense, organizations may finally have real-time darkweb monitoring that is not only possible, but viable, scalable and effective.
For any organization that is serious about reducing risk, there is no longer a choice as to whether or not to adopt API-first intelligence. It is imperative.