FIN11 is a financially motivated cybercrime group known for phishing-led malware distribution, ransomware enablement and initial access brokering. This post explains who FIN11 is, the other names it is tracked under, how its attacks work, which organizations it targets and how it has shaped the wider ransomware economy. The Brandefense Knowledge Hub also has the Indrik Spider threat group profile.
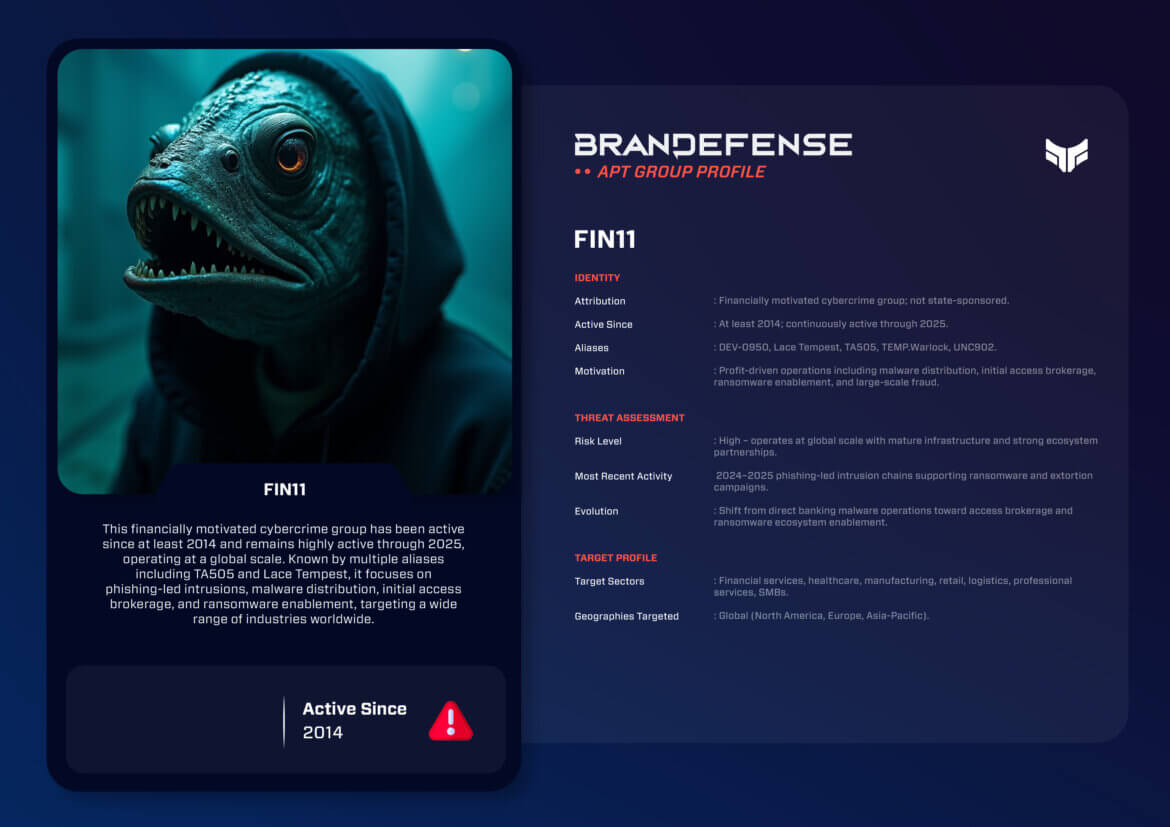
Since at least 2014 (the start date MITRE ATT&CK gives for TA505, a name this post links to FIN11), FIN11 has been one of the leading financially motivated cyber threat groups. This group frequently distributes malware, deploys ransomware and participates in other forms of cybercrime for the purpose of making money. FIN11 has been tracked under several different names-there are also DEV-0950, Lace Tempest, TA505, TEMP. Warlock and UNC902-cofounders, who have evolved from organized crime to fully-fledged, enterprise-type operations capable of running exceedingly complex global campaigns. MITRE ATT&CK has no FIN11 page; for TA505 it lists only the aliases Hive0065, Spandex Tempest and CHIMBORAZO (MITRE ATT&CK G0092). CISA attributes the May 2023 MOVEit exploitation to the CL0P ransomware gang, also known as TA505 (CISA AA23-158A).
In General, FIN11’s goal is to make a profit and not necessarily to engage in espionage as does with state-sponsored APTs. In addition to distributing malware to other criminals as well as serving as an initial access broker, FIN11 plays a key role in shaping the current cybercrime ecosystem by both providing criminals with the means to conduct ransomware and extortion operations.
This blog post presents an in-depth analysis of the identity of FIN11 as well as motivation, Tactics, Major Operations and how they strategically Influence the Global Cyber threat landscape.
Who is FIN11 and what motivates it?
The cybercrime organization FIN11 appears to be motivated by financial gain and most likely originated out of Eastern Europe. It does not appear to have direct links to any nation-state but is comparable to some nation-state cyber espionage groups based on the scale, organization, and duration of its operations.
Tracking and Alias Names of FIN11:
– FIN11
– DEV-0950
– Lace Tempest
– TA505
– TEMP.Warlock
– UNC902
The various names used to track this organization show that it has been operating for an extended period of time and that it has been tracked under different names at different points in time.
The primary motivation of FIN11 is to obtain money. It obtains money through many different means. Some ways in which FIN11 generates money include:
– Theft of sensitive accounts on a large scale
– Access to networks
– Ransomware
– Sale of data
FIN11 targets organizations based primarily on how easy or difficult it will be to compromise the organization as well as the amount of potential financial return that it will receive from the attack rather than on political objectives.
Tactics, Techniques, and Procedures (TTPs)
The distinctive features of FIN11 include its large scale of operation, rapid execution of attacks and high level of success associated with its attacks due to the use of well-developed processes, advanced tools, multiple vectors of attack, and automation.
Initial Access
FIN11 gains access to its target systems primarily through the following methods:
- Mass phishing campaigns that deliver either a malicious link or an attachment.
- Themed emails such as invoices, payment notifications, shipment updates, or business communications.
- Malicious document types (Word and Excel) utilizing embedded macros and/or code exploiting software vulnerabilities.
- Utilizing HTML smuggling techniques, which allow for the delivery of malicious payloads through web browsers and/or third party services, often circumventing email security measures.
Most often, FIN11 uses localized email communications based on the language and/or region of the target, enabling the simultaneous targeting of many individuals around the world.
Execution & Malware Tooling
FIN11 has been linked to the distribution and/or use of various families of malware, including:
- Dridex – a banking Trojan/loader.
- FlawedAmmyy – a remote access Trojan (RAT).
- ServHelper – a downloader and persistence tool for malware.
- SDBbot – a Backend for the facilitation of subsequent payloads.
- Clop Ransomware (historically associated with FIN11).
Malware execution is staged. For example, most malware loaders will fetch secondary payloads after successfully validating the malware environment.
Persistence
FIN11 uses several persistence techniques to maintain long-term access to systems to pursue their monetization goals:
– Registry run keys
– Services posing as legitimate software
– Reinstalling Malware using secondary loaders if the original infection is removed.
Command & Control (C2)
FIN11 employs a highly distributed and rapidly rotating C2 architecture. The C2 architecture consists of compromised or bulletproof servers and utilizes encrypting technologies such as HTTPS or unique encryption schemes.
Due to the short lifespan of C2 domains, it becomes increasingly difficult to take down these domains and attribute them to an attacker.
Defense Evasion
FIN11 heavily depends on obfuscation and packing of payloads, delayed execution and anti-sandboxing, use of LOLBins, and rapid switching between malware families when the likelihood of detection rises.
- Phishing emailMass phishing delivers a malicious link or attachment, often themed as invoices or shipments.
- Staged malwareLoaders fetch secondary payloads after checking the environment.
- PersistenceScheduled tasks, registry run keys and services posing as legitimate software.
- Command and controlRapidly rotating servers using HTTPS or custom encryption.
- Defense evasionObfuscation, packing, delayed execution, anti-sandboxing and LOLBins.
Which organizations does FIN11 target?
FIN11 targets the Following Organizations:
-Financial Services Organization
-Retail and E-commerce Organization
-Manufacturing and Logistics Organization
-Health Care Provider Organizations
-Professional Services and Small to Medium Business Organization
FIN11 Is Globally Distributed and Has Global Reach across North America, Europe, Asia, etc.
FIN11 is not focused on any one industry; instead, it focuses on volume and diversity to maximize ROI.
Notable Operations
TA505 Global Phishing Waves
According to the post, FIN11 was responsible for executing some of the largest Phishing Campaigns to date under the TA505 tag. These Phishing Campaigns were sent globally in large volumes and led to Dridex infections in corporations around the world.
Clop Ransomware Ecosystem
The post says FIN11 played an important role in developing the early Clop Ransomware Model by providing Initial Access and distributing malware. While FIN11’s roles have changed over time, operating as an Infrastructure Provider and Access Brokerage was one of the most significant contributors to Clop’s success.
Shift Toward Initial Access Brokerage
In recent years, FIN11 has transitioned its focus toward selling or transferring access to Compromised Networks to other Ransomware Operations to deploy payloads:
-DoppelPaymer
-LockBit (indirect associations)
-Add Other Extortion
-Focused Actors
This change has reduced operational risk while maintaining profitability.
Recent Developments (2022–2025)
FIN11 has adapted to the changing defensive landscape: Reduced reliance on macros, moving toward HTML smuggling and ISO/VHD delivery, Increased use of loaders and droppers as opposed to Full RATs. FIN11 has been publishing campaigns for a little less than a month, typically refreshed weekly or sometimes daily. FIN11 is now working more closely with Ransomware-as-Service (RaaS) Ecosystems.
What is FIN11’s strategic impact?
FIN11 has had a significant impact on the cybercrime economy and continues to hold substantial influence within it.
Ecosystem Enabler: FIN11 distributes malware and acts as an Access Broker for numerous criminal entities operating throughout the world.
Operational Scale: No other criminal groups can match FIN11’s capability of executing Globally Co-ordinated Phishing Operations in Synergy with the other groups.
Financial Damage: Criminal entities benefiting from FIN11’s malware usually experience significant financial losses as a result of their infiltration by Ransomware, Fraud and Operations Disruption.
Defensive Implications: FIN11’s adaptability requires organizations to continually adjust their Email Security, Endpoint Protection and User Awareness programs to be one step ahead of them.
Conclusion
FIN11 is a prime example of today’s professional level of Cybercrime. FIN11’s large-scale phishing campaigns, use of assorted malware, and links to Ransomware illustrate how Financially-motivated attacks are now carried on a large scale.
As companies continue to strengthen their defenses against Nation-State APTs, Cybercrime Organizations such as FIN11 show that Financially motivated Cybercriminals also represent a significant threat, probably even more significantly than Nation-State APTs, primarily due to their emphasis on scale, speed, and monetization. FIN11 and its many variations will continue to be a significant threat to all organizations and must be mitigated through Continuous Monitoring, Strong Email Security, Speedy Patch Management, and Threat Intelligence integration.
You can download and review the sheet for all the details!