Leaked credentials are usernames and passwords exposed through infostealer logs, data breaches and combolists. Ransomware groups use them to log in as normal users, so they skip malware delivery and start inside the network. Initial access brokers sell this access to ransomware affiliates. The post cites the Black Basta chat leak as showing systematic use of combolists.
Executive Summary
Data breaches remain a critical challenge for cybersecurity. Sensitive data can now spread fast on the dark web and feed targeted attacks, fraud, and ransomware. Over the last two years, several data breaches have stood out for their scale and the lessons they teach. Here are the 10 most critical breaches, and what they mean for businesses and people.
Key Findings
- Credential Supply Chain is Mature: Info‑stealer logs + breach dumps + combolists power a constant stream of valid logins (post‑Genesis: Russian Market, Styx, Telegram subscriptions).
- Industrialization via RaaS/IAB: Initial access is commoditized; brokers sell VPN/RDP/SaaS footholds or share revenue for high‑privilege creds.
- Kill Chain Bypassed: Adversaries skip Weaponization/Delivery and enter with T1078 Valid Accounts/T1133 Outside Remote Services, blending in as normal users.
- Case Corroboration: BlackBasta chat leak (2023–2024) shows systematic use of combolists, self‑run stealers (e.g., Lumma), and third‑party logs (e.g. Meduza), plus coordination around brute force targets.
- Ecosystem Resilience: Genesis takedown accelerated decentralization (more markets, more Telegram), not deterrence.
Why It Matters
- Faster, Quieter Breaches: Shorter time‑to‑initial‑access; reduced detection opportunities.
- Scalable Operations: Low-cost, repeatable campaigns across many victims.
- Third-Party Blast Radius: Trusted relationships (T1199) create lateral risk via suppliers/partners.
- Compliance & Reputation: Identity-led incidents drive notification, penalty, and brand damage costs.
MITRE ATT&CK Quick Map
- Resource Development: Get/compromise accounts: T1650, T1586
- Initial Access: Valid Accounts: T1078; Outside Remote Services: T1133; Trusted Relationship: T1199.
- Post-Access: Persistence/PE/Defense Evasion through the same valid accounts.
- Credential Access: T1003, T1555, T1552, T1056, T1040, T1557
- Lateral Movement: T1021, T1550, T1563
Case Insight: Black Basta
- Even “advanced” actors lean heavily on combolists and brute force to get in.
- Mixed sourcing: IAB + own stealer (Lumma) + third‑party logs (Meduza)
- Central leadership (targets, password lists, tasks) lets the group grow.
Implication: Basic identity gaps (password reuse, weak MFA coverage, exposed RDP) are enough for a major breach, unless identity controls and analytics come first.
Introduction
For decades, cybersecurity has meant perimeter defense: building higher walls and stronger gates to keep intruders out. But what happens when the attacker does not bother breaking down the gate, and simply walks through the front door with a stolen key?
This is not a hypothetical scenario. It is the new reality behind modern ransomware attacks. A huge cybercrime economy has grown around a single product: your credentials. A supply chain now exists to harvest, package, and sell stolen logins to Ransomware-as-a-Service (RaaS) affiliates on demand. It runs from vast dark web credential markets to specialized Initial Access Brokers (IABs). Access is now something you can buy. This changes how attacks begin, because the main battleground moves from the network edge to the user’s identity.
This deep dive explains how this credential-fueled ecosystem works. We look at how info-stealer logs and massive data breaches feed ransomware. We then map the new attack chain with the MITRE ATT&CK® framework. Finally, we study leaked chats from the Black Basta ransomware group to show how these tactics work in practice. The analysis shows why defending against today’s threats means moving from perimeter security to an identity-first approach.
Info-Stealer Logs and Credential Broker Markets
Before its takedown in 2023, Genesis had about 80 million stolen credentials, taken from more than 1.5 million infected computers. This made it one of the largest illicit credential markets.
Credential-as-a-service platforms like this made it much easier for ransomware groups to start. They offered ready-made access packages. Genesis “enabled many cybercriminals to rapidly expand their operations and carry out targeted attacks,” fueling ransomware campaigns.
Many other marketplaces (e.g. Russian Market, 2Easy, and invite-only forums) still sell stolen account logs and even direct network access. Ransomware affiliates can shop for victims’ credentials and sessions in bulk.
Access is usually limited by sign-up steps such as invitation codes or upfront fees. Users fund internal wallets with cryptocurrency and then spend that balance on single data listings. The platform often acts as an escrow agent. It releases data only once payment is verified. Most sites are reached through Tor. Some also offer clearnet mirrors or I2P-based options as a backup.
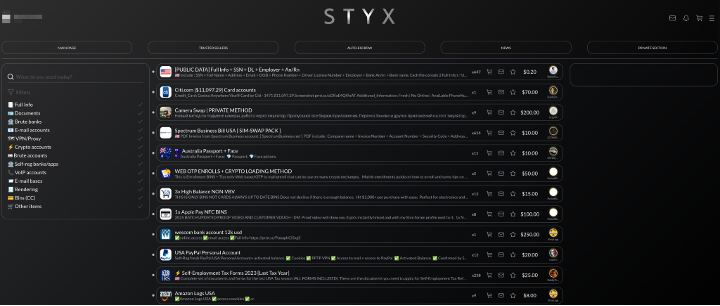
Figure 1: STYX dark web market screenshot.
Deals run through Telegram bots or through direct chats with administrators. Buyers send set commands (for example, /buy [listing_id]) and pay with cryptocurrencies such as Bitcoin or Tether. Once the payment is confirmed, the data often arrives as a direct file transfer or a download link. Some channels run on subscriptions. Paying members get regular access to bulk dumps of newly stolen data.
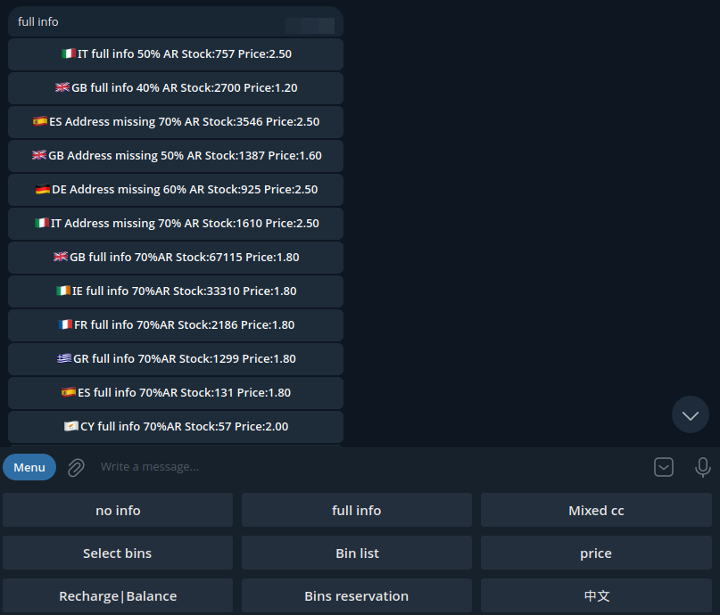
Figure 2: A Telegram-based marketplace screenshot.
Both models stress speed, anonymity, and scale, so threat actors can turn stolen data into money quickly. The Telegram-based model shows a clear shift toward mainstream chat platforms. They avoid the usual hurdles of dark web commerce.
Victim Data Breaches and Large Credential Dumps
Besides malware logs, ransomware actors harvest credentials from public data breaches and “combolists” (combined credential lists). When companies or online services suffer data breaches that leak usernames and passwords, those credentials often circulate on dark web forums or get compiled into massive lists. Over time, billions of credentials from breaches have been gathered into wordlists (e.g. Collection#1-5, RockYou2021) and sold or shared openly. These large leaks often hold millions or even billions of username-password pairs, and they have a real effect. Ransomware operators or their partners can use them for credential stuffing and brute-force attacks to get into networks.
If staff reuse passwords across systems, a leaked password could become the key to the corporate VPN, RDP server, or email account. In time, much of this stolen data becomes public. There it is cross-checked and recombined into targeted password dictionaries.
Attackers build combolists for certain technologies or services, for example VPN or Citrix-specific credential sets. This raises their success rate when they brute-force company systems.
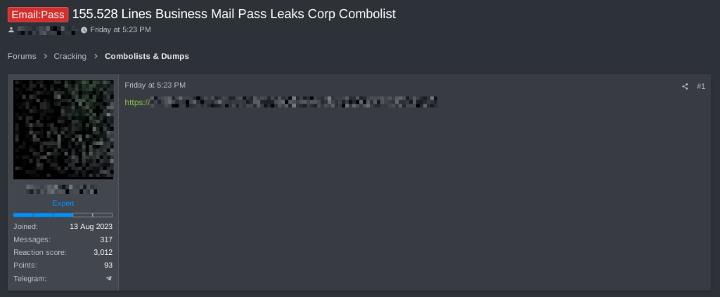
Figure 3: An underground-forum post titled “155,528 Lines Business Mail Pass Leaks Corp Combolist,” shared for free.
So many leaked credentials give attackers “fertile ground.” Even fairly unskilled threat actors can try mass logins with automated tools. Giant credential lists gathered from past breaches and stealer logs help them.
In short, passwords keep spilling from data leaks and malware infections. Ransomware groups never run short of valid logins to try on possible victims.
How Do Initial Access Brokers Fit the RaaS Model?
Ransomware-as-a-Service (RaaS) has pushed credential abuse further, because it splits the work among cybercriminals. In the RaaS model, core developers maintain the ransomware payload and payment infrastructure. Affiliates (often independent hackers) carry out the breaches and share a cut of the profits. This split gave birth to Initial Access Brokers (IABs). These threat actors focus on getting footholds in targets, through stolen credentials, web shell backdoors, vulnerable RDP/VPN servers, and similar routes. They then sell that access to ransomware affiliates.
An IAB might, for instance, use phishing or an infostealer to take over a staff member’s account. It then sets up lasting access in the network and quietly offers that access for sale on hacker forums.
Ransomware affiliates can simply buy ready access instead of breaking in themselves. This outsourcing has greatly widened the reach of attacks. A skilled social engineer or credential thief can feed many ransomware operations without ever deploying malware.
Criminal forums have been full of offers for RDP login pairs or VPN accounts to corporate networks, often at modest prices that depend on the company’s size. Some IABs share profits with ransomware gangs instead of asking a fixed price. For example, a broker might negotiate to receive 30% of any ransom paid if they provide a domain admin credential for initial access. This shows how valuable high-privilege credentials are in the underground economy. The affiliate structure of RaaS means many kinds of actors can take part in ransomware attacks. They range from seasoned exploit developers to low-skill credential harvesters. Figure 4 shows how leaked credentials sit at the center. They lower the technical bar for affiliates and keep the wider RaaS ecosystem going.
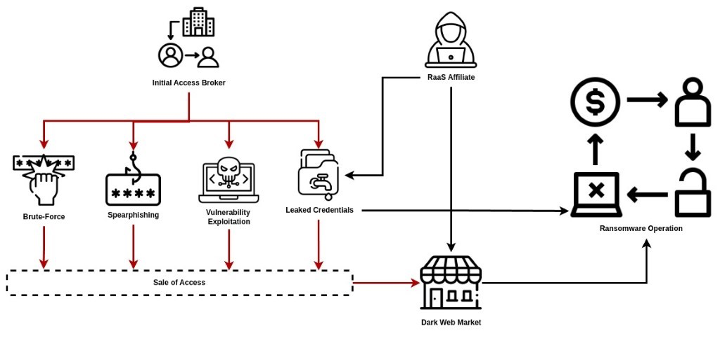
Figure 4: Credential Supply Chain Feeding Ransomware Operations.
Ransomware affiliates also exploit known vulnerabilities to get credentials or bypass logins. Overall, the RaaS model boosts credential abuse by matching credential suppliers with ransomware deployers. Because affiliates are so varied, any exposed credential can quickly find its way into an attack. It may come from a malware log, a phishing kit, or a database leak. This “cybercrime supply chain” has turned initial access into a product. The result is a faster ransomware operation that is easier to scale, where credentials are currency.
Initial Access Brokers (IABs) get in through brute-force attacks, spear phishing, vulnerability exploitation, or leaked credentials. They sell that access directly or on dark web markets, where RaaS affiliates buy it to launch ransomware operations. Some ransomware operators skip IABs altogether. They study leaked credentials themselves and use them to gain initial access.
Attack Chain and MITRE ATT&CK Mapping
Traditional cyberattacks often begin with malware delivery or an exploit that breaks through the network perimeter. Leaked credentials give attackers a shortcut. They move the main attack surface from the network perimeter to the identity layer. Attackers can then skip the noisy first stages of an attack and work from a position of trust. This analysis maps the attack with both the Cyber Kill Chain® and the MITRE ATT&CK® frameworks. It shows the shift in strategy and the need for identity-centric defense plans.
What Does the Traditional Attack Chain Look Like?
To see why compromised credentials help, first look at the standard cyberattack steps. The Lockheed Martin Cyber Kill Chain® lists the first, noisy stages an attacker must finish from the outside: Weaponization and Delivery. In the Weaponization phase, the adversary builds a malicious payload, such as malware, designed to exploit a known vulnerability. The Delivery phase sends this payload to the target, often through phishing emails or compromised websites. These steps take a lot of effort and must cross the network perimeter. That gives defenders clear chances to detect and block the attack.
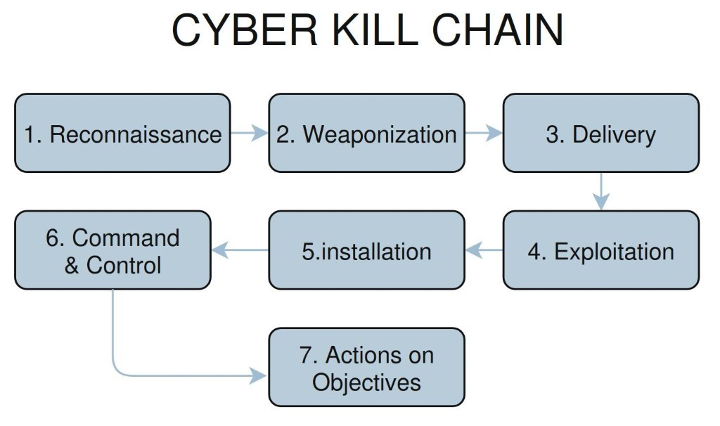
Figure 5: The Cyber Kill Chain outlining the seven stages of a typical cyber attack.
Leaked Credentials Hijack the Kill Chain: A MITRE ATT&CK Analysis
Initial Access: Walking Through the Front Door
An attack that uses leaked credentials skips the Weaponization and Delivery stages entirely. The adversary uses a stolen key to unlock the front door. The attack then starts inside the perimeter, as an authenticated user.
| Topic | Traditional attack | Leaked credentials |
|---|---|---|
| Way in | Malware delivery or an exploit at the network perimeter | A stolen key: logs in as an authenticated user |
| Weaponization and Delivery | Resource-intensive steps that must cross the perimeter | Bypassed entirely |
| Detection | Clear opportunities for defenders to detect and block | Blends in with legitimate user traffic |
| Main attack surface | The network perimeter | The identity layer |
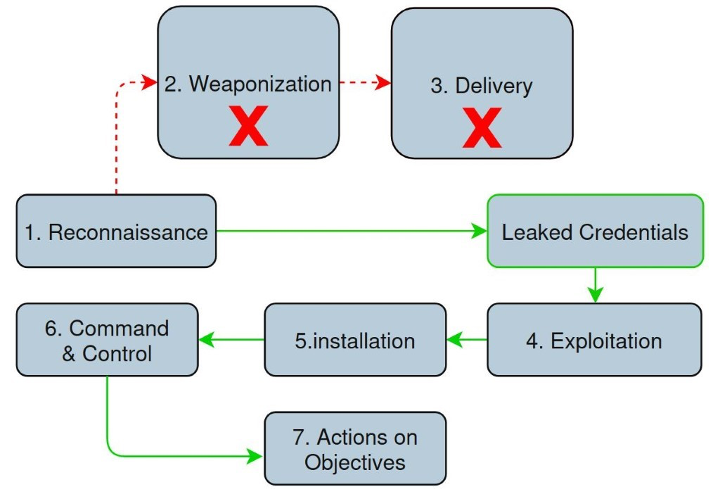
Figure 6: Attack using leaked credentials to bypass first stages and infiltrate as an authenticated user.
The MITRE ATT&CK® framework, which details what adversaries do after they get access, is the best way to study this approach.
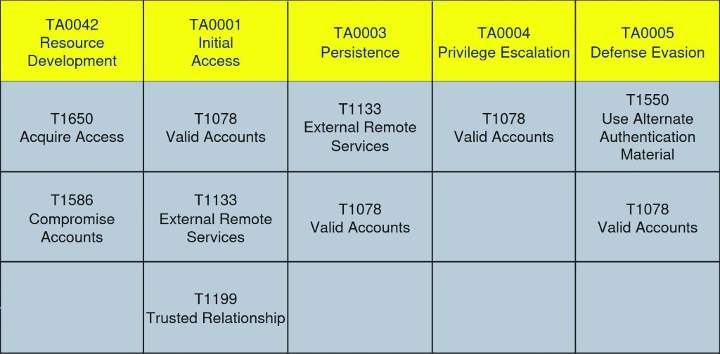
Figure 7: MITRE ATT&CK table illustrating how leaked credentials help every attack step.
- Resource Development: In a typical attack, Resource Development covers the ways adversaries create, buy, or steal resources that can support targeting. With stolen credentials, the credential is the main resource. Adversaries get these in many ways. One is buying them from criminal marketplaces, a behavior mapped to T1650 (Get Access). Another is harvesting them from previous breaches and testing them against new targets. This technique is known as credential stuffing and aligns with T1586 (Compromise Accounts). Both cut the attacker’s upfront time and effort sharply.
- Initial Access: This tactic is where the biggest gain comes. With legitimate credentials, adversaries can get around perimeter security controls built to stop inbound threats. This behavior is cataloged as T1078 (Valid Accounts) and is often used against public-facing applications or T1133 (Outside Remote Services) like VPNs and RDP gateways. The attacker can set up a foothold silently and look like legitimate user traffic. In other cases, an attacker might use T1199 (Trusted Relationship) by compromising a third-party vendor with legitimate access to the target network.
- Persistence, Privilege Escalation, and Defense Evasion: A valid account is a powerful tool with many uses. It helps with three crucial tactics after access. It gives a quick way to keep Persistence. The attacker can simply keep logging in via T1078 (valid account) without installing lasting malware. The account also serves as a base for Privilege Escalation. From a seemingly legitimate position, the adversary can explore the network for misconfigurations. Finally, every action taken as a valid user works as a strong form of Defense Evasion. Malicious activity blends with routine network traffic, which makes detection much harder.
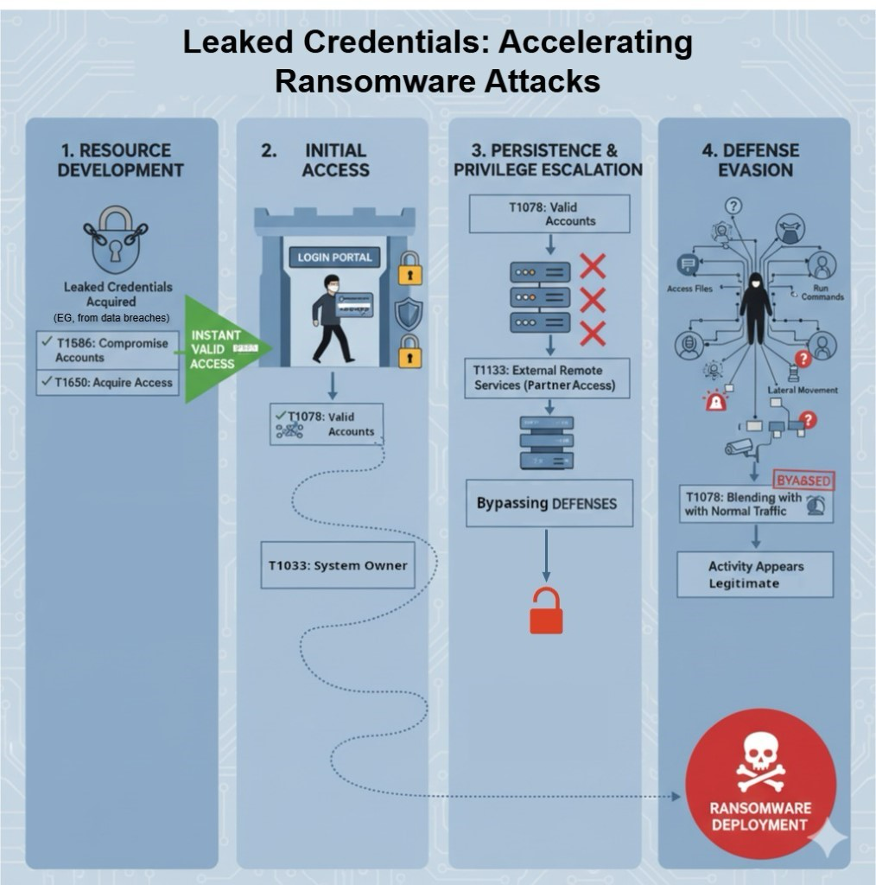
Figure 8: Diagram illustrating how leaked credentials accelerate a ransomware attack.
The Credential Cascade: Full-Scale Network Compromise
Once a first foothold is in place, the adversary’s focus shifts to spreading inside the network. The goal is to use the initial access to get more credentials and raise privileges. The adversary then moves sideways through the network until it controls high-value assets.
Credential Access: The first goal after the break-in is to harvest more credentials from inside the compromised environment. Adversaries use several techniques for this, including T1003 (OS Credential Dumping) to pull hashes and cleartext passwords from system memory. They also go after credentials stored in applications with T1555 (Credentials from Password Stores) and scan for T1552 (Unsecured Credentials) kept in configuration files or scripts. To capture credentials as they are typed, they may use T1056 (Input Capture) via keyloggers. They may also listen to network traffic with T1040 (Network Sniffing) or intercept login attempts using T1557 (Adversary-in-the-Middle) tactics.
Discovery: With a growing stash of credentials, the adversary starts to learn the layout of the internal network. This reconnaissance phase uses several techniques. T1087 (Account Discovery) identifies user and administrative accounts. T1083 (File and Directory Discovery) searches for sensitive data on file shares. T1217 (Browser Information Discovery) finds internal websites and service portals. This intelligence informs the next stage of the attack.
Lateral Movement: With the knowledge and credentials gained, the attacker moves from the first entry point to other systems on the network. This lateral movement often relies on legitimate admin protocols to stay unseen. Common techniques include T1021 (Remote Services), which abuses protocols like RDP and PowerShell Remoting. Others are T1550 (Use Alternate Authentication Material), which authenticates with stolen hashes or Kerberos tickets, and T1563 (Remote Service Session Hijacking), which takes over active user sessions.
- Valid account footholdAdversary enters as an authenticated userTechnique T1078 (MITRE ATT&CK, opens in a new tab)
- Credential accessHarvest more credentials from inside the environmentTechnique T1003 (MITRE ATT&CK, opens in a new tab)
- DiscoveryBuild awareness of the internal networkTechnique T1087 (MITRE ATT&CK, opens in a new tab)
- Lateral movementPivot to other systems using legitimate admin protocolsTechnique T1021 (MITRE ATT&CK, opens in a new tab)
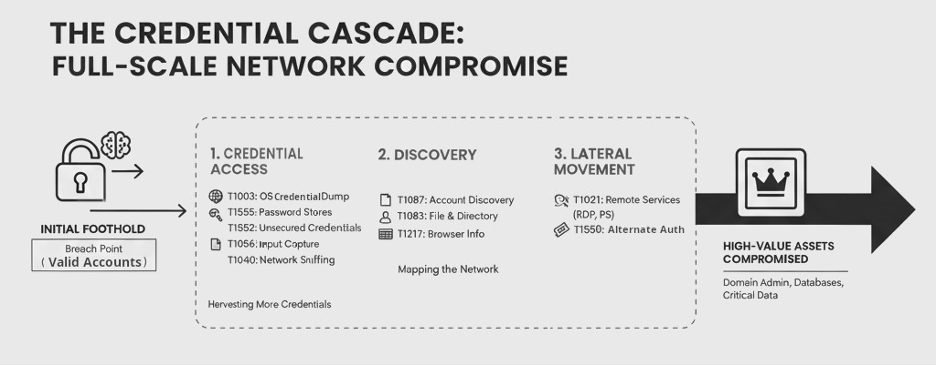
Figure 9: Diagram showing how leaked credentials enable a full-scale network compromise.
Case Study
Black Basta: Credential-Fueled Tactics from Leaked Chats
In early 2025, an unexpected leak of Black Basta’s internal Matrix chat logs (roughly 200,000 messages spanning Sept 2023 to Sept 2024) gave fresh insight into their operations. A core theme in these chats is how widely Black Basta used stolen credentials, and how its tactics changed when certain malware was taken down. Black Basta “leveraged stolen credentials from multiple sources for initial access, persistence, and lateral movement” in their ransomware incidents. In other words, at almost every phase of an attack, they would try to use some set of credentials. They might log into a compromised VPN account to get in, use dumped admin passwords to spread across systems, or keep access by creating hidden accounts.
Black Basta’s leader (alias “GG”) and members ran campaigns to brute force internet-facing servers by trying credentials from combolists. Targets included VPN gateways, RDP servers, and company web apps. These combolists were often built from infostealer logs (also called Login:Password – lists) and other leaked databases.
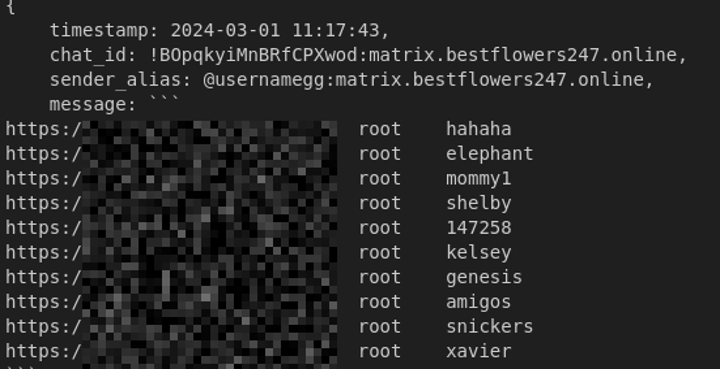
Figure 10: @usernamegg and team brute-forcing an ESXi panel using passwords generated from combolists.
Even though it is an “advanced” group, Black Basta found plain credential guessing to be one of the most reliable ways in. This shows that simple weaknesses, like weak or reused passwords on outside systems, remain a critical risk for companies.
In many messages, GG gives operational direction: sharing credential lists, assigning targets to specific operators, and reviewing brute-force results. This suggests GG worked as the operational lead or at least coordinated initial-access activity.
- Source.
- Internal Matrix chat logs, leaked in early 2025.
- Size.
- Roughly 200,000 messages.
- Period.
- Sept 2023 to Sept 2024.
- Operational lead.
- Alias “GG”, described as the operational lead.
- Own infostealer.
- Lumma.
- Third-party logs.
- Meduza.
There are also direct references to using Initial Access Broker (IAB) channels.
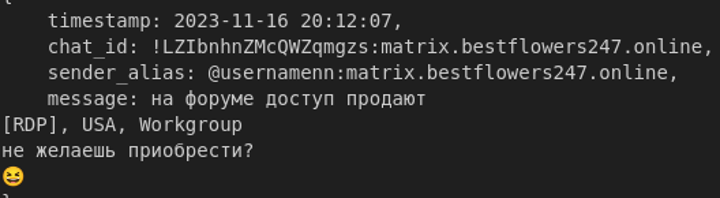
Figure 11: Post on an underground forum advertising RDP access to a U.S.-based company (“Workgroup” environment), offering to sell access.
Black Basta did not rely solely on IABs. The chats show the group distributing its own infostealers most notably Lumma to harvest fresh credentials for operations.
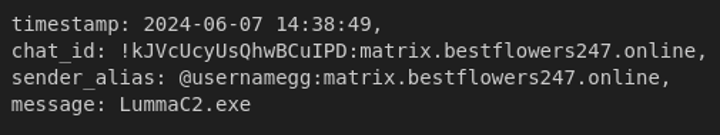
Figure 12: Lumma infostealer binary shared by GG.
Follow-up messages reference an “encrypted LummaC2.exe,” described as extracting “everything” i.e., harvesting credentials and other data at scale.
The chats also include examples of logs from other stealers being used for sensitive targets. For instance, a Meduza log was circulated to access a panel on a .gov domain.
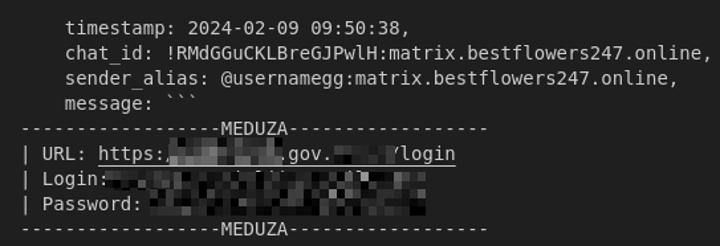
Figure 13: Meduza infostealer log shared by GG to access a government-domain panel.
Trends After the Genesis Market Shutdown
The takedown of Genesis Market in April 2023 was a key moment for cybercrime. It was one of the largest and best organized platforms for trading stolen data. Its closure sent shockwaves through the underground economy. The event changed how threat actors behave and reshaped the markets across 2023 and into 2024.
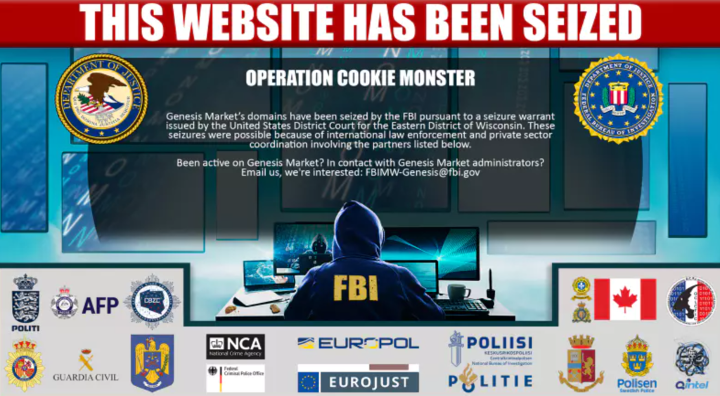
Figure 14: Surface-web homepage after the FBI seizure banner replaced Genesis, April 2023.
After Genesis Market shut down, threat actors quickly moved to other marketplaces. These came to the fore after the closure of Genesis:
- Russian Market
A dark web marketplace reached through Tor, which specializes in logs collected by many data-stealing malware families. Listings often include account credentials, browser cookies, autofill data, saved payment data, system metadata, and sometimes cryptocurrency wallet seeds. Each listing often previews details such as the number of credentials, cookie counts, operating system, and browser types.
- BidenCash
A carding-focused market operating since 2022. On June 4–5, 2025, U.S. authorities seized ~145 darknet and clearnet domains and associated funds tied to BidenCash. The seized domains now redirect to a law-enforcement banner. This operation badly disrupted BidenCash’s infrastructure. (Any reappearing mirrors have been unreliable/short-lived.)
- Styx Marketplace
An English-language darknet market active since 2023, offering infostealer logs and other illicit data. Unlike older markets, it aims at a wider audience that does not speak Russian.
At the same time, Telegram channels became major hubs for sharing stolen data. Subscription-based credential dump services multiplied, which made it easier for less experienced threat actors to start. Telegram operations are decentralized, so they are harder to take down.
Without Genesis’s advanced browser fingerprinting tools, threat actors had to adapt. Manual methods for using stolen cookies and credentials became more common. The absence of Genesis also led to new tools, sold for profit, that process raw infostealer data and put it to use.
After Genesis, infostealer data trading became more decentralized and fragmented, yet it stayed resilient. Major platforms like Russian Market grew their share, Telegram-based operations flourished, and threat actors quickly adapted their operational security practices and exploitation techniques. The underground economy proved highly agile in the face of disruption.
Conclusion
Info-stealer logs in credential broker markets have sharply changed the ransomware threat. They have created a cybercrime ecosystem where compromised credentials are the currency of compromise. What began as one central platform, Genesis Market, has grown into a resilient, decentralized network. It consists of marketplaces, Telegram channels, and Initial Access Brokers. Together they make it easier than ever to start a ransomware operation.
The evidence shows that credential abuse has become the favorite way in for today’s ransomware groups. It runs from the large-scale operations seen in Black Basta’s leaked communications to the fast adaptation after Genesis Market’s takedown. With stolen credentials, threat actors can skip traditional perimeter security and enter networks as authenticated users, working from a position of built-in trust. This is a shift from noisy, detectable intrusion methods to silent ones that blend malicious behavior with legitimate network traffic.
The RaaS model has made this threat bigger by creating specialized roles in the cybercrime ecosystem. Initial Access Brokers sell network entry points like goods. Ransomware affiliates can focus on deploying the payload and encryption instead of overcoming the hurdles of the first compromise. This division of labor has increased the scale and frequency of attacks. It has also put advanced attack capabilities in the hands of many more threat actors.
Perhaps the most troubling sign is how resilient this underground economy is. When Genesis Market was taken down, it only sped up the move toward more distributed models that are harder to take down. Telegram-based operations, many marketplace options, and a steady flow of fresh credentials from malware campaigns will keep this threat alive. It will persist and evolve whatever happens to single platforms.
For defenders, this reality means a basic change of plan. A plan focused on perimeters is still needed, yet it is not enough when the threats begin with valid credentials. Companies must adopt identity-centric security plans that assume compromise and focus on detecting unusual behavior rather than preventing initial access. This includes strong credential hygiene, multi-factor authentication, and privileged access management. It also includes behavioral analytics that can tell normal user activity from credential abuse.
The credential supply chain that feeds ransomware operations will keep growing under three conditions. Password reuse stays common, data breaches keep leaking login data, and info-stealer malware keeps spreading. The underground economy has proven it can adapt quickly to disruptions. To make a real dent in this threat, defenders need steady pressure on several fronts: technical countermeasures, law enforcement action, and basic changes in how people sign in.
In the end, the growth of credential markets shows cybercrime maturing into a skilled, resilient industry. As this ecosystem keeps changing, defenders must adapt just as fast. They need to move beyond reactive security measures toward proactive, intelligence-driven approaches. Today, credentials are currency, and every leaked password is a possible ransomware incident waiting to happen.
To act on this, see our guide to defending against leaked credentials.