

The lessons of 2024 give a strong base for 2025, as cybersecurity keeps getting more complex. Organizations have seen that security spending needs a plan. Money should go to the tools and practices with the biggest effect. Businesses can strengthen their defenses and control costs by putting AI-driven solutions, proactive risk management, and social optimization first. Success in 2025 will depend on using these lessons to build a security posture that can take a hit. That posture must handle current and new threats.
Cost-Effective Cybersecurity: Prioritizing Investments
The digital threat landscape grows more complex, and organizations are under constant pressure to get the most from their cybersecurity budgets. A cost-effective cybersecurity approach is more than cutting costs. It needs a plan and a deep understanding of risk profiles. Organizations must find their most vulnerable assets and spend on securing them. High-priority areas such as endpoint protection, automated threat remediation, and real-time monitoring need the most attention. Advanced tools that detect and stop threats early in their lifecycle give strong defenses without extra cost.
Full cyber threat intelligence feeds are one of the most effective ways to improve cost-efficiency. They give insights into emerging risks that teams can act on, so organizations can expect threats and stop them before they grow. When such feeds connect to existing systems, operations stay smooth, work overlaps less, and security teams work more efficiently. Optimizing Security Operations Centers (SOC) with AI-driven tools and automation also improves how resources are used. These methods make sure every dollar spent on cybersecurity helps build a defense that can adapt to current and future challenges.
AI-Driven Solutions for Streamlined Threat Detection
Adding AI-driven solutions to cybersecurity operations changes how organizations detect and respond to threats. With artificial intelligence, businesses can analyze vast volumes of data in real time. They can find subtle patterns and anomalies that traditional systems might miss. These insights help security teams act quickly and with confidence, often stopping risks before they turn into major incidents. AI is especially good at spotting complex attack vectors and correlating data points across different systems. That makes it a must-have in modern security.
AI-driven tools also detect threats more accurately and take a big load off human analysts. They can filter out low-priority alerts, so security teams can focus on genuine risks. Adding AI to proactive risk management strategies means vulnerabilities are found and fixed before attackers can exploit them. AI can also learn from new information, which makes it essential to any forward-looking cybersecurity strategy. These technologies streamline threat detection. They also pay off over the long term, because organizations stay ahead of changing cyber threats.
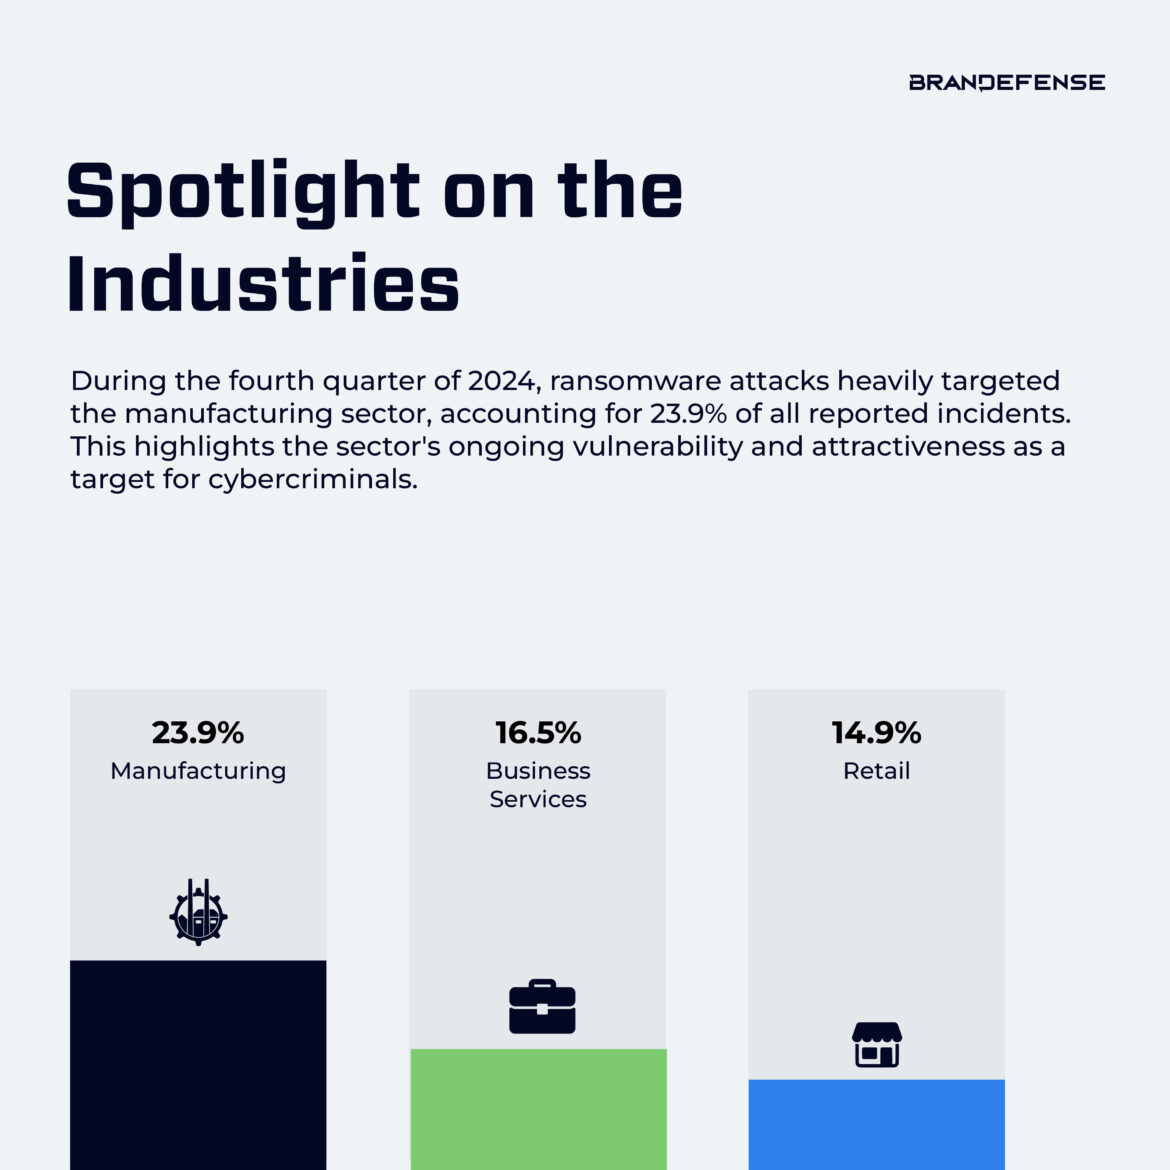
The Q4 2024 Ransomware Trends Report shows a surge in global ransomware activity. Attacks on critical industries rose notably, and the leading threat actors shifted.
For this report, we mainly studied the attacks carried out by various cybercriminal groups. Our analysts watched these groups closely from October to December. We then worked out the 3-month trends of the attacking groups from several factors. These factors are the countries targeted, the industries affected, the ransom amounts demanded, and the annual revenue of the targeted companies.
To gain more details, Download the Report
Vendor Risk Management in a Complex Digital Ecosystem
Companies rely heavily on third-party vendors and service providers, so vendor risk management has become a key part of any cybersecurity strategy. These outside partners often have access to sensitive systems and data. Managing these risks takes a strong framework with three parts: regular assessments of vendor security practices, continuous monitoring of their digital footprints, and strict access controls. This approach keeps weak spots in the supply chain from harming an organization’s broader security posture.
These solutions help businesses enforce compliance with industry standards and regulations. That lowers the chance of breaches that start in supply chain weak spots. Adding automated threat remediation to vendor management also lets organizations respond quickly to incidents and limit their impact. A proactive and shared approach to vendor risk management strengthens defenses and builds trust across the digital ecosystem.
Managing Third-Party Risks with Brandefense: A Strong Shield Against Cyber Threats
Cybersecurity is no longer just about protecting internal networks. It now also means protecting a whole supply chain of business partners, suppliers, and outside service providers. This wider network also brings third-party cyber threats.
This is where Brandefense comes in. It offers a proactive threat intelligence solution that helps organizations manage third-party risks well.
But how does Brandefense’s Third-Party Risk Management (TPRM) solution support businesses?
How Does Brandefense’s Third-Party Risk Management Solution Help Reduce Risks?
Brandefense is a full cybersecurity platform that helps organizations find and manage security risks that come from third parties. The TPRM solution continuously monitors all stakeholders in the supply chain, so you can detect possible security threats at an early stage.
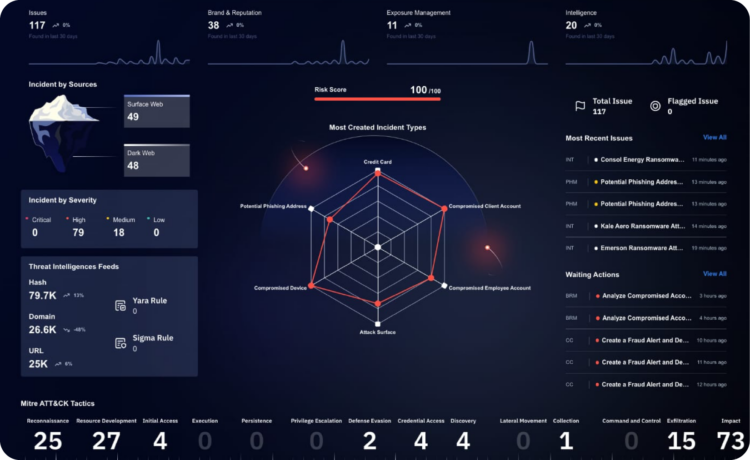
1. Continuous Monitoring of Third-Party Risks
Traditional security approaches often rely on periodic assessments of third parties. But cyber threats are dynamic and always changing. Brandefense’s automated and continuous monitoring system lets organizations evaluate the cybersecurity posture of their suppliers and business partners in real time.
2. Attack Surface Mapping and Vulnerability Detection
Third-party companies may have security vulnerabilities without knowing it. Brandefense uses vulnerability scans, open port analysis, credential leak detection, and attack surface evaluation. With them it finds possible security gaps in your vendors and ranks the risks.
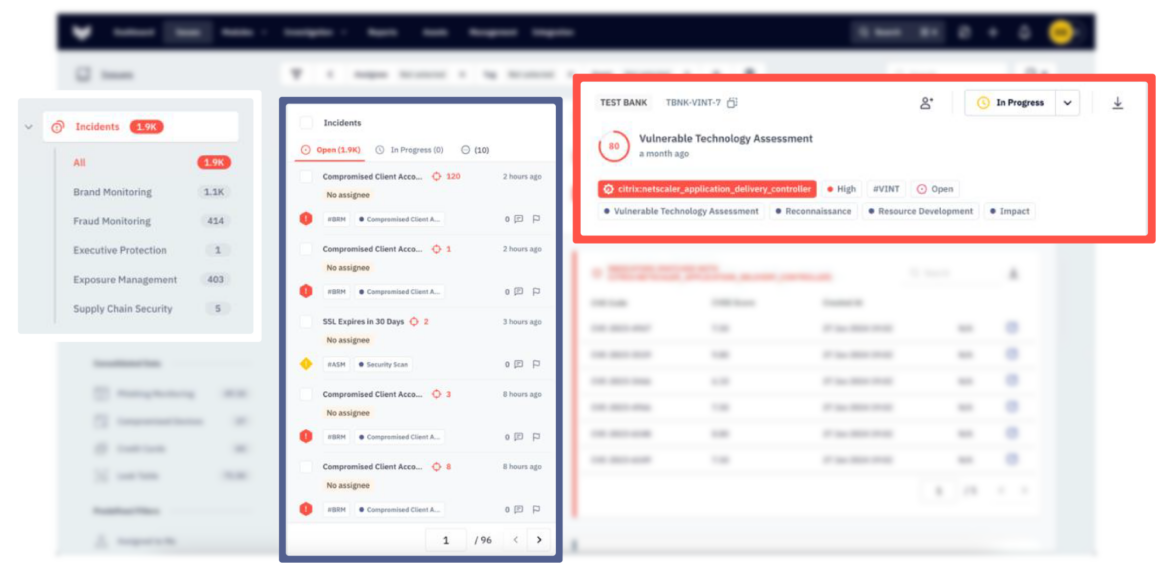
3. Dark Web and Deep Web Monitoring
Many data breaches and malicious activities happen in underground forums or inside private attacker networks. Brandefense continuously scans the dark web and deep web to detect leaked information about your third parties. This lets you act before an incident grows.
4. Risk Prioritization with Security Scoring
Not all third-party relationships carry the same level of risk. Brandefense uses advanced threat intelligence analytics to give each third party a security score. This helps security teams rank high-risk vendors first and build a more effective risk management strategy.
5. Automated Alerts and Reporting Mechanism
When Brandefense detects a risk, it sends automated alerts so security teams act at once. It also produces detailed reports. These help SOC analysts, CISOs, CIOs, and CTI analysts make proactive security decisions.
The cyber threat landscape is getting more complex, and the security posture of your business partners directly affects your own. The Brandefense Third-Party Risk Management (TPRM) solution gives automated, continuous, and proactive monitoring to strengthen your cybersecurity posture. With real-time threat intelligence, security scoring, and dark web monitoring, Brandefense is an essential tool for SOC teams, CISOs, CIOs, and all cybersecurity professionals.
Reducing False Positives to Save Time and Resources
One of the most lasting problems in cybersecurity is the huge number of false positives from traditional detection systems. These alerts are meant to protect assets, but they often swamp security teams. They pull attention away from genuine threats and waste effort. Fixing this takes advanced false positive reduction strategies that make threat detection systems more accurate. Machine learning algorithms and AI-driven analytics help a great deal here. They can analyze data, add context, and tell real threats from harmless anomalies.
Fewer false positives mean better efficiency, and organizations can use their resources more effectively. Security teams can focus on high-priority incidents and fix critical vulnerabilities promptly. Automated threat remediation tools improve this process further by allowing rapid responses to confirmed threats. These systems can isolate affected assets, neutralize risks, and restore operations with little disruption. With fewer false positives, organizations can optimize their SOC operations and reduce the risk of alert fatigue. They also keep a stronger overall security posture as threats change.
Proactive Risk Management for Enhanced Security Posture
With threats changing so fast, proactive risk management has become a cornerstone of cybersecurity. It means expecting possible threats, assessing vulnerabilities, and acting to reduce risks before they cause harm. Companies that move from reactive to proactive strategies lower the chance of a successful cyberattack. Continuous monitoring of digital assets and regular vulnerability assessments form the base of this approach. They let businesses keep a flexible security posture that responds to change.
A key part of proactive risk management is using cyber threat intelligence feeds. These feeds give real-time insights into the tactics, techniques, and procedures (TTPs) of threat actors. Security teams can then expect attacks and counter them. Organizations can combine this intelligence with advanced analytics and risk modeling to rank what to fix first. This sends resources to the most urgent vulnerabilities. The result is better security and a culture of vigilance and preparedness. It helps organizations face an increasingly complex digital landscape with confidence.