Angry Likho is a spear-phishing espionage group, also tracked as Sticky Werewolf. Public reporting says it mainly targets government agencies and large organizations in Russia and Belarus. Its attacks start with emails that carry malicious attachments, such as archives or Windows shortcut files, and use the Lumma stealer to take data. Other names for the group include Core Werewolf, GamaCopy and PseudoGamaredon.
The past couple of years have seen more mid-sized espionage groups that use adaptive, opportunistic and low-noise cyber tactics. One of the most significant is Angry Likho, which is regularly referred to by multiple aliases. The intelligence reports on Angry Likho list several of them.
Larger and more established Advanced Persistent Threat (APT) groups overshadow it. Even so, Angry Likho is developing into a persistent and strategically significant threat to organizations in Russia and Belarus.
The blog below will provide a comprehensive review of Angry Likho’s identity, including its motivations, tradecraft, notable activities, and evolving capabilities up to 2025. The blog contains no plagiarised content and is presented in a professional and threat intelligence format.
Introduction: A Mid-Tier APT With High Strategic Output
Angry Likho is one of many cyber threat actors that do not always have the financial backing to develop highly sophisticated implants. In many cases, it has used the same techniques as its competitors. These are persistence, operational agility and social engineering skills. It also adapts rapidly to keep a relevant cyber presence.
Angry Likho has gained an international reputation for consistently targeting government agencies and large organizations in Russia and Belarus. Its activity includes:
- espionage
- credential theft
- covert information gathering
- rebuilding quickly after being taken down
- a modular malware ecosystem based on copying and repurposing components from other cyber threat actors in the region
Angry Likho does not have the same global reach as traditional Advanced Persistent Threats (APTs). It does, however, present an ongoing and focused threat to organizations in Russia and Belarus.
Who is Angry Likho and what drives it?
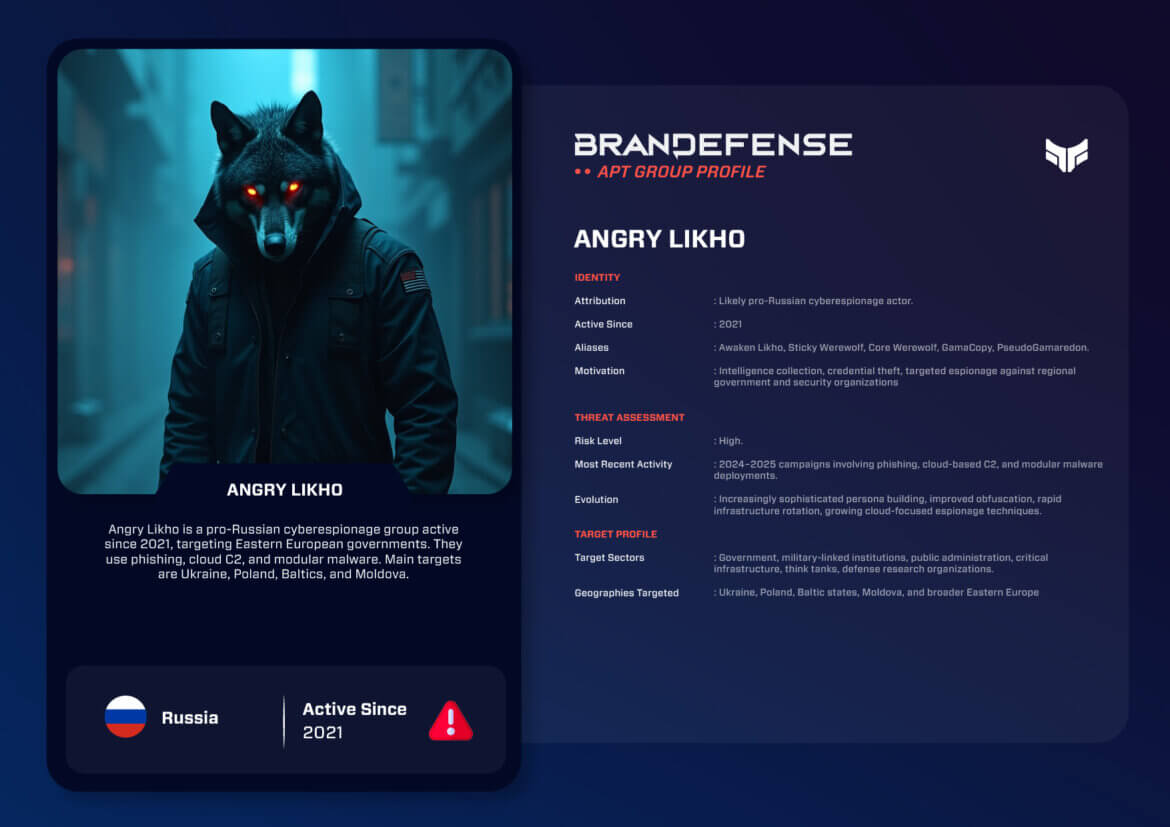
Numerous aliases of Angry Likho indicate its scope of operation across numerous campaigns/malware clusters. These aliases include the following examples:
- Sticky Werewolf & Core Werewolf for persona-based phishing waves
- GamaCopy for code lineage and reliance on copy-based toolchains
- PseudoGamaredon for operational similarities to the well-established Gamaredon gang, but not the same group
Motivational Overview
Angry Likho is motivated by espionage/intelligence gathering. It has four major objectives:
- Exfiltrating sensitive sovereign (government) administrative documents
- Harvesting credentials to provide long-term access for persistent monitoring
- Gaining persistent access to federal/military linked systems
- Supporting additional broad operational objectives
While not formally labeled as a specific nation-state unit, Angry Likho has overlapping infrastructure, targeting patterns and tool set philosophy with other groups. Public reporting does not settle who is behind it.
TTPs: The Operational Playbook of Angry Likho
Angry Likho distinguishes itself from others by having very precise, consistent tradecraft, rather than the most advanced exploits. They carry out their operations with staged infection flows, tailored phishing and lightweight malware.
1. Initial Access: Social Engineering at Scale
The majority of their campaigns start with a highly believable phishing message that is often themed around the following topics:
- Government Communications
- Defence Mobilization
- Invites to Official Meetings
- Security Bulletins
- Registering or Identifying Yourself
Angry Likho is very effective in imitating the Eastern European Government Institutions’ Tone, Visual Identity and Communication Styles. The way they deliver their phishing campaigns includes the following methods:
- Malicious Microsoft Office documents
- Shortcuts (.lnk files)
- Archive files containing dropper scripts
- URLs pointing to attacker controlled websites
- Fake PDF notices hosted on temporary cloud storage services
Additionally, Angry Likho’s phishing lures are quick to adapt and incorporate current real-world political and military events, which contributes to their overall success rates.
- Phishing messageA believable lure, often on a government themeTechnique T1566 (MITRE ATT&CK, opens in a new tab)
- Attachment or link openedOffice file, shortcut, archive or link to a fake site
- Small script or backdoor runsPowerShell, C# or macro loader that blends in
- Access is keptScheduled tasks, registry run keys or startup folderTechnique T1053.005 (MITRE ATT&CK, opens in a new tab)
- Data is takenOften sent out through cloud file storage
2. Payloads: Lightweight, Modular, and Designed for Stealth
Angry Likho purposefully uses minimalistic malware designs as opposed to large noisy implants. Instead, the group favors:
- PowerShell or C# based small backdoors
- Macro-based loaders
- Script-based collectors
- Clipboard Monitors
- File Exfiltration tools
- Credential harvesters
The significant features of their malware are:
- Minimal Code Signature
- Obfuscation of command strings
- Use of common Windows Utilities to blend into standard system behavior
- Modular architecture that allows for rapid swapping of components
This creates a challenge for detection, particularly when there is little EDR visibility in a given environment.
3. Persistence & Lateral Movement
Angry Likho maintains their presence on target networks using traditional but effective mechanisms for persistence:
- Scheduled tasks
- Registry Run Keys
- Startup Folder Persistence
- Credential Reuse to Pivot between Systems
Lateral Movement is usually done methodically and deliberately. Instead of spreading to other computers across the network, the group prefers to gain a foothold at the most valuable assets, such as:
- Email Servers
- Administrative Workstations
- File Servers with Strategic Documentation
This behavior reflects the group’s objectives that are more aligned with espionage than with destructive or monetary goals.
4. Command & Control (C2): Disposable and Cloud-Aware
This group employs short-lived C2 infrastructures with the following characteristics:
- They leverage compromised WordPress sites
- They use Dynamic DNS (Domain Name Service)
- They host their operations using disposable VPS hosts;
- They utilize cloud file storage as a way to store exfiltrated data from their victims
- They create secure communications through encrypted (HTTPS) channels.
As cloud platforms evolve, they are becoming more important to attackers. Attackers use them to conceal their operations and to exfiltrate data without conventional outbound connections.

Who does Angry Likho target?
Angry Likho has consistent regional targeting as well as their main targets being:
- Government Ministries/Affiliated Agencies
- Military/Affiliated Organizations
- Entities Related to Critical Infrastructure
- Municipal/Public Administration Agencies
- Think Tanks/Policy Organizations
- Universities/Securing Informations(Classified) Related to Defense
Additionally, public reporting says the main focus of Angry Likho’s activity is organizations in Russia and Belarus. This suggests a strategic intelligence effort that supports monitoring of political, military and civil defense activities.
Notable Operations & Campaigns
Some campaigns have been reported on less than others. The following still shows the growth of Angry Likho.
2023: Emergence as Sticky Werewolf
Malpedia lists the group as active since 2023. Public reporting describes its phishing campaigns as aimed at government agencies and large organizations in Russia and Belarus.
2023–2024: GamaCopy and PseudoGamaredon Tooling
During 2023 and 2024, we noticed code overlap between Angry Likho tools and Gamaredon-style tools. The infrastructure and operational behavior were unique, however, so we named the tools “PseudoGamaredon.”
2024–2025: Multi-Vector Espionage with Improved OPSEC
Most Recent Angry Likho Campaigns demonstrate the following:
- Higher encryption levels on C2 traffic
- Better Phishing Approaches and Methods
- Increased use of Cloud-based Data Exfiltration
- Longer operational dwell times.
The change in ciphering methods shows that Angry Likho has developed further as a malicious actor. It now uses better development techniques than before.
What do recent developments in 2025 reveal?
Indicators from 2025 show several important trends:
- Refined persona development via direct outreach to targeted staff.
- Improved loader obfuscation.
- Faster infrastructure rotation.
- Use of commercially available remote management tools to provide stealth access.
- Increased focus on cloud account compromises, particularly email and document storage.
These findings indicate that Angry Likho is maturing as an organization and transitioning to more cloud aware, resilient espionage workflows.
Conclusion: A Persistent Espionage Threat Requiring Continuous Monitoring
Angry Likho shows a new generation of mid-tier APT (advanced persistent threat) groups. They are not necessarily the most technically advanced. They are, however, extremely adaptable, aware of their environments, and strategically aligned with ongoing regional conflicts. Their reliance on social engineering makes them difficult to detect, and small C2 infrastructures are easier to redeploy after a takedown.
Defensive Recommendations
Defensive recommendations for organizations that are vulnerable should include:
- Strengthening phishing defenses.
- Enforcing strict access control and multifactor authentication.
- Continuously monitoring all cloud authentication activities.
- Utilizing behavioral endpoint detection and response tools to help identify script-based malware.
- Conducting user awareness training based on recent geopolitical events.
Angry Likho’s operations will likely increase through the remainder of 2025. Governments and organizations throughout Eastern Europe, and beyond, need to adopt intelligence-driven defenses.
You can download and review the sheet for all the details!