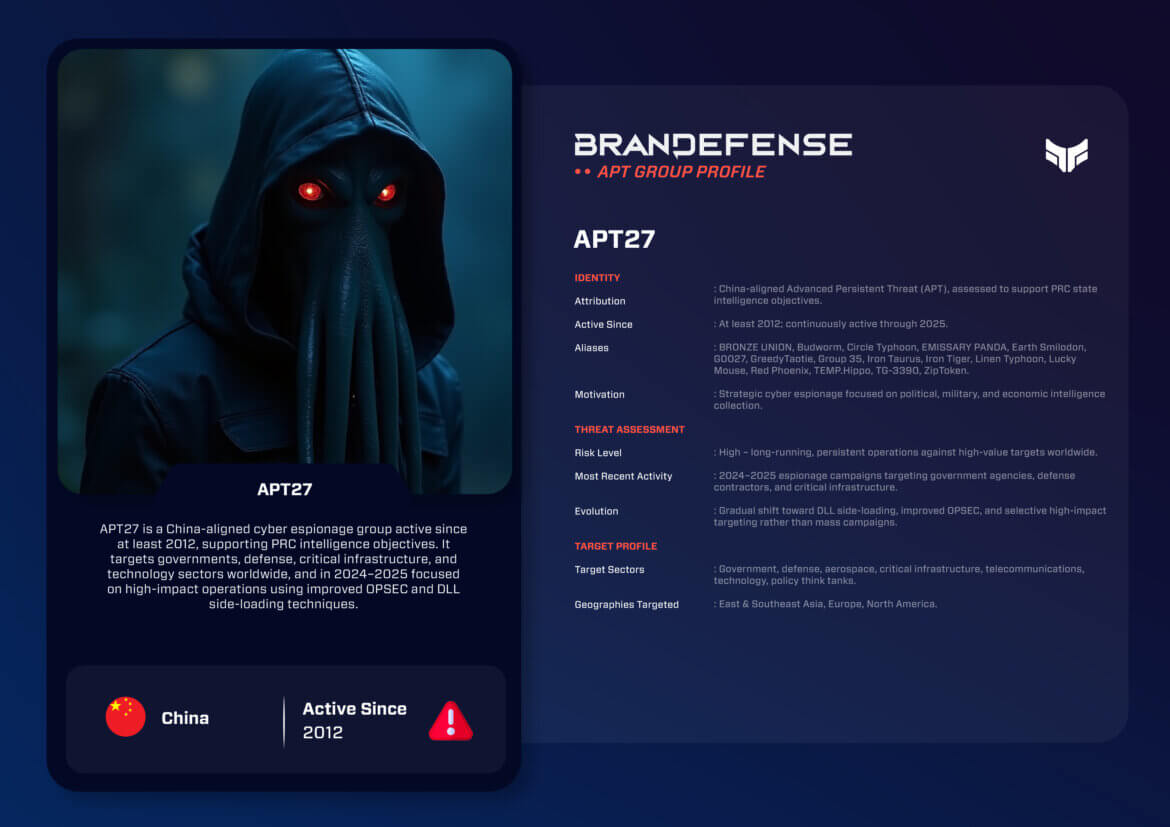
APT27 is an advanced persistent threat group. MITRE ATT&CK describes it as a Chinese threat group conducting cyberespionage. The post says its activity has been documented since at least 2012. It targets government agencies, defense contractors, critical infrastructure, technology companies and think tanks in Asia, Europe and North America.
Our APT27 threat group profile lists the US Department of Justice, Treasury, German and Belgian statements with dates. Another China-linked group with a profile is APT41.
APT27 has been one of the most prolific and long-running China-aligned Advanced Persistent Threat Groups (APTs) in history. It has a sustained history of cyber-espionage operations dating back more than ten years. The cyber security community has many different names for APT27. They include BRONZE UNION, Budworm, Circle Typhoon, EMISSARY PANDA, Earth Smilodon, G0027, GreedyTaotie, Group 35, Iron Taurus, Iron Tiger, Linen Typhoon, Lucky Mouse, Red Phoenix, TEMP.Hippo, TG-3390, and ZipToken. APT27 shows how vendor naming is split for cyber operations of the Chinese government.
The main purpose of APT27’s campaigns is long-term collection of intelligence, as opposed to disruption, or financial gain. The group has targeted, on a continual basis, Government Agencies, Defense Contractors, Critical Infrastructure, Technology Companies, and Think Tanks across Asia, Europe and North America. This blog article will provide an in-depth Intelligence analysis of APT27’s identity, motivation, tactics, Major Operations, and Strategic impact.
Who is APT27 and what does it want?
Most of the community agrees that APT27 is aligned with the intelligence priorities of the People’s Republic of China. There are several indications that APT27 has an association with elements of the military or the intelligence services of China. These come from public indictments and from analysis of technological resources. The exact command structure is unclear.
The community has attributed APT27 to China. It has linked the group to activities directed by either the People’s Liberation Army (PLA) or Ministry of State Security (MSS). This is based on the timeframe of the campaigns and the type of target.
APT27’s activity has been documented since at least 2012, and it has continued to operate up through at least 2025.
APT27 is known by a variety of names, including BRONZE UNION, Budworm, Circle Typhoon, EMISSARY PANDA, Earth Smilodon, G0027, GreedyTaotie, Group 35, Iron Taurus, Iron Tiger, Linen Typhoon, Lucky Mouse, Red Phoenix, TEMP.Hippo, TG-3390, and ZipToken.
The main motive of APT27 is cyber espionage that serves China’s strategic interests. This includes acquiring sensitive information within the political, military, and economic areas. That information would help China shape its national security strategy, advance its foreign policy goals, and improve its technology.
- Also known as
- BRONZE UNION, Emissary Panda, Iron Tiger, Lucky Mouse, TG-3390, G0027 and others
- Alignment
- China-aligned, per the post
- Activity
- Documented since at least 2012, per the post
- Motive
- Cyber espionage (the post and MITRE ATT&CK)
- Targets
- Government, defense, critical infrastructure, technology, think tanks
- Regions
- Asia, Europe, North America
What tactics does APT27 use?
The approach to TTPs undertaken by APT27 is a balance between stable and flexible technologies. They favor tried-and-true methods. APT27 also use a few new tools in their operations.
Initial Access
APT27’s preferred methods of gaining initial access to victim networks include the use of:
- Spearphishing E-mail messages, related to Diplomacy, the Military or Policy
- Delivery of Backdoor malware via Malicious links and/or attachments
- Exploitation of a Known Vulnerability in Publicly Available Web Servers/Edge Devices
- Using fake Credentials Hoarding Web portals that impersonate Real Government/Enterprise Services
Phishing remains a core access vector. It is often tailored to the language and institutional context of the target.
Execution & Tooling
Once inside a network, APT27 deploys a mix of custom and commodity malware, including:
- Remote Access Trojans (RATs) such as PlugX and HyperBro variants
- Custom loaders and shellcode runners
- Tools for credential dumping and system reconnaissance
The Knowledge Hub also has the Derusbi malware page.
The group favors lightweight, modular malware. It can be easily replaced if detected.
Persistence
APT27 sets up persistence using:
- Registry run keys and scheduled tasks
- DLL side‑loading via legitimate software
- Web shells on compromised servers
- Redundant backdoors to maintain access
These mechanisms allow the group to survive partial remediation efforts.
Command and Control (C2)
C2 infrastructure is typically:
- Distributed globally across compromised servers
- Hidden behind dynamic DNS and frequently rotated domains
- Encrypted using HTTPS or custom protocols
APT27 often blends malicious traffic with legitimate web traffic. This reduces detection.
- Initial accessSpearphishing, exploited web servers or edge devices, fake portals
- ExecutionPlugX and HyperBro remote access trojans, custom loaders
- PersistenceRun keys, scheduled tasks, DLL side-loading, web shells
- Command and controlCompromised servers, dynamic DNS, HTTPS
- Defense evasionObfuscation, LOLBins, selective malware activation
Defense Evasion
Defense evasion techniques include:
- Obfuscation and encryption of payloads
- Use of living‑off‑the‑land binaries (LOLBins)
- Avoidance of noisy lateral movement
- Selective activation of malware functionality
Who does APT27 target?
The victimology of APT27 shows that they are very strategic in who they attack.
Primary Sectors:
- Ministries/agencies of Governments
- Defense contractors and Aerospace
- Critical Infrastructure and Energy organizations
- Telecommunications providers
- Technology companies and Research Institutions
Geographic Focus:
- East and Southeast Asia
- Europe
- North America
Targets are typically chosen for their importance to China. This relates to regional security issues, modernization of defense capabilities, or on-going economic initiatives.
What are APT27’s notable operations?
Government and Defense Espionage
APT27 has executed numerous campaigns against government and military systems. The aim is to collect intelligence on how they plan, procure, and ally with one another with respect to Defense. APT27 typically performs long-term dwell times. Their attacks remain undetected for long periods such as months to years.
Critical Infrastructure Intrusions
APT27 has broken into many of the country’s largest providers of Electric, Gas, Telecommunications, and Water. This was presumably to get knowledge of the infrastructure’s resiliency model and their overall Network Topology. It was also presumably to develop their Emergency Response Planning Program.
International Policy and Think Tank Targeting
APT27 has shown a continuous interest in think tanks and policy organizations. These study China’s Foreign Relations, Trade Issues, and Regional Security Dynamics.
Long‑Running Web Shell Campaigns
APT27 has frequently used long-term Web Shells on compromised servers. They give continued access and periodic access to data.
What changed in APT27 activity from 2023 to 2025?
The APT27 actor has changed over the past two years. The change can be called a slow, uneven development. It has recently started to show some signs of greater sophistication.
Some of the recent developments include:
- Utilization of DLL side loading as a method for bypassing modern endpoint protection
- More precision in choosing targets and resulting in fewer but higher-value victims.
- Improved operational security, including faster infrastructure rotation
- Improved operational security measures, including quicker infrastructure rotation.
The same tools overlap with those of the other PRC APT actors. This indicates that they are likely using the same resources and/or working together to develop their tools.
APT27 may not always have been the cutting edge of zero-day exploitation. Still, the group has been effective in its execution of consistently disciplined attacks.
Strategic Impact
The activities of APT27 directly contribute to the overall strategic posture of the Chinese government regarding intelligence gathering.
- Military Advantage: Access to data on military capabilities helps build military capability and run threat assessments.
- Political Insight: Breaking into government communications gives APT27 a view of how foreign governments decide. These decisions cover foreign policy statements and initiatives.
- Economic Benefits: APT27’s ability to steal sensitive technical and industrial data can speed domestic innovation. This has positive benefits on the Chinese economy.
APT27 will continue to persist in its efforts to provide the Chinese government with long-term, sustainable access to intelligence. It does so through APT-based cyber espionage.
Conclusion
APT27 continues to be a serious cyber-espionage threat as of 2025. The cybercriminal group has used steady spear-phishing techniques. It has established reliable malware families. It has also kept a disciplined way of working. With these it has broken into high-value targets on a global scale. The group’s numerous aliases indicate the scope of its activities, as opposed to a fragmentation within the group. They also highlight how long APT27 has been active across multiple industries and regions.
Organizations in the government, military, critical infrastructure, and technology sectors should treat APT27 as an imminent threat. Therefore, government, military, critical infrastructure, and technology organizations should adopt strong email security, continuous monitoring, and a threat-intelligence-driven defense strategy. Geopolitical rivalry is on the rise. So it’s reasonable to presume that APT27 will remain a viable and enduring agent of China’s cyber operations.
You can download and review the sheet for all the details!