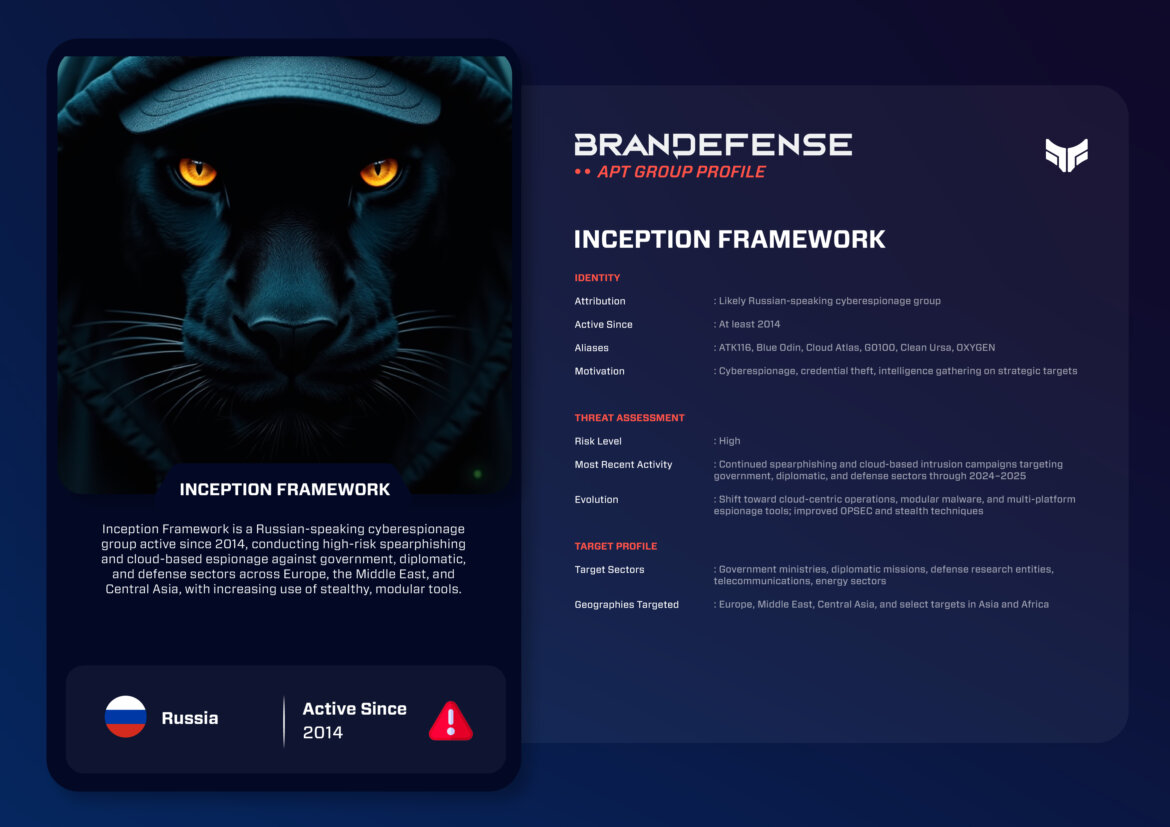
Inception Framework is a cyberespionage group that has been tracked since at least 2014. It is also known as Cloud Atlas and Blue Odin. The group uses targeted spearphishing, modular malware and cloud services to collect intelligence from government, diplomatic, defense and energy networks. Attribution is open to debate.
The past decade has brought fast shifts in global cyberespionage. Actors now use cloud native tools, modular malware, and advanced social engineering. They use them to break into government, diplomatic and high value networks around the world. One actor came to our attention during our ongoing investigations: Inception Framework. It is also known as Blue Odin, Cloud Atlas, Clean Ursa, ATK116, G0100 and OXYGEN. It is arguably one of the most persistent, stealth-focused espionage groups now active.
Inception Framework has been tracked since at least 2014. It has a strong reputation for high operational security (OPSEC) and highly targeted spearphishing. It can also change course fast as technology and tools change. This blog looks at Inception Framework in turn: who it is, what it wants, how it works, what it has done, and how it has changed more recently.
Introduction: A Stealth-Focused Espionage Actor
The Inception Framework surfaced during a time of high geopolitical tension, when states relied heavily on cyber operations. Who is behind it is still open to debate. Still, several reviews by the intelligence community suggest the group is Russian-speaking. They also suggest it works in line with the interests of a state that collects strategic intelligence.
Unlike actors who want money, the Inception Framework wants long-term, steady access to high-value networks. Its main goal is still collecting intelligence. Targets include diplomatic communications, classified government documents and papers that show strategic lines of effort. They also include sensitive research from the defense and energy sectors.
Two things shape how Inception Framework builds its campaigns. One is disciplined spearphishing. The other is scheduled malware staged on cloud services. Its C2 setup also has many layers, so investigators see less.
Who Is Inception Framework and What Motivates It?
Who Is Inception Framework?
Inception Framework is a multi-staged espionage actor. It works under tight OPSEC and uses a modular toolset. Intelligence vendors also call it Cloud Atlas and ATK116. All the names point to the same operational footprint.
- Aliases.
- Blue Odin, Cloud Atlas, Clean Ursa, ATK116, G0100, OXYGEN.
- Tracked since.
- At least 2014.
- Main aim.
- Long-term intelligence collection.
- Targets.
- Government, diplomatic, defense and energy networks.
Core Motivation
• Long-term espionage goals
• Credential harvesting to gain access to critical networks
• Monitoring diplomatic and/or governmental communications
• Intelligence gathering that supports energy, defense intelligence and geopolitical goals
The group always puts stealth, persistence and adaptability first. This makes it hard to detect. Once it slips past detection, it is especially hard to remove from a network.
What Tactics and Tools Does the Group Use?
The group’s techniques have changed a great deal since 2014. They show an organized push toward modular tools and cloud obfuscation.
1. Initial Access: Precision Spearphishing & Cloud Abuse
Framework is known for:
- Highly tailored, targeted spearphishing emails that use geopolitical lures
- Malicious document attachments that use vulnerable Microsoft Office libraries
- Current-enabled OAuth abuse against major cloud providers, such as Google, Azure or O365
- Multi-stage droppers disguised as documents on diplomacy or policy
Their initial access methods take advantage of human trust, policy workflows and cloud integration. This lets them bypass traditional security controls.
Public references line up with this pattern. MITRE ATT&CK lists the group as Inception (G0100), active since at least 2014. It uses spearphishing with weaponized documents that exploit Microsoft Office vulnerabilities. It also uses chains of compromised routers to proxy command and control traffic (MITRE ATT&CK G0100). Palo Alto Networks’ 2014 analysis of the Cloud Atlas and Inception campaigns found that both used weaponized documents. Both also used, to some degree, the CloudMe cloud service for command and control (Palo Alto Networks).
2. Persistence: Long-Term Espionage Footprint
Persistence is a basic part of their approach. Methods used include:
- Modular backdoors with encrypted configuration files.
- WMI-based persistence across Windows hosts
- Registry-based footholds
- Session token theft for long-term cloud access
Together, local persistence and stolen cloud access tokens let the group keep access, even after the victim has reset the credentials that were valid at the time.
3. Command & Control: Cloud-Centric and Obfuscated
Inception continues to use cloud services as both staging and C2 channels:
- Abuse of Dropbox, Google Drive, and OneDrive for payload delivery
- Dynamic DNS cycling to obscure endpoint infrastructure
- Encrypted, low-noise C2 traffic that blends into benign user activity
- Multi-stage payload delivery, to limit attribution
This cloud-centric method makes detection much harder for standard on-premise security products.
4. Malware & Tools: Modular, Encrypted, and Adaptable
Inception has built custom malware families made for stealth and flexibility:
- Encrypted droppers based on documents
- PowerShell reconnaissance frameworks
- Second-stage payloads hosted in the cloud
- Cross-platform implants that target Windows, Linux and mobile devices
Each tool again keeps forensic traces to a minimum and follows OPSEC principles.
Notable Operations: A Timeline of Activity
2014–2016: Initial Discovery
Security researchers link Cloud Atlas operations to European government and diplomatic activity. Early operations used encrypted document droppers and payloads hosted in the cloud
2017–2019: Expansion into Middle East & Central Asia
The group widened its operations. It used spearphishing and cloud C2 to target ministries, foreign ministries and telecommunications service providers
2020–2022: Shift Toward Cloud-Hosted Malware Delivery
As more of the world moved to the cloud, Inception began to use cloud storage services more often to stage second-stage malware. This made it much harder to spot.
2023–2025: Renewed Espionage Surge
The most recent burst of activity involved OAuth hijacking of accounts, improved modular backdoors and even more advanced spearphishing. It targeted defense and national security companies
The group is active across many geopolitical hotspots. That hints at where it may keep a long-term interest, in line with its longer-term collection targets.
- 2014 to 2016Initial discoveryCloud Atlas operations linked to European government and diplomatic activity.
- 2017 to 2019ExpansionMiddle East and Central Asia, with ministries and telecommunications providers targeted.
- 2020 to 2022Cloud-hosted deliveryCloud storage used more often to stage second stage malware.
- 2023 to 2025Renewed surgeOAuth hijacking, improved modular backdoors and spearphishing of defense and national security companies.
How Has the Group Evolved Recently?
The Inception Framework has kept improving its tradecraft in many key areas:
- More advanced spearphishing templates that are attached to real diplomatic events
- More abuse of the cloud ecosystem for staging, C2, and data exfiltration
- More encryption at every stage, which makes reverse engineering hard
- Wider targeting in Africa and the Asia-Pacific region
- Better OPSEC to avoid overlaps in infrastructure with prior campaigns
These changes show a threat actor that has moved a step ahead, both in strategic relevance and in operational stealth.
Conclusion: Strategic Impact & Defensive Recommendations
The Inception Framework represents the next stage of state-sponsored espionage: cloud-first, modular and highly persistent. Its focus on government, diplomatic and national security targets shows the strategic effect it has on the company.
Defensive Takeaways
To defend against the Inception Framework, enterprises should:
- Deploy phishing-resistant MFA and monitor OAuth
- Monitor for anomalous cloud behavior and token hijacking
- Need rigorous logging and alerts on WMI, registry changes, and accessing cloud resources
- Segment sensitive government and diplomatic networks
- Monitor for low-signal, low-noise intrusions with advanced behavioral analytics
- Deploy phishing-resistant MFA and monitor OAuth
- Monitor for anomalous cloud behavior and token hijacking
- Log and alert on WMI, registry changes and access to cloud resources
- Segment sensitive government and diplomatic networks
- Use behavioral analytics to spot low noise intrusions
As the world becomes more digital from a geopolitical view, the Inception Framework and similar groups will remain a major threat. Its wide cloud traffic ability, modular payload delivery and stealthy long-term access put it among the most advanced espionage actors in the world today.
You can download and review the sheet for all the details!