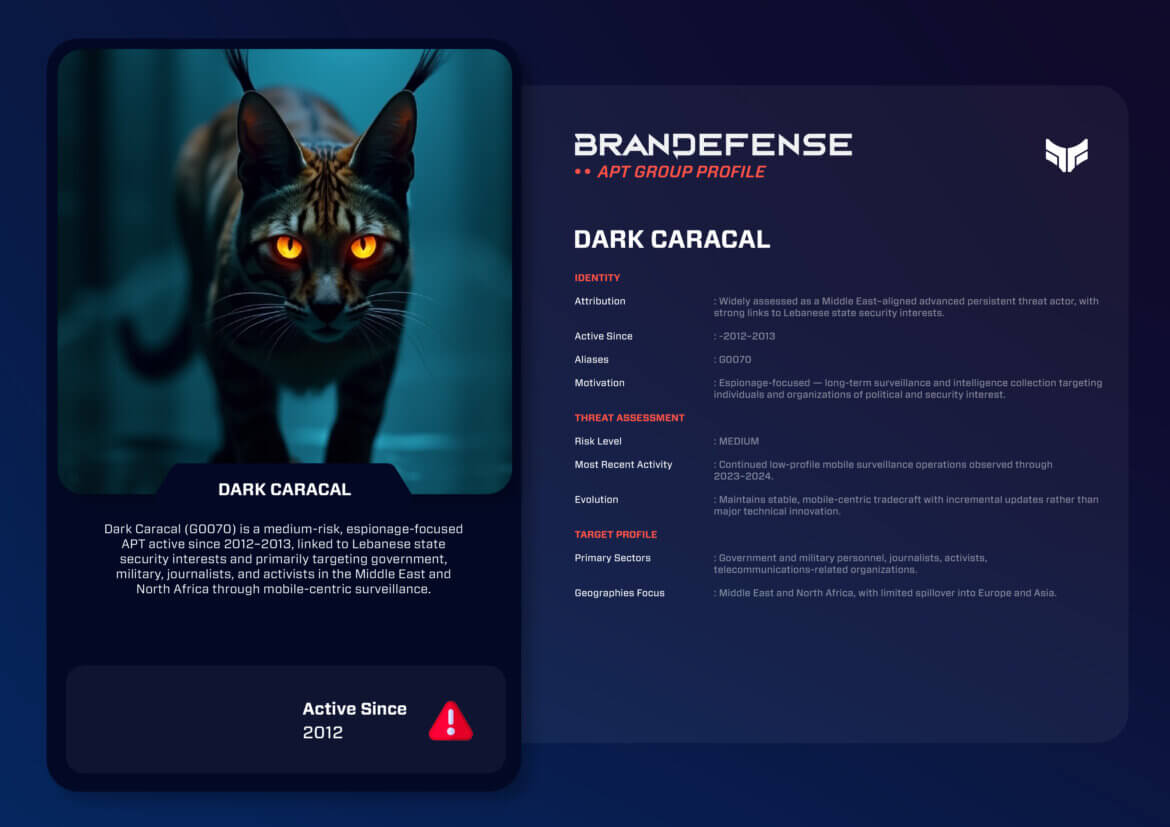
Dark Caracal is an espionage group that spies on people mainly through their phones, especially Android devices. MITRE ATT&CK tracks it as G0070 and its activity is attributed by MITRE ATT&CK to the Lebanese General Directorate of General Security. The group relies on social engineering and fake apps rather than advanced exploits. It targets officials, military staff, journalists and activists, mostly in the Middle East and North Africa.
Introduction
The Dark Caracal group is an unusual advanced persistent threat group. It focuses mainly on long-term intelligence collection through mobile surveillance. Many other APTs target entire networks or firms. Most of Dark Caracal’s operational success relies upon access to devices, most notably Android mobile phones, to monitor people rather than firms. So Dark Caracal is very relevant to talks about digital privacy, targeted surveillance, and the overall security of the mobile ecosystem. The Dark Caracal group is also known by the G0070 identifier. Several sources describe it as a regional espionage entity. Its activity combines traditional cyber espionage with mass digital surveillance campaigns.
Who is behind Dark Caracal?
Dark Caracal is currently seen as a nation-state aligned cyber threat from the Middle East. Its mission is espionage against many kinds of people, including but not limited to government officials and military members. Open-source research and the Trends Internationa l2020 analysis have revealed who is behind Dark Caracal. They link its infrastructure and methods to entities tied to the Lebanese government security services. As such, Dark Caracal is one of only a handful of publicly known APTs linked to that geographic area.
In contrast to most APTs in relation to established cyberpower status, Dark Caracal operates at a very small scale. To make up for this lack of technical expertise, Dark Caracal relies on persistence. It uses fairly simple social engineering to gain access to target systems. It does not depend on advanced malware or zero-day exploits. Dark Caracal has kept succeeding through steady, targeted surveillance. It does not attack its targets with advanced, skilled methods.
- Tracked as.
- G0070 (MITRE ATT&CK).
- Attributed by MITRE ATT&CK to.
- Lebanese General Directorate of General Security.
- Main platform.
- Android mobile devices.
- Also uses.
- Windows malware.
- Main method.
- Social engineering and fake apps.
- Main regions.
- Middle East and North Africa.
Strategic Motivation
Dark Caracal is mainly motivated for the purpose of executing espionage missions. Dark Caracal aims to collect classified or sensitive personal, political, and company data from its targets. These targets are often government officials, military officials, journalists, activists, and people who work in high-risk jobs.
Dark Caracal usually runs highly targeted operations. They aim at set goals within the limits of its resources. Its data collection approach also suggests that it is likely responding to specific domestic and operational intelligence collection directives as part of its mission. Examples of these directives are: monitoring political movements and opposition figures, following domestic and international events through public data, and building awareness of a set area within the Near East.
Tactics, Techniques, and Procedures (TTPs)
Dark Caracal relies on mobile malware and social engineering. It does not use complex exploitation chains to reach its goals.
Initial Access
Dark Caracal often gains its initial access through social engineering campaigns. These trick victims into downloading malicious applications. These Malicious Applications may be Disguised as:
- Messaging/Chat Applications
- VPN/Security Software
- News/Media Applications
- Productivity/Utility Software.
Distribution of these Malicious Applications comes from either Phishing Emails; Phishing SMS; or Direct Messages On Social Networking Sites. In many cases, Dark Caracal has also compromised legitimate websites to serve the payloads of downloadable malicious applications.
- LurePhishing email, SMS or social network message
- Fake appVictim downloads an app disguised as chat, VPN, news or utility
- ExecutionRuns with the permissions granted at install
- CollectionCalls, SMS, contacts, location, audio, photos
- ExfiltrationData sent over HTTP or HTTPS
Execution and Persistence
Once the malicious application is installed, Dark Caracal malware runs with the permissions granted at installation. So it needs no privilege escalation exploit to run.
Today, Dark Caracal combines two kinds of persistence. Icons remain after an app is uninstalled, and background processes recreate themselves after a restart. This makes its malware look like legitimate applications. Dark Caracal uses a simple trojan and a simple remote access tool. This reflects its preference for simplicity and reliability.
Command and Control
Command-and-control (C2) communication often uses standard internet protocols, such as HTTP and HTTPS. Servers are often hosted on compromised infrastructure (for example, cloud hosting providers) and on commercial hosting providers. This group lacks the infrastructure management features of some more advanced groups. It makes up for this by often rotating its servers and keeping spares.
Collection and Surveillance
The group’s greatest strength is its ability to collect data. The spyware that Dark Caracal has created for mobile devices can collect the following data:
– Call and SMS logs
– Contact book
– GPS location data
– Audio recordings made by the microphone
– Photographs, documents and application data
Collecting this type of data from mobile devices lets Dark Caracal run near real-time surveillance of the people it wants to watch. This builds an ongoing record of personal surveillance that goes beyond traditional cyber espionage.
Malware and Tooling
The Android spyware framework developed by a hacker collective known as “Dark Caracal” is considered their top signature. The frameworks of Dark Caracal are very modular. The operator can switch surveillance functions on or off as needed.
Dark Caracal has a second method for espionage in its Windows-based malware arsenal. However, its Windows malware is often less advanced than its Android version. It generally involves credential theft and the exfiltration of data from victims’ systems. Much of Dark Caracal’s tooling is custom-using common open-source parts or well-known frameworks.
Who does Dark Caracal target?
Dark Caracal focuses on people and firms of intelligence interest on a regional basis. In general, the following is a list of Dark Caracal’s main targeting categories:
Primary Targets
– Government officials, public servants
– Military personnel and security personnel
– Journalists and media persons
– Civil society members and activists
– Staff of telecommunication and defense-related firms
Geographic Focus
Dark Caracal’s main targeting areas are:
– Middle East
– North Africa
– Europe and Asia (only those targeting areas that focus on the Middle East)
Victims are selected based on location/relation (not company solely).
Notable Operations
Dark Caracal is linked to many long-term surveillance projects. MITRE ATT&CK dates the group’s activity to at least 2012. Its early mobile espionage used trojanized Android applications, which were mostly distributed through phishing and fake websites. Between 2017 and 2018, Dark Caracal was publicly exposed. It had a major amount of infrastructure and surveillance tools, which had been used to spy on people. These were linked to buildings of the Lebanese government. From 2019 to 2021, they kept up mobile surveillance, now with even more malicious malware variants. They still used mobile malware to target journalists and activists. While they continue to run their operations in a low-profile way (not drawing attention to themselves), they are still doing so with incremental updates to their technical features.
These long-term surveillance efforts show a pattern of consistent operations, rather than greatly escalating operations.
Evolution and Current Activity
After the public exposure, the group carried on with its operations. However, it changed some of its infrastructure and made small improvements in its operational security practices. Many of the original operational practices used by Dark Caracal have not changed. In addition, the main infection vector for the group continues to remain social engineering and user interaction.
These methods keep working for a well-known threat actor. This shows that even well-known threat actors can stay strong if they can keep exploiting human trust and weak user security practices on mobile devices.
Threat Assessment
The threat posed by Dark Caracal is of medium risk but is a severe invasion of personal privacy due to the impact that they can have on the victim’s life. Dark Caracal is not as advanced as major nation states. However, its impact on victims can last a long time. It can include major invasions of privacy, sharing of confidential data, and threats to personal safety.
Any firm, business, or person that works in or is tied to the Middle East should know about Dark Caracal and its ability to run surveillance. This is especially true for people with high political or social visibility.
How can you defend against Dark Caracal?
The way to defend against Dark Caracal is to focus strongly on user education about possible risks to mobile devices due to lack of user knowledge:
– Restricting installing apps from unknown sources
– Implement mobile device management (MDM) and mobile threat defense (MTD) technology
– Educating users about phishing and social engineering
– Monitoring network traffic for suspicious patterns linked to mobile exfiltration of data.
Using only technical controls will not suffice without having human based security measures in place as well.
Conclusion
Dark Caracal shows just how much can be done with targeted surveillance of mobile devices without cyber hardware. The group has run espionage over long periods. It targets specific people, exploits trust, and stays persistent.
Mobile devices matter more every day for daily activities. So the risk linked to Dark Caracal and similar actors will keep growing. Learning about their tactics gives insight into how cyber espionage is changing as the line between digital intrusion and personal security blurs.
You can download and review the sheet for all the details!