The post describes FishMonger as a China-aligned advanced persistent threat (APT) group that carries out cyber espionage. It focuses on long-term, stealthy intelligence collection and mainly targets governments, universities, think tanks and technology companies in Europe, Asia and beyond. It says the group is also tracked under other names, including Earth Lusca and AQUATIC PANDA.
What is FishMonger?
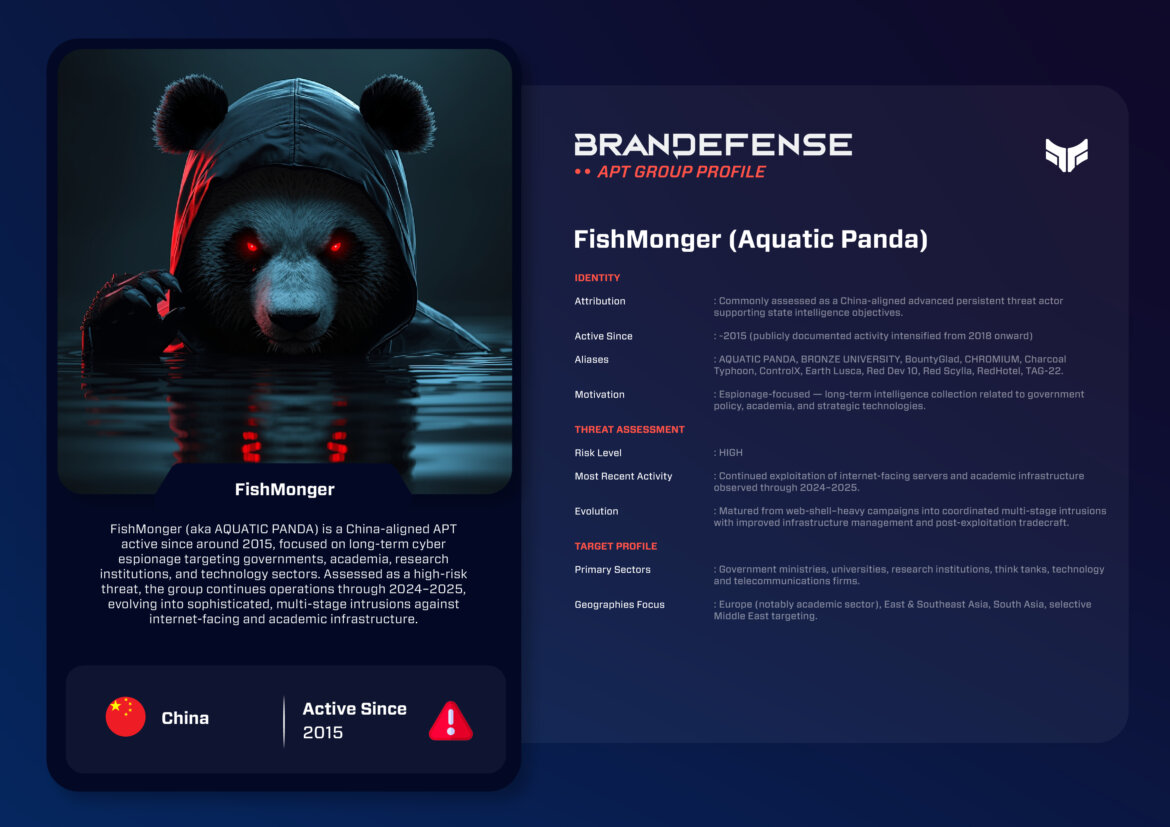
FishMonger is an advanced persistent threat (APT) that has run cyber espionage very well for the last 10 years. It is closely tied to Chinese state-linked cyber operations. It is best known for targeting government bodies, universities, think tanks, and technology companies in Europe, Asia, and beyond.
Its operations have mostly focused on long-term intelligence collection and a stealthy, hidden presence. The goal is to collect intelligence, not to make money or cause direct harm.
The cyber community knows FishMonger under many different names. The group can work at a wide scale, and its tradecraft overlaps with many other China-aligned threat clusters. Some of the names used for FishMonger are:
- BountyGlad
- AQUATIC PANDA
- BRONZE UNIVERSITY
- Charcoal Typhoon
- ControlX
- Earth Lusca
- TAG-22
- RedDev 10
- RedPhenometer
- RedMorph
- RedScylla
- RedHotel
The names vary widely. Analysis of infrastructure, malware, and targeting patterns shows that they share a fair level of likeness. All of them point back to the goal of espionage.
What motivates FishMonger?
The FishMonger group is listed as a Chinese-based advanced persistent threat (APT) actor. It works to support Chinese national strategy and political intelligence efforts. FishMonger’s aim is espionage. It focuses on collecting sensitive political, diplomatic, academic, and technology data.
Sources differ on motive. This post describes espionage as the aim. MITRE ATT&CK, for the group it tracks as Earth Lusca, says some operations may be financially motivated. The post says FishMonger values long-term access and the collection of data with high intelligence value.
Victim choice often matches China’s national foreign policy interests. These include new technology and geopolitical events discussed within China and across East Asia. Public and private universities, research institutions, and policy think tanks all have high intelligence value. They help shape the debate on strategic issues and new technologies.
Tactics, Techniques, and Procedures (TTPs)
In its operations, FishMonger is known for a mix of custom tooling, exploitation of publicly known vulnerabilities, and strict operational security. FishMonger does not always exploit a “zero-day” vulnerability.
It is very skilled at taking newly disclosed vulnerabilities and weaponizing them. It then chains the exploits together with a custom “post-exploitation” toolbox.
Initial Access
The usual way to get initial access to a target is to exploit servers and applications that are reachable over the internet. The FishMonger group has used Web Server application packages, application frameworks, and VPNs after patches were released.
Along with these vulnerabilities, the group also ran targeted spear phishing campaigns. The targets were people who work in academia or on policy-focused work. The group used documents that looked harmless or links that looked benign to lure its victims.
Execution and Persistence
When the FishMonger group gains access to a company’s network, it deploys its own loaders and backdoors to set up and keep a presence. It builds its own persistence methods using Scheduled Windows Tasks. It also installs Services or Web Shells on compromised servers.
It uses Living Off the Land techniques, which means using legitimate system utilities for malicious ends. This way, its activity blends in with regular admin activity.
Command and Control
The C2 Infrastructure used by the FishMonger group often uses HTTP/S protocols to connect to the attacker’s servers. The domain names that serve the infrastructure are often registered to look like legitimate academic bodies, cloud service providers, or technology companies. This helps lower the chance of detection.
The group changes its infrastructure often, and compromised servers are the source for follow-on staging operations.
Collection and Exfiltration
Data Collection means taking documents, e-mails, credentials, and research data that relate to the Strategic Value of the victim’s company. Data exfiltration is usually done in small, staged transfers. This avoids setting off Data Loss Prevention (DLP) and other monitoring controls that the victim has in place.
FishMonger’s operations are built to be as quiet as possible, to serve a long-term espionage goal.
- Initial accessExploits internet-facing servers, VPNs and applications, or sends spear phishingTechnique T1190 (MITRE ATT&CK, opens in a new tab)
- FootholdDeploys loaders, backdoors and web shells; uses scheduled tasks and servicesTechnique T1505.003 (MITRE ATT&CK, opens in a new tab)
- Command and controlConnects to attacker servers over HTTP/S using look-alike domains
- Collection and exfiltrationGathers documents, e-mails and credentials, then sends them out in small staged transfers
Malware and Tooling
The FishMonger group uses a wide range of malware and tooling. It ranges from bespoke backdoors to web shells and, in some cases, modified open-source toolkits. FishMonger’s skill at adapting its tooling to the target’s environment is one of the group’s most defining traits.
FishMonger often uses web shells as part of its tactics, techniques, and procedures. It uses them when targeting universities and publicly available research portals. Web shells are an efficient way for attackers to keep access with a very small footprint. They also enable lateral movement and data staging inside the target company.
FishMonger also uses modular backdoor malware built for endpoint environments. It can run commands, change files, and collect credentials, which keeps the group operational.
Who does FishMonger target?
FishMonger picks targets mainly for their intelligence value, rather than for their immediate impact on operations.
Primary Targets
- Government ministries and diplomatic institutions
- Universities and academic research centers
- Think tanks and policy research organizations
- Technology and telecommunications companies
Geographic Focus
FishMonger operates on a global scale, with strong concentrations of activity in:
– Europe (particularly Central/Western Europe)
– East/Southeast Asia
– South Asia
– Selected Middle Eastern targets
Historically, European academic institutions have been prominent targets for FishMonger. The likely reason is their role in supporting advanced research and international cooperation. They also advise on policymaking decisions.
Notable Operations
FishMonger has run many highly skilled espionage campaigns during its existence. The following is an overview of FishMonger history in its espionage activity:
- From 2019 (MITRE ATT&CK dates Earth Lusca to at least April 2019): Early campaigns targeted European universities and foreign policy agencies. They exploited insecure web servers and used web shells.
- 2020: A marked increase in targeting of government-linked research organizations and public health organizations, in step with worldwide geopolitical events and the start of COVID-19.
- 2021–2022: More focus on technology and telecommunications organizations, through improved post-exploitation tooling and better organization of compromised tools and infrastructure.
- 2023–2024: Continued exploitation of edge devices and enterprise applications, and a continuing focus on universities and organizations with an emphasis on public policy.
These campaigns give ample evidence of the FishMonger Group’s ability to keep consistent and adaptive strategies.
Recent Developments and Evolution
Over time, FishMonger has improved its operational discipline. Most importantly, its basic techniques have not changed. Still, better infrastructure hygiene, malware obfuscation, and victim-specific customization point to a more mature operation than before.
FishMonger appears to work with other actors across the China-nexus cyber ecosystem. Overlap of tooling and infrastructure with other clusters points to more operational cooperation.
FishMonger’s ability to exploit recently patched vulnerabilities shows a trend among many advanced threat actors. An advanced threat actor can weaponize a vulnerability fast and at scale. Combined with good reconnaissance and targeting, this can outweigh the need for a zero-day exploit.
Threat Assessment
Organizations involved with government policy, advanced research, and strategic technology development face a very high risk of espionage attacks by FishMonger. FishMonger’s campaigns are highly stealthy, extremely persistent, and built to meet the long-term intelligence needs of its sponsors.
FishMonger does not usually carry out destructive attacks or ransomware. Even so, the strategic impact of its espionage can be extremely damaging.
The loss of sensitive research and projects, policy documents, or diplomatic communications can have long-term national security and economic effects.
How can organizations defend against this threat?
Organizations who want to reduce the risk posed by FishMonger may want to focus on:
1) Quickly patching Internet-Facing systems
2) Monitoring for web shell activity or other anomalies tied to Administrative privileges
3) Setting up strong Network Segmentation and Least Privilege Access controls
4) Using Threat Intelligence (TI) to improve detection of adversaries who use Tactics, Techniques and Procedures (TTPs) tied to China.
For Academic and Research Institutions that work through Open Collaboration Models, it is extremely important to balance Open Collaboration with Security Controls.
Conclusion
FishMonger is an example of how Modern State-Sponsored Espionage Threats have become patient, Adaptive, and Strategically focused. FishMonger has run intelligence collection operations well for many years. Three things explain this: disciplined exploitation of vulnerabilities, flexible tooling that adapts to its goals, and careful target selection.
Geopolitical rivalries are reaching into cyberspace, so we need to accept that FishMonger will remain an active and relevant threat actor. Organizations that want to protect state secrets and withstand constant espionage campaigns must learn about FishMonger’s attack methods and motives. They must also learn which types of victims it selected.
Download the FishMonger APT group fact sheet (PDF) for all the details!