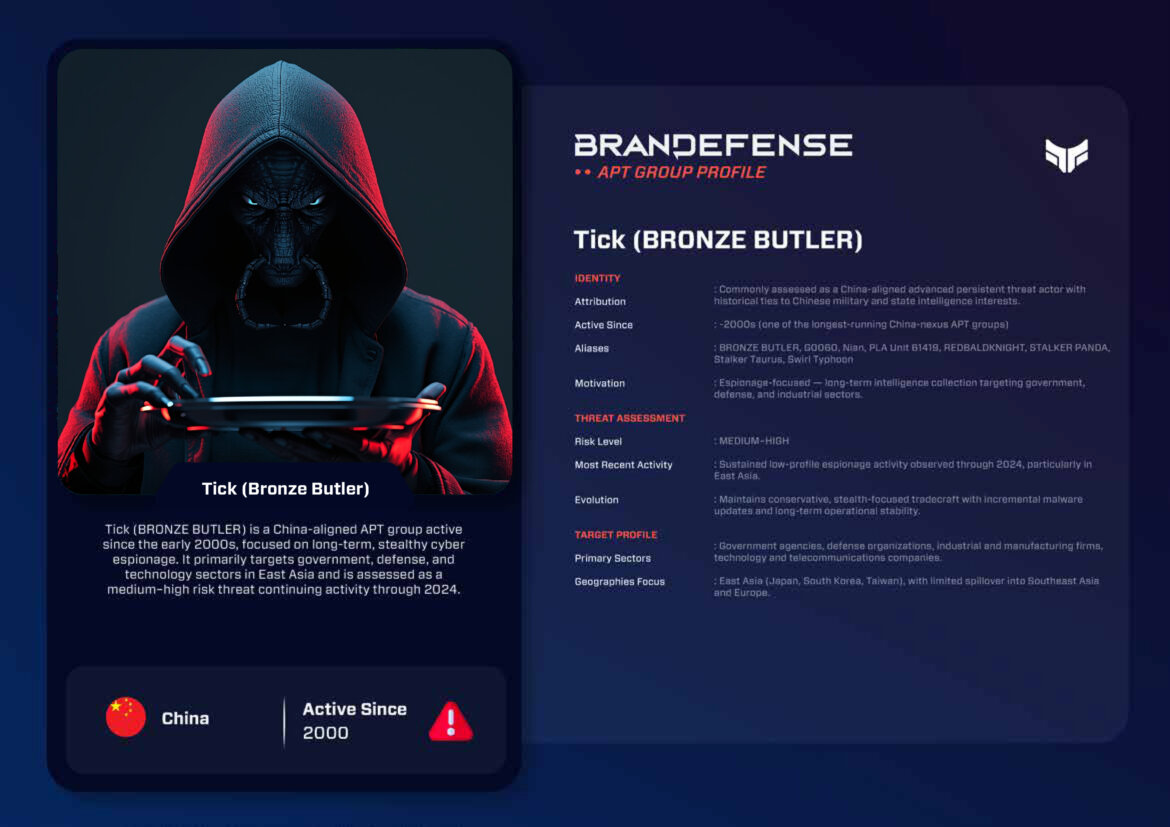
The Tick APT group, also tracked as BRONZE BUTLER, is a cyber espionage actor that MITRE ATT&CK describes as having likely Chinese origins. It has been active since at least 2008, according to MITRE, and has mainly targeted Japanese government, biotechnology, electronics manufacturing and industrial chemistry organizations. It relies on spearphishing and quiet, long-term access to collect sensitive information.
What is the Tick APT group?
The Tick group has been one of the noteworthy long-term Advanced Persistent Threat (APT) actors associated with East Asia’s cyber-espionage activity. It has continued to operate in a persistent and disciplined way. Its main goal is gathering intelligence rather than carrying out large-scale attacks.
Tick does not make headlines for attacks that seriously damage critical infrastructure. However, its prolonged and stealthy nature makes it an important threat. This is especially true for businesses and individuals in or linked to the East Asian region.
Tick has had multiple names, including BRONZE BUTLER, Nian and PLA Unit 61419, as well as REDBALDKNIGHT, STALKER PANDA, Stalker Taurus and Swirl Typhoon. Many of these names reflect parallel tracking by different research organizations and intelligence agencies. They have observed similar infrastructure, malware and targeting patterns for many years.
Who is Tick linked to?
Tick is best assessed as an advanced persistent threat (APT) actor in China, primarily focused on regional espionage. Historically, several reports have linked Tick to specific Chinese military intelligence interests, including the People’s Liberation Army (PLA) Unit 61419. Current assessments tend to be more general. They place Tick as part of a broader landscape of cyber espionage connected to China.
Some newer APT groups evolve their tools rapidly. Tick has instead improved its abilities and tools slowly and step by step, which led to operational stability. This cautious approach has let Tick stay active and operationally capable. It also avoids the attention that more aggressive or experimental tool use may bring from authorities.
Strategic Motivation
The motivation for Tick’s activity is primarily espionage. Tick conducts operations to gain access to sensitive political, diplomatic, military and industrial information. Many APT groups seek to profit from the information they gain, by monetizing access or deploying ransomware. Tick’s primary focus is different. It aims to sustain persistent access to the highest value networks and extract information without detection over long periods.
Analysis of Tick’s target selection indicates a significant interest in national strategic planning, defense research and development, and the industrial capabilities of East Asia. Tick’s campaigns are also usually aligned with the current geopolitical and security dynamics of the Asia region. This indicates that Tick is likely either directed by the Chinese government or supported by governmental agencies.
Tactics, Techniques, and Procedures (TTPs)
The Tick Group’s tradecraft rests on three patterns of operation: patience, low noise and deliberately selected targets. The group combines a strong Operational Pattern Level (OPL) with moderately advanced technical and operational methods.
Initial Access
Initial Access for the Tick Group generally comes from spear phishing campaigns that target specific companies or people. The email contains a link or an attachment designed to look like a legitimate government or business document. In some instances, the group has also exploited known vulnerabilities in unpatched, publicly available systems (internet-facing servers).
Execution and Persistence
After the Tick Group obtains a foothold in a target’s environment, it uses custom malware loaders and backdoor programs. They were created to provide a long-term presence. Persistence is achieved by manipulating the Registry, establishing Scheduled Task entries and adding malicious Service entries. The group chooses to compromise environments that favor stability over speed. As a result, access stays intact even if the system is rebooted or partially recovered.
Command and Control
The Tick Group’s command-and-control infrastructure uses HTTP or HTTPS to conceal malicious traffic within normal web activity on the internet. Domains and servers for C2 are chosen deliberately to blend in with other benign domains. Infrastructure from different campaigns is often reused, with only small changes to the original C2 infrastructure.
The Tick Group shows a great deal of discipline in how it manages its infrastructure. While it runs multiple campaigns, it does not reuse the same infrastructure within one campaign any more than it must. This limits the possibility of easy attribution or takedown of a campaign.
Lateral Movement and Collection
When Tick moves laterally in a compromised environment, it moves selectively. It only goes to systems that are most likely to hold sensitive documents or stored credentials. The group is extremely careful not to gather credentials and perform network reconnaissance too frequently, because it wants to reduce the risk of detection.
The internal documents it typically collects are internal reports, emails, technical documents and strategic planning materials.
- Spear phishing emailLink or attachment posing as a government or business document.
- FootholdCustom loaders and backdoors are installed.
- PersistenceRegistry, scheduled task and service entries keep access after a reboot.
- Selective movementOnly systems likely to hold documents or credentials are visited.
- CollectionInternal reports, emails, technical documents and planning materials.
- Command and controlHTTP or HTTPS traffic blends in with normal web activity.
Malware and Tooling
The Tick Group has been associated with numerous families of custom malware that it has developed and maintained for a long time. Most of its tools are relatively small and modular. They focus primarily on stealth and avoiding detection rather than on advanced functionality. The group constantly updates its tools to work with modern operating systems and security controls. However, the updates are evolutionary rather than revolutionary.
Reliability is probably one of the most defining features of the Tick Group’s tools. The malware is designed to run for extended periods without crashing or drawing attention. This supports the group’s long-term espionage activity.
Who does Tick target?
Tick’s targets emphasize a localized and targeted selection strategy.
Primary Targets
- Government agencies and public administration bodies
- Defense and military-related organizations
- Industrial and manufacturing companies
- Technology and telecommunications firms
Geographic Focus
- East Asia (Japan, South Korea, Taiwan)
- China-adjacent regions
- Some Southeast Asia and Europe-targeting shopping assignments with connections to East Asia
Historically speaking, Japan has been one of Tick’s most traditional targeting sources. This shows Tick’s focus on intelligence in this region.
Notable Operations
Over its long operational history, Tick has been linked to numerous sustained espionage campaigns:
- At least 2008 to 2010 (MITRE ATT&CK dates activity to at least 2008): Early campaigns in Japan focused on Japanese Government, Industrial Targets established a consistent long term presence.
- 2011–2015: Target set geographically expanded further beyond E. Asian countries. Malware has been improved upon during that time with respect to (stability/persistent that is improved).
- 2016–2019: Conduct was activity below radar, mainly focused on military/defense intelligence. Conduct has been maintained with attention off to dating incidents with reports.
- 2020–2024: Targeted espionage events Seem to be ongoing using new equipment, still conducting using stealth methodology.
These campaigns show consistent capabilities and no noteworthy changes.
Recent Developments and Evolution
Recently, Tick has continued to update its malware by adapting it to work with newer operating systems and security frameworks. Other groups have begun to use aggressive tactics against victims. Tick has stayed with its current methods of operation.
Tick’s sustained activity may be due to its ability to avoid creating excessive alerts. It also limits the amount of malware it uses, which reduces the chances of getting caught.
Threat Assessment
Tick is considered a medium- to high-level espionage threat. It affects organizations in East Asia and organizations that work with East Asia on security or industrial development. Some other threat-actor groups create a high degree of technical novelty. Tick instead relies on discipline and patience to maintain a long-term relationship with its target.
Organizations affected by Tick may not detect the effect of a breach immediately. Over a long period, they may discover that they have lost the ability to track sensitive data.
- Also known as.
- BRONZE BUTLER, Nian, REDBALDKNIGHT, STALKER PANDA, Swirl Typhoon.
- Origin.
- Likely Chinese origins, according to MITRE ATT&CK.
- Active since.
- At least 2008, according to MITRE ATT&CK.
- Main goal.
- Espionage, not profit.
- Targets.
- Government, defense, industry, technology and telecommunications.
- Region.
- East Asia, with Japan the most traditional target.
- Threat level.
- Medium to high.
How can organizations defend against Tick?
Dealing with Tick means preparing for long-term threat detection, not only reactive incident response. To protect themselves against Tick, organizations should focus on the following:
- Strong awareness and controls around spear phishing attempts through email.
- Continuous monitoring for long-term intrusions that occur at low frequency.
- Regular review of outbound network traffic pattern monitoring.
- Strong internet-facing patch maintenance (permanent maintenance of all internet-facing applications).
Any organization in or near Japan that believes it may be targeted by Tick should plan its defenses with Tick’s ongoing interest in mind.
Conclusion
Tick is an excellent example of a mature and disciplined espionage actor. It relies on patience and consistency rather than flashy technology. Its long-term track record shows how incremental improvements can support long-term intelligence collection through strict confidentiality.
Geopolitical competition within Asia continues to develop. Tick will most likely remain an active and significant threat to all nations operating in its area of interest. A thorough understanding of how Tick conducts its operations will help teams see how it works. It will also help them become aware of and reduce the risks of these operations over a long period.
You can download and review the sheet for all the details!