HAFNIUM is a China-aligned cyber espionage group, also tracked as Silk Typhoon. It is best known for exploiting Microsoft Exchange Server vulnerabilities in 2021, which led to the compromise of thousands of servers worldwide. The group targets internet-facing servers to collect email and other intelligence. In a CISA alert, the U.S. Government attributed the Exchange activity to actors affiliated with China’s Ministry of State Security.
One of the Exchange flaws from that period has its own page: ProxyLogon (CVE-2021-26855).
HAFNIUM (worldwide assessment: China-aligned cyber espionage) is one of the most impactful APT groups of the past 10 years. It has played a significant role in many of the largest exploitation campaigns ever seen against enterprise architectures. The group became known for its global exploitation of Microsoft Exchange Server vulnerabilities (2021). This changed how many defenders think about the risks of internet-facing enterprise applications.
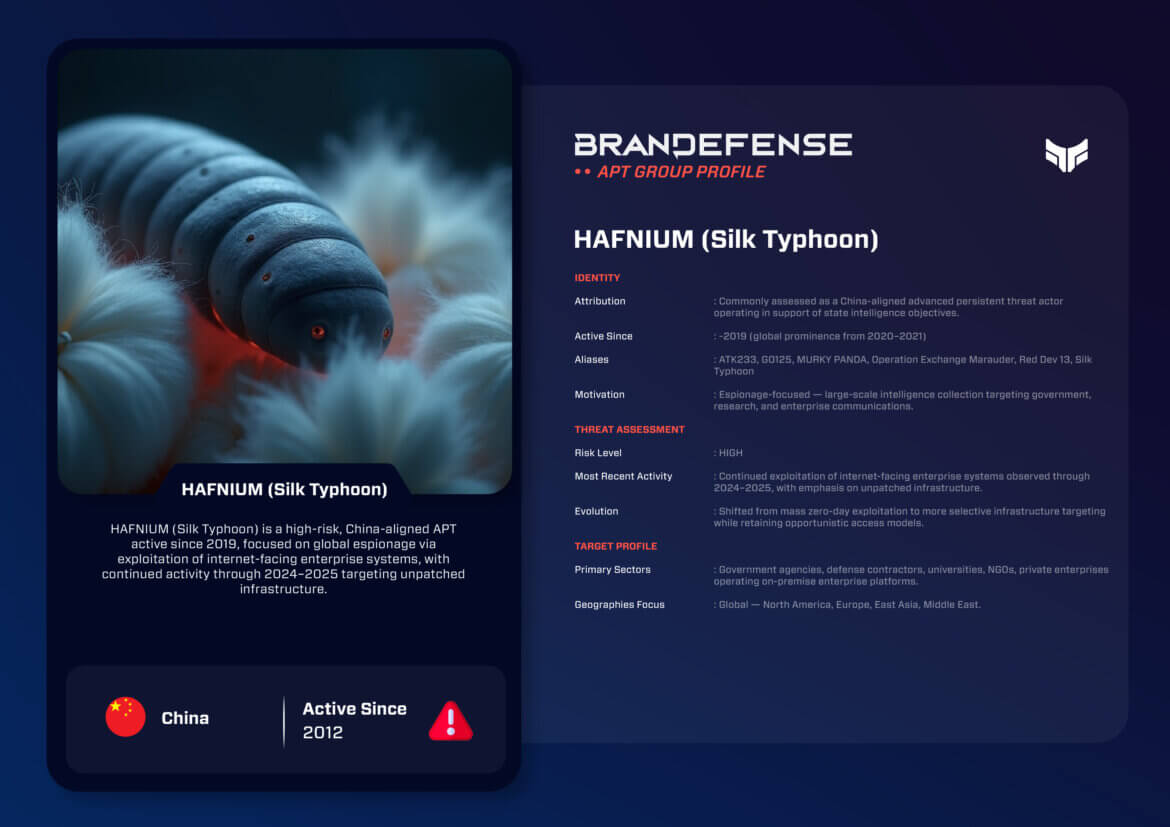
HAFNIUM has been tracked under multiple names (e.g., ATK233, G0125, MURKY PANDA, Operation Exchange Marauder, Red Dev 13, and Silk Typhoon). It is regarded as a China-aligned cyber espionage actor. Its operations focus on collecting strategic intelligence. It exploits large numbers of target organizations (thousands) through scale, speed, and opportunistic methods.
Who is HAFNIUM and who is behind it?
It is widely believed that HAFNIUM is a Chinese state-sponsored cyber operation. Many governments have publicly attributed HAFNIUM’s activities to intelligence collection that meets Chinese intelligence requirements. These requirements relate in particular to foreign policy, technology acquisition and strategic awareness.
HAFNIUM stands apart from other APT groups in two ways. It aggressively exploits server-side vulnerabilities, and its espionage goals give it a larger reach. Its campaigns have blurred the line between typical targeted APT operations and large-scale intrusions.
- Also tracked as
- ATK233, G0125, MURKY PANDA, Operation Exchange Marauder, Red Dev 13, Silk Typhoon
- Assessment
- China-aligned cyber espionage actor
- Main goal
- Collecting strategic intelligence
- Best known for
- Exchange Server vulnerabilities, 2021
- Typical way in
- Internet-facing servers
What does HAFNIUM want?
Unlike many cyber adversaries who have combat as their primary motivation, HAFNIUM exists to gather intelligence. HAFNIUM is interested in gathering sensitive communications, intellectual property and strategic information from victims in government, academic institutions, not-for-profit and commercial enterprises.
HAFNIUM uses internet-exposed infrastructure. This gives it more opportunity to collect intelligence from a broad audience at the same time. This way of gathering data also fits state intelligence goals well. Those goals stress breadth of access, long-term data collection and opportunistic exploitation of global digital dependencies.
Tactics, Techniques, and Procedures (TTPs)
HAFNIUM’s tradecraft is built on opportunism and practicality. It does not rely on complex social engineering. Instead, the group prefers to work within existing infrastructure and target weak areas in it to gain access.
Initial Access
HAFNIUM is defined by its targeting of vulnerabilities in internet-facing servers as a source of initial access. It is known for exploiting multiple zero-day vulnerabilities in Microsoft Exchange Server in a chain. The chain allows remote code execution, authentication bypasses, and arbitrary writes to the file system within Exchange.
Most of HAFNIUM’s operations focus on Exchange servers. The group still shows interest in other platforms and enterprise services, especially those with a large footprint and a longer patching cycle. This lets HAFNIUM scale its access quickly with little direct interaction from end-users.
Execution and Persistence
Once it has access, the HAFNIUM team usually uses web shells to keep persistent access to a compromised server. A web shell is a lightweight way to run commands, change files, and deliver further payloads. It uses as little space and as few server resources as possible.
The group leaves multiple web shells in different directories. This gives it persistent access and resilience against partial remediation of a compromised server. HAFNIUM prefers redundant but functional persistence mechanisms over more complex ones.
Command and Control
HAFNIUM often uses compromised servers to build its Command & Control (C2) infrastructure. Traffic is routed through these intermediary systems over HTTP/HTTPS. This hides malicious traffic among legitimate internet traffic.
HAFNIUM has also used cloud-based C2 and dynamically registered domains to help manage their operations and reduce the likelihood of quickly being eradicated.
Lateral Movement and Collection
While HAFNIUM has broad-based access through exploitation, their activities post-exploitation are more targeted. To identify high-value resources such as inboxes, document stores and credential repositories.
HAFNIUM uses opportunities for lateral movement through the use of stolen credentials, or using legitimate administrative functionality. Their data collection usually consists of emails, attachments, contacts, internal documents and other items of strategic intelligence value.
- Exploit an internet-facing serverOften a Microsoft Exchange Server flawTechnique T1190 (MITRE ATT&CK, opens in a new tab)
- Drop web shellsKeep access across directoriesTechnique T1505.003 (MITRE ATT&CK, opens in a new tab)
- Run command and controlCompromised servers hide traffic in HTTP and HTTPS
- Move sidewaysStolen credentials or legitimate admin tools
- Collect dataEmails, attachments, contacts and documentsTechnique T1114.002 (MITRE ATT&CK, opens in a new tab)
Malware and Tooling
HAFNIUM does not have a significant amount of custom malware. Instead, they utilize:
- Web shells to maintain connections.
- Native Operating System tools to execute commands.
- Basic loaders or scripts to collect data.
The reduced number of tools limits development costs and helps mitigate detection through signature based defenses. The success of HAFNIUM shows that the achievement of sophisticated result does not necessarily require the sophisticated use of malware.
Who does HAFNIUM target?
HAFNIUM’s set of possible targets is much broader than what we usually see from an APT group. This points to a focus on infrastructure.
Primary Targets
- Government agencies
- Contractors that support the US physical or cyber defense sector & National Security focused think tanks or research groups
- Research and educations institutions (universities, institutes of technology/development)
- Non-profit organizations that support technology or research initiatives
- Businesses across different markets/industries
Geographic Focus
HAFNIUM’s operations have affected many organizations around the world: North America, Europe, East Asia, & the Middle East.
The scope of these operations was clearest in HAFNIUM’s exploitation of Microsoft Exchange. Tens of thousands of Microsoft Exchange servers worldwide were exploited.
Notable Operations
HAFNIUM has been involved in multiple significant Operations:
- 2020–2021: Microsoft Exchange exploitation of multiple zero-day vulnerabilities in Microsoft Exchange Server, which resulted in mass compromise of thousands of on-premise Microsoft Exchange servers worldwide.
- 2021–2022: Ongoing exploitation of unpatched Microsoft Exchange servers, along with any ‘copy-cat’ actors performing follow on intrusions/attacks against HAFNIUM introduced vulnerabilities to Microsoft Exchange Software.
- 2023–2024: Cyber-activity targeting internet connected (Ip) infrastructure (Data Centers/repositories). The activity continues, although less so than a previous operation, at a significantly reduced operational tempo versus 2020/2021.
HAFNIUM’s operations in these periods changed how industries view supply-side risk. They also raised the urgency of patch management for business operations.
Evolution and Current Activity
HAFNIUM went through severe public exposure and strategic remediation, making their activity less visible but not completely inactive. The group has transitioned to diversifying their infrastructure targets and decreasing their reliance on one specific vulnerability cluster.
Several other China-aligned threat actors have used HAFNIUM’s tooling, techniques, and lessons from earlier campaigns. This has magnified their impact on the threat landscape over the long term.
Threat Assessment
Organizations that use public-facing enterprise software face a high espionage risk from HAFNIUM. The group’s campaigns show how quickly vulnerabilities in those systems can be exploited at scale. The result is systemic risk across multiple sectors and geographies.
Most organizations, regardless of whether they have been directly targeted as strategically valuable, will still experience opportunistic compromise and be subject to downstream intelligence exploitation.
How can organizations defend against HAFNIUM?
Defending against actors similar to HAFNIUM requires a new way of thinking about defensive strategies:
- Focus on rapid patching of public-facing systems
- Monitor for indicators of web-shells and anomalous behavior on the web servers
- Assume that compromise will occur while vulnerabilities are being disclosed
- Utilize comprehensive defense-in-depth controls for email and identity systems
Traditional user-focused security controls will not adequately protect organizations that are vulnerable to exploitation of their server-side vulnerabilities at scale.
Conclusion
In summary, HAFNIUM shows how state-sponsored cyber espionage has evolved. It has moved from a nation-state focus to include cybercriminal affiliates who use the same vulnerabilities for similar operations worldwide. HAFNIUM’s techniques exploit massive vulnerabilities at high speed and with high opportunism. They show how one set of mass-scale vulnerabilities can enable mass-scale collection of intelligence and data.
Organizations rely more and more on complex, public-facing technologies. The lessons from HAFNIUM will therefore stay highly relevant. Understanding and preparing for HAFNIUM’s methods will protect against this group. It will also help prepare for the next generation of cyber espionage aimed at infrastructure.
You can download and review the sheet for all the details!