APT19 is a China-aligned threat group that has run cyber espionage for over a decade. The post lists Deep Panda as an alias, but MITRE ATT&CK says it is unclear from open sources whether the two are the same group. APT19 steals credentials at scale and targets government, technology, telecommunications and defense organizations.
For a source-checked summary of what MITRE ATT&CK records about this group, see our APT19 threat group profile. Other China-linked groups with profiles are APT41 and APT40.
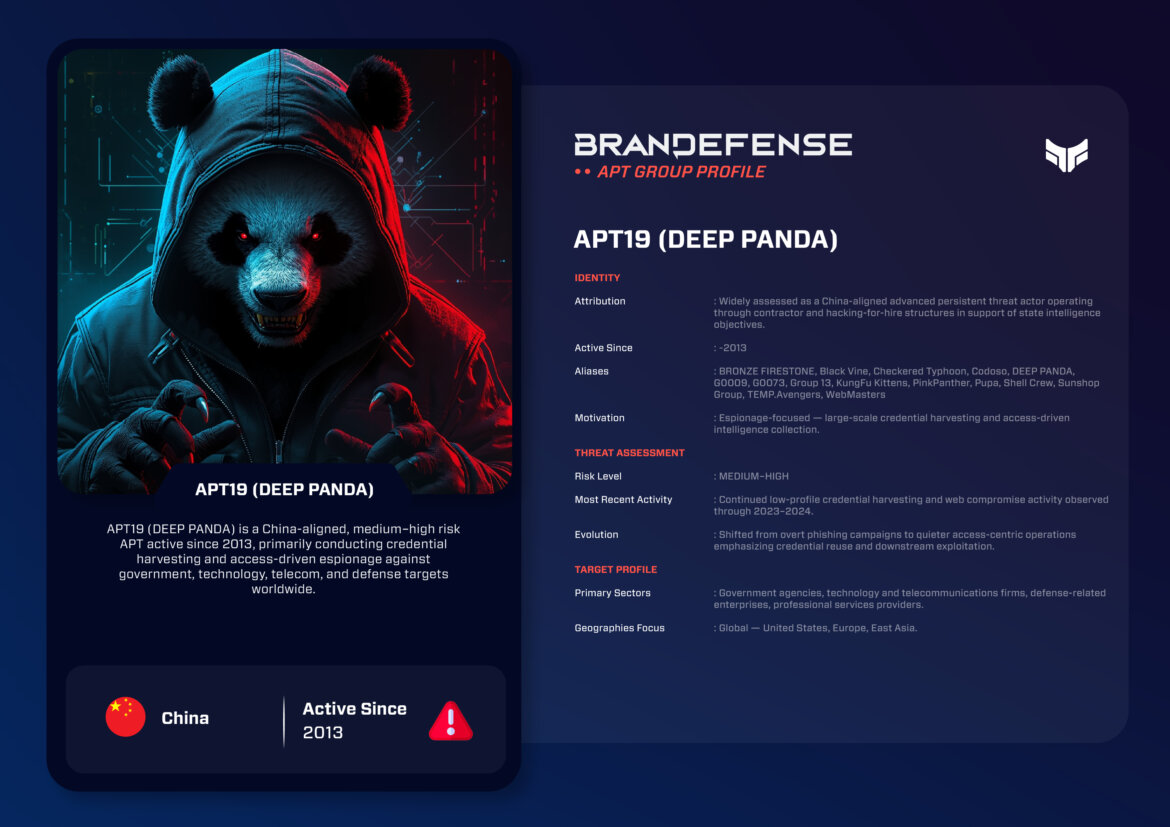
APT19 is an advanced persistent threat (APT) group that has engaged in sustained cyber espionage operations for over a decade. It has also operated many large-scale credential harvesting campaigns. This group has a unique place within the Chinese-nexus cyber threat landscape. It uses traditional state-assisted intelligence gathering methods as well as cybercrime-type methods, such as the mass harvesting of credentials and access brokers.
APT19 operates under multiple aliases. This proliferation of names reflects its wide operational scope and overlaps in activity clusters among groups. Its aliases include, but are not limited to:
- BRONZE FIRESTONE
- Black Vine
- Checkered Typhoon
- Codoso
- DEEP PANDA (also known as G0009)
- G0073
- Group 13
- KungFu Kittens
- PinkPanther
- Pupa
- Shell Crew
- Sunshop Group
- TEMP.Avengers
- WebMasters
Despite the many names, consistent patterns of infrastructure, malware, and victimology show that this is the same entity acting in a coherent way.
- Also known as
- Codoso, Sunshop Group, Black Vine, BRONZE FIRESTONE, Checkered Typhoon
- Active
- Over a decade
- Main method
- Spear-phishing, compromised web servers, credential theft
- Targets
- Government, technology and telecommunications, defense, professional services
Who is behind APT19?
The APT19 threat group is understood to have been established to support the nation’s intelligence efforts in China. Many of their members are reportedly Chinese citizens with hacking-for-profit skills who act like contractors or businesses. They take part in espionage fully aligned with Chinese government needs. Many also report on their work to one or more of the associated contractors. This creates a dual-use capability, meaning a means in addition to collecting intelligence.
Understanding APT19 as a hybrid structure explains why it is so willing to run wide-ranging and often opportunistic campaigns. These campaigns gather large amounts of credentials, which can later be filtered for intelligence value.
Strategic Motivation
Strategically, APT19’s primary motive is to acquire information of all types that has political, economic, or technological significance. In contrast to traditional state-sponsored espionage, APT19 has shown a clear interest in acquiring large quantities of credentials. These large numbers of credentials let APT19 access various corporate, cloud, and personal accounts. APT19 can keep access and gather intelligence long after the initial compromise.
APT19 chooses its targets based on perceived intelligence value. It also compromises service providers or managed services to reach multiple lower-tier victims. This access-oriented targeting fits the central tasks of Chinese intelligence prioritization. These tasks call for situational awareness and long-term access.
How does APT19 attack its victims?
APT19 has combined phishing, website compromise, and credential harvesting with disciplined operational persistence as their tradecraft.
Initial Access
Typically, APT19 will obtain initial access via spear-phishing campaigns containing malicious attachments or links. Spear-phishing emails may appear as valid business communications, conference invitations or as security alerts. Initial access has also been obtained through compromised web servers and content management systems (CMS) by deploying web shells. This lets APT19 keep access to the compromised hosting environment.
Execution and Persistence
After gaining initial access, APT19 obtains and deploys lightweight backdoors and web shells to establish and maintain persistence. Persistence mechanisms include registry changes and scheduled tasks on endpoint systems. Web shells on compromised servers provide long-term access without detection and survive partial remediation efforts.
Credential Harvesting
APT19’s operations represent a pattern for the theft of credentials from its victims. The group utilizes:
– Keyloggers – Browser credential dumping
– Phishing websites using compromised infrastructure
APT19 often reuses credentials stolen from one platform on multiple application platforms which allows for lateral movement into email, VPN and other cloud-based services.
Command and Control
APT19 uses HTTP/HTTPS-based C2 channels for its operations. Command and control infrastructure is frequently reset. Domain names are designed to look legitimate and often pose as established businesses or technology service providers. The use of compromised servers as relay nodes for both inbound and outbound command-and-control communications has made determining attribution extremely difficult.
- Spear-phishingEmail with a malicious attachment or link
- Web shellsAccess through compromised web servers and CMS
- PersistenceBackdoors, registry changes and scheduled tasks
- Credential theftKeyloggers, browser dumping, phishing sites
- Command and controlHTTP/HTTPS channels and relay servers
Malware and Tooling
APT19 is a threat group that uses many tools and malware families. It focuses on credential theft and keeping access rather than sophisticated exploitation. Among these are custom backdoors, web shells and credential harvesting utilities. The APT19 group develops its own tools as well as tailoring public tools to remain undetected and integrate seamlessly into their operational workflow.
Instead of focusing on zero-day exploits, APT19 prefers to use tried-and-true methods that are deployable across a variety of environments repeatedly.
Who does APT19 target?
APT19’s targets reflect both strategic intelligence objectives and opportunistic access to obtain intelligence information.
Primary Targets
– Government Agencies/Public Sector
– Companies in Technology/Telecommunications
– Companies in the Defense Industry
– Consultants/Professional Services
Geographic Focus
APT19 has targeted organizations in globes, with significant activity in:
– United States
– Europe
– East Asia
APT19 has extended their reach into multiple geographies/industries by compromising service providers.
Notable Operations
Significant operations have connected APT19 with many important initiatives.
- The first instance was between 2013 and 2016 when they conducted numerous cyberattack attempts to acquire users credentials through phishing emails and using web shells.
- Later in 2016-2017 there was significant compromise of many managed service providers and the cloud, allowing access to a number of organizations and victims.
- In 2018 members of APT19 were publicly indicted for being involved with hacking for hire.
- In 2019 until the present (2023) there have been continued smaller-scale operations being run in the same pattern (the same type as previous).
These campaign activities show that APT19 is still continuing its activity regardless of government oversight of the group.
Evolution and Current Activity
Since the public indictments by the United States and the press, the group has continued its cyber operations. However, it has changed the visibility and tempo of its operations to be more discreet.
Analysts stated that the group appears to have greatly reduced its overt operations, based on historical observations. However, it still runs campaigns that are easily traced to APT19 tradecraft. This suggests the group has reorganized rather than stopped.
APT19’s tactics, techniques, and procedures (TTPs), mainly for acquiring user credentials and selling access, have been adopted by many non-state and state-sponsored actors. This creates a gray area, or no distinction at all, between the two types of actor in the threat landscape.
Threat Assessment
The APT19 cyber espionage group is recognized as posing a medium-to-high risk against entities worldwide. APT19 is not recognized as the most technically advanced group. Still, it takes a methodical, access-based approach to espionage rather than relying on technical novelty. This makes it a particularly dangerous adversary. Long-term access and second-level exploitation via compromised credentials also lead to a greater level of risk for those organizations targeted by APT19.
Organizations affected by APT19 activities may also see a cascading effect. Stolen credentials can be reused or resold, which extends the impact beyond the initial intrusion.
How can organizations defend against APT19?
To effectively defend against APT19 organizations must concentrate their defenses upon identity and access protections:
– Implement strong phishing detection mechanisms and ensure that all users are well trained in recognizing phishing attempts.
– Use MFA for all external services.
– Monitor for anomalous credential usage.
– Conduct regular audits of web servers and hosting environments.
By maintaining proper credential hygiene organizations can reduce the principle operational advantage that enables APT19 (and similar threat actors) to be successful in conducting espionage.
Conclusion
APT19 demonstrates a hybrid model of espionage that integrates Government-directed intelligence objectives with large-scale credential theft. By focusing on access and continued access over technical ingenuity, APT19 remains relevant despite continually changing/advancing defenses.
Identity-based attacks continue to evolve at an increasing rate. The lessons learned from APT19 can show how malicious actors may use stolen or compromised credentials to gain a strategic advantage at the global level.
Download the APT19 (Deep Panda) fact sheet (PDF) for all the details!