Turla is a Russia-linked advanced persistent threat (APT) group. It carries out long-term cyber espionage. MITRE ATT&CK says it has been attributed to Russia’s Federal Security Service (FSB). The group has been active since the early 2000s.
It is known for modular malware such as Snake, Carbon and Kazuar. It targets governments, defense contractors and diplomatic missions. Related reading: the Snake (Uroburos) and Kazuar malware pages.
Turla stands out as one of the Russian-linked advanced persistent threat (APT) groups. It is known for its strong ability to persist and for its long life as an APT group.
Turla is also known as: Snake, Uroburos, Waterbug, VENOMOUS Bear, and Secret Blizzard. It has been active since the early 2000s. Through cyber espionage, it has been tracking and collecting information on behalf of Russian intelligence services.
Turla’s distinguishing mark is the development and use of modular and stealthy malware families. These include, but are not limited to, Snake, Carbon, Epic Turla, and Kazuar. The malware has mainly been used in sustained campaigns. These target government, defense contractors, and foreign diplomatic missions.
As we enter 2025, Turla remains an advanced threat actor. It persists with cryptic ability. It alters its toolsets and tactics to embed itself in sensitive networks across Europe, North America and beyond.
This blog will explore the identity of Turla, its associated tactics, attention-grabbing operations, and relevant configuration rotations.
Who Is Turla and What Motivates It?
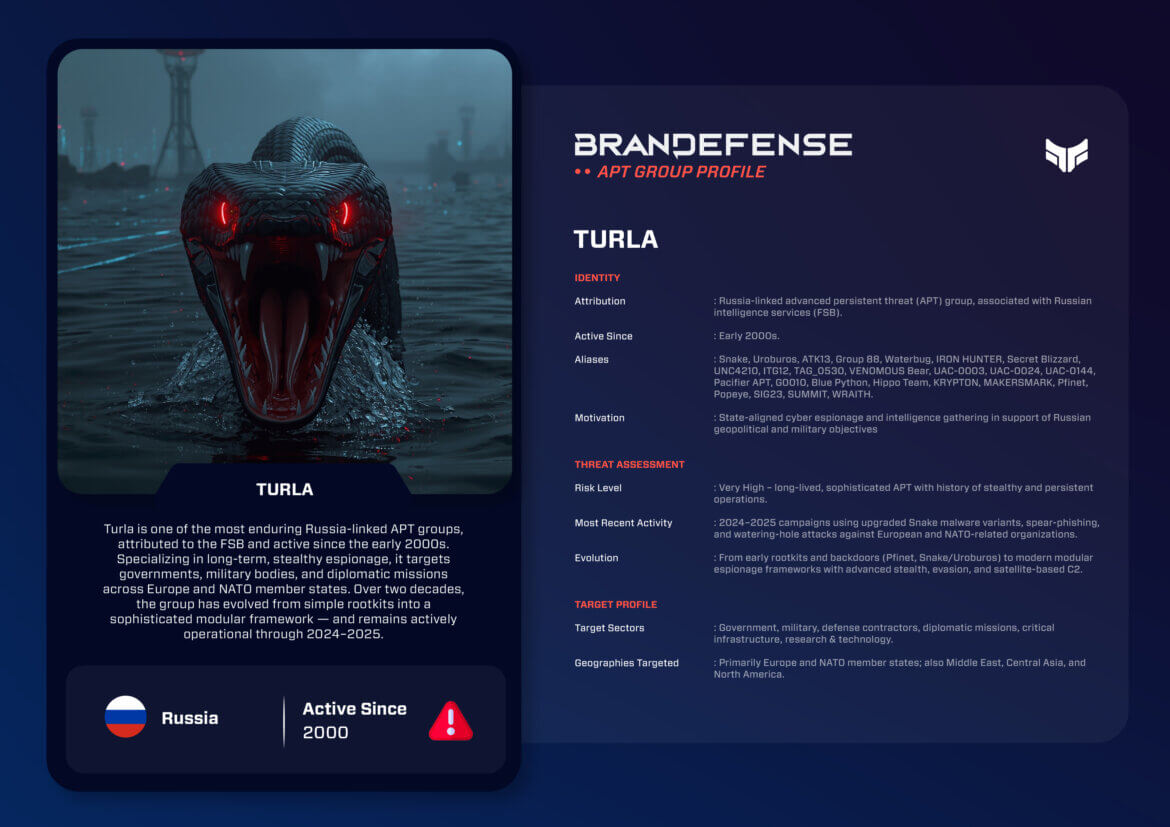
- Attribution: Russian state-affiliated. Widely attributed to the Federal Security Service (FSB).
- Active Since: Early 2000s.
- Aliases: Snake, Uroburos, ATK13, Group 88, Waterbug, IRON HUNTER, Secret Blizzard, UNC4210, ITG12, TAG_0530, VENOMOUS Bear, UAC-0003, UAC-0024, UAC-0144, Pacifier APT, G0010, Blue Python, Hippo Team, KRYPTON, MAKERSMARK, Pfinet, Popeye, SIG23, SUMMIT, WRAITH.
- Motivation: Long-term cyber espionage. It serves Russian geopolitical, military, and diplomatic objectives.
The mission for Turla has no financial motive. Rather, the group aims to keep indefinite access to high-value targets. It also aims to gather sensitive information and to degrade adversaries of Russia through covert and indefinite operations.
- Attribution
- Russia-linked, attributed to the Federal Security Service (FSB)
- Active since
- Early 2000s
- Aliases
- Snake, Uroburos, Waterbug, VENOMOUS Bear, Secret Blizzard
- Malware
- Snake, Carbon, Epic Turla, Kazuar
- Targets
- Government, defense contractors, diplomatic missions
- Motivation
- Long-term cyber espionage
TTPs: Methods, Tools, and Persistence
Turla is known for its innovation. It can run operations under the radar for long periods.
Initial Access:
- Spear-phishing using malicious attachments or links.
- Watering-hole attacks on highly-valued targets.
- Supply chain compromises.
- Exploiting vulnerabilities regarding VPNs and public-facing servers.
Persistence and Lateral Movement:
- The use of a Snake/Uroburos rootkit for holy-grail, long-term stealthy access.
- Scheduled tasks, registry manipulations, and trojanized software.
- Credential theft and privileged escalation to expand methods across networks.
C2 (Command & Control):
- Satellite-based C2 channels to obfuscate attribution and monitoring for detection.
- Multi-hop proxy chains and using compromised infrastructure.
- Encrypted HTTPS and domain fronting.
Malware/Tools:
- Snake/Uroburos: Modular rootkit/backdoor, flagship tool.
- Carbon: Modular espionage framework used for prolonged operations.
- Kazuar: Backdoor with .NET components linked to later activity related to SolarWinds.
- Epic Turla: Reconnaissance toolkit for initial compromise.
- Pfinet/Gazer: Espionage implants.
Techniques:
- Living-off-the-land (LOLBins) execution.
- Long-term stealth and persistence through advanced rootkits.
- Credential harvesting, exfiltration of sensitive documents.
- Initial accessSpear-phishing, watering-hole attacks, supply chain, VPN and server flaws
- PersistenceSnake/Uroburos rootkit, scheduled tasks, registry manipulations
- Lateral movementCredential theft and privileged escalation across networks
- Command and controlSatellite channels, multi-hop proxy chains, HTTPS, domain fronting
- CollectionCredential harvesting, exfiltration of sensitive documents
Target Profile
Turla regularly attacks high-value geopolitical sectors:
- Government ministries and agencies.
- Military and defense contractors
- Diplomatic missions and embassies.
- Providers of critical infrastructure.
- Research and technology organizations.
Geographies: The primary focus is on Europe and NATO countries. Operations also extend to the Middle East, Central Asia and North America.
Notable Operations
- 2008–2014: The Snake / Uroburos rootkit was deployed against European governments. It included C2 techniques based on satellite communications.
- 2015–2017: Turla and Carbon were used in espionage campaigns. These hit European and Middle Eastern diplomatic missions.
- 2018–2020: Attacks in the Middle East and Central Asian governments. Use of the Kazuar backdoor, associated with the SolarWinds supply chain compromise.
- 2021–2023: More targeting of NATO and European defense targets. It used advanced backdoors and multi-hop C2.
- 2024–2025: Renewed Snake activity targeting European ministries and associated with NATO. It exploited VPN vulnerabilities and was designed around a proxy infrastructure.
Recent Activities (2024–2025)
Recent activity indicates Turla continues to enhance its operations:
- Updated Snake Malware: Analysts reported new variants of the Snake Malware. They add more stealth and modularity.
- VPN Exploitation: Turla continues to exploit VPN appliances as a point of entry into government and defense networks.
- Enhanced Proxy Chains: Multi-layered proxy chains hid their infrastructure; this made attribution and response harder.
- Integration of Kazuar: Continued use of Kazuar, which shows links across Russian APT toolsets.
Strategic Impact
Turla’s use of advanced cyber capabilities shows a shift in Russia’s focus. Russia is moving from conventional military forces to a reliance on technology as a geopolitical tool:
- Strategic Espionage: Turla’s sustained operation in NATO and European networks gives long-term insight into their policy and military strategies.
- Persistent Threat: Turla uses rootkits. Its satellite command-and-control intent shows a goal of staying undetected for years.
- Global Risk: Turla’s operations span not only Europe but also the Middle East and North America. Such capabilities indicate its ambition is evolving beyond Europe.
How Can Organizations Defend Against Turla?
Organizations can protect themselves from Turla with layered defenses:
- Use phishing-resistant MFAHarden access controls.
- Deploy EDR/XDRLook for rootkits and stealthy implants.
- Monitor C2 trafficWatch for anomalous satellite or proxy traffic.
- Threat hunt for IOCsSnake, Carbon, Kazuar and Epic Turla.
- Segment the networkEnforce least-privilege within sensitive networks.
- Use phishing-resistant MFA and hardened access controls.
- Implement advanced EDR/XDR that can find rootkits or stealthy implants used for decades.
- Monitor for anomalous satellite or proxy C2 traffic.
- Threat hunt for Snake, Carbon, Kazuar, and Epic Turla IOCs.
- Enforce segmentation and least-privilege within sensitive networks.
Conclusion
Turla (Snake) is one of the most advanced and persistent Russian APT groups. It has operated for over two decades. Turla has shown resilience, adaptability, and a unique ability to stay dormant within victim networks for long periods.
Turla’s operations target European governments, NATO organizations, and critical infrastructure. They reveal Moscow’s long-term espionage priorities.
As of 2025, Turla’s upgraded Snake malware, along with enhanced C2 techniques and stealthy persistence, reinforce Turla’s strategic role as a cyber weapon for Russia.
Defenders must treat Turla not as a temporary threat, but a long-term counter adversary. It requires continuous monitoring, sharing of intelligence, and proactive defense.
You can download and review the sheet for all the details!