

Ghostwriter is an advanced persistent threat (APT) actor that CERT-UA describes as Belarus-aligned and tracks as UAC-0057, also known as UNC1151. It combines disinformation campaigns with cyber espionage and credential theft. Its main targets are NATO member states, Eastern Europe and the EU. This post dates its activity to at least 2016.
Introduction
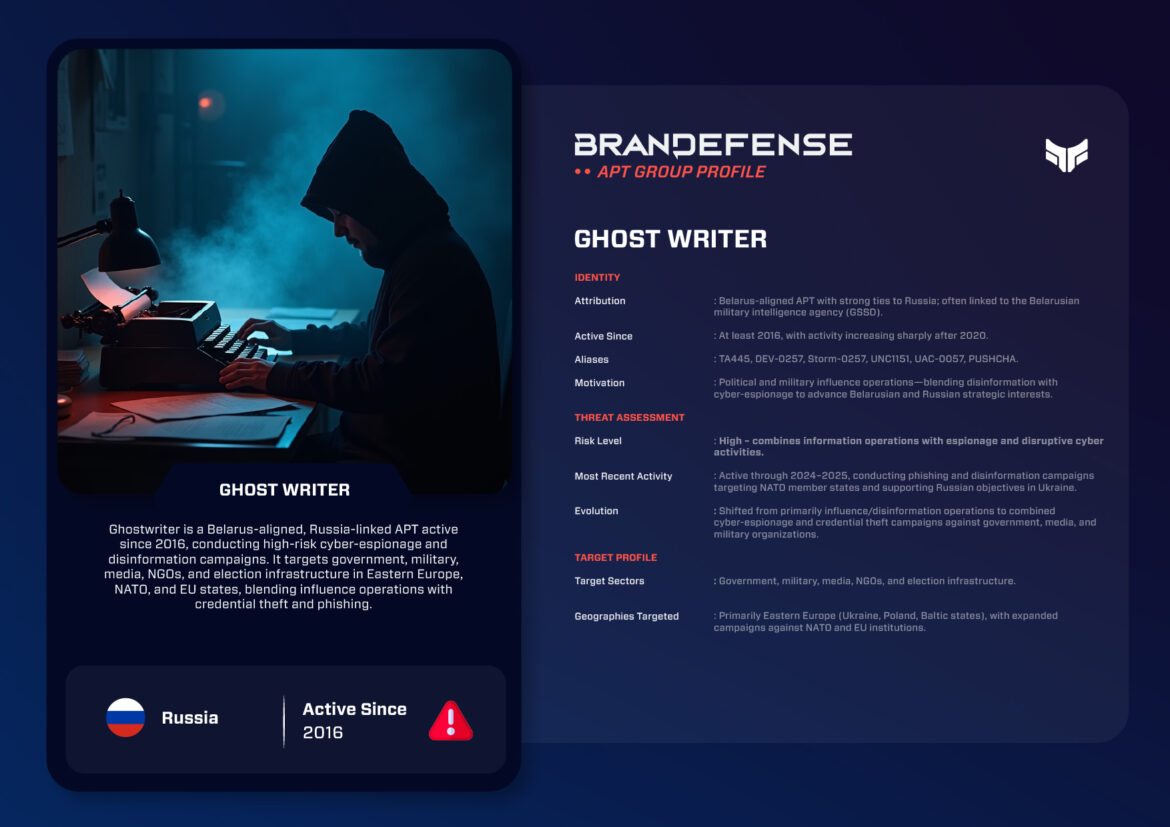
Ghostwriter, also tracked as TA445, DEV-0257, Storm-0257, UNC1151, UAC-0057, and PUSHCHA, is a Belarus-aligned advanced persistent threat (APT) actor with strong ties to Russia. Ghostwriter has been active since at least 2016. It has developed a hybrid approach that uses both disinformation campaigns and cyber espionage and credential theft techniques (for example, stealing login credentials). These techniques are mainly directed against NATO member states, Eastern Europe, and the EU. They operate for Belarus and are somewhat aligned to Russian state objectives. This is particularly clear in the ongoing context of the war in Ukraine.
Who Is Ghostwriter and What Does It Want?
Attribution differs by source. CERT-UA describes Ghostwriter as Belarus-aligned. The European Union declaration of September 2021 said some member states had associated the Ghostwriter activity with the Russian state. Mandiant said in November 2021 that it had traced UNC1151 to Belarus while not ruling out Russian contributions (SecurityWeek).
German authorities attributed attacks to the Russian military intelligence service GRU, as reported by TechCrunch. The group still has aspirations to assist greater Russia’s goals. It seeks political and military influence objectives by combining an information operations strategy with direct cyber intrusions. Ghostwriter’s primary threat vector is to target policy makers, journalists, and military institutions. The goals are to discredit NATO, disrupt elections, and weaken Western support for Ukraine. Other aliases for Ghostwriter include TA445, DEV-0257, Storm-0257, UNC1151, UAC-0057, and PUSHCHA. Another Russia-aligned group that targets Ukraine and NATO-linked governments is RomCom, which Microsoft tracks as Storm-0978.
- Also tracked as.
- UNC1151, UAC-0057 (CERT-UA).
- Active since.
- At least 2016, as stated in this post.
- Alignment.
- Belarus-aligned per CERT-UA; the EU declaration of September 2021 associated it with the Russian state.
- Main targets.
- NATO member states, Eastern Europe, the EU.
- Method.
- Disinformation combined with espionage and credential theft.
How Does Ghostwriter Attack?
Ghostwriter campaigns are unique in that they successfully combine both propaganda and technical intrusions.
- Initial Access: Phishing emails with either malicious attachments or links to credential harvesting sites, as well as by exploiting vulnerabilities in website content management systems.
- Persistence: By maintaining access through stolen credentials, long-term utilization of compromised email accounts, and the creation of false identities online.
- Command and Control (C2): By utilizing compromised infrastructure and hijacked websites to funnel traffic and maintain communications.
- Malware and Tools: By utilizing credential harvesters, infostealers, backdoors and publicly available tools, just repurposed for espionage.
- Techniques: A blend of traditional espionage techniques (credential theft, lateral movement, exfiltration) with disinformation campaign elements. These included fake news sites and actions that manipulated social media activity.
Notable Operations
2016–2019: Conducted disinformation campaigns aimed at NATO forces in Poland and the Baltic states in fake news articles aimed at undermining trust.
2020: Heavily engaged in phishing and disinformation attacks against Polish officials, while also attacking NATO personnel. The group used this year to shift toward fusing technical intrusions with propaganda.
2021: Expanded into operations against journalists, NGOs, and government officials across Eastern Europe and fusing credential theft with influence operations.
2022: Increased activity during the Russian invasion into Ukraine while specifically pushing a pro-Russian narrative, while simultaneously conducting phishing on Ukrainian and NATO aligned entities.
2023: The group conducted hybrid campaigns against European political organizations and electoral infrastructure in an effort to disrupt democratic processes and promote anti-NATO sentiment.
2024–2025: The group continued this combined campaign against NATO officials, EU political organizations, and regional media organizations. Its latest operations have focused on fracturing Western unity in support of Ukraine. It does this with further coordinated cyber intrusions and political influence operations.
- 2016 to 2019Disinformation against NATO forcesAimed at Poland and the Baltic states.
- 2020Phishing and disinformationPolish officials and NATO personnel; technical intrusions fused with propaganda.
- 2021Wider targetsJournalists, NGOs and government officials across Eastern Europe.
- 2022Invasion of UkrainePro-Russian narrative plus phishing of Ukrainian and NATO aligned entities.
- 2023European political organizationsHybrid campaigns against electoral infrastructure.
- 2024 to 2025NATO, EU and mediaContinued combined campaigns.
Recent Developments
Ghostwriter remains active as of 2025. Reports of ongoing phishing campaigns against NATO and EU institutions continue. They exist alongside various forms of propaganda aimed at degrading the public’s trust in the West’s governing bodies. Many APTs pursue either espionage or disinformation on their own. Ghostwriter’s ability to blend the two, to create more psychological and operational effect from cyber attacks, is unique. Its activities are also likely more potent than those of other APTs. Its alignment with Russian interests has only intensified since the escalation of the war in Ukraine. As a result, it essentially serves as a hybrid warfare tool in the information context.
Its operations link network intrusions with propaganda narratives and keep communication going between the two. This has given the group value in amplifying its narratives while it develops and compromises assets on the other side of the pro-Western action it was considering.
Conclusion
Ghostwriter is a serious threat, not just because it can spy but also because it can carry out an information warfare campaign. This multifaceted capability makes Ghostwriter a high-risk adversary to NATO, EU institutions, and the Eastern European governments mentioned previously.
How Can You Defend Against Ghostwriter?
- Improve phishing resiliency and employee training.
- Monitor for compromised logins and credentials.
- Monitor social media and news for suspicious use and disinformation campaigns.
- Harden election/all media infrastructure from cyber intrusions and information campaigns.
If hybrid warfare continues to define the threat environment in Eastern Europe, Ghostwriter will be a predictable and adaptable adversary. The continued melding of influence operations with cyberspace espionage is an indicator of the evolving nature of state-sponsored threats in 2025 and beyond.
You can download and review the sheet for all the details!
