
Introduction
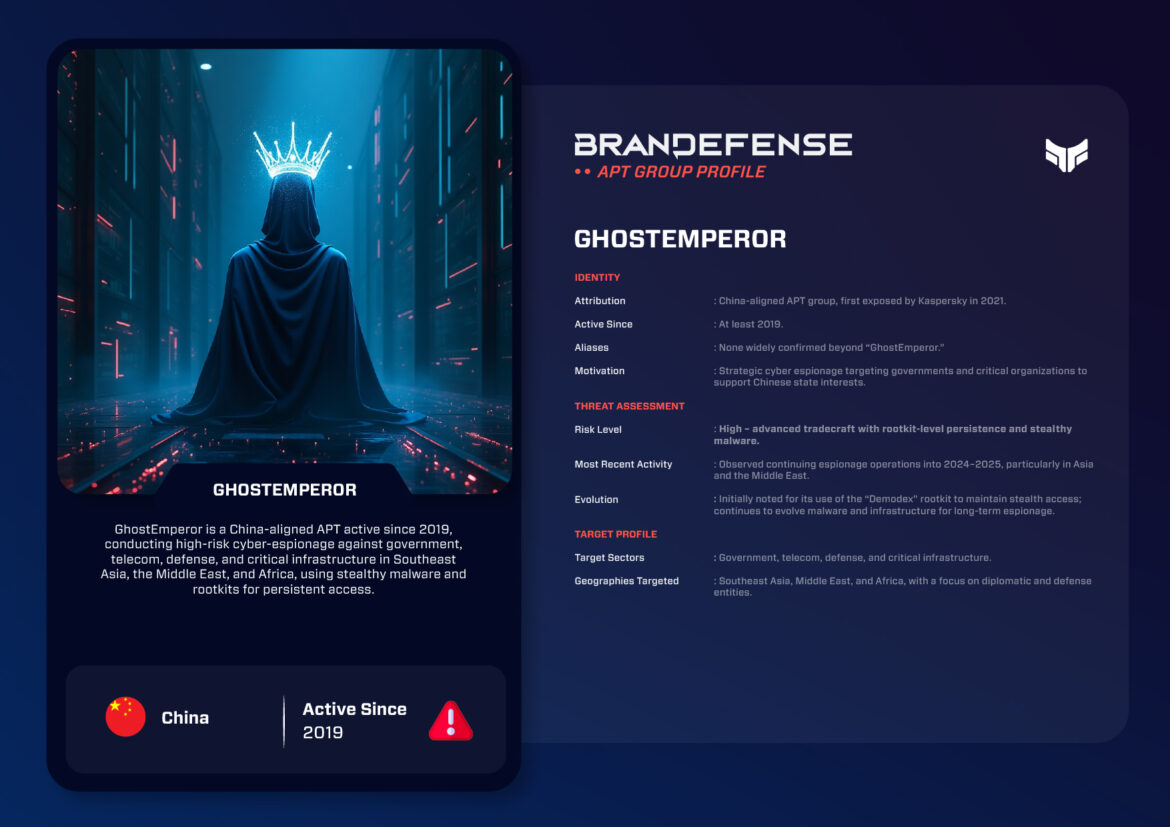
GhostEmperor is an advanced persistent threat (APT) group. This post describes it as widely suspected of working toward Chinese state intelligence goals. No official attribution has been made.
It is best known for the Demodex rootkit. This tool gives it hidden, lasting access at the kernel level. The post describes it as active since at least 2019. Its targets are governments, defense industries and critical infrastructure in Asia, the Middle East and Africa.
GhostEmperor is an APT group linked to China. It was publicly exposed in 2021. Here are the key facts:
- It has been active since at least 2019.
- It is best known for Demodex, one of the most advanced rootkits seen in recent years.
- It runs espionage campaigns mainly against governments, defense industries and critical infrastructure.
- Its targets are in Asia, the Middle East and Africa.
- It can hide at the kernel level for a long time. This makes it one of the more advanced spying threats in line with Chinese state goals.
Who is behind GhostEmperor and what motivates it?
GhostEmperor is widely suspected of working toward Chinese state intelligence goals. No official attribution has been made. Still, its targets and its TTPs mostly match China’s geopolitical interests.
What it wants
Its main motive is believed to be strategic cyber espionage. It goes after sensitive intelligence of three kinds:
- Political.
- Military.
- Diplomatic.
This work fits China’s aim to grow its economic and security influence in Asia, the Middle East and Africa.
TTPs
GhostEmperor uses many advanced tools built for stealth and lasting access. Its best-known tool is the Demodex rootkit. It lets the group hide its activity much deeper inside hacked systems.
- Initial Access: Exploiting flaws in unpatched servers that face the internet. Spear-phishing campaigns.
- Persistence: A custom rootkit such as Demodex, for hidden, long-term access.
- Command and Control (C2): Custom backdoors that talk over HTTPS and hidden channels. A large infrastructure with rotating servers to avoid detection.
- Malware and Tools: The GhostEmperor backdoor framework, the Demodex rootkit, custom-loaded modules and privilege escalation modules.
Notable Operations
2019: First campaigns against Southeast Asian governments. These were mostly spying break-ins.
2020: Widened its targets to telecom providers and diplomatic bodies. Used stealth malware to keep long-term access.
2021: Publicly exposed. The reports revealed its use of the Demodex rootkit. They also linked it to major espionage campaigns.
2022: Kept up operations against Middle Eastern governments. Focused on defense and foreign affairs ministries.
2023: More activity in Africa. Targets included governments and infrastructure projects tied to China’s Belt and Road Initiative.
2024–2025: Ongoing espionage in Asia and the Middle East. Clear signs of more advanced persistence and tougher infrastructure.
Recent Developments
GhostEmperor is still active as of 2025. It still spies on government and strategic sectors on several continents.
- It seems to keep improving its rootkit and backdoors. This makes it ever harder to detect or clean up.
- Its campaigns point to long-term intelligence gathering. This lines up with Beijing’s geopolitical aims.
For another China-aligned group that works through network infrastructure, see the PlushDaemon profile.
Why Demodex sets it apart
The Demodex rootkit also sets GhostEmperor apart from many other Chinese APT groups. It gives the group a very stealthy way to stay inside a system. Such tools are rarely seen in the wild. As a result, GhostEmperor can keep access for long periods and keep gathering intelligence.
Conclusion
GhostEmperor is a China-linked espionage threat with very high technical skill. It uses advanced rootkits, stealthy persistence and targets around the world. So it poses a high risk to government bodies and critical infrastructure providers.
How can organizations defend against GhostEmperor?
- Patch servers that face the internet quickly.
- Look out for odd kernel-level activity or signs of a rootkit.
- Use behavior-based detection to find hidden persistence.
- Watch credentials closely and detect lateral movement.
- Share any intelligence on new indicators of compromise tied to GhostEmperor campaigns.
As China keeps expanding around the world, GhostEmperor will stay a spying tool. Its activity shows how state-backed APTs are getting stealthier and tougher.
Future attacks will keep showing why defenders must track this group. They also need first-hand indicators of compromise. These help strengthen defense and incident response in 2025 and beyond.
You can download and review the sheet for all the details!
Frequently Asked Questions
What is GhostEmperor?
GhostEmperor is an advanced persistent threat group. The post says it is widely suspected of working in line with Chinese state intelligence goals, has been active since at least 2019 and focuses on espionage against governments, defense industries and critical infrastructure.
What is the Demodex rootkit?
Demodex is the rootkit GhostEmperor is best known for. The post says it gives stealthy, long-term persistence at kernel level. MITRE ATT&CK describes rootkits as hiding malware by modifying operating system API calls.
Who is GhostEmperor attributed to?
The post says the group is widely suspected of working in line with Chinese state intelligence goals, but that no official attribution has been made.
How can organizations defend against GhostEmperor?
The post advises patching internet-facing servers quickly, watching for kernel-level activity and rootkit signs, using behavioral detection, monitoring credentials and lateral movement, and sharing indicators of compromise.
