Handala (also Handala Hack and Handala Hack Team) is a persona that MITRE ATT&CK lists under VOID MANTICORE. MITRE assesses that this group works for Iran’s Ministry of Intelligence and Security (MOIS). The US Department of Justice (19 March 2026) says the Handala domains it seized were controlled by MOIS. The FBI (20 March 2026) assesses that the persona is linked to the Homeland Justice persona, which MOIS cyber actors also run.
| Also known as | Handala Hack, Handala Hack Team, Homeland Justice, Karma; group names VOID MANTICORE, Banished Kitten, Red Sandstorm |
| Attributed to | Iran's Ministry of Intelligence and Security (MOIS) |
| Attributed by | MITRE ATT&CK, the US Department of Justice and the FBI (2026) |
| Active since | 2022 (per the group profile) |
| MITRE ATT&CK ID | G1055 (VOID MANTICORE) |
| Main targets | Government, critical infrastructure, medical technology, Israeli organizations and personnel, and Iranian dissidents and journalists |
| Latest activity reported | March 2026, per the US Department of Justice and the FBI |
Sources, timeline and government actions are in the Handala threat group profile.
Introduction
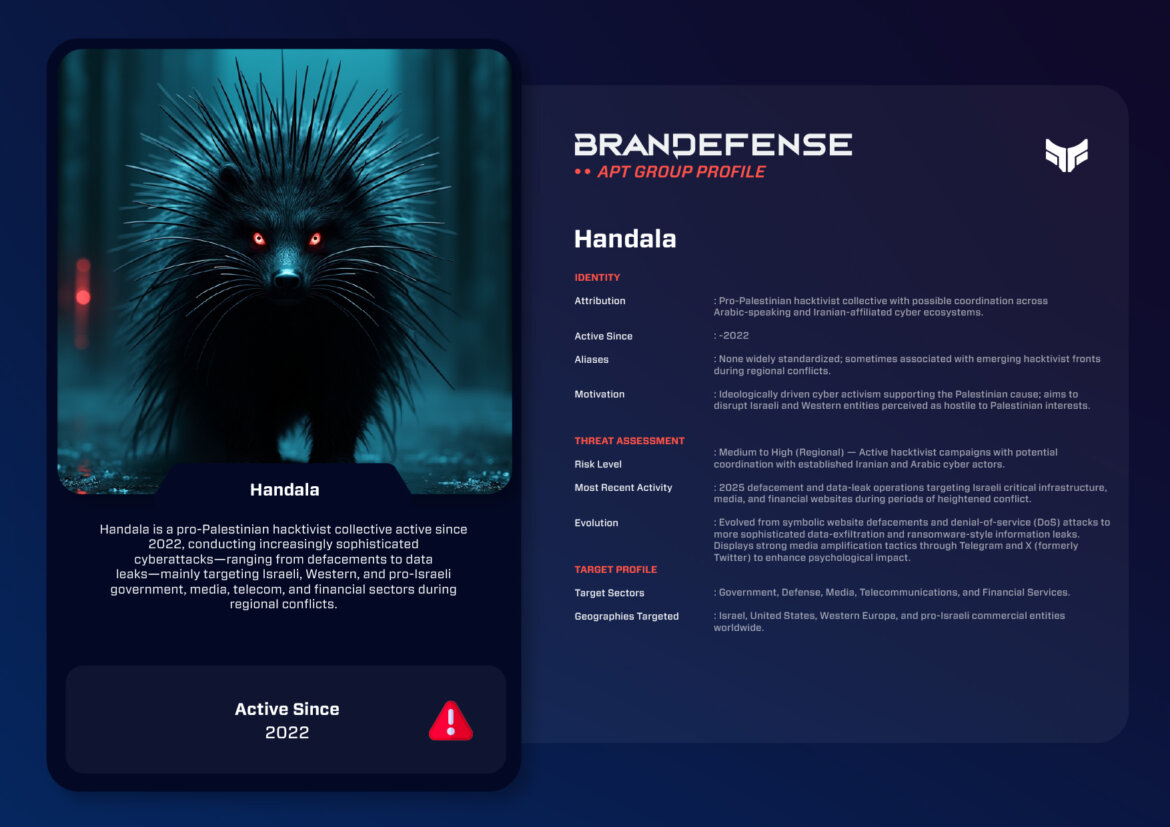
Since 2022, Handala has become one of the most visible and disruptive cyber actors. It presents itself as a pro-Palestinian hacktivist collective, although MITRE and the US government link it to Iran’s MOIS. Handala is named after the well-known symbol of Palestinian resistance created by the political cartoonist Naji al-Ali. It stands for a different generation of ideologically motivated cyber actors. They work in a new space that links hacktivism, information warfare, and psychological operations. Handala’s campaigns consist of web defacements, distributed denial-of-service (DDoS) attacks, and data-leak operations. They act as digital protests. Their aim is to raise attention for the Palestinian cause and to hit back at perceived Israeli and Western aggression.
Many APTs are known for stealth and persistence. Handala’s operations are about visibility and symbolism. Every defaced website or leaked dataset is more a message than a covert operation. Many people still assume hacktivism is less skilled. That view is out of date. Hacktivism has grown into a more significant form of asymmetric influence warfare.
- Type.
- Decentralized pro-Palestinian hacktivist collective.
- Active since.
- 2022.
- Methods.
- Website defacements, DDoS attacks and data leaks.
- Motivation.
- Ideological: support the Palestinian cause and retaliate against Israel and Western supporters.
- Government link.
- MITRE ATT&CK assesses ties to Iran’s MOIS; the post says it cannot be definitively stated.
Who Is Handala and What Motivates It?
This is not one organization with a single national goal or central control. It is a networked movement of people and small groups. Most members seem to be Arabic-speaking hackers across the Middle East and North Africa, and in the diaspora. Iranian-linked cyber actors may coordinate with it or inspire it. Analysts have seen overlaps in the timing of operations, threats, and propaganda themes between Handala, Anonymous Sudan, and Cyber Av3ngers. At a minimum this reinforces ideological connections. At most it points to collaboration and coordination.
The motivations of Handala are ideological:
1. They support the Palestinian Resistance. This means raising awareness about the plight of Palestinians, and also punishing the Israeli state and corporations.
2. They retaliate against the public, private, semi-private, and government institutions of Western countries that support Israel.
3. They wage psychological warfare. It can influence public opinion, cause fear, and amplify regional narratives of resistance, helped by mass media news coverage of the incidents.
The group uses the image of the barefooted boy from al-Ali’s artwork. It stands for defiance and perseverance in the face of hardship. The image is part of the visuals and messaging that go with their cyber operations.
Tactics, Techniques, and Procedures (TTPs)
The group is not as skilled as nation-state actors. It relies on speed, teamwork, and a feel for online influence. Its attacks mix old hacktivist methods with modern information campaigns.
Initial Access
The group usually gets into websites and servers through public-facing vulnerabilities or stolen credentials. It often uses open-source penetration testing tools or public CVEs. It goes after unpatched web apps and misconfigured cloud services. Some campaigns have used stolen credentials from earlier data breaches, or phishing kits bought from underground sources.
Attack Methods
- Website Defacements: The group often changes the look of target websites and posts images, videos, or slogans as propaganda. The defacement often refers to Gaza, shows the Handala symbol, or contains anti-Israel statements.
- Distributed Denial-of-Service (DDoS) Attacks: The group has run large-scale DDoS attacks by coordinating volunteer botnets. These use shared toolkits, like a modified version of the Low Orbit Ion Cannon (LOIC). Its DDoS attacks often land at the same time as big political events in the target’s region.
- Data Exfiltration and Leaks: Sometimes the group claims to have stolen sensitive data, such as employee credentials, government documents, or internal files. It posts this data in public on Telegram or on dark web forums.
- Ransomware-Style Pressure Tactics: The group has tried ransomware-style pressure with stolen data before it publishes the data. It is not a money ransom. The ransom is political. The group asks for changes in policy or a public response instead of payment.
Command and Control (C2)
The group can work without central servers. It prefers Telegram, dark web channels, and social media to plan action and spread propaganda. These channels also serve for recruiting and fundraising. They ask volunteers to join DDoS campaigns or to boost messages on social media.
Propaganda and Psychological Operations
A hallmark of Handala’s campaigns is information amplification. It times its attacks closely with news stories. It uses coordinated posts, hashtags, and short videos to make attacks more visible. Posts are usually backed by infographics and “victory messages,” which exaggerate the size of the attacks and increase their psychological impact.
Notable Campaigns and Targets
Handala’s cyber campaigns, all of them after its emergence, show how it changed from a symbolic activist into a multi-vector operation. It can now cause disruption at a regional level.
- 2023 – #OpIsrael Campaign: The group took part in coordinated website defacements during an annual anti-Israel hacktivist operation. Dozens of government and private-sector websites were temporarily taken offline. They showed Handala imagery and pro-Palestinian slogans.
- 2024 – Data Leak Campaign: The group leaked data it claimed was stolen from Israeli defense contractors. A technical review indicated that one of the affected organizations published recycled or mixed data. Even so, the media coverage maximized the intended psychological impact.
- 2025 – Infrastructure Disruption: The group ran multi-wave distributed denial of service (DDoS) attacks against Israeli telecom and energy companies. They were short-lived. Still, they caused visible service disruption and drew international media attention.
- 2025 – Collaboration with Anonymous Sudan: As regional tensions worsened, the group co-branded cyber operations with Anonymous Sudan. These operations were aimed at western media and finance organizations. The stated purpose of the campaign was solidarity with Gaza and “digital resistance.”
Each campaign included an aggressive social media push. It supported the group’s two-part plan of cyber action and control of the story.
- 2023#OpIsrael CampaignCoordinated website defacements during an annual anti-Israel hacktivist operation.
- 2024Data Leak CampaignLeaked data it claimed was stolen from Israeli defense contractors.
- 2025Infrastructure DisruptionMulti-wave DDoS attacks against Israeli telecom and energy companies.
- 2025Collaboration with Anonymous SudanCo-branded operations against western media and finance organizations.

Evolution and Organizational Dynamics
Handala signals an evolution of hacktivism. Ideological collectives now work as decentralized influence networks, not as traditional hacker groups. Its agility and reliance on open-source tools make attribution and disruption extremely difficult.
Key characteristics of this evolution are:
– Decentralized Command Structure: There is no formal hierarchy. Semi-autonomous clusters carry out operations under the Handala label.
– Open Recruitment: Hackers, sympathizers, and script kiddies are invited to join as volunteers through public Telegram channels.
– Shared Infrastructure: Its hackers share botnets, leaked databases, and DDoS tools. They get them from allied hacktivist collectives.
– Media Based Metrics: Success is measured by attention and virality, not by long-term network access or data exfiltration.
Between 2024 and 2025, cybersecurity researchers noted overlaps between Handala and Iranian-linked influence campaigns. It cannot be definitively stated that Handala is connected to the Iranian government. However, the messaging or themes, the choice of target audience, and the timing are similar. These suggest that at least some tacit alignment exists.
Strategic Impact
The rise of Handala shows how hacktivism has become a key part of modern geopolitical conflict. The group takes the battlefield beyond the physical world through social media and decentralized technology. Its attacks are part of the information warfare ecosystem. They erode public trust, amplify polarizing narratives, and keep up constant digital unrest.
From a cybersecurity view, Handala poses a medium to high level of threat because it is unpredictable and can mobilize quickly. The attacks are not technically sophisticated. But the group uses them with good timing during military escalations, political crises, or symbolic dates (e.g. Nakba Day) to increase their psychological and political effect.
The group can also call up mass volunteer DDoS attacks fast. This strains the ability of established security models to hold up against hacktivist attacks. Many of Handala’s campaigns also build on public sentiment. That complicates mitigation, since it is as much a communications problem as a technical one.
How Can Organizations Defend Against Handala?
Proactive Monitoring: States, especially Israel and Western nations, should track new hacktivist chatter on Telegram and dark web forums. This may give them early warning of future Handala-linked operations.
DDoS Resilience: Organizations should set up scalable DDoS protection. This matters most in sectors such as government, energy, and telecoms, which are known for advanced targeting.
Vulnerability Management: Organizations can patch public facing applications early and check configurations often. This lowers the chance of exploitation.
Information Response: Responses to “symbolic” cyber attacks will likely bring disinformation. Agencies need a solid communication strategy. It should counter the disinformation that is likely to follow when the reputational side of a cyber incident is handled badly.
Regional Intelligence Sharing: Sharing data through CERTs and ISACs lets teams work together to establish known TTPs. They can then identify TTPs quickly and coordinate defensive measures effectively.
- Proactive monitoringTrack hacktivist chatter on Telegram and dark web forums for early warning.
- DDoS resilienceUse scalable DDoS protection, especially in government, energy and telecoms.
- Vulnerability managementPatch public facing applications and routinely check configurations.
- Information responseDevelop a robust communication strategy to counter disinformation.
- Regional intelligence sharingShare data via CERTs and ISACs to identify TTPs and coordinate defense.
Conclusion
Handala is a clear sign of modern hacktivism: fast, decentralized, and driven by ideology. It shows that small collectives can wield outsized power through digital disruption and information warfare. In 2025, the collective keeps using global attention on Middle Eastern conflicts to run offensive cyber attacks and push its stories online.
For cybersecurity professionals, Handala is both a technical and an emotional threat. Its campaigns show that in the age of hybrid warfare, ”Visibility=Power”. It has proven effective at turning digital protest into geopolitical impact.
You can download and review the sheet for all the details!