

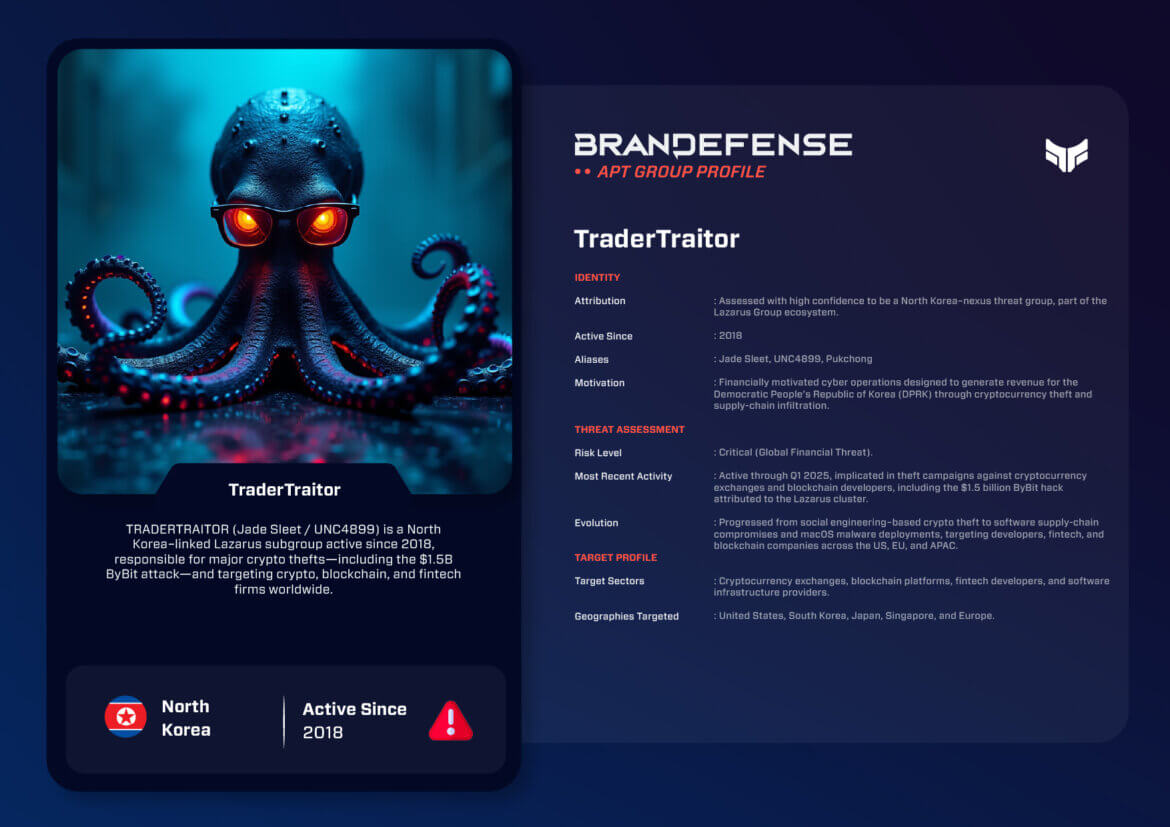
TraderTraitor is the name the FBI uses for North Korean state-backed hackers who steal cryptocurrency. Microsoft calls it Jade Sleet, and Palo Alto Networks Unit 42 calls it Slow Pisces or Pukchong. Google says its UNC4899 likely matches it. It targets crypto exchanges, DeFi services, trading firms, venture funds and large holders.
It gets in mostly through fake job offers that lead to trojanized trading apps.
What to check first is in the section “What Should You Check Now?” below. We checked the facts on this page against CISA and FBI notices, and named press reports, on 11 November 2026.
- Also called.
- Jade Sleet (Microsoft); Slow Pisces and Pukchong (Palo Alto Networks Unit 42); UNC4899 (Google, likely match).
- Alignment.
- North Korea state-sponsored; CISA lists Lazarus Group, APT38 and BlueNoroff as names for the same group.
- First seen.
- At least 2020 (CISA).
- Motivation.
- Financial gain that funds the DPRK regime.
- Targets.
- Crypto exchanges, DeFi protocols, trading companies, venture funds and large holders.
- Common entry.
- Spearphishing with fake job offers that push targets to download trojanized trading apps.
- Latest FBI alert.
- Binance theft of more than $6 billion, October 2026, blamed on North Korea; Decrypt and BleepingComputer report it names TraderTraitor.
Latest Activity: Binance Incident, October 2026
On 31 October 2026 the FBI said North Korea was responsible for the theft of more than $6 billion in virtual assets from Binance. The FBI says the theft took place on or about 29 October 2026. Decrypt and BleepingComputer report that the alert names the activity TraderTraitor. They also report that the FBI, the Secret Service and IRS Criminal Investigation saw the stolen assets converted mainly into Ether.
According to the same reports, the FBI expects more laundering through DeFi and instant swap services. It asks node operators, instant exchanges and DeFi services to block transactions with the addresses it published. Binance puts the incident at about $6.3 billion, and press reports say it restarted withdrawals in phases on 1 November 2026. TRM Labs and Chainalysis had linked the theft to TraderTraitor before the FBI alert came out.
Our Binance security incident analysis shows how the funds moved and what is still not known. A study of Telegram and X posts after the hack shows when the TraderTraitor name reached underground channels.
Introduction
TraderTraitor, also known as Jade Sleet, UNC4899, and Pukchong, is a North Korea-aligned threat group. It has become one of the most prolific financial cyber actors in the world. It is part of the larger Lazarus Group.
TraderTraitor focuses on cryptocurrency theft, blockchain exploitation, and software supply-chain breaches. Its campaigns mix espionage tactics with cybercrime for money. The aim is to support North Korea’s sanctioned economy.
Since at least 2020, according to CISA, the group has moved from simple phishing attacks to more complex operations. These include trojanized developer tools, fake cryptocurrency platforms, and malware that targets both Windows and macOS systems. Its constant innovation has helped it steal billions of dollars in cryptocurrency. The victims are exchanges, blockchain developers, and fintech firms around the world.
Who Is TraderTraitor and What Motivates It?
TraderTraitor is linked to the Democratic People’s Republic of Korea (DPRK). It shares operational ties with the notorious Lazarus Group. This larger group includes subclusters like APT38 and Andariel. Unlike the espionage-focused branches of Lazarus, TraderTraitor mainly aims for financial gain.
Its actions directly raise funds for the DPRK regime. The money supports nuclear weapons programs, helps evade international sanctions, and keeps state operations running.
The group’s names Jade Sleet, UNC4899, and Pukchong refer to overlapping activity. This activity keeps targeting cryptocurrency developers, exchanges, and blockchain software providers. It shows a clear focus on the digital finance space.
GitHub said in July 2023 that Microsoft Threat Intelligence calls the group Jade Sleet. Google’s threat intelligence team said in July 2023 that UNC4899 likely corresponds to TraderTraitor. Palo Alto Networks Unit 42 listed Jade Sleet, TraderTraitor and Pukchong as other names for Slow Pisces in April 2025.
What Tactics, Techniques and Procedures Does TraderTraitor Use?
TraderTraitor has a set approach that blends social engineering, supply-chain compromise, and custom malware. The group is known for breaking into trusted development environments. They often reach victims indirectly through third-party dependencies or tainted software packages.
Initial Access: The group mainly uses spear-phishing and social engineering. Its operators pretend to be recruiters or investors from real cryptocurrency firms. They reach out via LinkedIn, Telegram, and email.
They lure victims into downloading malicious attachments or fake job-related applications with backdoors. In some cases, it publishes malicious packages to open-source registries such as npm, which GitHub reported in 2023.
Persistence: After gaining access, TraderTraitor stays in for the long term. It uses modified update processes, persistent registry entries, and hidden malicious code inside legitimate applications. On macOS systems, the group has been seen using signed binaries to avoid detection. It takes advantage of developer certificates and Apple’s notarization process.
Command and Control (C2): The group uses HTTPS-based encrypted communication. It sends stolen data to servers controlled by DPRK or to compromised servers. Its infrastructure often mimics real blockchain or developer platforms. This makes detection difficult.
Malware and Tools:
– TraderTraitor apps: CISA’s name for the trojanized trading and price prediction apps, built with Electron and Node.js. CISA says they resemble the Lazarus Group’s earlier AppleJeus apps.
– Custom Loaders: These deliver secondary payloads, such as remote access trojans (RATs) and data stealers.
– Trojanized Developer Tools: malicious npm packages and GitHub repositories (GitHub, 2023) and coding challenges that hide Python malware (Palo Alto Networks Unit 42, 2025).
– Fake Wallet Apps: These are found on macOS, Windows, and Linux systems. They trick users into sending funds to DPRK-controlled wallets.
Techniques: The group mixes credential harvesting, data exfiltration, code signing abuse, and cryptocurrency wallet compromise. It also shows growing skill in exploiting the software supply chain. State-sponsored spies often dominate this area.
Notable Operations
Before TraderTraitor (AppleJeus): CISA says TraderTraitor uses tactics similar to the Lazarus Group’s earlier AppleJeus campaign. AppleJeus spread cryptocurrency trading apps modified to include malware that steals cryptocurrency.
Supply-Chain Compromises (2023): GitHub said in July 2023 that Jade Sleet sent developers repository invitations and used malicious npm package dependencies. The same month, Google’s Mandiant tied UNC4899 to a supply chain compromise that began with spear phishing at a software provider.
Social Engineering Surge (2023): Using professional networking platforms, the group pretended to be recruiters from well-known crypto firms and offered fake interviews. Victims were tricked into downloading infected applications. This gave TraderTraitor remote access to their systems. For how a fake job interview and a tampered developer tool led to a 2026 exchange theft, see the Binance fake job interview attack chain.
Bybit and Blockchain Exploitation (2024–2025): The FBI attributes the theft of about $1.5 billion in virtual assets from the Bybit exchange in February 2025 to North Korea. It says TraderTraitor actors moved the stolen assets across thousands of addresses on multiple blockchains.
- 2020First TraderTraitor activityCISA says the group has been active since at least 2020.
- 2023Supply-chain compromisesMalicious npm packages (GitHub) and a software provider breach (Google).
- 2023Social engineering surgeFake recruiters offered interviews that led to infected applications.
- 2025Bybit exchange hackThe FBI attributes the theft of about $1.5 billion to North Korea.
- 2026Binance theftThe FBI attributes the theft of more than $6 billion to North Korea; Decrypt and BleepingComputer report it names TraderTraitor.
What Should You Check Now?
These checks come from CISA advisory AA22-108A and the FBI alerts. Start with the first three, because they match how CISA says the group gets in.
- Job offers: ask staff in system administration and DevOps roles whether anyone got a high-paying job offer by message, and what they opened afterwards.
- Trading apps: look for trading or price prediction apps on work devices. CISA describes the trojanized apps as Electron and Node.js programs for Windows or macOS.
- Software sources: allow downloads only from reputable or primary sources, and verify them.
- Logins: enforce multifactor authentication and watch for anomalous logins.
- Access: patch known exploited vulnerabilities first, and apply least privilege and network segmentation.
- Domains: monitor or block newly registered domains.
- Laundering addresses: if you run an exchange, node, bridge or DeFi service, block transactions tied to the addresses in the FBI alerts.
- Reporting: put the FBI and CISA in your incident response plan.
Strategic Impact and Defensive Takeaways
TraderTraitor’s operations highlight the link between state strategy and organized financial cybercrime. The DPRK uses cyber efforts in a systematic way for economic gain. This blurs the line between spying and stealing. Each successful campaign directly supports North Korea’s larger geopolitical goals.
For defenders, TraderTraitor stresses the need to secure development environments. It also stresses verifying code integrity and enforcing strict access controls across blockchain infrastructure. Key defensive recommendations for development teams are below:
- Enforce multifactor authenticationFor all developer and exchange accounts.
- Validate code signaturesUse SBOM practices to find unauthorized dependencies.
- Hunt for known signsAppleJeus, UNC4899 infrastructure and fake recruiter campaigns.
- Monitor outbound connectionsWatch for domains that mimic blockchain APIs or fintech platforms.
Conclusion
TraderTraitor ranks as one of the most successful financially motivated threats in history. It combines espionage-level skills with a constant drive for money. As of November 2026, the group remains active: Decrypt and BleepingComputer report that the FBI’s Binance alert names TraderTraitor. It uses social engineering, supply-chain infiltration, and advanced malware to exploit the digital financial ecosystem.
Its persistence and adaptation show how cybercrime, state policy, and economic need meet in today’s threat landscape. Billions have been stolen and many organizations compromised. TraderTraitor is both a warning and a benchmark for what state-supported financial cyber operations can do.
Download The TraderTraitor Profile (PDF)
Download the one-page TraderTraitor profile as a PDF. It sums up the names, tactics and notable operations on this page. The page has the newer facts.
Frequently Asked Questions
What is TraderTraitor?
TraderTraitor is the name the FBI uses for North Korean state-backed hackers who steal cryptocurrency. CISA calls the activity a North Korean state-sponsored campaign against crypto companies. The post places it within the Lazarus Group.
What else is TraderTraitor called?
Microsoft calls it Jade Sleet, and Palo Alto Networks Unit 42 calls it Slow Pisces and also lists Pukchong. Google says its UNC4899 likely corresponds to TraderTraitor.
Who does TraderTraitor target?
CISA lists cryptocurrency exchanges, DeFi protocols, play-to-earn crypto games, crypto trading companies, venture capital funds investing in crypto, and individual holders of large amounts of crypto or valuable NFTs. The post adds developers and blockchain software providers.
How does TraderTraitor get into a victim’s systems?
CISA says it mainly uses spearphishing, with messages that mimic a recruitment effort and offer high-paying jobs to push victims into downloading trojanized cryptocurrency applications. It reports social engineering over a variety of communication platforms.
Was TraderTraitor behind the Bybit hack?
The FBI says North Korea was responsible for the theft of approximately $1.5 billion in virtual assets from Bybit on or about February 21, 2025. Its alert refers to TraderTraitor actors dispersing the stolen assets across thousands of addresses on multiple blockchains.
Was TraderTraitor behind the Binance theft?
The FBI says North Korea was responsible for the theft of more than $6 billion in virtual assets from Binance on or about October 29, 2026. Decrypt and BleepingComputer report that the alert names the activity TraderTraitor. Binance puts the incident at about $6.3 billion.
How can organizations defend against TraderTraitor?
CISA advises enforcing multifactor authentication, training staff to spot social engineering, and downloading files only from reputable or primary sources. The post adds code signature checks and SBOM practices.
Sources
- CISA: Advisory AA22-108A, TraderTraitor, North Korean State-Sponsored APT Targets Blockchain Companies
- FBI: North Korea Responsible for $6 Billion+ Binance Attack (31 October 2026)
- FBI IC3: PSA250226, North Korea Responsible for $1.5 Billion Bybit Hack
- Google Cloud Threat Intelligence: North Korea supply chain attack (24 July 2023)
- Palo Alto Networks Unit 42: Slow Pisces (14 April 2025)
- GitHub: Security alert: social engineering campaign targets technology industry employees (18 July 2023)
