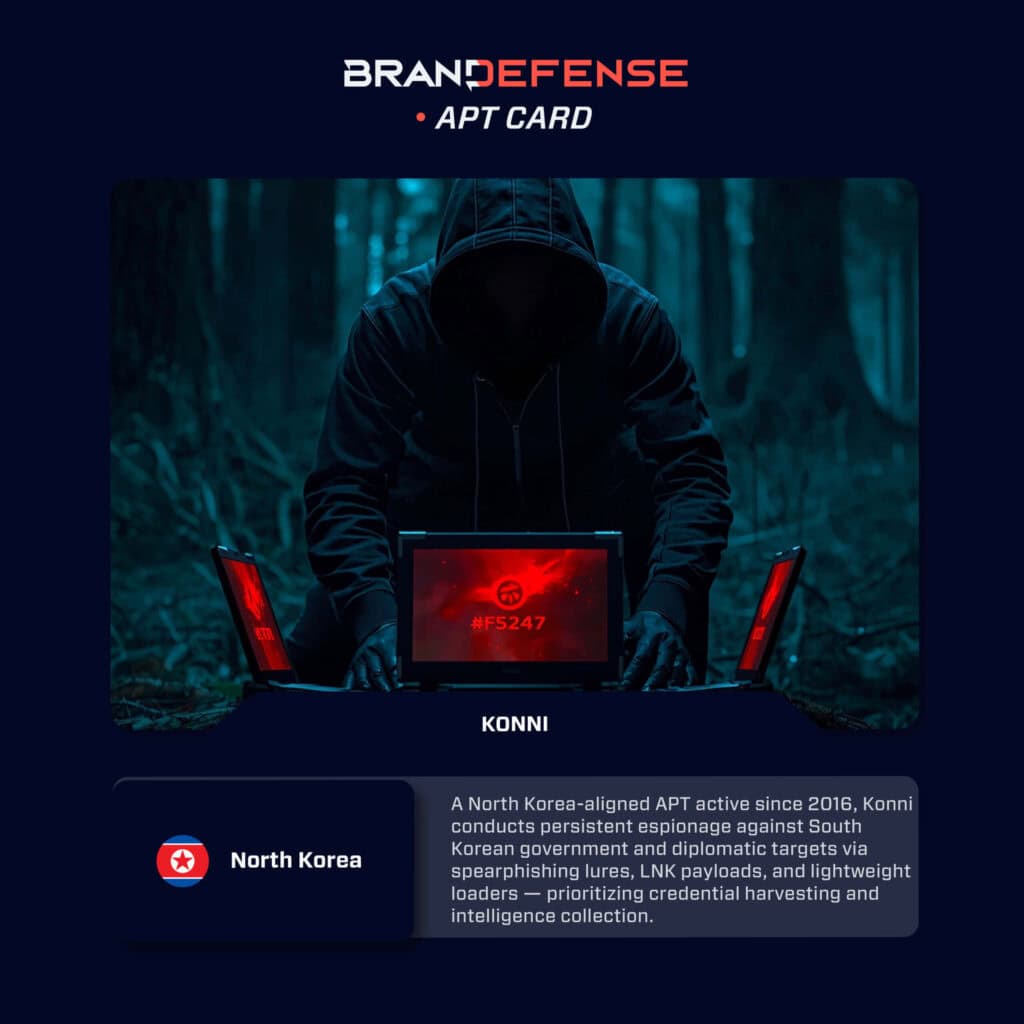
The Konni APT group is a North Korea-linked cyber-espionage group, also tracked as Vedalia, TA406, Opal Sleet and OSMIUM. It focuses on long-term intelligence collection against South Korean, Japanese, Russian and wider diplomatic targets, mostly through spearphishing and the KONNI remote access tool. This post covers its aims, methods, past operations and how defenders can respond.
What is the Konni APT group?
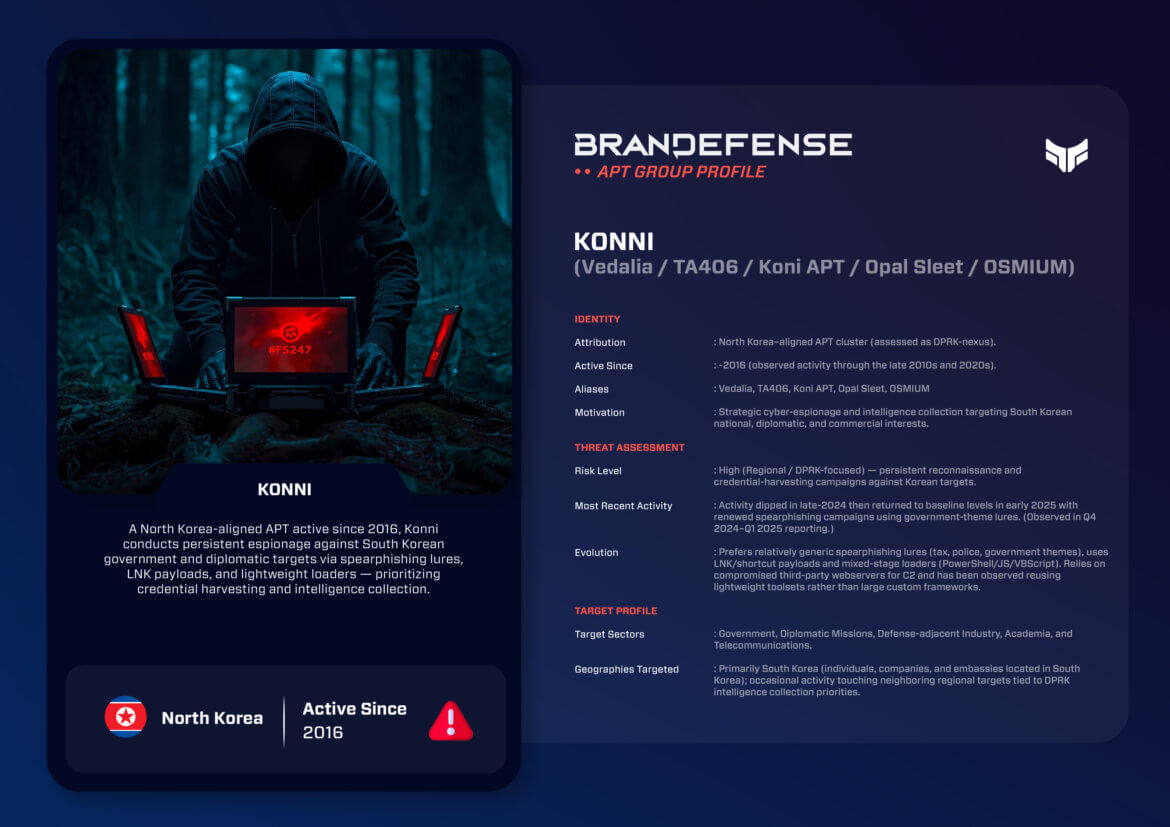
Konni is also called Vedalia, TA406, Opal Sleet and OSMIUM. It is one of North Korea’s most consistent and systematic cyber-espionage groups. It has been active since at least 2016. It focuses on gathering intelligence on South Korean, Japanese, Russian and broader targets in the international diplomatic space. Some DPRK-linked groups, such as Lazarus or Andariel, have a stronger financial motive. Konni focuses on discreet, long-term intelligence collection. This advances one of Pyongyang’s geopolitical goals.
Konni’s pattern of work matches the mission profile of North Korea’s Reconnaissance General Bureau (RGB). The RGB is the state’s leading intelligence service. It is responsible for many of North Korea’s global cyber operations. For almost a decade, Konni has kept a steady pace. It has refined its techniques to balance deception and persistence. This lets it get useful political, military and policy-related intelligence.
- Also tracked as.
- Vedalia, TA406, Opal Sleet, OSMIUM.
- Active since.
- At least 2016, according to this post.
- Mission.
- Long-term intelligence collection, not financial gain.
- Targets.
- South Korean, Japanese, Russian and wider diplomatic targets.
- Aligned with.
- North Korea’s Reconnaissance General Bureau (RGB).
- Signature tool.
- KONNI RAT, a remote access tool.
What does Konni want?
Konni’s main mission is strategic intelligence. It collects sensitive intelligence on inter-Korean relations, defense policy and diplomatic issues. This advances North Korea’s national interests. The group times its activity to geopolitical events, such as sanctions deals or joint military exercises by South Korea and the United States.
Its motivations consist of:
- Political and Diplomatic Intelligence: Getting intelligence on embassies, ministries and think tanks involved in Korean Peninsula policy.
- Military and Security Awareness: Getting defense communications and research data on military topics.
- Strategic Counterintelligence: Monitoring activities of [organizations] monitoring for DPRK sanctions or nuclear developments.
This focus shows how Pyongyang carries out its wider plan. It uses cyber abilities to offset its limited ability to collect traditional HUMINT, while still gaining influence in the region.
Tactics, Techniques, and Procedures (TTPs)
Konni shows a fair and effective level of technical skill. Its success is largely due to well-run social engineering. Its stealthy malware is designed to evade detection while staying persistent.
1. Initial Access
Spearphishing, or targeted phishing, is a key initial access vector for Konni. The group sends emails that appear to come from South Korean or international government, defense or media companies. The attachments are mostly weaponized Microsoft Office or RTF files that rely on embedded macros or scripts. Lately, the group has used LNK (shortcut) files and archive tricks more and more to bypass email filtering.
2. Execution and Persistence
Once initial access has been achieved, Konni uses lightweight loaders written in PowerShell, VBScript or JavaScript. These loaders then retrieve extra payloads, which are usually a variation of KONNI RAT or CARROTBAT malware. To keep persistence, KONNI malware uses scheduled tasks, registry changes and abuse of real Windows tools.
3. Command and Control (C2)
Konni’s infrastructure is straightforward yet resilient. The group often relies on real hosting services and compromised web servers for C2 traffic. Communication usually uses HTTP/S or FTP and blends in with normal traffic. Cloud infrastructure has also appeared more often in campaigns since 2023.
4. Malware Arsenal
Konni has a small but stable malware ecosystem:
- KONNI RAT: The signature malware of the group. It allows command execution, captures screenshots and exfiltrates files.
- CARROTBAT-ered: Used to deliver secondary payloads and set up persistence.
- BabyShark: A Visual Basic script-based malware family associated with several North Korean campaigns. MITRE ATT&CK links it mainly to Kimsuky. It is used for espionage and reconnaissance.
- PowerShell-based loaders: Light scripts used for stealthy delivery and lateral movement.
The tools that Konni uses are not overly advanced. They are carefully designed to avoid detection and allow long-term infiltration.
5. Exfiltration and Data Handling
The group exfiltrates sensitive data over encrypted HTTP/S channels. This includes user credentials, internal documents and system data. Analysts believe the stolen intelligence helps diplomatic talks and strategic planning for North Korea.
- Spearphishing emailWeaponized Office, RTF or LNK attachmentTechnique T1566.001 (MITRE ATT&CK, opens in a new tab)
- Lightweight loaderPowerShell, VBScript or JavaScript fetches payloadsTechnique T1059.001 (MITRE ATT&CK, opens in a new tab)
- PersistenceScheduled tasks, registry changes, real Windows toolsTechnique T1547.001 (MITRE ATT&CK, opens in a new tab)
- Command and controlHTTP/S or FTP to hosting services and compromised serversTechnique T1071.001 (MITRE ATT&CK, opens in a new tab)
- ExfiltrationCredentials, documents and system data over encrypted HTTP/STechnique T1041 (MITRE ATT&CK, opens in a new tab)
What are Konni’s notable operations?
Konni’s campaigns show its tenacity and adaptability in DPRK cyber-espionage.
- 2017 – KONNI RAT Campaign: In its early campaigns, Konni targeted South Korean government staff. It used spearphishing with fake diplomatic mail to deliver KONNI RAT malware.
- 2020 – BabyShark Variant Deployment: Weaponized and updated malware was used in a campaign against policy institutes and defense research centers in Seoul.
- 2022 – Credential Harvesting Operation: Beginning in February 2022, the attackers started a wave of phishing attacks to capture user credentials. They used malicious LNK files that referred to talks on future international cooperation between North and South Korea.
- 2024 – Opal Sleet Overlaps: Overlaps in indicators and artifacts suggest some level of shared work with other DPRK groups or actors such as Kimsuky. They targeted South Korean defense contractors.
- 2025 – Diplomatic Espionage Campaign: New phishing campaigns spread fake South Korean ministry documents. Heavily improved and weaponized PowerShell loaders and new modular RATs point to ongoing refinement.
- 2017KONNI RAT campaignSpearphishing with fake diplomatic correspondence aimed at South Korean government staff.
- 2022Credential harvestingPhishing with malicious LNK files, starting in February 2022.
- 2025Diplomatic espionageFake South Korean ministry documents and improved PowerShell loaders.
The campaigns show Konni’s patience and its ability to stay relevant as the threat environment in the region changes.
Evolution and Group Dynamics
Konni has moved from a fairly isolated espionage cell to a deeper role in North Korea’s wider cyber ecosystem. Analysts note that the group’s TTPs increasingly overlap with Kimsuky (Velvet Chollima) and Andariel (Silent Chollima). This suggests shared resources or central direction from the RGB.
Trends seen in the evolution of Konni include:
- Infrastructure Rotation: Changing C2 domains and hosting servers often to reduce attribution.
- Lightweight Malware Design: Smaller payloads and multi-stage loading processes, to keep stealth.
- Coordination: Possible teaming with other DPRK threat groups to share data and split tasks.
- Attention to Geopolitical Timing: Operations often occur around key summits, sanctions or international reports that affect North Korea.
Konni’s restrained, espionage-based approach is a clear break from financially motivated groups such as Lazarus. It reflects North Korea’s intelligence-driven cyber method: quiet, systematic and persistent.
Strategic Impact
Konni’s activity reaffirms North Korea’s long-standing commitment to cyber espionage as a core way to gather intelligence. The group helps Pyongyang understand its regional political and military environment. This supports informed planning and diplomatic posturing.
From a wider view, Konni shows the growing skill of the DPRK cyber units. By focusing on South Korean policy and defense, the group meets North Korea’s need to anticipate actions in response to its nuclear and missile activity. The intelligence likely guides political talks, propaganda for home audiences and regime decisions.
The group’s technical methods are not complicated. Yet its ability to operate consistently for nearly a decade shows the operational discipline needed to achieve its goals. Like other DPRK cyber operations, it also shows the group’s ability to exist in the public eye yet remain relevant.
How can defenders reduce the risk of Konni attacks?
Proactive steps can reduce the risk of KONNI attacks through phishing awareness, network monitoring and behavioral detection:
- Email Security: Use advanced filtering and attachment sandboxing to catch malicious documents and LNK payloads.
- Use threat intelligence: Monitor IOCs for the KONNI RAT, CARROTBAT and connected domains.
- Behavioral Detection: Focus on detecting odd PowerShell or scripts, rather than relying only on signatures.
- Credentials: Set up MFA and monitor for abnormal login attempts.
- Joint Responsibility: Encourage intelligence sharing among South Korean, Japanese and allied computer incident response teams to monitor DPRK activity.
Conclusion
Konni is the persistent, disciplined part of North Korea’s cyber espionage apparatus. It lacks the financial motives of Lazarus Group and the destructive potential of Andariel. Even so, Konni’s persistent, low-profile approach has made an important contribution to Pyongyang’s worldwide intelligence goals. Its spearphishing campaigns and modular Remote Access Trojans (RATs) keep providing collections in support of the DPRK’s political and military goals.
In 2025, Konni is still active, responsive and aligned to the state’s long-term priorities. Its sustained use shows a mature North Korean cyber operation. That operation puts data dominance and continuity ahead of theatrics. For defenders, staying vigilant against this sly but persistent threat is critical to regional resilience against a possible cybersecurity incident.
You can download and review the sheet for all the details!