Crazy Evil is a Russian-speaking cybercrime group that has been active since 2021. It works as a traffer team, a group of social engineering specialists who send people to malicious pages. The goal is to install infostealer malware on Windows and macOS and steal cryptocurrency, NFTs and account logins. Its targets include Web3 projects, developers and influencers.
Cyber crime in the cryptocurrency and Web3 era has produced increasingly sophisticated threat actors. They blend scalable malware distribution with advanced social engineering. Crazy Evil is among the most prolific Russian-speaking traffer teams active today. It uses Telegram, dark web forums and a growing phishing infrastructure. This has made the group a key facilitator of global digital asset theft. This blog gives an intelligence overview of Crazy Evil: who they are, the tactics they use, what operations they conduct, and the traits that keep them a persistent threat into 2025.
Introduction: A New Breed of Cybercriminal Actor
Crazy Evil represents a new type of organized crime in the digital world. It blends traditional phishing methods with high-volume social engineering, specialized breaking and entering subteams (aka “traffers”) and multi-platform infostealer malware. While Crazy Evil is not a state-sponsored APT, the group shows operational discipline and scale similar to many established threat clusters. It particularly endangers people and organizations tied to NFT markets, cryptocurrency platforms, Web3 startups, developers and digital influencers.
Threat intelligence providers and cybersecurity vendors repeatedly note the rise in frequency and scale of financially motivated operations. These target credential theft, wallet draining and identity fraud. Crazy Evil fits this category easily. It gained monetization opportunities after rival cybercrime groups collapsed or were disrupted. It has absorbed traffers and expanded into a global network.
Who Is Crazy Evil and Why Does It Attack?
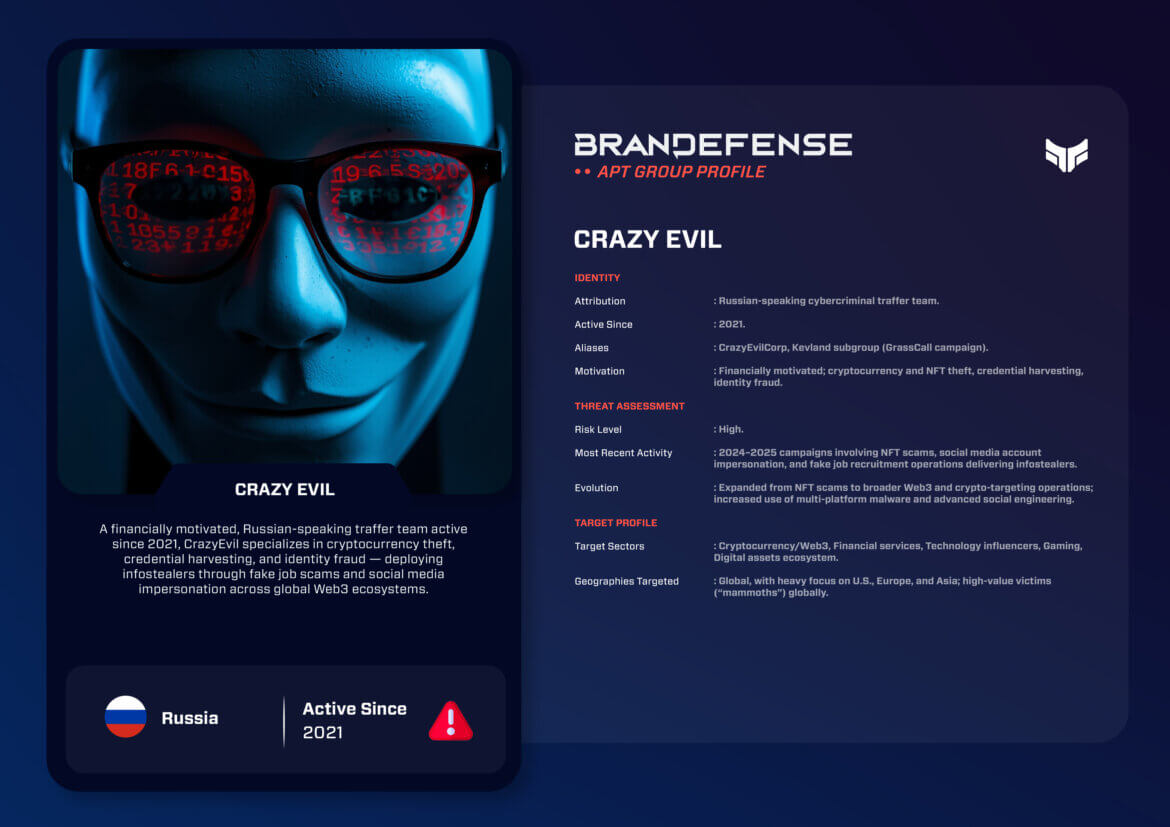
Crazy Evil is a Russian-speaking cybercriminal organization that has operated since 2021. Unlike ransomware gangs and botnet operators, it works as a traffer team. This is a decentralized team of social engineering professionals that moves legitimate web traffic towards a malicious payload.
The group has public and semi-public Telegram channels with thousands of members. Subteams like Kevland (that promote the GrassCall campaign) post dedicated lure postings, including the recent variant of fake job recruitment targeting Web3 professionals.
- Active since.
- 2021.
- Type.
- Russian-speaking traffer team.
- Subteam.
- Kevland, which promotes the GrassCall campaign.
- Targets.
- NFT markets, crypto platforms, Web3 startups, developers and influencers.
What Drives Crazy Evil?
The group’s motivations are strictly financial based on:
- Theft of cryptocurrency and NFTs
- Breaches of high-value influencer and developer accounts
- Large-scale distribution of infostealer malware
- Credential harvesting for resell/reuse in future theft
As Web3 and DeFi ecosystems expand, so do potential attacks by groups like Crazy Evil, against wallets, applications, and identities, utilizing increasingly sophisticated techniques.
How Does Crazy Evil Operate?
The organization’s cookbook covers the attack lifecycle across many levels, combining human deception with high automation of its malware.
1. Initial Access
Crazy Evil hinges predominantly on social engineering to gain access to victims, including:
- Fake NFT airdrops to promise early access
- The impersonation of influencers or founders of projects
- Phishing links sent via Telegram, Discord, X, Instagram
- Malvertising campaigns aimed at crypto-related search terms
- GrassCall job recruitment scams that fooled candidates into downloading malware disguised as entry tools
These strategies tapped into trust and excitement in a Web3 opportunity.
- Fake job offerA Web3 candidate is lured with a job interview.
- Meeting toolThe candidate is asked to download GrassCall.
- MalwareAn infostealer is installed on Windows or macOS.
- Wallet theftWallets and credentials are stolen.
2. Persistence
After malware deployed, the group established footholds by:
- Modifications of the auto-start registry (for windows)
- Launch agents (for macOS)
- Browser-based extensions for session theft
- Cloud-based theft of authentication tokens
Persistence shifts the odds in favor of prolonged access, even when the victim was aware of a compromise.
3. Command & Control
Crazy Evil prefers:
- Telegram bots to coordinate in real-time.
- An encrypted web-based dashboard to manage and facilitate the stolen data.
- Domain infrastructure frequently rotating while using fast-flux.
This decentralized approach provides increased resiliency and diminishes the risk of attribution.
4. Malware & Tooling
This group has deployed a diverse malware toolkit that is in line with modern infostealer trends:
- RedLine, Lumma, Rhadamanthys, MetaStealer (core infostealers)
- Multi-vector payloads targeting Windows and macOS
- Browser-drainer extensions
- NFT and Cryptocurrency wallet phishing kits
The group avoids many detection mechanisms built for enterprise threats. It spends its resources and time on credential theft and wallet theft rather than relying on ransomware.
Notable Operations: A Timeline of Growth
2021 – Early NFT Drainer Operations
Crazy Evil starts distributing simple wallet drainer pages associated with smaller NFT projects.
2022–2023 – Expansion Through Dark Web Recruitment
The group stabilizes an organized traffer network, accumulating over 3,000 followers on Telegram.
2024 – Mass Infection Campaigns
Multi-OS infostealers are spread through influencer-targeted scams, in thousands of cases infecting tens of thousands of users globally.
2025 – The GrassCall Job Recruitment Campaign
The new Crazy Evil subgroup calls itself Kevland, targeting job interview scams at Web3 candidates that also drain their wallets.
The scale and sophistication reached through 2025 place Crazy Evil among the most active financially motivated threat groups worldwide.
How Has Crazy Evil Changed Recently?
The recent activity of Crazy Evil demonstrates a strategic pivot:
- Expanding beyond NFTs into fintech, gaming, and online banking
- Utilizing browser extensions for long-term access
- Utilizing profiles and messages developed by AI to enhance social engineering success rates
- Increased use of cross-platform malware, suggesting more varied systems of victims
- Use of better decentralized C2 techniques similar to APT-level operational security
Such flexibility follows a wider trend in cybercrime. Criminals move quickly to improve their infrastructure and exploit the next digital ecosystem.
Conclusion: Strategic Impact and Defensive Takeaways
Crazy Evil shows how actors focused on financial gain can compete with traditional APTs in operational tempo, persistence and global reach. It focuses on high-value Web3 users and combines wide-ranging, easily deployed malware with compelling social engineering. This makes it a serious concern.
How Can You Defend Against Crazy Evil?
- Require hardware wallets for all high-value digital assets
- Educate teams on recruitment use cases targeting crypto and tech jobs
- Monitor for infostealer logs for exposed credentials and logins
- Utilize phishing-resistant MFA using FIDO2
- Audit browser extensions
- Aware for new NFT-drainer kits and wallet-draining scripts
As 2025 begins, Crazy Evil shows how quickly cyber crime can spread when it uses the excitement and volatility of the digital asset space. All organizations and individuals working with digital assets need proactive defense strategies against this adaptive adversary.
You can download and review the sheet for all the details!