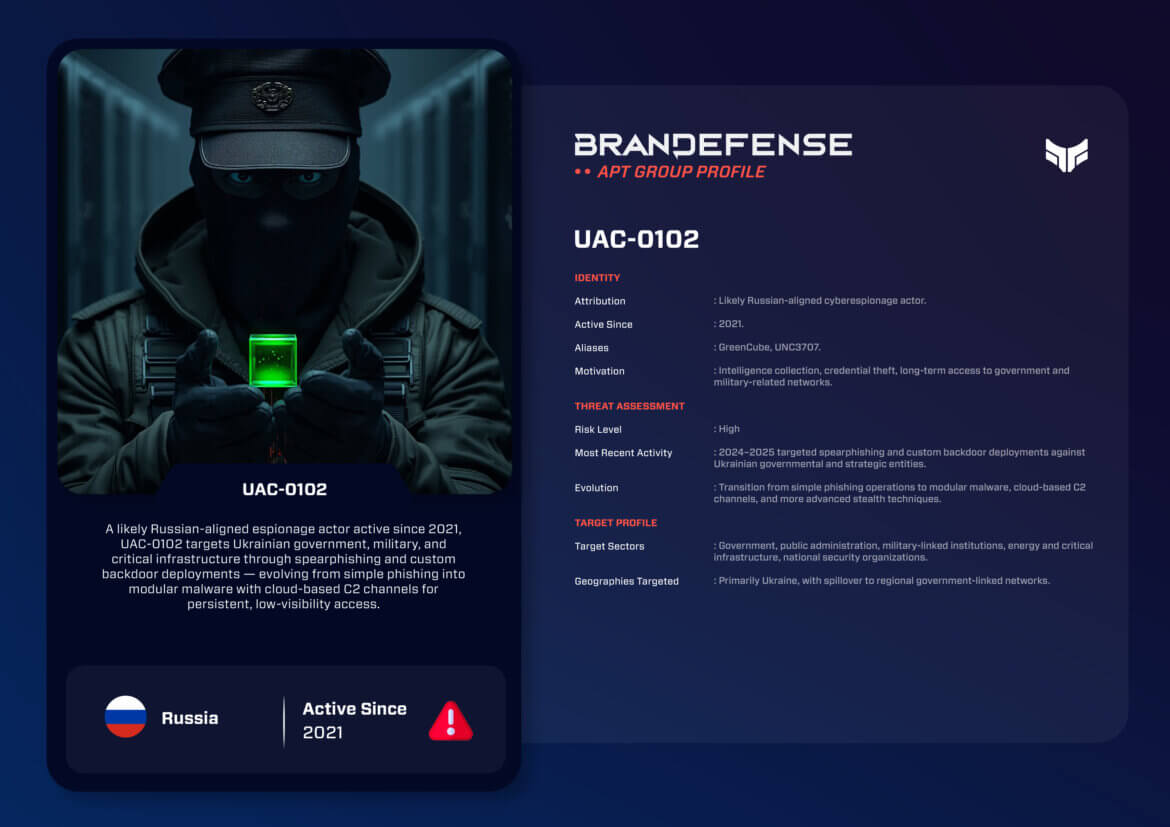
UAC-0102 is a tracking tag for a threat group that targets Ukrainian government and military organizations. CERT-UA, the Ukrainian national response team, uses UAC tags to name clusters of attacks. This profile says UAC-0102 is also called GreenCube and UNC3707, focuses on espionage, and uses phishing and cloud services for command and control. Some of these details come only from this profile.
The cyber espionage environment in Eastern Europe has changed in recent years, with more activity from several groups. One of them, UAC‑0102 (also called GreenCube or UNC3707 in this profile), is described here as focused on gathering intelligence on Ukrainian government and military bodies. It gets less media coverage than larger APT groups. This profile describes its operations as low-noise, with a focus on cloud services and a small number of well-defined targets.
This profile covers who UAC‑0102 is said to be, the techniques it is described as using, its reported history, and how to defend against it. Note that public MITRE ATT&CK group pages do not list UAC‑0102, GreenCube or UNC3707, so the aliases, the timeline and the tool details below are this profile’s account and are not confirmed by MITRE ATT&CK.
Introduction: A Quiet but Highly Targeted Actor
Compared with high-profile ransomware groups or large APT groups, UAC-0102 has a low profile. According to this profile, each campaign tends to target specific organizations. This profile links the targeting to Russian interests in Eastern Europe. It describes campaigns that use custom phishing, custom remote access tools (backdoors), and data collection from compromised organizations for intelligence rather than disruption.
Because the group has repeatedly targeted Ukrainian organizations, this profile attributes it to Russian intelligence. This attribution is made by this profile and is not stated by MITRE ATT&CK. This profile also says the group shows good operational security (OPSEC), rotates infrastructure and stages its payloads, as a traditional espionage group would.
Who is UAC-0102 and what does it want?
UAC-0102 is a tag used by CERT-UA. This profile lists the names GreenCube and UNC3707. The campaigns described indicate:
– Their primary motivation is espionage rather than financial gain.
– Their activities focus on military, government and policy-related intelligence.
– They prefer a stealthy, methodical approach over high-volume, aggressive probing.
What drives UAC-0102?
This profile sees four broad motives in the available indicators:
1. Gathering sensitive State and Military-related information
2. Monitoring Political and Administrative communications
3. Targeting political and administrative entities tied into National Infrastructure/Security frameworks
4. Sustaining long-term persistence on targeted Networks
This profile describes its way of working as deliberate and well planned, putting a high priority on staying undetected for as long as possible.
How does UAC-0102 attack? TTPs
This profile says UAC-0102 relies mostly on spear phishing, with custom malware chosen for each target organization. It says the techniques reflect steady objectives rather than brute force.
1. Initial Access: Targeted Phishing & Staged Delivery
This profile says the attackers send phishing emails designed to look like they come from legitimate government sources. Lures often include:
– Policy documents
– Military Briefings
– Communications
– Fake security alerts
The emails are said to deliver either:
– A document with a malicious macro or exploit stored in it
– A link to a staging server where the first stage of the attack is hosted
The phishing infrastructure is described as short-lived, which limits what investigators can recover afterwards. MITRE ATT&CK describes phishing as an adversary sending messages to gain access to victim systems, listed as technique T1566 under the Initial Access tactic.
2. Malware: Lightweight, Customized, and Modular
This profile says the attackers do not rely on publicly known malware. The components it names are:
– Custom backdoors for persistent access
– Reconnaissance scripts that collect system and network information
– Information stealers aimed at documents, communications and credentials
– Small, obfuscated payloads
– Payloads delivered to victims in phases
This modular approach is said to let the operators activate more capabilities on a victim once they judge its strategic value.
- Spearphishing emailLooks like a message from a government sourceTechnique T1566 (MITRE ATT&CK, opens in a new tab)
- LureA document with a macro or exploit, or a link to a staging server
- First stageSmall obfuscated payload delivered in phases
- Follow-on toolsBackdoors, recon scripts and information stealers
- CollectionDocuments, communications and credentials
3. Persistence and Lateral Movement: Quiet and Methodical
This profile lists these methods for reconnaissance and persistence:
1) Using scheduled tasks
2) Using registry run keys
3) Obtaining and using compromised credentials
4) Manipulating remote services to maintain access
Instead of spreading quickly, the group is said to pick a set of key systems to act as long-term data collection points.
4. Command and Control (C2): Cloud-Integrated Stealth
This profile calls the use of cloud services, cloud storage, legitimate websites and encrypted channels for command and control (C2) one of the group’s distinguishing traits. MITRE ATT&CK describes this general behavior as technique T1102, Web Service: using an existing legitimate external web service to relay data to and from a compromised system.
Blending C2 into public cloud services and dynamic DNS domains is said to lower the chance of detection by standard network tools.
Who does UAC-0102 target?
This profile lists these as typical targets:
- Government Ministries
- Military-affiliated institutions
- Agencies of Public Administration
- Energy, Communication, and Infrastructure sectors
- Non-Governmental Organizations (NGOs)
- Think Tanks related to Ukrainian National Security
Ukraine is the main target. This profile says some operations may also reach regional organizations involved in defense or policy-making in neighboring countries.
Notable Operations: A Timeline of Activity
This profile gives the following account of how the group developed. These dates come from this profile only and are not taken from a CERT-UA or MITRE ATT&CK record.
2021 to 2022: Emergence and Early Reconnaissance Campaigns
This profile says early reconnaissance in 2021 and 2022 used government impersonation in phishing emails sent to Ukrainian administrative networks.
2023: Development of More Mature Malware Families
This profile says lightweight backdoor and malware variants appeared from 2023 with:
– Better encryption
– More reliable C2 communication
– Broader reconnaissance than before
2024: Intensified Targeting During Regional Conflict Escalations
As regional conflicts intensified in 2024, this profile says UAC-0102 widened its targeting to:
– Governmental IT systems
– Infrastructure services
– Defense communications
2025: Expanded Use of Modular Tooling & Cloud-Based C2
For 2025 this profile reports continued use of modular tooling and more cloud-based C2, with:
– More modular backdoors
– C2 set up inside cloud environments
– Stronger obfuscation and detection evasion than before
This profile concludes that the group keeps building more resilient and stealthy capabilities.
Recent Developments: Indicators of a More Advanced Operation
This profile says these changes show how the group has become more complex over time:
– Increased use of cloud-based staging servers
– More professional spearphishing (phishing with accurate contextual information)
– More effective persistence that does not depend on typical registry paths
– More targeted data exfiltration that avoids spikes in bandwidth use
This profile says these activities increasingly resemble those of well-financed espionage organizations.
Conclusion: A High-Priority Espionage Threat
UAC-0102 is described as a modern espionage threat that favors stealth over brute force. This profile’s view is that its targeted victims and use of cloud-integrated OPSEC make it a serious threat to national security and government bodies.
- Tracked as
- UAC-0102
- Other names
- GreenCube, UNC3707 (as listed in this profile)
- Motivation
- Espionage, not financial gain
- Main targets
- Ukrainian government and military bodies
- Attribution
- Linked to Russian intelligence by this profile
- Typical method
- Targeted phishing, custom backdoors, cloud-based command and control
How can organizations defend against UAC-0102?
Organizations at risk should take the following actions:
1. Implement email authentication and anti-phishing measures.
2. Monitor for signs of abnormal cloud access.
3. Deploy behavioral endpoint detection focused on script execution.
4. Segment key assets and apply strict access control.
5. Audit regularly for unauthorized tasks and persistence artifacts.
Given ongoing geopolitical tensions, this profile expects the group’s activity to continue, which is a reason to keep an intelligence-driven defensive posture.
You can download and review the sheet for all the details!