

The NIST Cybersecurity Framework is a set of guidelines from the National Institute of Standards and Technology that helps organizations manage cybersecurity risk. Version 2.0, released in 2024, adds a sixth function called Govern to Identify, Protect, Detect, Respond and Recover. It suits organizations of any size or sector, from large enterprises to small businesses. This post explains the updates, the benefits and how it compares to ISO 27001.
The NIST Cybersecurity Framework is a full set of guidelines from the National Institute of Standards and Technology (NIST). It helps organizations manage and reduce cybersecurity risk. The updated NIST 2.0 version, released in 2024, brings key improvements.
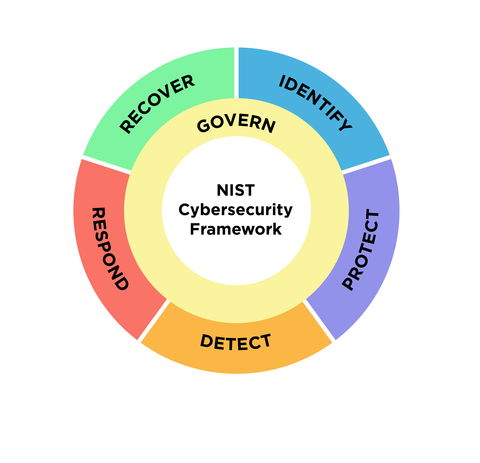
They make the framework fit changing cyber threats better. The NIST CSF has five core functions: Identify, Protect, Detect, Respond and Recover. They give a flexible and repeatable way to manage cybersecurity at scale.
Some organizations compare NIST vs. ISO 27001. Note the difference. NIST takes a risk-based approach.
ISO/IEC 27001 focuses on setting up an Information Security Management System (ISMS). Both serve similar goals.
NIST is better known in U.S. regulation, while ISO is widely used around the world. For full guidance, see the official NIST Cybersecurity Framework page.
How to use the NIST framework?
To put the NIST framework to use, start with a full self-assessment. It checks your current cybersecurity maturity, asset inventory and risk exposure. That means listing all hardware, software, data and network dependencies. It also means listing the internal and external threats that may exploit weak spots.
Once you have this baseline, map your security plan to the five core functions of the NIST 2 model: Identify, Protect, Detect, Respond and Recover. This makes cybersecurity work active and continuous, not only reactive.
The updated NIST CSF also encourages “profiles” made for each organization. They reflect its own business priorities, regulatory duties and risk tolerance. A profile works as a blueprint. It helps you rank investments, set measurable goals and build cybersecurity into enterprise-wide risk management.
The framework scales from a multinational enterprise with complex IT infrastructure to a small business with few resources. Every organization can build a strong defense posture that evolves with new threats. In the end, it is a roadmap for risk analysis, control rollout, policy writing and long-term cybersecurity governance.
- Self-assessEvaluate cybersecurity maturity, asset inventory and risk exposure.
- List dependencies and threatsIdentify hardware, software, data and network dependencies, and internal and external threats.
- Map to the core functionsFit the security strategy to Identify, Protect, Detect, Respond and Recover.
- Write profilesReflect business priorities, regulatory obligations and risk tolerances.
What’s New in NIST CSF 2.0 Compared to Version 1.1?
The release of NIST v2 brings several big updates that set it apart from version 1.1. The biggest change is a sixth core function called “Govern.” It puts strong weight on the structures, roles and responsibilities needed to oversee cybersecurity well. This function covers leadership involvement, stakeholder alignment and governance frameworks. They make sure cybersecurity is not confined to IT departments but built into the whole business.
Version 2.0 also adds sector-specific guidance, with implementation examples you can adjust. Organizations in healthcare, finance, manufacturing and energy can adopt the framework in a way that fits their industries more closely.
Another big step is that supply chain risk management and third-party oversight now sit inside the core framework. This reflects how complex and connected modern digital systems have become. These changes alter the answer to what NIST is. It is not merely a technical tool but a full governance structure.
It lines up cybersecurity with the enterprise’s mission, compliance and strategic resilience. The changes make the six NIST CSF 2.0 functions easier to act on and easier to adapt to any organization. It supports both regulatory alignment and readiness to innovate.
What Are the Core Functions of the NIST Cybersecurity Framework?
At the heart of the NIST cybersecurity framework are five basic functions. They remain the cornerstone of cybersecurity strategy in version 2.0:
- Identify asks organizations to gain deep visibility into their assets, business context, data flows and risks. This is the basis for sound security decisions.
- Protect focuses on safeguards such as access controls, data encryption, awareness training and secure software development, to lower the chance of incidents.
- Detect improves the organization’s ability to monitor systems, find anomalies and receive threat intelligence, so incidents are caught early.
- Respond prepares the organization to contain damage, reduce impact and keep talking with internal teams and outside stakeholders during a cyberattack.
- Recover restores affected systems and services quickly and efficiently, and records lessons learned so the incident does not happen again.
With NIST 2.0, the new “Govern” function sits alongside these five. It builds leadership duties, policy enforcement and performance measurement into every phase of the cybersecurity lifecycle. Together, these functions form a complete, lifecycle-based approach. It improves resilience and operational integrity when threats are constant.
Who Should Use the NIST Cybersecurity Framework?
The NIST 2.0 framework is built to apply to everyone. It suits organizations of all sizes, sectors and cybersecurity maturity levels. Large enterprises have complex infrastructure and many regulatory duties. They can use the NIST CSF to bring security policies in line across departments and countries.
They can also stay aligned with frameworks such as HIPAA, PCI DSS and federal compliance standards. Small and mid-sized businesses can scale the framework to fit their skills, resources and risk appetite. It gives them a base for practical defenses and a long-term cybersecurity roadmap.
The NIST framework was first designed for critical infrastructure, such as power grids and financial systems. It is now widely used across industries, including healthcare, education, manufacturing and government services. Its flexible design is based on outcomes. Organizations can adopt only the parts that fit their mission and grow toward fuller use over time.
Service providers and technology vendors also benefit. They can use the framework as a benchmark to check that their solutions meet what clients and regulators expect.
In short, three kinds of organization should treat the NIST CSF as a key part of their cybersecurity strategy. The first handles digital assets. The second processes personal or sensitive data. The third is part of a wider supply chain.
What Are the Benefits of Implementing the NIST Framework in Your Organization?
Organizations comparing NIST vs. ISO 27001 often like the NIST CSF for its flexibility. It does not dictate exact steps. It focuses on practical risk outcomes rather than strict procedural checklists.
One of the greatest benefits is better visibility across cybersecurity risk areas. People from IT, compliance, finance and leadership can agree on a shared language and action plan.
The framework also fits well with national and international regulations, including FISMA, GDPR and CMMC. This makes compliance reporting and audit preparation simpler. Its tiered maturity model and outcome-based metrics encourage steady improvement. They also let organizations measure their progress over time.
Using the framework also builds an active security culture. It assigns responsibilities clearly and encourages teamwork between departments, training and awareness. Cyber threats are getting more advanced and more frequent. Organizations that adopt the NIST method are better prepared to prevent, detect and recover from incidents.
This strengthens their resilience and keeps the trust of customers, regulators and partners. In the end, NIST is not just about defense. It is an adaptive, open approach to long-term digital security, driven by governance.
For newer 2026 detail, see planning a 2027 program with NIST CSF 2.0 and NIST and CISA post-quantum guidance.