
Key takeaways
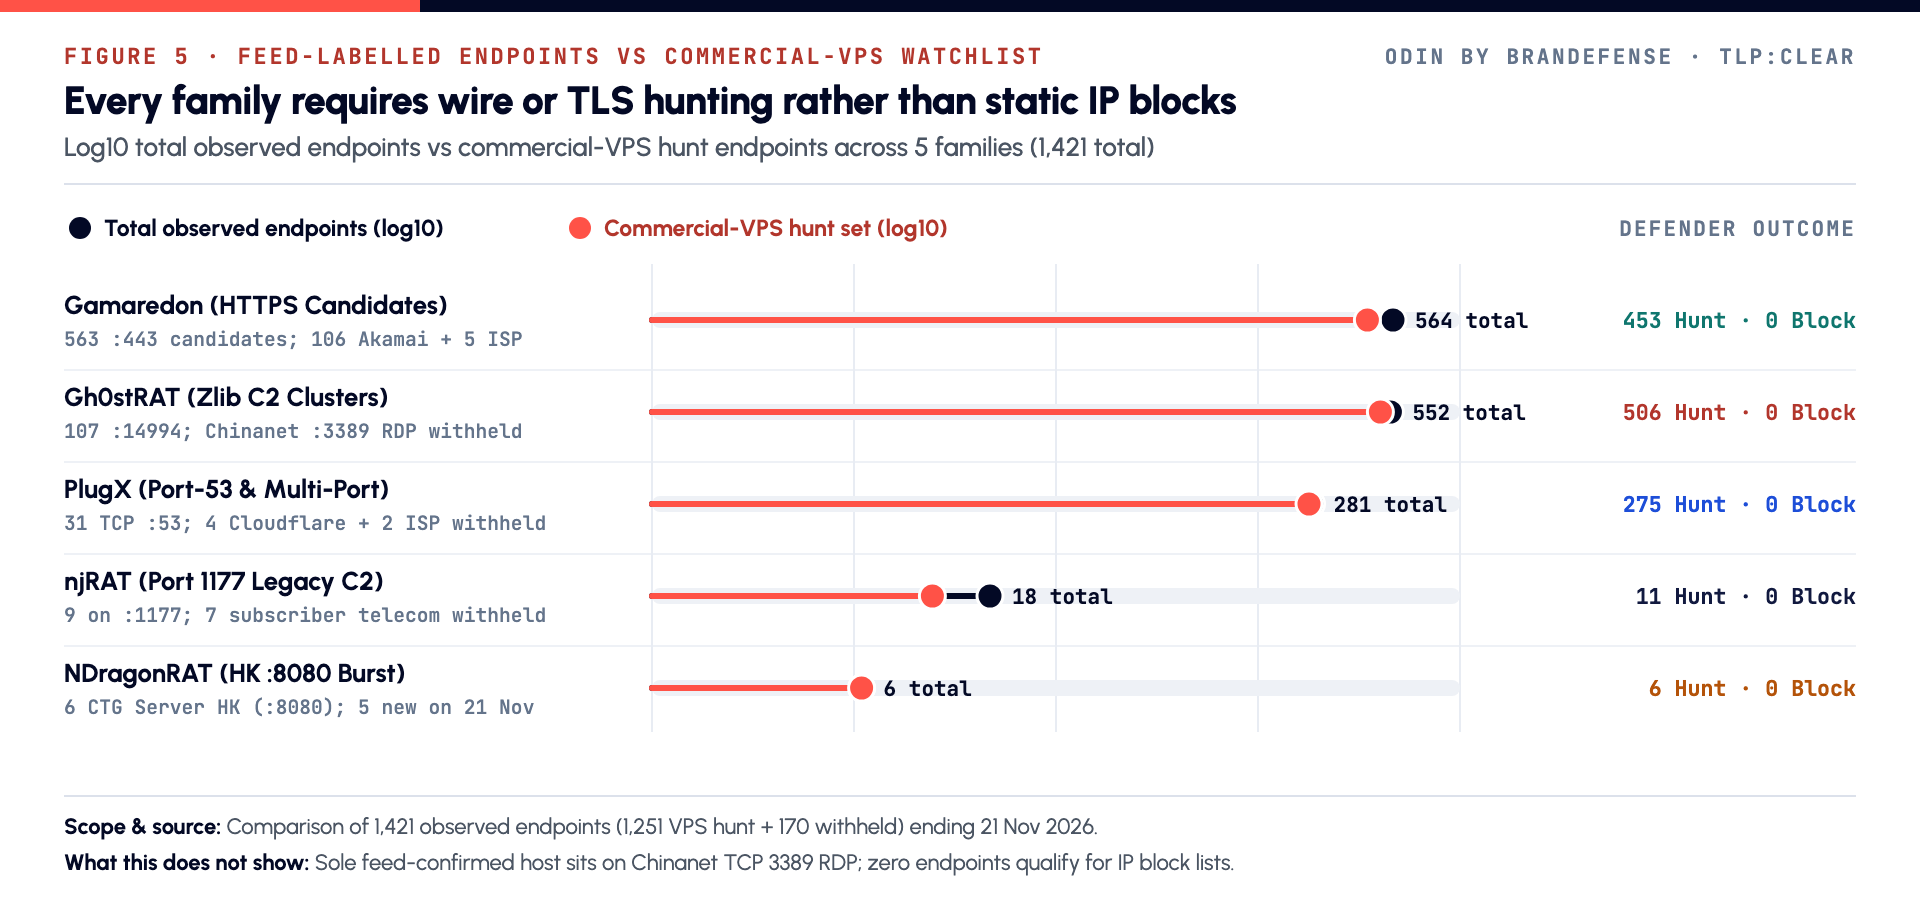
- Zero endpoints out of 1,421 examined records across Gamaredon, PlugX, Gh0stRAT, NDragonRAT, and njRAT held up for standalone firewall IP blocking.
- Gamaredon candidates place 563 of 564 endpoints on HTTPS port 443 across 517 /24 subnets, 479 of them single-host, while 106 rows collide with Akamai edge servers.
- PlugX candidates expose port 53 on 31 hosts (28 co-exposing web ports), and five port 53 hosts negotiate TLS handshakes directly on TCP port 53.
- Gh0stRAT places 107 endpoints on port 14994 and reuses CN=DcRat certificates on 11 endpoints, while five new NDragonRAT port 8080 hosts were recorded in Hong Kong on 21 November 2026.
- Block direct workstation port 53 traffic, restrict wscript and mshta HTTPS access, and deploy wire and certificate rules instead of blocking raw feed IPs.
None of the 1,421 feed-labelled endpoints, including remote access trojan (RAT) candidates, qualified for standalone IP blocking. Upstream feeds frequently tag cloud servers with family names from a single self-signed certificate, TLS server fingerprint, or port banner. Blocking those unverified lists cuts off Akamai and Cloudflare content delivery edges and broadband customers without verifying candidate relays or port-53 listeners.
Odin by Brandefense reviewed 1,421 historical feed records whose last-seen dates range from 13 June 2023 to 21 November 2026. They span 1,261 hosts and 942 /24 subnets under five upstream feed labels: Gamaredon, PlugX, Gh0stRAT, NDragonRAT, and njRAT.
Defenders can use external attack surface management to review ownership and ports, separating 1,251 commercial cloud hunt endpoints from 170 withheld CDN and telecom rows. Zero endpoints held up for standalone IP blocking after reviewing the sole feed-confirmed record on a Chinese broadband carrier running Windows Remote Desktop (3389).
This short read explains how defenders can use cyber threat intelligence to assess port-443 relay candidates, port-53 listeners, and regional RAT clusters on the wire. The full report holds the complete hosting breakdown, the eight published JARM fingerprints in the full report's Indicators tab, and the four rule files in the full report's Detection rules tab.
How do Gamaredon-labelled HTTPS candidates and PlugX port-53 listeners evade static firewall rules?
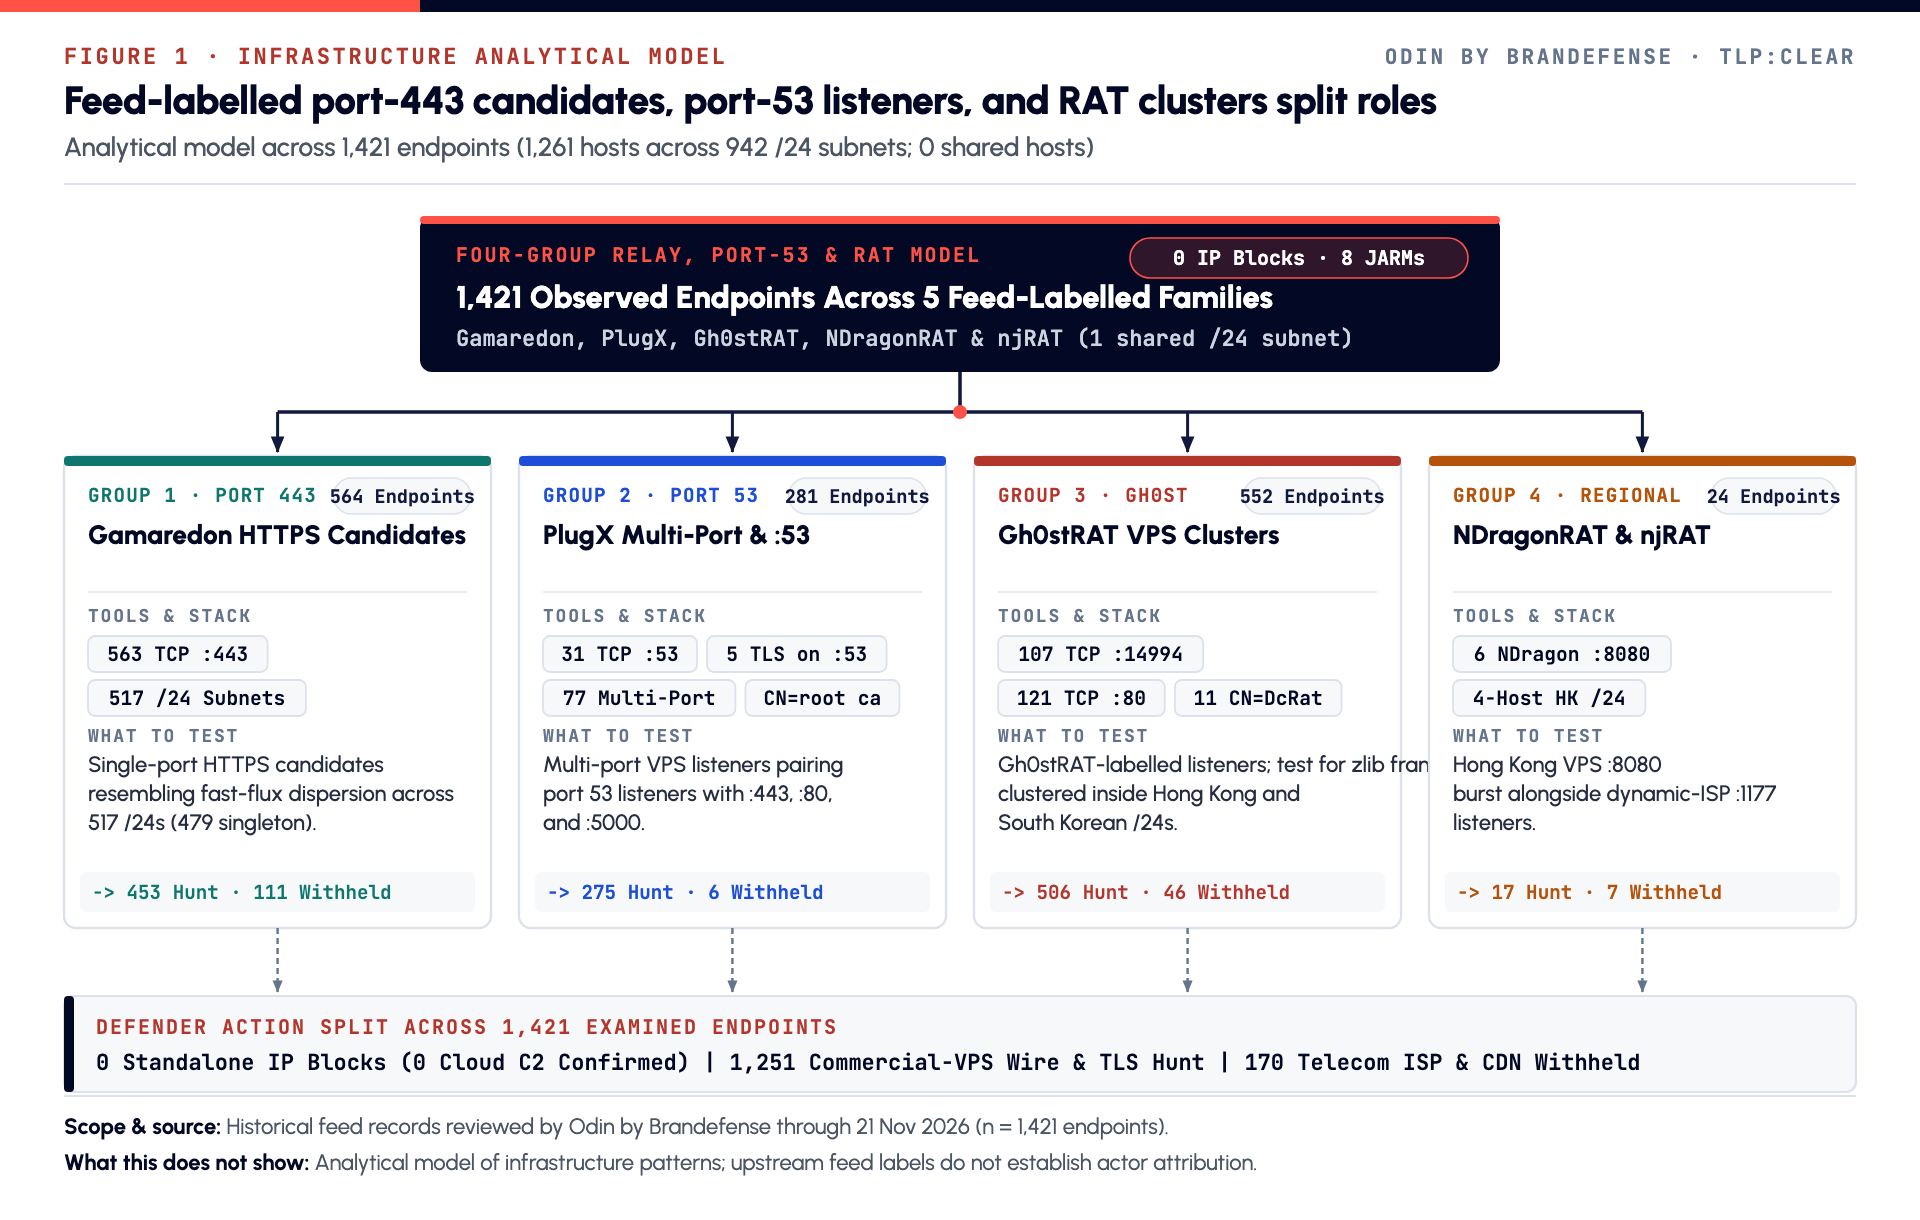
Gamaredon candidates (564 endpoints, with upstream feed record dates ending on 24 April 2025) and PlugX candidates (281 endpoints across 158 hosts) rely on opposite cloud layouts:
- Single-port port-443 distribution. Exactly 563 of the 564 Gamaredon endpoints (99.8%) listen on port 443 across 517
/24subnets, where 479 subnets hold just a single host. DigitalOcean hosts 361 endpoints (64.0%), and 22 hosts present a self-signedCN=Elasticscertificate (16 sharing JARM2ad2ad0002ad2ad22c42d42d0000008a5941c13f67e0c0a2c8a36bfeef6920). Meanwhile, 106 rows sit on Akamai edge networks on shared CDN networks, making IP block lists hazardous. - Multi-port VPS stacks and TLS on TCP port 53. Nearly half of all PlugX hosts (77 of 158, or 48.7%) expose two to five ports together across 443 (96), 80 (45), port 53 (31), and 5000 (29), with 15 serving self-signed
CN=root ca. Among the 31 port 53 hosts (30 on commercial cloud ASNs led by Amazon[.]com, Constant, and BGPNET), 28 also bind web ports (90.3%). Five PlugX port 53 hosts (plus one Gh0stRAT host) complete full TLS handshakes directly on TCP port 53 instead of standard DNS-over-TLS port 853. Plain port 53 can reflect an open DNS resolver. HTTP verbs or TLS handshakes on TCP 53 establish non-DNS framing; payload or endpoint evidence is needed to confirm a tunnel.
What links Gh0stRAT port-14994 clusters, DcRat certificates, and the Hong Kong /24 burst?
Gh0stRAT accounts for 552 examined endpoints across 515 hosts, led by port 80 (121) and characteristic high port 14994 (107 endpoints: 96 in Hong Kong and 8 in Japan). Two commercial VPS providers, CTG Server Limited (52) and Naruto (27), host 73.8% of all port 14994 listeners. Eleven Gh0stRAT-labelled endpoints across 9 hosts serve self-signed CN=DcRat certificates (10 sharing JARM 22b22b00022b22b22b22b22b22b22bd3b67dd3674d9af9dd91c1955a35d0e9), showing that commodity RAT TLS templates cross feed labels and cannot prove state attribution.
| Pattern | Family and count | Key network detail |
|---|---|---|
Top 25 /24 clusters | 22 Gh0stRAT + 3 PlugX clusters (187 endpoints) | Dense Asian VPS blocks on MOACK[.]Co[.]LTD (KR), CTG Server (HK), and Naruto (HK, JP) |
| Hong Kong :8080 burst | 6 NDragonRAT hosts on CTG Server Limited | Five new port 8080 hosts on 21 November 2026: four in one /24 and one in a shared Gh0stRAT /24 |
| Port 1177 split | 18 njRAT hosts across 18 /24 subnets | Nine listen on port 1177, including five on PALTEL and Saudi Telecom broadband lines |
Even TLS server fingerprints cross all five labels. Windows SChannel JARM 14d14d16d14d14d08c14d14d14d14dfd9c9d14e4f4f67f94f0359f8b28f532 appears on 75 endpoints across all five families despite zero shared hosts, fingerprinting default Windows Server TLS settings on rented virtual machines. Zero hosts overlap across the five families, so Figure 1 frames their four groups strictly as an analytical model.
What to do now
- Block direct outbound UDP and TCP port 53 traffic from workstations and servers outside internal DNS forwarders, and inspect allowed TCP 53 trunks for
HTTP/1.1or TLSClientHellopackets. - Prevent
wscript.exe,cscript.exe, andmshta.exefrom opening direct internet HTTPS sessions, and block unsignedrundll32.exeorregsvr32.exeside-loading inC:ProgramDataandC:WindowsTemp. - Deploy the Suricata, Sentinel KQL, Sigma, and YARA rules from the full report's Detection rules tab to catch
Gh0st+ zlib|78 9c|streams,njRATport 1177 check-ins, andCN=ElasticsorCN=DcRatcertificates. - Keep Akamai, Cloudflare, telecom ISPs, RDP port 3389, mail ports (465, 993, 995), and standalone JARM matches out of firewall block lists, using the eight JARM fingerprints in the full report's Indicators tab strictly for hunting.
What is…?
Short explanations of the tools and families named in this study.
What is Gh0st RAT?
Gh0st RAT is an old remote access trojan whose source code leaked, producing many variants used by criminal and state actors.
More about Gh0st RATRemote access trojanWhat is PlugX?
PlugX is a modular remote access trojan used by several China-nexus groups for over a decade, often loaded through DLL side-loading.
More about PlugXTechniqueWhat is JARM?
JARM is an open TLS server fingerprinting method from Salesforce. It hashes how a server answers a set of crafted TLS handshakes.
More about JARMFrequently asked questions
How do Gamaredon-labelled HTTPS candidates and PlugX port-53 listeners evade static firewall rules?
Gamaredon candidates (564 endpoints, with upstream feed record dates ending on 24 April 2025) and PlugX candidates (281 endpoints across 158 hosts) rely on opposite cloud layouts:
What links Gh0stRAT port-14994 clusters, DcRat certificates, and the Hong Kong /24 burst?
Gh0stRAT accounts for 552 examined endpoints across 515 hosts, led by port 80 (121) and characteristic high port 14994 (107 endpoints: 96 in Hong Kong and 8 in Japan). Two commercial VPS providers, CTG Server Limited (52) and Naruto (27), host 73.8% of all port 14994 listeners. Eleven Gh0stRAT-labelled endpoints across 9 hosts serve self-signed CN=DcRat certificates (10 sharing JARM 22b22b00022b22b22b22b22b22b22bd3b67dd3674d9af9dd91c1955a35d0e9), showing that commodity RAT TLS templates cross feed labels and cannot prove state attribution.