

A security vulnerability called “cross-tenant” has been detected by Datadog researchers in AppSync, a popular Amazon Web Services (AWS) tool. AppSync is a popular AWS service that allows developers to quickly create GraphQL and Pub/Sub APIs.
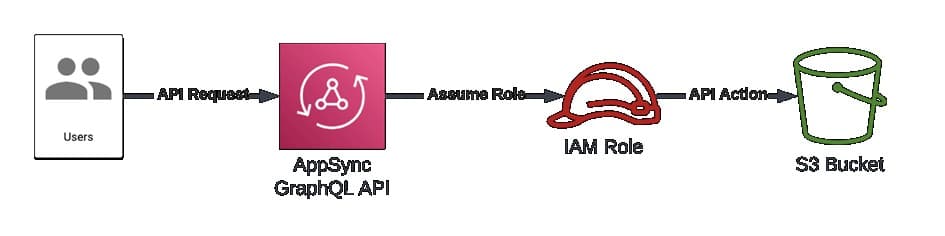
The vulnerability is due to a case-sensitivity parsing issue of the AppSync service that could potentially be used to bypass cross-account role usage validations and act as a service on customer accounts. Successful vulnerability exploitation allows threat actors to assume Identity and Access Management (IAM) roles in other AWS accounts.
The vulnerability detected on September 1, 2022, was immediately reported to AWS. AWS, which rescheduled the attack, verified the impact of the vulnerability and released a fix that fixed it. In addition, Amazon released a statement on Monday, November 21, confirming the details of the vulnerability and stating that no customers were affected by the vulnerability. There is no action for Amazon customers to take due to the vulnerability.
How did the AppSync flaw work?
Datadog Security Labs explains the root cause in its disclosure write-up. When a user creates a data source in AppSync, the service checks that the serviceRoleArn belongs to the caller’s own account. That check was tied to the exact spelling of the property name. If the researchers sent the same property with different letter casing, such as servicerolearn, the check was skipped but the service still used the value. AppSync then accepted a role ARN from another account.
Datadog calls this a confused deputy problem. A low-privileged user got AppSync, a service with more privileges, to act on their behalf. To use it, an attacker needed the ARN of a role in the victim account that trusts appsync.amazonaws.com. With that, the attacker could create a data source and a resolver in their own API. When the API ran, AppSync assumed the victim’s role and made the calls. The role’s own permissions limited what the attacker could reach.
What is the timeline?
- 1 September 2022: Datadog reports the issue to AWS.
- 2 September 2022: AWS reproduces the attack and confirms the impact.
- 6 September 2022: AWS deploys a fix to the AppSync service, and Datadog checks it.
- 21 November 2022: Coordinated public disclosure.
Were customers affected?
AWS says no. Its security bulletin AWS-2022-009 states that a review of logs back to the launch of the service found activity only between accounts that belonged to the researcher. AWS fixed the flaw inside the service, so customers have nothing to patch.
What can teams still learn from it?
Cloud teams can use this case to review roles that trust AWS services. Datadog points out that CloudTrail shows AssumeRole events with appsync.amazonaws.com as the caller, so misuse looks like normal AppSync activity. It suggests watching for spikes in AccessDenied events from AppSync and for unusual API calls from roles that trust the service. Keeping role permissions narrow limits the damage if a similar flaw appears in another service.