

SonicWall has released security updates that address a critical vulnerability that affects Firewall solutions. An unauthenticated, remote threat actor could exploit this vulnerability to execute arbitrary code and trigger a denial of service (DoS) condition on the vulnerable system.
The vulnerability tracked code CVE-2022-22274 exists due to a stack-based buffer overflow error in SonicOS’s web management interface that could cause remote code execution or a denial of service via a specially crafted HTTP request.
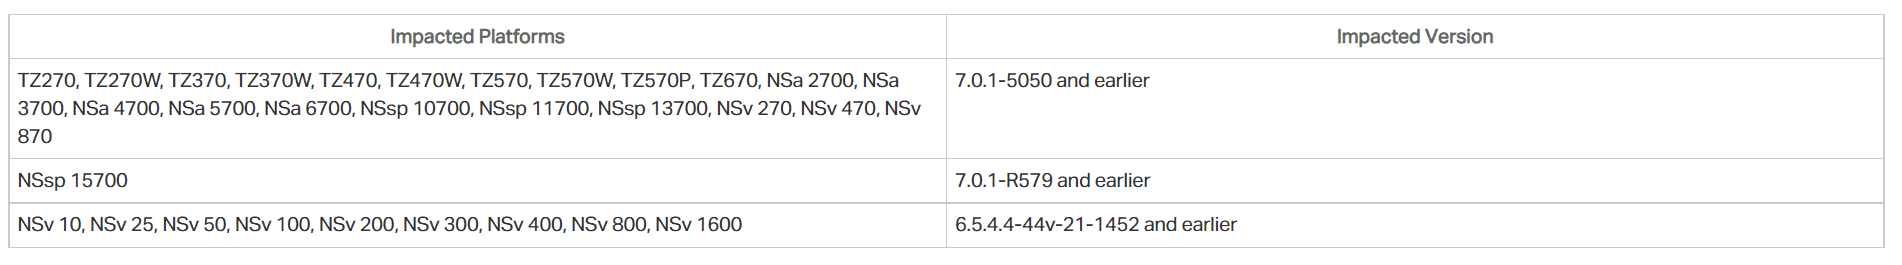
The critical vulnerability affects 31 different SonicWall Firewall solutions running the versions listed in the table below.
SonicWall stated that no evidence has yet been found for active exploitation of the vulnerability. To not be the target of attacks that can be carried out using the vulnerability, it is recommended that users who use vulnerable versions immediately apply updates that fix the vulnerability. Additionally, until updates are implemented, SonicWall advises customers to limit SonicOS management access to trusted source IP addresses.
What do the official records say about CVE-2022-22274?
The U.S. National Vulnerability Database lists CVE-2022-22274 as a stack-based buffer overflow in SonicOS. A remote attacker with no login can send an HTTP request and cause a denial of service. The same request could also lead to code execution on the firewall. The record was published on 25 March 2022 and carries a CVSS 3.1 base score of 9.8, which is the Critical rating. The vector is network based, needs no privileges and needs no user action. That is why the score sits so near the top of the scale.
SonicWall describes the flaw in its own security advisory, SNWLID-2022-0003. The vendor advisory is the place to check the exact list of affected models and the fixed firmware versions for each one. Do not rely on a summary like this one for version numbers.
Why does a firewall flaw matter so much?
A firewall sits at the edge of the network. It decides what gets in and what stays out. If an attacker takes control of it, the attacker sits in the most trusted spot of the network. A crash is also costly, because a firewall that stops working can cut off a whole site from the internet.
The affected part here is the web management interface. This is the page that administrators use to configure the device. When that page is reachable from the internet, anyone can send it requests. This flaw needs only one specially crafted request and no password.
What should you do now?
- Find out which SonicWall firewalls you run, and which SonicOS version each one uses. Compare them with the table in the SonicWall advisory.
- Install the fixed firmware on every affected device. SonicWall says it has found no sign of active exploitation so far, but that can change once details spread.
- Until you can update, limit management access to trusted source IP addresses, as SonicWall advises.
- Check whether the management page is open to the whole internet. If it is, close it. An external attack surface management scan shows which management pages are exposed to outsiders.
- Watch for news of exploitation. Cyber threat intelligence feeds tell you when attackers start to use a flaw like this one, so you can move it up your patch list.
Sources: NVD record for CVE-2022-22274 and SonicWall advisory SNWLID-2022-0003.