


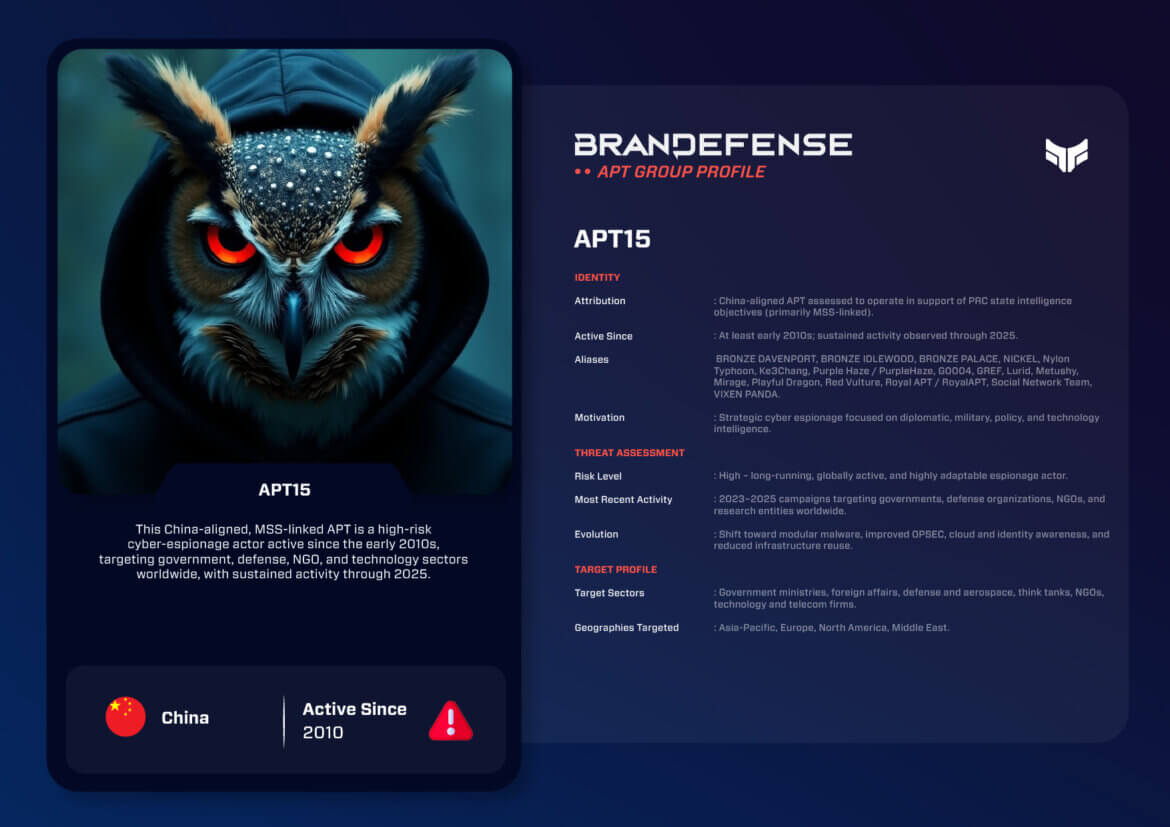
APT15 is a China-aligned advanced persistent threat group. It is also tracked as Ke3chang and Nylon Typhoon. It runs long-term cyber espionage. MITRE ATT&CK attributes it to actors operating out of China. It mainly targets government, diplomatic, defense and NGO organizations. Its aim is to collect intelligence, not to make money or cause damage.
Other China-linked groups with threat group profiles include APT40, APT41, APT27 and APT19.
APT15 is also known as BRONZE DAVENPORT, BRONZE IDLEWOOD, BRONZE PALACE, NICKEL, Nylon Typhoon, Ke3Chang, Purple Haze / PurpleHaze, G0004, GREF, Lurid, Metushy, Mirage, Playful Dragon, Red Vulture, Royal APT / RoyalAPT, Social Network Team and VIXEN PANDA. It is one of the longest running, most complex China-aligned advanced persistent threat (APT) Groups. The group has operated for over a decade. It has been tracked under many different aliases. These represent a large set of linked campaigns, not a single, static entity .
The group has lasted long, used many tools and reached targets worldwide. This marks its role in the wider Chinese cyber espionage scene. The major focus of APT15 has remained on gathering intelligence. It does not engage in disruption or financial cybercrime. So it closely aligns itself with China’s diplomatic, military and strategic interests . This profile outlines APT15’s identity, motivations, cyber operations and strategic impact.
What is APT15 and who is behind it?
APT15 (sometimes referred to by other names) is thought to be tied to the Chinese state. It has a close relationship with such entities as the PRC Ministry of State Security. APT15 has been tracked over time. Many security vendors and research agencies have tracked the same or similar activities. This led to a large number of aliases for the APT15 actor.
Different names have been used to describe APT15 activity. Still, several traits can be found across all of it:
- Long-term, intelligence-based campaigns
- Predominantly government and diplomatic targets
- Consistent use of specially developed malware types
- Patience and operational security
APT15’s primary focus is strategic cyber espionage. The goal is to get information needed to support Chinese foreign policy, defense planning and domestic security goals. It also seeks to expand China’s influence in the region. APT15 has little to no interest in financial gain. It does not take part in destructive operations.
- Also tracked as.
- BRONZE DAVENPORT, NICKEL, Ke3Chang, Nylon Typhoon, VIXEN PANDA.
- Focus.
- Strategic cyber espionage.
- Typical targets.
- Government, diplomatic, defense, NGO and think tank organizations.
- Active.
- Over a decade.
- Not interested in.
- Financial gain or destructive operations.
Tactics, Techniques, and Procedures (TTPs)
APT15 demonstrates mature and adaptive tradecraft, combining traditional espionage techniques with continuous technical evolution.
How does APT15 gain initial access?
APT15 often gains access in these ways:
- Targeted email phishing campaigns to diplomats, officials and researchers. These emails are themed around government relations, policy, conference invitations and media requests.
- Weaponized documents. They are designed to exploit known vulnerabilities or take advantage of trusted document formats.
- Sometimes they are able to compromise exposed internet-based services, especially in government networks.
The volume of these campaigns is low. But they are highly contextualized, because APT15 conducts extensive reconnaissance on their targets.
Execution & Malware Tooling
APT15 first gets into the target network. Then it deploys a variety of custom and semi-custom malware programs. These include:
- Ke3Chang (backdoors that allow for remote command execution and data theft)
- Modular loaders that can directly execute payloads from memory
- Credential harvesting tools aimed at browsers, email clients and operating systems
- Proxy and tunneling solutions that provide lateral movement within the environment, as well as covert access
The malware developed by this group is frequently modified and/or recompiled. This helps it avoid signature-based detection.
Persistence
APT15 uses multi-layered persistence methods to keep long-term access to compromised hosts. These include:
- Registry autorun keys and scheduled tasks
- DLL sideloading by using validly signed executables
- Installation of services presented as benign system components
- Redundant persistence routes that allow the group to survive cleanup operations
- Targeted phishingEmails to diplomats, officials and researchers
- Custom malwareBackdoors and loaders run payloads from memory
- PersistenceAutorun keys, scheduled tasks and DLL sideloading
- Covert C2HTTPS traffic blended with normal web traffic, kept low in volume
- Slow data theftData is staged, compressed, encrypted and sent out slowly
Command and Control (C2)
The Command and Control (C2) infrastructure of APT15 has these characteristics.
1. Resilience and Stealth:
- HTTPS Communications are encrypted and blended with normal web traffic
- Use of Compromised Servers and Dynamic DNS Services
- Frequent Rotation of Domains and IP Addresses
- Multi-hop Proxy Chains to Obfuscate the Operator’s Location
2. C2 Traffic Volume:
- C2 Traffic is kept to a Low Volume, which decreases the likelihood of triggering Network-Based Alerts
Defense Evasion
Defense Evasion is one of APT15’s Primary Strengths:
- Obfuscation and Encryption of Malware Payloads
- Utilizing Native System Tools for Living off the Land Techniques
- Minimal Reuse of Malware Artifacts and Infrastructure
- Timing of Execution of Operations to Avoid Peak Monitoring Times
These evasion techniques also make APT15 hard for traditional security controls to detect.
Data Collection & Exfiltration
APT15 does not perform every type of data collection and exfiltration. It is focused on collecting Intelligence Value, rather than Bulk Data Theft. Examples of Targeted Data Collections include:
- Communications from Government to Government
- Documents Maintaining Strategy
- Research
- Credentials and Access Preparation for Future Operations
All of the collected data is Staged, Compressed and Encrypted. It is then Slowly Exfiltrated. This avoids DLP (Data Loss Prevention Equipment) and Anomaly Detection Systems.
What operations has APT15 carried out?
APT15 has carried out numerous high profile espionage campaigns for many years now.
Diplomatic and Government Espionage
APT15 has consistently attacked foreign ministries, Embassies and inter-governmental organizations. By breaking into these institutions, APT15 was able to obtain information related to diplomatic negotiations between China and its allies. It also obtained other policy discussions concerning China.
Defense and Security Sector Targeting
APT15 continues its targeted attacks on defense contractors and security-related entities. These security breaches gave APT15 access to sensitive military strategy documents, research data, and communications regarding military modernization and regional security.
NGO and Think Tank Surveillance
APT15 has targeted think tanks, NGOs, and academic institutions involved with studying China, regional conflict, and human rights issues. This furthers PRC’s objectives in the area of internal security and narrative management.
Global Reach Campaigns
APT15 has been linked to APT15 activities that span the globe. They span Asia Pacific, Europe, North America and the Middle East. This indicates that APT15 has a global operational presence.
Recent Developments (2022–2025)
APT15 has continued to develop and show increased sophistication in operations over the last few years. Specifically, APT15 now uses unique campaigns for each of its active operations. This is not typical of their prior operational security practices. APT15 has also made its malware frameworks more complex. They are more modular in design. This lets APT15 create tools specifically designed for specific targets (i.e. based on their target’s characteristics). Furthermore, APT15 has created a hybrid approach to targeting systems in both on-premises and cloud environments (e.g. identity and endpoint access instead of focusing solely on the exploitation of networks). Finally, many APTs associated with the People’s Republic of China (PRC) have been publicly exposed and are becoming less active. APT15 continues to be active. APT15 has no indications of slowing down in terms of strategic tasking.
Strategic Impact
APT15’s significance to China’s long-term strategy for collecting intelligence from foreign sources cannot be overstated. There are several ways in which the group can aid the PRC in collecting information. This covers its political and diplomatic goals, conducting military operations, developing emerging technologies, and monitoring specific NGOs and think tanks that represent competing viewpoints or interests. Hence, APT15 will always remain at the forefront of China’s strategy of targeting foreign government entities for intelligence collection. This is due to their continued existence and the amount of information collected by APT15..
Conclusion
APT15, which has also been called BRONZE DAVENPORT, NICKEL, Ke3Chang, Nylon Typhoon, VIXEN PANDA, and various other names, is one of the most flexible and long-lasting China-oriented cyber intelligence organizations. It can adapt, work in hidden ways and act worldwide, and has done so for longer than ten years. So both the technical development of their tools and the importance of the strategy of this organization has never been more pertinent.
It will continue to stay a prominent risk as we enter a time of greater international competition. Digital infrastructure is becoming an even more critical component of national powers. To mitigate risks of such an organization requires significant workforce, enhanced behavioral detection, aggressively patching and an ongoing threat intelligence program. More so, corporations should realize that the most dangerous adversaries are those who may go about their operations in a very stealthy manner, taking calculated risks and with strategic purpose.
- Behavioral detectionMalware is often modified to avoid signature-based detection.
- Aggressive patchingKnown vulnerabilities are used in weaponized documents.
- Threat intelligence programAn ongoing program to track the group.
You can download and review the sheet for all the details!
For another long-running espionage group with a thin public record, see our APT18 threat group profile. It is also known as Dynamite Panda and Wekby.