Introduction
APT40 (also Leviathan and Gingham Typhoon) is a Chinese cyber espionage group that MITRE ATT&CK says has been active since at least 2009. The US and UK governments (2021) and agencies in eight countries (2024) attribute it to China’s Ministry of State Security.
| Also known as | Leviathan, Gingham Typhoon, MUDCARP, Kryptonite Panda, BRONZE MOHAWK, TEMP.Periscope |
| Attributed to | China's Ministry of State Security (MSS), Hainan State Security Department |
| Attributed by | US and UK governments (2021); agencies in Australia, Canada, Germany, Japan, New Zealand, South Korea, UK and US (2024) |
| Active since | At least 2009 (MITRE ATT&CK) |
| MITRE ATT&CK ID | G0065 |
| Main targets | Maritime, naval, defense, government, academia, healthcare and manufacturing |
Full sources, timeline and government actions are in the APT40 threat group profile.
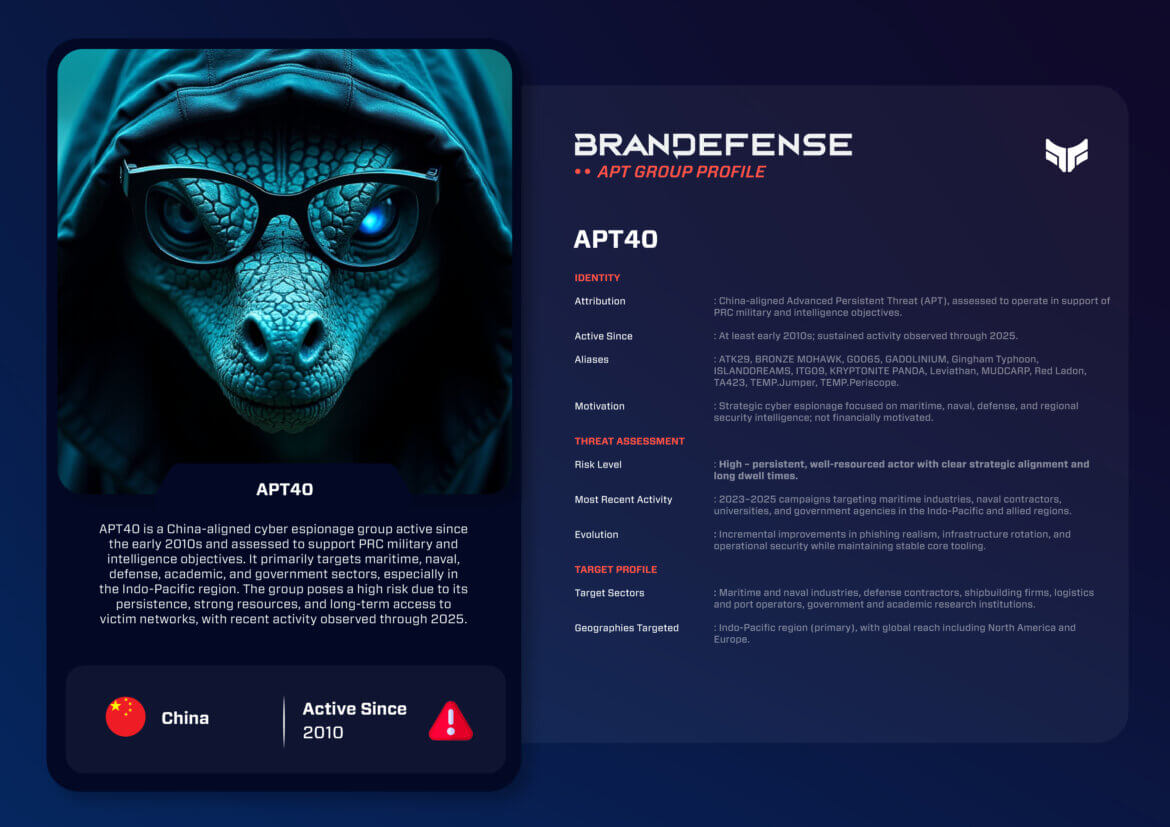
APT40 is a sophisticated, established cyber espionage organization. It has been active for over 15 years and is widely believed to have ties to the People’s Republic of China (PRC). Throughout its existence, the group has consistently targeted organizations in the maritime, naval and defense sectors. It has focused on entities linked to the South China Sea, Indo-Pacific security and international naval logistics. With over a decade of cyber operations, APT40 has developed a distinct set of working practices. It has a systematic approach to gathering intelligence and a clear alignment to Chinese military and strategic priorities.
APT40 operates under many aliases, including ATK29, BRONZE MOHAWK, GADOLINIUM, Gingham Typhoon, Leviathan, TA423 and TEMP.Periscope. This shows how threat actor names are often fragmented across security organizations. Despite the many names, most cyber security experts agree that APT40 is a single, coherent threat actor. Its mission is to support China’s naval modernization and expand its regional influence through long-term cyber espionage. This blog gives a detailed analysis of APT40’s history, identity, motivations, tactics, significant operations and overall impact.
- Aliases.
- ATK29, BRONZE MOHAWK, GADOLINIUM, Gingham Typhoon, Leviathan, TA423, TEMP.Periscope.
- Active.
- Since at least 2009, per MITRE ATT&CK.
- Attributed by.
- MITRE ATT&CK and CISA, to China’s Ministry of State Security.
- Main targets.
- Maritime, naval and defense sectors.
- Focus.
- South China Sea, Indo-Pacific security, naval logistics.
Who is APT40 and what does it want?
APT40 is assessed to be a cyber espionage group (CEG) with links to Chinese military or intelligence agencies. It is believed to have connections to the People’s Liberation Army Navy (PLAN) and to other defense-related research groups.
APT40 has been active since the beginning of the decade until at least 2025.
The group’s objectives are to collect intelligence rather than to seek profit or monetary gain (financially). Therefore, the group’s primary focus will be on the following:
- The collection of sensitive information regarding naval and maritime activities
- The tracking of defense contractor and shipbuilders’ activities
- The monitoring of government activities that are related to the disputes in the South China Sea
- The preparation of the intelligence that they will need to meet the military objectives that they may encounter.
The countries and regions targeted by the group represent APT40’s Maritime Strategic priorities.
What tactics does APT40 use?
The techniques and procedures of APT40, an advanced persistent threat group, rely on predictable, reusable methods. They favor consistency over unique or opportunistic approaches.
Initial Access
APT40’s primary methods of gaining initial access are through:
- Spearphishing emails containing content related to maritime, defense, and logistics
- Impersonating journalists, researchers, or event organizers
- Sending malicious attachments, and/or sending users links to credential harvesting websites
- Exploiting known vulnerabilities associated with public Internet-facing applications
The group typically targets individuals working in engineering, analyst and purchasing roles, as well as maritime research positions.
- Initial accessSpearphishing, or exploiting public-facing applications
- ExecutionCustom remote access tools, PowerShell and WMI
- PersistenceRegistry run keys, scheduled tasks, several back doors
- Command and controlEncrypted HTTPS, fallback domains, compromised servers
- Defense evasionObfuscation, legitimate admin tools, slow low-volume data theft
Execution & Tooling
After APT40 has established access, the group uses:
- Custom built remote access tools, including ISLANDDREAMS and MUDCARP (modular)
- Lightweight remote access tools to execute commands and perform reconnaissance
- Scripting languages such as PowerShell and Windows Management Instrumentation (WMI)
All malware developed by the group is generally considered very stable and produces minimal noise, allowing for long-term usage.
Persistence
APT40’s methods of persistence include:
- Registry run keys and scheduled tasks
- Using legitimate appearing software to install services
- Using multiple back doors to allow for redundancy between back doors, thus allowing Alternative Methods of Access to persist through system reboots and partial remediation.
Command and Control (C2)
A typical APT40 C2 infrastructure includes:
- Encrypted HTTPS communications
- Hard-coded fallback domains
-Use of compromised servers and VPS infrastructure.
C2 servers are usually hosted in geographical areas that can be hidden from normal victim traffic patterns.
Defense Evasion
Defense evasion techniques APT40 employs include:
- Code obfuscation of malware and configuration files
- Leverage administrative tools that would otherwise be legitimate if not for the ransomware (LOLBins)
- Minimizing lateral movement to better avoid detection
- Utilizing a slow-release, low-volume method to exfiltrate data.
Notable Operations
APT40 has participated in numerous high-profile hacking campaigns.
Global Maritime and Naval Targeting
The group has a strong interest in stealing information from:
- Naval design companies
- Companies that build and maintain vessels
- Research institutions engaged in the study of maritime issues
- Shipping and marine logistics companies
The stolen information from these attacks can include data about vessel design, ship maintenance schedules and the naval operational capabilities associated with a particular vessel.
Government and Defense Espionage
APT40 has hacked into government and military organizations in countries involved in maritime disputes with China.
The data stolen from these organizations can include:
- Documents related to military policy
- Documents relating to the planning of military operations
- Communications related to the security of regional partners.
Academic and Research Surveillance
Universities and think tanks that are focused on the research of maritime law, naval strategy, and regional security have been frequent targets of APT40.
Phishing campaigns impersonated:
- a collaborator (e.g., a professor)
- a journalist that was seeking an interview
- a conference invitation.

Recent Developments (2023–2025)
Over the past few years, APT40 has kept the same methodology described above. The group has, however, made small changes to how it operates. It has improved its social engineering with more sophisticated phishing emails. These are aimed at specific individuals, look polished and are better localized than before. This gives targets a stronger reason to open the malicious emails.
C2 domain rotation has also improved. The group works faster and reuses malware samples less often from one operation to another.
APT40 is actively widening its scope beyond purely maritime targets. It now also targets aerospace suppliers, advanced manufacturing, and government agencies that are not specifically involved in defense.
Strategic Impact
However, the original intent behind APT40’s operations has not changed. The group still focuses on gaining access to the kind of information that will give China military superiority over its adversaries.
Military Advantage:Acquiring access to Naval Engineering and Logistics supports China’s modernization and operational planning of its Navy.
Regional Security Risk: Surveillance of all governments involved in South China Sea disputes provides China with improved diplomatic and Military Superiority.
Economic and Industrial Espionage: Taking Intellectual Property from the Western countries reduces the Timeframe to develop equivalent products for China’s Defense and Maritime Industries.
Persistent Threat Environment: APT40 is an example of a patient and methodical threat actor. It can keep control of access to data for long periods.
Conclusion
APT40 is still one of the most sophisticated and strategically-minded state-sponsored groups that conduct cyber-espionage on behalf of the Chinese government today. The group uses well-planned spear phishing campaigns and reliable malware, and it has a clear connection to maritime and defense priorities. For many years it has provided valuable intelligence to Chinese leaders.
As tensions in the Indo-Pacific region continue to escalate, organizations involved in maritime security, defense manufacturing, logistics and policy research should expect APT40 to be very active over the coming months and years. To protect against this threat, organizations need to:
- Implement strong email security protocols
- Provide ongoing monitoring of user activity
- Make all users in high-risk roles aware of the threats to their environment
- Develop and deploy long-term threat intelligence strategies
APT40’s longevity and its consistent focus on providing intelligence to the Chinese government show how cyber espionage serves as an effective instrument of statecraft by governments around the world.
You can download and review the sheet for all the details!