

Callisto is a Russia-based cyber espionage group, also known as COLDRIVER, SEABORGIUM, Star Blizzard and TA446. UK, US and allied agencies assess it is almost certainly subordinate to the Russian FSB (Center 18). It uses spear-phishing to steal email credentials from governments, defense bodies, think tanks, NGOs and academics, mainly in NATO countries.
Introduction
The Callisto Advanced Persistent Threat (APT) group is also called COLDRIVER, SEABORGIUM, TA446, and UNC4057. It is one of the best-known spy groups tied to Russia. Since at least 2019 (MITRE ATT&CK), Callisto has steadily targeted governments, defense bodies, think tanks, NGOs, and universities. Most of its targets are linked to NATO and European security policy.
Unlike ransomware crews or groups that want money, Callisto gathers intelligence over the long term. This supports Russian strategic goals. Its usual techniques are credential harvesting, spear-phishing with flawless lures, and abuse of cloud tools to stay in place.
This blog covers who Callisto is, how it works, and its notable operations. It also covers how its campaigns affect international security.
Who is Callisto and what motivates it?
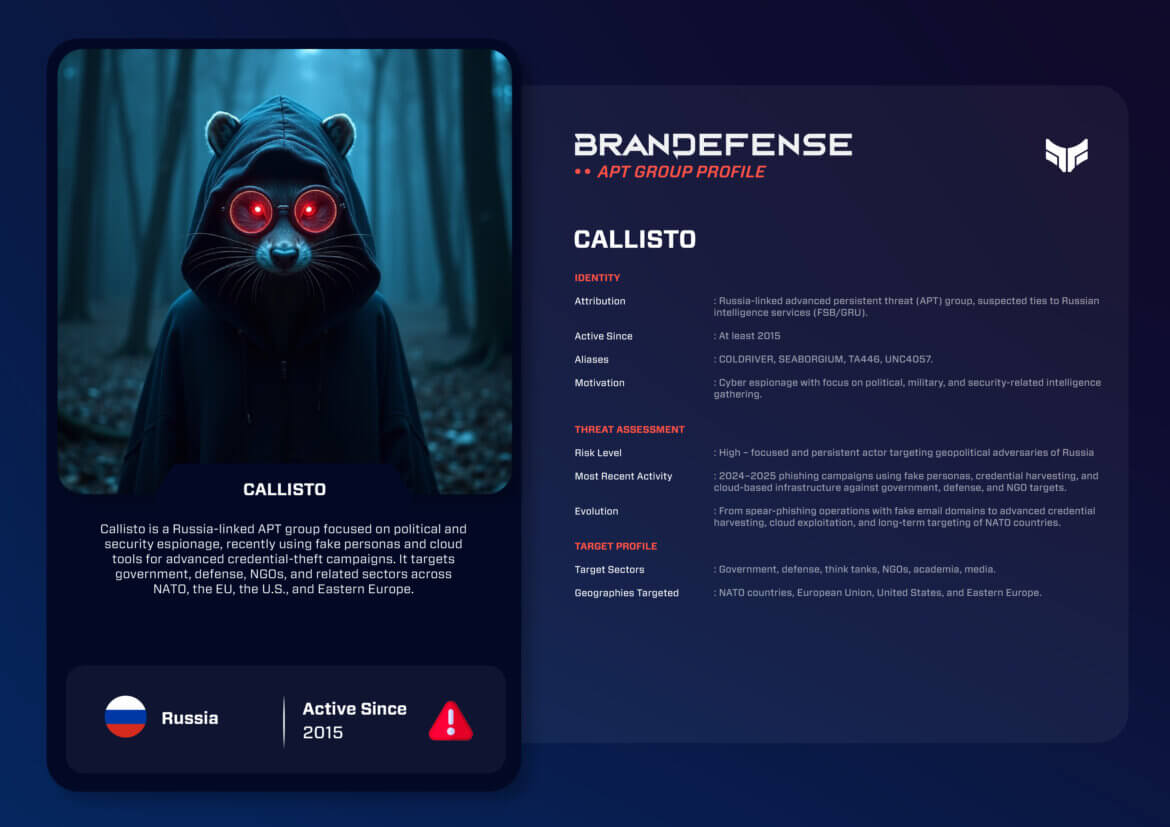
- Attribution: Russia-based, assessed by UK, US and allied agencies to be subordinate to the Russian FSB (Center 18).
- Active Since: at least 2019, according to MITRE ATT&CK.
- Aliases: COLDRIVER, SEABORGIUM, TA446, UNC4057.
- Motivation: Espionage and long-term intelligence collection against political actors that Russia sees as geopolitical adversaries.
Callisto does not work for money. It wants sensitive data, mainly diplomatic messages, military plans, talks about sanctions, and policy discussions. This intelligence can help Russia in negotiations and give it a better view of world affairs.
- Aliases.
- COLDRIVER, SEABORGIUM, Star Blizzard, TA446.
- Attribution.
- Assessed by UK, US and allied agencies to be subordinate to the Russian FSB (Center 18).
- Motivation.
- Espionage and long-term intelligence collection.
- Targets.
- Governments, defense bodies, think tanks, NGOs, academia.
What tactics and tools does Callisto use?
Initial Access
- Spear-phishing: Highly tailored phishing campaigns that appear legitimate. The emails may pose as members of the press, academicians, or political analysts.
- Credential-harvesting sites: Fake log-in portals that steal email and teamwork credentials.
- Watering-hole compromises: Rarely, an independent policy website is hacked to send the target to confirmation malware.
- Tailored spear-phishing emailLure appears legitimate
- Fake log-in portalSteals email and teamwork credentials
- Credential theftAttacker logs in as the victim
- Mailbox accessLong-term collection of email and documents
Persistence
- Web shells on compromised servers for long-term control.
- Service accounts and scheduled tasks for a stealthy presence.
- Abuse of legitimate remote management tools and backup software to blend in with normal operations.
Command & Control (C2)
- Encrypted HTTPS traffic to steal the data.
- Domain fronting and cloud-hosted redirector pages to hide C2 communications.
- Hacked infrastructure used as staging locations.
Malware & Tools
- Light custom backdoors to gain a foothold.
- Credential-harvesting kits used during phishing operations.
- PowerShell loaders and others that abuse Living-off-the-land-binaries (LOLBins).
- Utilities for mailbox exports and targeted data gathering.
Techniques
- Person-based social engineering: Callisto puts large resources into believable personas, which stay active for several years.
- Short-lived infrastructure: Callisto often rotates domains and servers to avoid detection.
- Targeted exfiltration: Callisto does not steal data at random. It focuses on specific high-value datasets.
Who does Callisto target?
- Sectors: Government ministries, foreign affairs departments, defense contractors, diplomatic missions, NGOs in security and sanctions work, think tanks, and academic research institutes.
- Geographies: NATO member states, European Union countries, the United States and Eastern Europe. The Middle East and Central Asia may also be targeted at times, based on geopolitical relevance.
Callisto keeps focusing on NATO and EU institutions. This shows that it follows Russian state interests.

Notable Operations
2015-2017: First credential-harvesting operations against Eastern European diplomats and policy researchers. Built long-term personas to make spear-phishing attacks believable.
2018-2019: Reach grew to NATO-affiliated networks. Web shells were used, and phishing operations changed to break into government portals and email accounts.
2020-2021: COVID-19-themed lures were used to follow talks about health policies and international travel. Targets grew to include NGOs and other policy researchers.
2022-2023: OAuth consent-based phishing gave access to cloud accounts and led to the theft of long-lived tokens. With this access, Callisto could reach hacked mailboxes and teamwork software.
2024-2025: Focus returns to NATO-affiliated firms and diplomats. Infrastructure changes fast and uses cloud-based redirectors, and credential theft continues.
Recent Developments (2024–2025)
Callisto has changed to fit today’s security setting:
- Cloud-Focused Operations: We see more and more reliance on breaking into cloud accounts, especially through phishing for OAuth consent.
2. Infrastructure Rotation: Domains and C2 servers turn over within days. This makes them harder to detect and take down.
3. Frequent Credential Theft: Phishing and fake portals still serve to gain access to credentials. This shows that even the best defended firm can suffer a successful cyber intrusion.
4. Policy-Driven Targeting: Callisto campaigns follow world crises, such as NATO coordination efforts and sanctions regimes.
Strategic Impact
– Geopolitical Intelligence: Callisto gives Russia a view into Western diplomacy, sanctions, and defense policy.
– Influence on Policy: Stolen data can help adversaries act first, hit back, or manipulate.
– Security Risk: A break-in to email and teamwork tools can open the way to disinformation operations and long-term surveillance.
– Operational Persistence: Callisto keeps a long-term view of how its adversaries decide, through hidden persistence.
How can organizations defend against Callisto?
Firms can reduce the threat from Callisto with these steps:
- Use phishing-resistant MFA (e.g., FIDO2 tokens).
- Monitor OAuth grants and permissions on cloud accounts.
- Actively hunt for web shells and anomalous service account behavior.
- Use EDR/XDR to find misuse of LOLbins and PowerShell commands.
- Set up segmentation and least-privilege access controls on email and document stores.
- Share data and intelligence among governments, CERTs, and private firms. This helps stop ongoing campaigns and keep up with changing tactics.
- Use phishing-resistant MFAFor example FIDO2 tokens.
- Monitor cloud OAuth grants and permissions
- Hunt for web shells and odd service account behavior
- Use EDR/XDR to spot misuse of LOLBins and PowerShell
Conclusion
As of 2025, Callisto is still one of the most persistent Russian spy groups. Callisto steals credentials, abuses cloud services, and stays inside NATO-aligned targets for a long time. This will keep it a reputational threat for many firms. It is also an international security threat. Callisto has shown great skill at adapting, and great patience. It has spent years on long-term personas and infrastructure to reach its goals, despite years of exposure.
In 2025, Callisto is a clear example of modern espionage. It is a low-profile, persistent, and focused adversary that works where technology and geopolitics meet. To defend against Callisto, you need the right technical controls and mitigations. You also need to understand its strategic goals and tradecraft, which keep changing.
You can download and review the sheet for all the details!
Want to find and disrupt APT-driven credential theft before it escalates?
👉 Discover how Brandefense delivers actionable threat intelligence across surface, deep, and dark web.