

Gamaredon Group is a Russia-linked espionage actor, also called Shuckworm, Primitive Bear or Aqua Blizzard, active since at least 2013. MITRE describes it as a suspected Russian cyber espionage group that targets military, law enforcement, judiciary and non-profit entities in Ukraine. The post adds that it more and more targets NATO members and their partners. The Brandefense Knowledge Hub also has the Ember Bear threat group profile.
Introduction
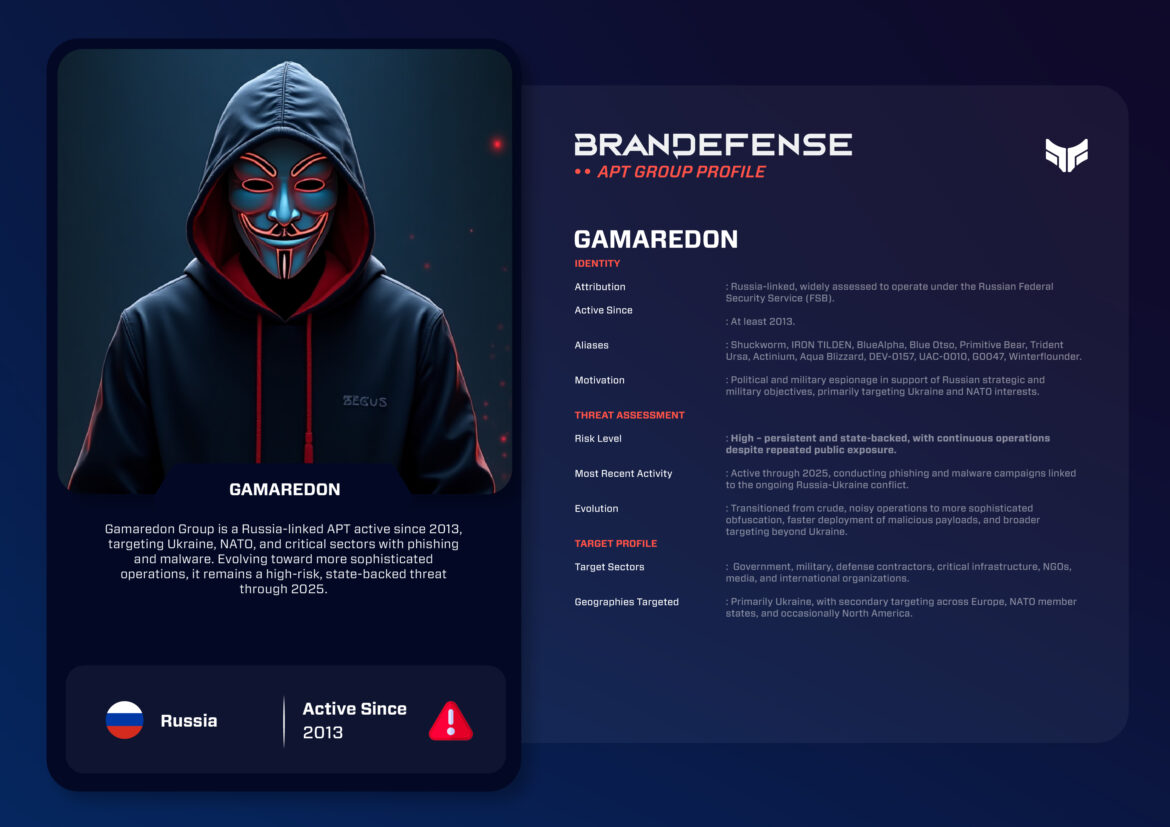
Gamaredon Group, also known as Shuckworm, Primitive Bear, Trident Ursa or Aqua Blizzard, is one of the most active and politically complex Russia-aligned advanced persistent threat (APT) actors. Gamaredon has been active since at least 2013. It is clearly and consistently linked to the Russian Federal Security Service (FSB). Gamaredon has mainly run espionage operations against Ukraine. There is growing evidence that it is also widening its operations against members and partners of NATO. In the Russia-Ukraine conflict, Gamaredon is a high risk threat as we move into 2025. The group’s campaigns keep growing more complex and longer term.
Who is the Gamaredon Group and what does it want?
Gamaredon is a Russia-aligned APT group that runs military and political operations in line with the key goals of Moscow. Its main motive is military and political espionage, mostly tied to the Russia-Ukraine conflict. It has more than one motive. It seeks data about military, government and defense targets. It also seeks data from NATO members and other Western alliances. The persistence of this APT shows that it acts as an intelligence arm that furthers Russia’s geopolitical ambitions.
Aliases include: Shuckworm, IRON TILDEN, BlueAlpha, Blue Otso, Primitive Bear, Trident Ursa, Actinium, Aqua Blizzard, DEV-0157, UAC-0010, G0047, and Winterflounder.
- Active since.
- At least 2013.
- Main target.
- Ukraine, with growing NATO targeting (the post).
- Motivation.
- Military and political espionage.
- Attribution.
- Ukrainian government named FSB Center 18 in November 2021 (MITRE ATT&CK).
- Notable malware.
- Pterodo, PowerPunch.
How does Gamaredon attack?
Gamaredon’s campaigns are often seen as opportunistic, fast, and sometimes noisy. Historically they have not been as advanced and stealthy as other Russian APTs. Over time, though, Gamaredon has improved in speed and obfuscation.
Techniques: Uses PowerShell, fileless methods, fast deployment cycles, and lateral movement through stolen credentials.
Initial Access: Spear-phishing emails with malicious attachments or hyperlinks. The group also occasionally uses unpatched/dated vulnerabilities in public-facing applications.
Persistence: The group sets up persistence through registry entries, scheduled tasks, and custom backdoors.
Command & Control (C2): Uses custom malware families while keeping rotating infrastructure. HTTP-based C2 servers with rotating domains are common.
Malware & Tools: Some notable malware includes Pterodo, PowerPunch, custom downloaders, malicious VBS and BAT scripts, and remote access tools.
- Spear-phishing emailMalicious attachment or linkTechnique T1566 (MITRE ATT&CK, opens in a new tab)
- PowerShell and scriptsFileless methods, VBS and BAT scriptsTechnique T1059 (MITRE ATT&CK, opens in a new tab)
- PersistenceRegistry entries, scheduled tasks, custom backdoors
- C2HTTP servers with rotating domains
- Lateral movementStolen credentials
Notable Operations
- 2013–2018: Gamaredon focused on Ukrainian government institutions and used crude spear-phishing campaigns.
- 2019–2021: Gamaredon moved towards more advanced malware, such as Pterodo. The operation’s focus expanded to include phishing against Ukrainian military and diplomatic networks
- 2022: With Russia’s full-scale invasion of Ukraine, the group escalated their espionage and phishing campaigns to support the invasion
- 2023: The group retained strong interest in Ukraine while opening additional targeting against NATO and European allies.
- 2024–2025: Gamaredon’s work stays firmly aimed at Ukrainian and NATO-related entities. It is also growing more complex and obscure, and its malware toolsets are becoming more varied.
Recent Developments
MITRE ATT&CK describes Gamaredon as a suspected Russian cyber espionage group. It has targeted Ukrainian military, law enforcement, judiciary and non-profit entities since at least 2013. Gamaredon is still not the most advanced of the Russian APT groups. Even so, it should not be underestimated as a new threat actor. It is persistently disruptive, works at a quick tempo, and stays focused on Ukraine.
The group is targeting and moving to attack government and military entities. It is more and more targeting NGOs, media outlets, and critical infrastructure providers, and it has attacked them before. This wider range of targets points to Moscow’s intent to surveil and disrupt networks that support Ukraine and their data ecosystems. These include firms that are not strictly military in nature.
Conclusion
The Gamaredon Group shows the endurance and flexible approach of Russian cyber-espionage. Gamaredon may not be seen as advanced like some of its peers (like Sandworm). Still, its volume, pace of activity, and purpose fit a steady agenda tied to Russian geopolitical goals. For these reasons Gamaredon is a notable adversary. Defenders should watch for Gamaredon’s spear-phishing operations. They should also watch for its ever-growing malware and its spread beyond opportunistic targeting of Ukraine.
Defensive Takeaways
– Improve phishing defenses and staff education
– Watch for PowerShell and unusual scheduled tasks
– Keep up patch management to limit exploitability
– Monitor new rotating domains and possible malware indicators tied to Gamaredon’s campaigns
Tensions are high and the threat landscape keeps shifting. Gamaredon will remain a reliable asset for intelligence operations that serve Russian interests at least to the end of 2025.
You can download and review the sheet for all the details!
