MuddyWater is a cyber espionage group aligned with Iran. MITRE ATT&CK describes it as a subordinate element of Iran’s Ministry of Intelligence and Security (MOIS). A joint US and UK advisory says the same. It targets government and private organizations in telecommunications, defense, energy and other sectors across the Middle East, Europe and North America.
What Is MuddyWater?
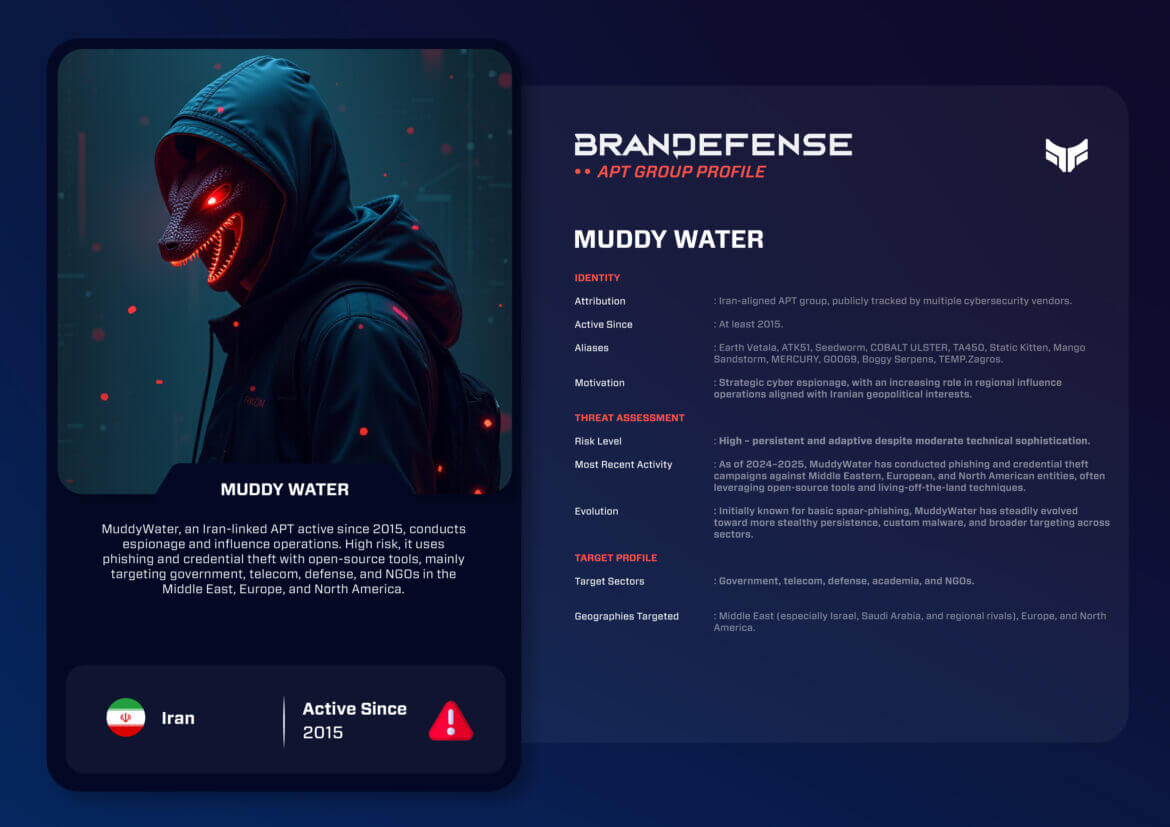
MuddyWater is an advanced persistent threat (APT) group aligned with Iran. According to MITRE ATT&CK, it has been active since at least 2017. It is also known as Earth Vetala, Seedworm, COBALT ULSTER, TA450, Static Kitten, Mango Sandstorm, MERCURY, G0069, Boggy Serpens, ATK51, and TEMP.Zagros. MuddyWater has strong ties to Iran’s Ministry of Intelligence and Security (MOIS). It runs long-term cyberespionage operations against governments, telecom providers, defense contractors and non-governmental organizations in the Middle East, Europe and North America.
MuddyWater plays the long game. It leans on patience and the ability to adapt, more than on technical skill. Its operations and methods keep changing, even beyond formal state service.
Identity and Motivation
Many sources tie MuddyWater to cyber operations that the Iranian state backs. Its main aim is to collect intelligence that helps Tehran reach its goals in world politics. That means watching regional players, spreading influence and building Iran’s cyber skills.
MuddyWater also runs regional influence operations against groups in Israel, Saudi Arabia and Western countries. It often hits them again, or hits their partner companies, to steal sensitive political, defense and energy data or to get access to it.
Aliases: Earth Vetala, ATK51, Seedworm, COBALT ULSTER, TA450, Static Kitten, Mango Sandstorm, MERCURY, G0069, Boggy Serpens, TEMP.Zagros.
What Tactics and Techniques Does MuddyWater Use?
MuddyWater uses methods that last but need little skill. It is known for using legitimate tools, open-source frameworks and custom PowerShell malware. These let it keep access for a long time.
Techniques: Credential theft. Lateral movement with stolen administrator accounts. Use of living-off-the-land binaries (LOLBins). Data theft over encrypted channels.
Initial Access: Phishing and spear-phishing messages with malware-laced documents. Attacks on internet-facing apps that have unpatched vulnerabilities.
Persistence: Changes to the registry, malicious scheduled tasks, real tools used for admin work, and stolen administrator credentials.
Command and Control (C2): Open-source frameworks, custom scripts and publicly available malware. These keep quiet communication channels open to the victim’s systems.
Malware and Tools: POWERSTATS, PowGoop, Small Sieve, MuddyC3, and malicious PowerShell/VBS scripts.
- Phishing or spear-phishingMessages with malware-laced documentsTechnique T1566 (MITRE ATT&CK, opens in a new tab)
- Exploit internet-facing appsUnpatched vulnerabilities give a way inTechnique T1190 (MITRE ATT&CK, opens in a new tab)
- Run scripts and toolsCustom PowerShell malware, open-source frameworks, LOLBins
- PersistRegistry changes, scheduled tasks, compromised admin accounts
- Move and stealStolen administrator accounts, lateral movement, exfiltration over encrypted channels
Notable Operations
2017–2018: Conducted mass phishing campaigns against government and telecommunications organizations in the Middle East.
2019: Extended their reach to Europe, targeting the academic and NGO sectors.
2020: Used open-source frameworks along with custom PowerShell malware in espionage campaigns.
2022: U.S. Cyber Command, with CISA, the FBI and the UK NCSC, issued a joint advisory dated 24 February 2022. It pointed to MuddyWater’s use of open-source tools.
2022: Focus was increased toward the defense and energy sectors of Israel and Saudi Arabia.
2023: Expanded target scope to include North American research institutions and European government agencies.
2024–2025: Phishing and credential theft continued and grew across Europe, North America, and the Middle East. The group used a mix of open-source and custom malware.
- 2017 to 2018Mass phishingGovernment and telecommunications targets in the Middle East.
- 2019Reach extended to EuropeAcademic and NGO sectors.
- 2020Open-source frameworks and custom PowerShell malwareUsed in espionage campaigns.
- 2022More focus on defense and energyIsrael and Saudi Arabia.
- 2023Wider target scopeNorth American research institutions and European government agencies.
- 2024 to 2025Phishing and credential theft continuedEurope, North America and the Middle East.

Is MuddyWater Still Active?
As of 2025, MuddyWater is still an active Iranian cyber espionage threat actor. It has changed its tactics in public view, for example by mixing publicly available tools with its own custom malware. This makes attribution harder and detection more complex.
Its day-to-day tradecraft is generally seen as low-level. Even so, its persistence, its adaptability and its close fit with the goals of the Iranian state keep it relevant on the global threat map. The group is aiming more and more at sectors linked with critical infrastructure and energy security. This also fits Iran’s interest in watching, and in affecting, the energy security and regional policy work of its rivals.
Conclusion
MuddyWater is a high-risk, state-sponsored cyber espionage threat actor. It lacks the technical skill of its peers. Still, it is consistent, it adapts, and it fits the goals of its state sponsor. That makes it a real cyber threat in many countries.
Defensive Takeaways
- Train staff to spot phishing and spear-phishing emails.
- Patch public-facing software apps on time.
- Look for anomalous usage of PowerShell and scheduled tasks.
- Detect anomalous credential usage and lateral movement.
- Use threat intelligence features to detect indicators of compromise linked with MuddyWater campaigns.
Tehran continues to use cyber operations to show power and to handle strategic intelligence. MuddyWater will no doubt be a key part of Iran’s offensive cyber ecosystem through 2025 and beyond.
You can download and review the sheet for all the details!