What Is APT42?
APT42 is a cyber espionage group that MITRE ATT&CK describes as Iranian-sponsored, also tracked as CALANQUE. It uses spear-phishing, credential harvesting and surveillance malware against policymakers, NGOs, academics, journalists and dissidents. MITRE ATT&CK says it has been active since at least 2015. Its goal is intelligence for Iran’s interests, not money. For a sourced summary, see our APT42 threat group profile. It sets out what the UK NCSC, the Israel National Digital Agency, the US Treasury and MITRE ATT&CK say about this group.
APT42, also known as UNC788 and CALANQUE, is one of Iran’s most important cyber espionage groups. Ransomware actors want money. APT42 does not. Its operations have political, military and intelligence goals that fit Iran’s national interests. APT42 steadily targets policymakers, non-governmental organizations (NGOs), academics, journalists, medical organizations and dissidents. This serves the regime’s goals in world politics and security.
APT42 remains an active cyber actor as of 2025. It has upgraded its tools with credential phishing, surveillance malware, mobile exploitation and supply chain compromises. It stays effective because it shifts fast as defenses improve worldwide.
Identity and Motivation
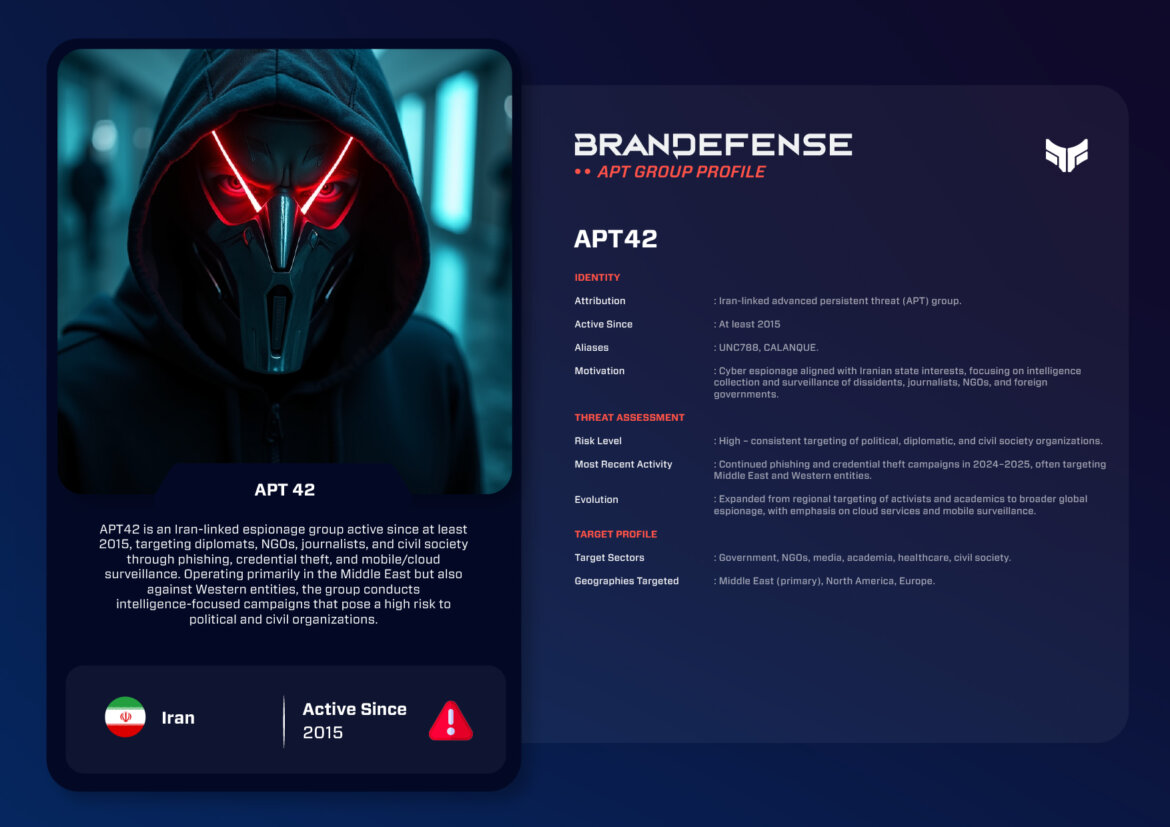
Aliases: APT42, UNC788, CALANQUE
Attribution: Iran-aligned and attributed to state intelligence operations.
Active since: At least 2015 with a clearly visible increase in activity after 2018.
Motivation: Espionage, threat-based surveillance, and suppressing perceived threats to the Iranian regime.
APT42 is not driven by money. Its main mission is to collect intelligence on adversaries, watch targets, and silence dissident voices through fear and surveillance.
- Aliases.
- APT42, CALANQUE.
- Attribution.
- Iranian-sponsored threat group, per MITRE ATT&CK.
- Active since.
- At least 2015, per MITRE ATT&CK.
- Motivation.
- Espionage, surveillance and suppressing perceived threats to the Iranian regime.
How Does APT42 Operate?
Initial Access
APT42 is very good at spear-phishing campaigns. It often poses as trusted groups such as think-tanks, NGOs or news outlets. Its lures are well made, and they play on the social and political worries of the targets.
Credential Harvesting
Hacked email accounts often serve as a stepping stone to reach more of the larger organization. The stolen credentials show internal messages, diplomatic talks and policy planning.
Malware & Tools
- Custom Mobile Malware: Watches mobile devices. It pulls down contacts and messages and tracks GPS location.
- Reverse Tunnels: Seen often in recent campaigns. They keep the attackers inside secured networks.
- Cloud Service Abuse: Heavier use of an organization’s cloud and VPNs has let the actors hide C2 traffic.
Persistence & C2
APT42 often stays in place by using legitimate remote monitoring and management (RMM) tools. These let the attackers watch a network for a long time. They also blend in with normal IT work.
Who Does APT42 Target?
APT42 runs campaigns across many continents, yet its target areas stay the same:
Regional Focus: Middle East, Europe, North America, and occasionally Africa.
Government & Diplomacy: Ministries of foreign affairs, embassies, and intergovernmental organizations.
Healthcare: Especially during COVID-19, targeting pharmaceutical and research organizations for vaccine data.
NGOs & Academia: Groups that shape the global story about Iran.
Media & Journalists: To collect intelligence for tracking reports on Iran and to scare those who disagree.

Notable Operations (2015–2025)
2017–2019: APT42 targeted western think tanks and academics who researched Middle East policy.
2020–2021: APT42 used COVID-19 to target liberal arts institutions, healthcare institutions, and pharmaceutical research.
2022: Harassment campaigns against journalists and dissidents rose. The group made heavy use of Android malware to watch people.
2023: Spear-phishing campaigns against government agencies in both the Middle East and Europe.
2024: Cooperation with MuddyWater and Lyceum, and a joint effort using RMM software against Israeli and Central Asian targets.
2025 (Ongoing): Continuing interest in the transportation and energy sectors. Also targeting networks in cloud environments and inside diplomatic missions.
- 2017 to 2019Western think tanks and academicsResearch on Middle East policy was targeted.
- 2020 to 2021COVID-19 luresLiberal arts, healthcare and pharmaceutical research targeted.
- 2022Harassment and Android malwareJournalists and dissidents were targeted.
- 2023Spear-phishingGovernment agencies in the Middle East and Europe.
- 2025Ongoing activityTransportation, energy, cloud networks and diplomatic missions.
Recent Developments (2024–2025)
APT42 has adapted its activity in four ways:
- Mobile-first surveillance: Android malware use has grown. It is used to watch dissidents and journalists abroad.
- Reverse Tunnels: They get around security and keep the group in the network longer.
- Collaboration with Other Iranian Units: There is evidence it has worked jointly with MuddyWater, as well as sub-groups of OilRig.
- Cloud Exploitation: The unit has been using fully cloud-based services to steal data, and even for command-and-control. This makes detection even harder.
All four points show that APT42 is moving toward hybrid espionage operations. These mix classic phishing and/or malware exploitation against advanced persistence networks or targeted mobile managed devices.
What Is the Strategic Impact of APT42?
APT42 is one of the most strategically disruptive Iranian APTs. It differs from destructive groups like CyberToufan, which put chaos and disruption first. APT42 favors long-term espionage. The intelligence it collects reflects Iran’s plans for diplomatic talks, control at home, and influence operations abroad.
At a minimum, companies should:
– Harden email security and train their staff to spot spear-phishing attempts.
– Monitor for signs that legitimate RMM tools have been abused.
– Detect anomalous traffic over VPNs and clouds.
– Put protections on mobile devices using endpoint detection.
APT42 keeps coming back, and that shows the need for a layered defense, proactive threat hunting and intelligence sharing. This includes sharing within government and between public and private partners.
- Harden email securityTrain staff to spot spear-phishing.
- Watch for RMM tool abuseLook for signs that legitimate tools are misused.
- Detect odd VPN and cloud trafficLook for anomalies.
- Protect mobile devicesUse endpoint detection.
Conclusion
APT42, also called UNC788 and CALANQUE, is a pillar of Iran’s cyber espionage efforts. After nearly a decade of operations, the group has shown patience and the ability to adapt. It has built and used new tools for each new capability. These include phishing, credential harvesting, mobile device surveillance and cloud exploitation.
As of 2025, APT42 will continue to target government bodies, NGOs, journalists, health organizations and academic organizations in line with Iran’s security interests. Its operations show how modern APTs build on long-standing espionage tradecraft in each new cyber intrusion.
For defenders, the message is clear: APT42 will be a long-standing threat. It calls for constant watch, defenses that run on intelligence, and teamwork across countries on countermeasures.
You can download and review the sheet for all the details!