

Scattered Spider is a financially motivated cybercriminal group, also tracked as UNC3944 and Octo Tempest, made up mainly of English-speaking actors. It has been active since at least 2022. The group steals data to extort victims, uses social engineering such as phone calls to IT help desks, and has deployed ransomware, most recently DragonForce. Related reading: the UK retail attacks incident page.
Introduction
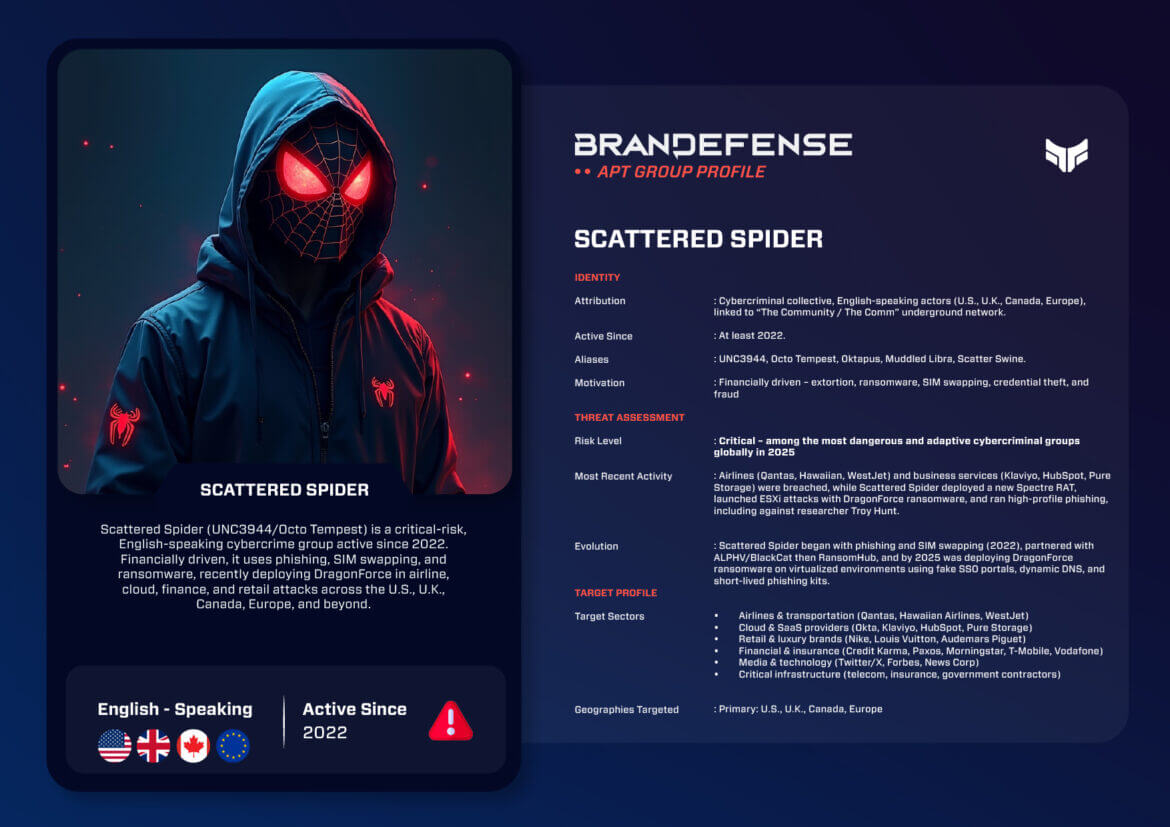
Scattered Spider, aka UNC3944, Octo Tempest, 0ktapus, Muddled Libra, and Scatter Swine, is one of the most dangerous and adaptive financially motivated groups in the cyber threat landscape in 2025.
The group is connected with the underground network often referred to as “The Comm.” It is infamous for combining sophisticated social engineering with ransomware operations. After large-scale arrests in 2024, the collective kept ramping up operations. This shows it was able to bounce back and adapt.
Who Is Scattered Spider and What Motivates It?
• Attribution: Cybercriminal collective primarily comprised of English-speaking actors located in the U.S., U.K., Canada, and Europe.
• Active Since: At least 2022.
• Aliases: UNC3944, Octo Tempest, 0ktapus, Muddled Libra, Scatter Swine.
• Motivation: Financial gain through extortion, ransomware, credential theft, and SIM swapping.
The group is decentralized. This lets it withstand the arrest of its leaders. It can still escalate attacks in a coordinated way across different industries.
- Aliases.
- UNC3944, Octo Tempest, 0ktapus, Muddled Libra, Scatter Swine.
- Active since.
- At least 2022.
- Made up of.
- Mainly English-speaking actors located in the U.S., U.K., Canada, and Europe.
- Motivation.
- Financial gain through extortion, ransomware, credential theft, and SIM swapping.
- Structure.
- Decentralized, so arrests of leaders did not stop the attacks.
TTPs
Scattered Spider uses a combination of living-off-the-land (LotL) techniques, commercially available tools, and their own unique malware. Social engineering at scale is still their hallmark.
• Initial Access: Phishing & smishing campaigns with fake Okta/SSO portals, dynamic DNS domains and MFA fatigue.
• Social Engineering: Voice phishing (vishing) impersonating IT staff to convince help desks to reset credentials.
• Execution: RMM tool abuse (AnyDesk, TeamViewer, ScreenConnect, Tailscale VPN) as well as the deployment of Spectre RAT and off-the-shelf malware (WarZone, Vidar, Raccoon).
• Persistence: Using malicious Identity Providers in cloud comms, privileged accounts and persistence via any VPN/RMM.
• Defense Evasion: Hypervisor-level attacks on VMware ESXi; use of proxies, rotating IPs, blending in with legitimate PowerShell/PsExec activity.
• Exfiltration & Impact: Using cloud storage (MEGA.nz, AWS S3) for exfiltration and DragonForce ransomware for double extortion (encryption + leak).
- Phishing and smishingFake SSO portals, dynamic DNS domains and MFA fatigue
- VishingImpersonating IT staff to convince help desks to reset credentials
- Remote tools and malwareRMM tool abuse and deployment of Spectre RAT
- PersistenceMalicious identity providers, privileged accounts, VPN/RMM
- Exfiltration and impactCloud storage for exfiltration, DragonForce ransomware for double extortion
Notable Operations
• 2025 (Jul): Breach of Qantas Airways revealing 6M customers with Hawaiian Airlines, WestJet affected;
• 2025 (Mar): High-profile phishing attack against security researcher Troy Hunt using mailchimp-sso[.]com;
• 2025 (Feb – Apr): Klaviyo, HubSpot and Pure Storage targeting with an updated Spectre RAT;
• 2025 (Ongoing): ongoing deployment of DragonForce ransomware against VMware ESXi hypervisors;
• 2024: went from ALPHV/BlackCat to RansomHub after law enforcement engagements disrupted activity;
• 2023 (in September) – MGM Resorts and Caesars Entertainment breach $100M+ damage.
• 2022 – Initial SIM swapping and Okta portal phish campaigns.
- 2022SIM swapping and phishingInitial SIM swapping and phishing campaigns against sign-in portals.
- 2023MGM and Caesars breachesMGM Resorts and Caesars Entertainment breach, $100M+ damage.
- 2024Link to RansomHubMoved from ALPHV/BlackCat to RansomHub after law enforcement engagements disrupted activity.
- 2025Hypervisor ransomwareDragonForce ransomware against VMware ESXi hypervisors, with growth in aviation and SaaS.
Timeline of Evolution
– 2022 – SIM swapping shows up and phishing starts.
– 2023 – MGM/Caesars breaches occurred.
– 2024 – Association with RansomHub, indictments and arrests occur but they continue to operate.
– 2025 – Hypervisor ransomware (DragonForce), expand significantly in aviation and SaaS.
Recent Activity
• Newer variants of Spectre RAT with obfuscation and new C2 procedures are available.
• DragonForce ransomware targeting ESXi hypervisors to maximize damage.
• Impermanent phishing infrastructure (5-30 minutes) is difficult to detect.
• Global targeting: airlines, SaaS, retail, finance, telecommunications, and media.
These highlight Scattered Spider’s predilection for scaling social engineering, while also addressing enterprise infrastructure vulnerabilities increasingly.
Takeaway
Scattered Spider is now a dangerous global threat actor with unique advantages. Its members are native English speakers and know Western enterprises well. Its social engineering campaigns can run independently and, in the end, very effectively. Their clear progression to hypervisor-level ransomware, and SaaS valueless credential theft campaigns, is alarming.
How Can Organizations Defend Against Scattered Spider?
• Monitor for outbound short-lived phishing domains and Okta/SSO impersonation domains.
• Strengthen MFA, prefer phishing-resistant solutions, and protect against SIM swapping.
• Restrict and monitor RMM tools (AnyDesk, Tailscale, TeamViewer). If you run Tailscale yourself, see which of its features a researcher reported as exposed in the Tailworm analysis of Tailscale features.
• Determine VMware ESXi security posture against ransomware-type security events, if applicable.
• Anticipate double extortion scenarios, including negotiation playbooks.
You can download and review the sheet for all the details!
