
APT28 is a Russian cyber espionage group. It is also called Fancy Bear, Sofacy and Sednit.
MITRE ATT&CK says it has been active since at least 2004. The US, UK and EU attribute it to the GRU’s 85th Main Special Service Center (military unit 26165). Czechia (May 2024) also links it to the GRU.
| Also known as | Fancy Bear, Forest Blizzard, Sofacy, Sednit, Pawn Storm, STRONTIUM |
| Attributed to | Russia's GRU, 85th Main Special Service Center, military unit 26165 |
| Attributed by | The US, UK and EU; Czechia (May 2024) links it to the GRU |
| Active since | At least 2004 (MITRE ATT&CK) |
| MITRE ATT&CK ID | G0007 |
| Main targets | Government, military, defense, political parties, media, energy and logistics, mostly in Europe, North America and Ukraine |
Full sources, timeline and government actions are in the APT28 threat group profile.
Introduction
APT28 goes by many names. They include Fancy Bear, Sofacy, Sednit and STRONTIUM. It is the best-known and longest-running advanced persistent threat (APT) group still active. It is the tip of the spear of Russia’s state-linked cyber power.
The group can be traced back to 2004. National intelligence agencies assess with high confidence that it is tied to Russian military intelligence (GRU, Unit 26165).
For twenty years, APT28 has played a leading role in three areas:
- Cyber espionage.
- Political interference.
- Hybrid warfare.
It keeps targeting NATO, the European Union, the United States and international bodies that work against Russian interests. Its effects line up with Moscow’s goals on the world stage.
This post looks at who APT28 is and how it works. It covers its tactics, its tools and how it has changed up to 2025. It ends with what this means and the lessons for defenders.
Who Is APT28 and What Motivates It?
APT28 is believed to be part of the Russian General Staff Main Intelligence Directorate (GRU). It sits in Unit 26165. Its long record of operations always lines up with Russian state interests. These include:
- Collecting intelligence.
- Gaining political influence.
- Weakening the institutions of rivals.
What drives APT28
APT28 spies, tries to sway political results and works to unsettle rivals. It uses disinformation and information warfare to do this.
Its known roles in election interference show its value to the Kremlin. It is a spying asset. It is also a tool for Russia’s wider influence goals.
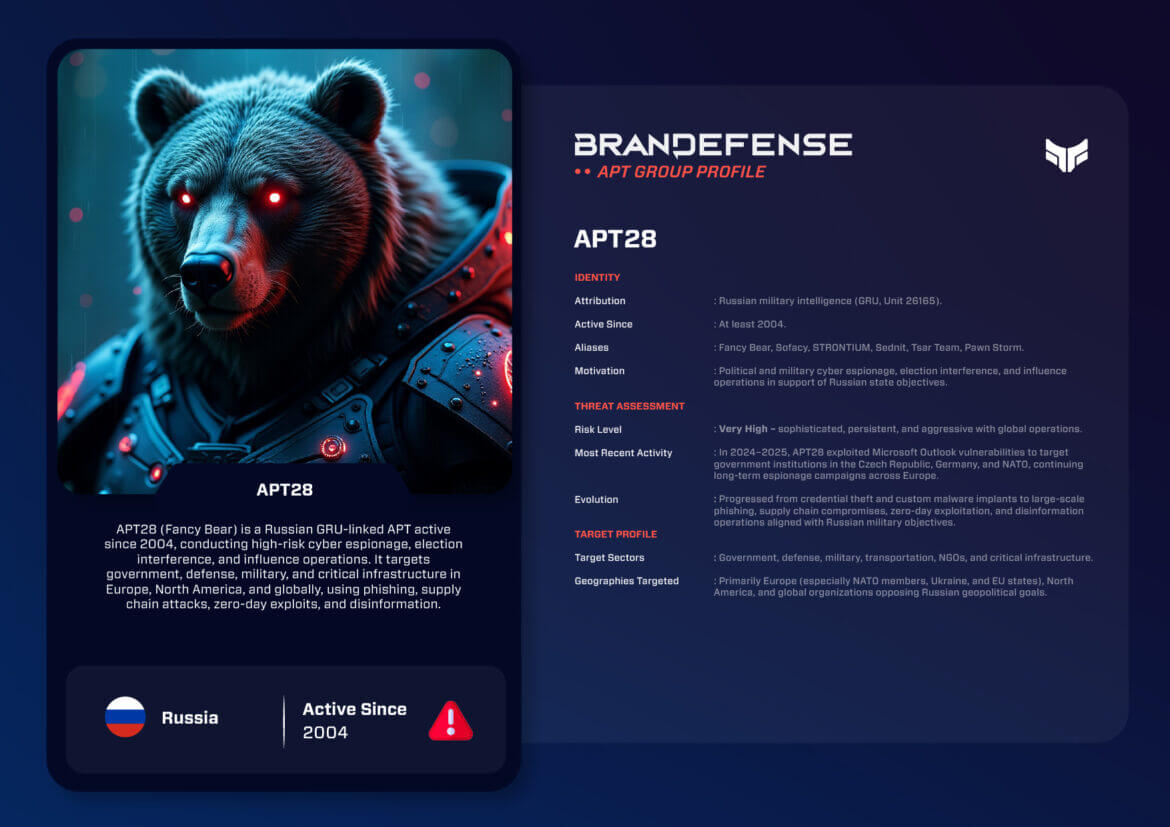
Aliases: Fancy Bear, Sofacy, STRONTIUM, Sednit, Tsar Team, Pawn Storm.
Active Since: At least 2004.
Motivation: Political and military espionage. Election interference and influence operations that directly support Russian state policy.
- Aliases.
- Fancy Bear, Sofacy, STRONTIUM, Sednit, Tsar Team, Pawn Storm.
- Active since.
- At least 2004.
- Attributed to.
- Russian military intelligence (GRU), Unit 26165, assessed with high confidence by national intelligence organizations.
- Motivation.
- Political and military espionage, election interference and influence operations.
- Sectors.
- Government, defense, military, transportation, non-governmental organizations, media, critical infrastructure.
- Geographies.
- Primarily NATO countries, Ukraine, EU members and North America.
TTPs (Tactics, Techniques & Procedures)
APT28 adapts well. It uses advanced zero-day exploits. It also keeps quiet, low-level access for long periods.
Its methods are flexible and can scale. It can turn them on a wide range of targets.
Initial access
- Spear-phishing with attachments or links to harmful content.
- Zero-day flaws in widely used software, such as MS Outlook, MS Office and Windows parts.
- Credential theft and brute-force attacks.
Persistence
- Custom implants such as Sednit and Zebrocy.
- Scheduled tasks and registry changes.
- Stolen credentials that give long-lasting access.
Command and control (C2)
- Custom malware families with encrypted C2 traffic.
- Hacked servers and dynamic DNS infrastructure.
- Hidden channels inside trusted services.
Malware and tools
- X-Agent: a modular implant built for Windows, Linux and iOS.
- The Sednit/Sofacy loader.
- The Zebrocy Trojan, used to steal credentials and scout networks.
- Backdoors such as Chopstick and GameFish.
- Exploit frameworks aimed at Outlook flaws.
Techniques
- Credential harvesting and password spraying.
- Lateral movement across company networks.
- Supply chain attacks to get into trusted systems.
- Data theft at scale.
- Planned disinformation and hack-and-leak operations.
- Initial accessSpear-phishing, zero-day exploits, credential theft and brute force
- PersistenceCustom implants such as Sednit and Zebrocy, scheduled tasks, registry changes
- Command and controlEncrypted C2, compromised servers, dynamic DNS infrastructure
- Lateral movementMovement throughout enterprise networks
- Data exfiltrationData theft at scale
Who Does APT28 Target?
APT28 picks targets that match Russia’s political and military goals.
- Sectors: Government, defense, military, transport, NGOs, media and critical infrastructure.
- Geographies: Mainly NATO countries, Ukraine, EU members and North America. Also any body that works against Russian interests.
This wide range of targets shows that APT28 is a multi-mission intelligence service. It is not a single-purpose spying unit.
Notable Operations
APT28 has been tied to some of the biggest cyber events of the last decade. Each one came at the same time as a key Russian move on the world stage.
- 2016Interference in the U.S. Presidential ElectionInfiltrated political party networks and exfiltrated emails.
- 2017Targeting of European electionsAttempted to penetrate French election campaigns and German political organizations.
- 2018Doping investigation espionageTargeted organizations investigating the Russian state-sponsored doping issue.
- 2020COVID-19 vaccine espionageSpear-phishing and intrusion operations against vaccine research facilities in Europe and North America.
- 2022Ukraine invasion supportTargeted NATO defense ministries, Ukrainian infrastructure and media.
- 2023Email exploit campaignsExploited vulnerabilities in email platforms against European governments.
- 2024 to 2025Outlook exploits against NATO and EUTargeted Czech, German and NATO government institutions.
2016: Interference in the U.S. Presidential Election
APT28 broke into political party networks and stole emails. It then helped release them. The aim was to sway the result of the U.S. presidential election.
2017: Targeting of European elections
APT28 tried to break into French election campaigns and German political groups. The aim was to sway political results. It also aimed to weaken trust in democratic institutions.
2018: Doping investigation espionage
APT28 targeted bodies looking into Russian state-sponsored doping. It stole sensitive data. The goal was to hurt the standing of international watchdogs.
2020: COVID-19 vaccine espionage
APT28 used spear-phishing and break-ins against vaccine research sites in Europe and North America. It wanted to steal their private medical research.
2022: Ukraine invasion support
APT28 stepped up its attacks as Russia invaded Ukraine. It targeted NATO defense ministries, Ukrainian infrastructure and media. These operations mixed spying and disinformation. The aim was to weaken Western support for Kyiv.
2023: Email exploit campaigns
APT28 used flaws in email platforms to spy on European governments. This shows its lasting interest in diplomatic and political intelligence.
2024–2025: Outlook exploits against NATO and EU
Most recently, APT28 has used Microsoft Outlook flaws. It targeted Czech, German and NATO government bodies. It keeps up its long-running spying with updated methods.
More APT28 operations, 2015 to 2021
APT28 did more than election interference. From 2015 to 2021 it ran a long series of phishing and exploit campaigns. Its targets were parliaments, NATO members, defense companies and foreign ministries.
- 2015German BundestagIntrusion into the parliament’s network in April and May 2015; the EU sanctioned Russian military intelligence officers for it in 2020.
- 2015EFF spoof, White House and NATOJava 0-day and a copy of the EFF domain name.
- 2016Pawn Storm adds TurkeyTurkish parliament and Prime Ministry added to its target list.
- Late 2016 to early 2017DealersChoice phishingFlash exploit documents sent to defense and foreign ministries, with lures about NATO and Turkish troops in Mosul.
- 2018Foreign affairs bodies in Europe and North AmericaPhishing email titled “Upcoming Defense events February 2018”.
- 2019Middle East defense companiesTheir compromised email accounts sent credential phishing; Exchange Autodiscover servers probed to brute force logins.
- 2020Zebrocy in a NATO-themed campaignDelphi version with a low detection rate.
- 2021MSHTML exploitationDefense and national security policy officials in Western Asia; OneDrive used for command and control. Attributed to APT28 with moderate confidence by Trellix.
Recent Developments (2024–2025)
APT28 is still very active. It keeps launching campaigns against Western government networks.
- Its use of Microsoft Outlook flaws shows it can still turn software bugs into weapons at scale.
- It mixes zero-days with credential theft and social engineering. This keeps it effective even as defenses get stronger.
- In October 2026, Symantec reported that APT28 used the HOOKEDGE backdoor. The targets were defense firms and a law enforcement agency in two NATO countries.
Our analysis of the 2026 HOOKEDGE campaign covers the attack chain.
Reports also say that disinformation backs up the technical break-ins. It spreads stories that help Moscow. It also splits NATO allies. Running cyber espionage and information warfare together is still a key part of Russian doctrine.
Strategic Impact
APT28 is one of the largest and most constant cyber threats in the world. Its operations have:
- Undermined trust in democratic processes through election interference.
- Helped Russian military operations by hitting NATO and Ukrainian targets.
- Threatened critical infrastructure through spying and groundwork for break-ins.
- Mixed cyber break-ins and disinformation so each makes the other stronger.
Its work shows how the line between spying and influence is fading in modern conflict. Data theft, leaks and propaganda can now work together toward the state’s goals.
How Can Organizations Defend Against APT28?
Defending against APT28 takes resilience and a steady plan:
- Patch critical flaws fast. This matters most for widely used tools such as Outlook and Office.
- Use multi-factor authentication. It makes stolen passwords far less useful.
- Watch for odd logons, privilege escalation and data leaving the network.
- Harden email gateways with advanced filtering and sandboxing.
- Share threat intelligence with partner organizations to spot campaigns early.
- Train staff on spear-phishing and password-stealing tricks.
APT28 is a highly skilled foe. Still, watching it more closely and responding to incidents faster can raise the cost of a break-in.
Conclusion
APT28 is a clear case of state-led cyber power. It pairs high technical skill with clear strategic intent.
For more than two decades, it has shaped how the world sees Russia’s cyber power. It has run distinctive, high-profile operations. It has kept adapting to new defenses. Because it is so persistent, it is very likely to stay a major threat in 2025 and beyond.
For organizations in NATO, the EU and allied nations, staying alert to APT28 is not optional. It is a must.
APT28 is not just a spying actor. It is also a weapon the Russian state uses in its contest with the West. While that contest goes on, APT28 stays a sharp digital spear for Moscow.
You can download and review the sheet for all the details!
Frequently Asked Questions
What is APT28?
APT28 is a threat group also known as Fancy Bear, Sofacy and Sednit. MITRE ATT&CK says it has been active since at least 2004. The post describes it as focused on espionage and political influence.
Who is behind APT28?
MITRE ATT&CK attributes APT28 to Russia's GRU 85th Main Special Service Center, military unit 26165. CISA's 2025 advisory uses the same attribution. The post says national intelligence organizations assessed this with high confidence.
What other names does APT28 go by?
MITRE ATT&CK lists many aliases, including Fancy Bear, Sofacy, Sednit, Pawn Storm, STRONTIUM, Tsar Team, Forest Blizzard and Threat Group-4127.
How does APT28 break into networks?
CISA lists credential guessing and brute force, spearphishing, and exploitation of flaws such as Outlook CVE-2023-23397. The post also names zero-day exploits and credential theft as common entry routes.
How can organizations defend against APT28?
CISA advises strong multi-factor authentication such as passkeys or smartcards, prompt security patches and network segmentation. The post adds monitoring for unusual logons and data exfiltration, and staff training on spear-phishing.
