WageMole is a name for a North Korean state-linked threat group that combines intelligence collection with cryptocurrency theft. The post describes it as active since at least 2018. It targets fintech, cryptocurrency and defense firms through fake recruiters, trojanized test projects and software supply-chain compromises. MITRE ATT&CK tracks the fake recruiter activity separately as Contagious Interview.
Introduction
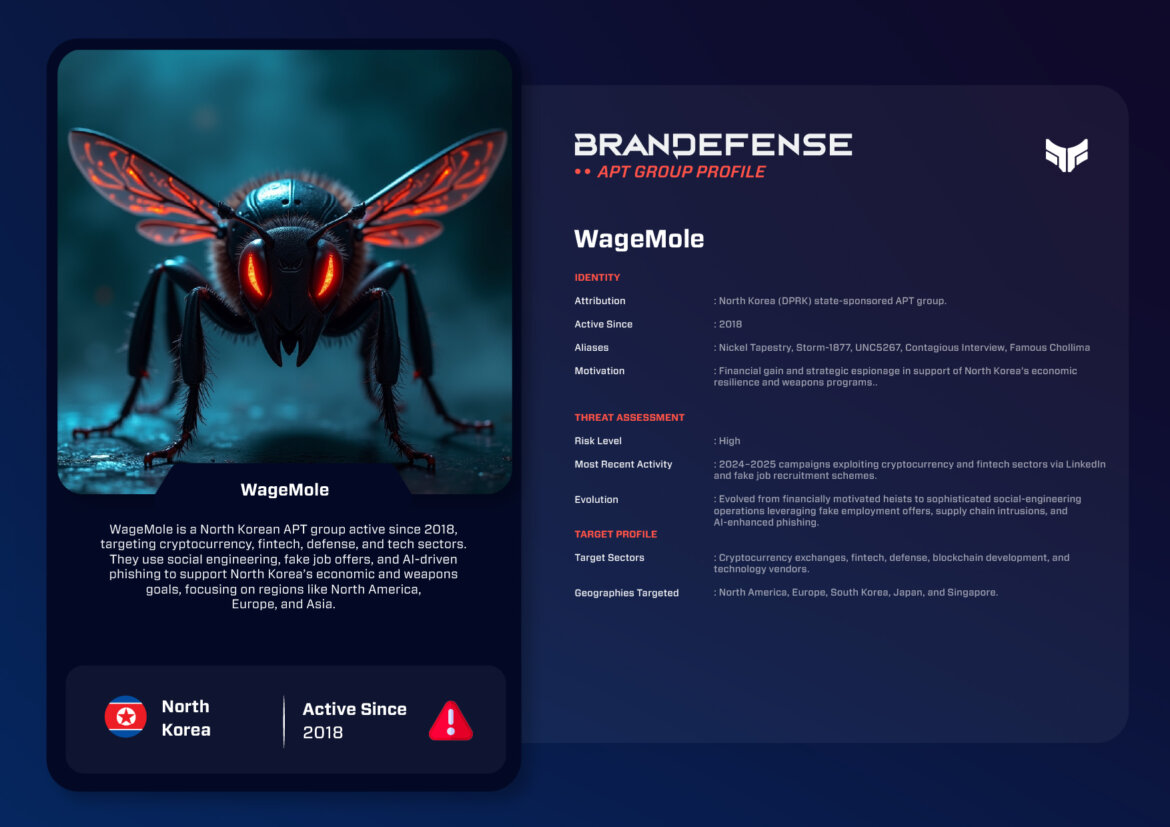
WageMole is a unique hybrid threat actor linked with the Democratic People’s Republic of Korea (DPRK). It is also known by aliases such as Nickel Tapestry, Storm-1877, UNC5267, Contagious Interview, and Famous Chollima. WageMole has been active since at least 2018. This advanced persistent threat (APT) group uses advanced tactics. It combines intelligence collection directed by the state with cybercrime for money, to fund North Korea’s sanctioned economy. In recent years, WageMole has also adapted its social-engineering campaigns, supply-chain attacks and cryptocurrency theft. These operations support both its funding and its strategic goals.
This blog explores WageMole’s origins, development, techniques and major campaigns from 2018 up to 2025. The case studies show how the group sits where espionage meets cybercrime, and how it fits into modern statecraft.
What is WageMole and what does it want?
WageMole’s actions serve the two goals of many DPRK cyber groups. One is to raise revenue for the regime. The other is to gather intelligence on foreign tools. The group mostly targets the financial tech (fintech), cryptocurrency and defense sectors, to extract funds or steal intellectual property. Other North Korean clusters work only to steal funds or only to gather intelligence. WageMole combines the two missions. It may switch between them as global opportunities arise.
The group’s actions fit North Korea’s strategic goal of self-sufficiency under economic sanctions. Its proceeds are understood to go directly to national weapons development programs or state-sponsored projects. The targets, tactics and timing of the group’s activity often overlap with major economic or political events tied to North Korea’s regional rivals.
- Aliases.
- Nickel Tapestry, Storm-1877, UNC5267, Contagious Interview, Famous Chollima.
- Linked to.
- The Democratic People’s Republic of Korea (DPRK).
- Active.
- Since at least 2018, as stated in this post.
- Targets.
- Fintech, cryptocurrency and defense sectors.
- Aims.
- Raising revenue for the regime and gathering intelligence on foreign tools.
Tactics, Techniques, and Procedures
WageMole uses a complex blend of technical skills and psychological manipulation to attack its victims. Its tactics change quickly. It often combines real tools with tailored malware to evade detection.
Initial Access
The group is well known for social engineering on social media sites such as LinkedIn. The hackers pose as recruiters for well-known tech or defense firms. They contact targets in engineering or development jobs. These contacts often lead to a staged interview for a position. There, the victim is asked to review malicious documents or to do a test project that holds trojanized executables.
Besides these social engineering schemes, WageMole has used exploits against vulnerable public-facing apps, remote desktop services and third-party software suppliers. The group’s supply-chain approach is getting more advanced. It compromises software build environments, so that malware goes out and installs with every update.
Execution and Persistence
After initial access, WageMole drops custom loaders and backdoors that allow remote command execution. It often uses PowerShell and Windows Management Instrumentation (WMI) to run its actions without being noticed, and to stay in a system. Scheduled tasks and registry key persistence give it ways to recover, so it keeps access to a compromised account.
WageMole also misuses real remote administration tools such as AnyDesk, Atera, and ConnectWise Control. This dual-use tactic helps it blend in with normal IT work while it keeps strong control channels open.
Command and Control
The group’s command and control (C2) infrastructure is built to blend in with normal enterprise traffic. The group usually communicates over HTTPS or cloud services such as Amazon S3 and Google Cloud Storage. Domain fronting and content delivery networks also help its traffic pass as everyday web activity while the crime goes on.
Data Theft and Monetization
WageMole appears to focus mostly on stealing cryptocurrency wallets, exchange credentials and blockchain API keys. Once stolen, the currency must be turned back into fiat money. To do this, the group launders the currency through mixers, chain-hopping and decentralized exchanges. Where it works through payment APIs, the group disrupts payments and manipulates them to cash out.
Profit is the main motive. But WageMole also takes private software source code, encryption algorithms and sensitive defense data. The reason for this theft is probably to help DPRK tech development, and for intelligence.
- Fake recruiter contactPosing as a well-known tech or defense firm, often on LinkedIn
- Staged interviewVictim asked to review documents or run a test project
- Malware runsTrojanized executables drop custom loaders and backdoors
- PersistencePowerShell, WMI, scheduled tasks and registry keys
- Command and controlHTTPS or cloud services such as Amazon S3 and Google Cloud Storage
- TheftCryptocurrency wallets, exchange credentials and blockchain API keys
Notable Campaigns and Targets
Operation Contagious Interview (since 2023, per MITRE ATT&CK)
This campaign used fake recruiting efforts that targeted developers and security researchers in the cryptocurrency and fintech ecosystem. Victims were sent a job description and a coding test. When they ran it, it delivered customized malware. The campaign showed WageMole’s mastery of social engineering. The group could tailor its operations to the professional context of the people it targeted.
Supply Chain Compromises (2024–2025)
Recent reporting from global cybersecurity firms indicates that WageMole has pivoted to compromising software providers to reach their downstream customers. In some cases, the group took over build environments to insert malware into trusted software updates. This way of working is typical of more advanced APT (Advanced Persistent Threat) activity. It shows growing technical skill in WageMole.
Cryptocurrency Heists (Ongoing)
Throughout 2024 and 2025, WageMole has carried out many heists against cryptocurrency exchanges in North America, Europe and Asia. It used account credentials obtained through spear-phishing and social engineering. The group exfiltrated stolen digital assets worth millions of dollars. These operations remain one of the DPRK’s major sources of foreign currency.

Recent Developments
WageMole’s change reflects the trends seen in North Korean cyber operations more broadly. The group has now added artificial intelligence to make its phishing and other content more real. For example, AI-generated profiles, resumes and interview data make it harder to tell these threats apart from real recruitment attempts.
WageMole is also continuing to develop its infrastructure management. It has begun to use a modular framework that runs across different delivery, command and exfiltration stages. These sit on many independent servers and cloud regions. This also makes attribution and incident response harder.
Strategic Impact
WageMole’s operations expose the blurred line between state-sponsored espionage and cybercrime for money. WageMole is an adaptable tool of North Korean cyber policy. It supports short-term revenue generation, and it also serves longer-term intelligence goals.
The group’s ability to gain access inside recruitment processes and through the development pipeline shows that it understands both human and technical weak spots. It exploits trust within professional work settings. This lets it bypass perimeter defenses and carry out high-value compromises, while using less technical exploits.
WageMole’s global reach also highlights how hard it is to respond to DPRK cyber operations. International sanctions on North Korea are extensive. Even so, the DPRK clearly continues to deploy technically skilled teams. These teams can work across time zones. The DPRK operates in a resilient way. It uses cloud-based infrastructure, anonymization tools and cryptocurrency-based laundering networks. These give it operational resilience and some financial independence.
How can you defend against WageMole?
Defending against WageMole takes a mix of user awareness, technical controls and early threat hunting.
Use Cloud and Network Visibility: Check outbound encrypted traffic for odd destinations and recently registered domains.
Confirm Recruitment Engagements: Companies should train staff on the dangers of unsolicited job offers. Recruiters should always use the company’s verified channels to talk to staff. They should never ask staff to install a package during an interview, or to click links from outside sources.
Isolate Developer Environments: Isolate and monitor ongoing integration and delivery (CI/CD) systems, and use multi-factor authentication (MFA) on them. Code-sign all software releases and check their integrity.
Monitor for Anomalous Remote Tools: Watch for odd AnyDesk, Atera or VPN installs, especially on workstations in finance or development.
Conduct Behavioral Detection: Tools that track lateral movement, PowerShell execution or credential theft can signal the presence of WageMole. This works whether or not signatures exist for the malware.
Increase Supply Chain Monitoring: Audit vendors and open-source dependencies on a regular basis to find any tampering or malicious commits.
Conclusion
WageMole is the next stage of North Korean cyber skill: agile, adaptable and enterprising. It is a state intelligence asset. At the same time, it is a financial engine for a sanctioned regime. It turns professional trust into a weapon and exploits national dependence on digital networks. This shows how complex the modern cyber threat landscape is.
WageMole will keep evolving through 2025 and beyond. Institutions must pay attention to behavioral detection, credential protection and human-based defense. To expect and defend against the threats this actor poses to the global digital economy, we need to learn how it combines social manipulation with technical precision.
You can download and review the sheet for all the details!