
Weekly Security News Archive, Q4 2022.
This page holds the weekly security news issues and newsletters that Brandefense published. It covers the 13 items from October 2022 to December 2022 (2022 Q4). Each entry keeps its first title, publish date and text, newest first. Old addresses of these entries now lead to the matching entry here. The overview page lists all periods.
Other periods: 2023 | 2022 Q4 | 2022 Q3 | 2022 Q2 | 2022 Q1 | Overview
All 13 Entries On This Page
- Security News – Week 52 (28 Dec 2022).
- Security News – Week 51 (21 Dec 2022).
- Security News – Week 50 (16 Dec 2022).
- Security News – Week 49 (7 Dec 2022).
- Security News – Week 48 (30 Nov 2022).
- Security News – Week 47 (23 Nov 2022).
- Security News – Week 46 (16 Nov 2022).
- Security News – Week 45 (9 Nov 2022).
- Security News – Week 44 (2 Nov 2022).
- Security News – Week 43 (26 Oct 2022).
- Security News – Week 42 (19 Oct 2022).
- Security News – Week 41 (13 Oct 2022).
- Security News – Week 40 (7 Oct 2022).
December 2022
Security News – Week 52
Published:
Godfather Trojan Activity Targeting Financial Sector Detected
The Group-IB Threat Intelligence team detected that the Godfather Android banking trojan targeted more than 400 international financial firms between June 2021 and October 2022. Half of the targeted financial firms are banks, and the other half are cryptocurrency wallets and exchanges. The Godfather’s targets include 49 US-based firms, 31 Turkish-based firms, and 30 Spanish-based firms.
Financial service providers in Canada, France, Germany, England, Italy, and Poland are among the hardest-hit firms.
The Godfather trojan was built using the source code of another banking trojan called Anubis. But The Godfather differs from Anubis with its updated features, such as updated command and control (C&C) contact, traffic encryption algorithm, a new module for managing virtual network computing (VNC) connections, and Google Authenticator OTPs.
The Godfather is spread through fake apps hosted on Google Play. Fake pages are placed on Godfather-infected devices. These fake web pages are opened when users click on fake notifications or open real apps targeted by the Godfather. All data entered on these pages (usernames and passwords) is sent to command and control (C&C) servers.
Godfather trojan software can do the following on an infected system.
- Recording the device’s screen.
- Creating VNC connections.
- Capturing keystrokes (keylogging).
- Leaking push notifications and SMS messages (to bypass 2FA).
- Send SMS messages.
- Forward calls.
- Execute USSD requests.
- Start proxy servers.
- Enabling silent mode.
- Establishing WebSocket connections.
A Godfather sample analyzed in September 2022 was observed to mimic Google Protect. When a user launches a harmful application, the application imitates the real Google application. But the Godfather actions are running in the background.
Once the malware is launched, it persists on the infected device, creates a pinned notification, and hides its icon from the list of installed apps. Considering these details, it is advised to consider the following security recommendations to avoid being a victim of targeted attacks that the Godfather malware may carry out.
- Emails, attachments, and links from unknown parties should not be respected.
- Downloaded apps should be downloaded from real application stores, and by checking the evaluations made.
- Full security tools should be used.
Critical RCE Alarm in Linux Kernel
A critical vulnerability has been found in the Linux Kernel that could allow threat actors to disclose private data and run arbitrary code on affected versions.
The vulnerability hitting the SMB2_TREE_DISCONNECT() part in ksmbd is a Use-After-Free error caused by not verifying the object’s existence before operations are performed on the object. Threat actors can exploit this vulnerability to run code in kernel context. Exploiting this vulnerability does not require authentication. Also, only systems with ksmbd enabled are affected by the vulnerability.
The purpose of the ksmbd program, which was integrated into the Kernel in 2021, is to provide fast SMB3 file serving performance. SMB is the main file server protocol in Windows on Linux over Samba. Ksmbd was designed to complement Samba, not replace it. Samba and ksmbd developers are working to make the programs work together.
Agenda Ransomware’s New Rust Variant Targets Critical Sectors
A new variant of Agenda Ransomware, built with the Rust programming language, has been detected to be used in campaigns targeting critical sectors. Agenda has become one of the ransomware that adopts the cross-platform programming language. This makes it easy to adapt to different systems such as Windows and Linux with the new variant.
Agenda, attributed to an operator named Qilin, is linked to a series of attacks targeting manufacturing and IT sectors in different countries. The Agenda Ransomware family, which is still under development, has recently been observed to target critical sectors such as the healthcare and education sectors.
Agenda’s new Rust variant, like the Royal ransomware, uses a partial encryption (also known as intermittent encryption) technique. It configures the parameters used to determine the percentage of file content to be encrypted. This method allows faster encryption and avoids detections based on malware read/write file operations.
Also, unlike older Agenda versions, the new variant can terminate the Windows AppInfo process and disable the User Account Control (UAC) feature. This feature helps prevent the execution of the malware with administrative rights.
Recently, it has been observed that the threat actors behind Ransomware software have started to migrate the ransomware codes to the Rust language. The Rust language is becoming more common among threat actors as it is harder to study and has a lower detection rate by antivirus engines.
It is advised to consider the following security practices to avoid being exposed to targeted attacks that can be carried out using advanced malware.
- E-mails, attachments, and links from unknown parties should not be respected.
- Do not download files, programs, or apps from illegal and suspicious-looking sources.
- Institution/firm staff should be made aware of target-oriented social engineering/phishing attacks.
- Network traffic should be always monitored for the possibility of harmful attempts and abnormal network behavior.
- Full security tools should be used.
- Critical files/systems should be backed up often.
IoC findings related to the campaign should be blocked from the security tools in use.
Security News – Week 51
Published:
Agenda Ransomware’s New Rust Variant Targets Critical Sectors
A new variant of Agenda Ransomware, built with the Rust programming language, has been detected to be used in campaigns targeting critical sectors. Agenda has become one of the ransomware that adopts the cross-platform programming language. This makes it easy to adapt to different systems such as Windows and Linux with the new variant.
Agenda, attributed to an operator named Qilin, is linked to a series of attacks targeting manufacturing and IT sectors in different countries. The Agenda Ransomware family, which is still under development, has recently been observed to target critical sectors such as the healthcare and education sectors.
Agenda’s new Rust variant, like the Royal ransomware, uses a partial encryption (also known as intermittent encryption) technique. It configures the parameters used to determine the percentage of file content to be encrypted. This method allows faster encryption and avoids detections based on malware read/write file operations.
Also, unlike older Agenda versions, the new variant can terminate the Windows AppInfo process and disable the User Account Control (UAC) feature. This feature helps prevent the execution of the malware with administrative rights.
Recently, it has been observed that the threat actors behind Ransomware software have started to migrate the ransomware codes to the Rust language. The Rust language is becoming more common among threat actors as it is harder to study and has a lower detection rate by antivirus engines.
It is advised to consider the following security practices to avoid being exposed to targeted attacks that can be carried out using advanced malware.
- E-mails, attachments, and links from unknown parties should not be respected.
- Do not download files, programs, or apps from illegal and suspicious-looking sources.
- Institution/firm staff should be made aware of target-oriented social engineering/phishing attacks.
- Network traffic should be always monitored for the possibility of harmful attempts and abnormal network behavior.
- Full security tools should be used.
- Critical files/systems should be backed up often.
IoC findings related to the campaign should be blocked from the security tools in use.
Critical RCE Alert in Foxit PDF Reader and PDF Editor
Foxit has released updates that fix a remote code execution (RCE) vulnerability hitting the PDF Reader and PDF Editor products. The vulnerability affects the Windows operating system and is found in Foxit PDF Reader 12.0.2.12465 and earlier and Foxit PhantomPDF-10.1.7.37777 and earlier.
The details of the detected security vulnerability are as follows.
The vulnerability, tracked as CVE-2022-28672, allows remote threat actors to run arbitrary code on affected installations of Foxit PDF Reader. Exploiting this vulnerability requires user interaction.
The related vulnerability has been fixed in Foxit PDF Reader 12.1 and Foxit PDF Editor 12.1. In order not to be the target of attacks that can be carried out using the said vulnerability, PDF Reader users are advised to apply the updates that fix the vulnerability at once.
Multiple Vulnerabilities Detected in Nessus Network Monitor
Many security vulnerabilities have been found in Nessus Network Monitor due to third-party parts. They could allow threat actors to carry out remote code execution (RCE) and Denial of Service attacks on affected installations.
The details of the critical vulnerabilities found are as follows.
- The security vulnerability, tracked as CVE-2022-24785, is due to an input validation error in the npm version of Moment.js. A remote threat actor can access files on the system by sending a crafted HTTP request. (Moment.js is a JavaScript date library for parsing, validating, manipulating, and formatting dates.).
- The security vulnerability, tracked as CVE-2021-23369, is due to incorrect login validation. A remote threat actor can run arbitrary code on the target system through a crafted request.
Tenable has released Nessus Network Monitor version 6.2.0, which fixes the vulnerabilities. Nessus Network Monitor 6.2.0 updates moment.js to version 2.29.4 and Handlebars to version 4.7.7 to fix found security vulnerabilities. It is advised to at once upgrade to the current version published in order not to be the target of attacks that can be carried out using vulnerabilities.
Security News – Week 50
Published:
Critical RCE Alarm on Citrix ADC and Citrix Gateway
The security vulnerability tracked as CVE-2022-27518 is caused by incorrect access restrictions on systems configured as SAML SP or SAML IdP. An unauthenticated, remote threat actor can gain access without permission to the system and run arbitrary code.
The following supported versions of Citrix ADC and Citrix Gateway are affected by this vulnerability.
- Citrix ADC And Citrix Gateway 13.0, Before 13.0-58.32.
- Citrix ADC And Citrix Gateway 12.1, Before 12.1-65.25.
- Pre 12.1-55.291 Citrix ADC 12.1-FIPS.
- 1-55.291 Pre-Citrix ADC 12.1-NDcPP.
Citrix ADC and Citrix Gateway version 13.1 are not affected by the vulnerability. Also, the vulnerability is actively exploited by threat actors. The following scripts specify whether the Citrix ADC or Citrix Gateway is configured as SAML SP or SAML IdP. If any of these scripts are present in the ns.conf file and the version is affected, the application needs to be updated.
- Add Authentication SamlIdPProfile.
- Add Authentication SamlAction.
It is advised that users using vulnerable versions and configurations at once apply the published updates in order not to be the target of attacks that can be carried out using the vulnerability. Customers using Citrix-managed cloud services or Citrix-managed Adaptive Authentication do not need to take any action about the vulnerability.
ZeroBot: New Botnet Malware Using IoT Security Vulnerabilities
A new botnet malware named ZeroBot has been detected that spreads through IoT security vulnerabilities. Developed with Golang, Zerobot exploits many vulnerabilities detected in IoT devices to gain access to targeted systems and spread further.
Vulnerabilities exploited in the deployment process of Zerobot malware include bugs in Zyxel firewalls, TOTOLINK routers, F5 BIG-IP, Spring Framework, D-Link DNS-320 NAS, Hikvision cameras, and FLIR AX8 thermal imaging cameras. It has also been observed that the botnet targets i386, amd64, arm, mips64le, mipsle, arm64, mips, mips64, ppc64, ppc64le, riscv64 and s390x CPU architectures.
After communicating with the command and control (C2) server via the WebSocket Protocol, extra instructions allow Zerobot to run arbitrary commands and launch attacks over some network protocols, including TCP, TLS, UDP, ICMP, and HTTP.
Zerobot is built with a propagation exploit module that makes it harder to detect as it infects more IoT devices. Zerobot has been found as a critical threat as it can gain access without permission to vulnerable systems and prevent targets from stopping the Zerobot program through its AntiKill module.
To avoid attacks that can be carried out using Zerobot, it is advised to use the most up-to-date versions of the systems and programs used and to prevent the shared IoC findings related to the botnet from the security tools in use.
Critical RCE Alarm in FortiOS sslvpnd
A critical security vulnerability has been detected in FortiOS’s SSL-VPN (sslvpnd) that could allow threat actors to remote code execution (RCE) on affected installations.
The security vulnerability tracked as CVE-2022-42475 is caused by a Heap-based Buffer Overflow hitting the sslvpnd daemon part. An unauthenticated, remote threat actor can manipulate the SSL-VPN part through crafted data, triggering a stack-based buffer overflow and executing arbitrary code on the targeted system. Fortinet states that this vulnerability is actively exploited and recommends that users check their systems for the following indicators of compromise.
If the following log string is observed more than once in user systems, check the items below.
- Logdesc=”Application Crashed” And Msg=”[…] Application:sslvpnd,[…], Signal 11 Received, Backtrace: […].
If the existence of the following structures is detected in the file system, check the items below.
- /Data/Lib/Libips.Bak.
- /Data/Lib/Libgif.So.
- /Data/Lib/Libiptcp.So.
- /Data/Lib/Libipudp.So.
- /Data/Lib/Libjepg.So.
- /Var/.Sslvpnconfigbk.
- /Data/Etc/Wxd.Conf.
- /Flash.
If connections are made from FortiGate to the following suspicious IP addresses:
- 34.130.40:444.
- 131.189.143:30080,30081,30443,20443.
- 36.119.61:8443,444.
- 247.168.153:8033.
Threat actors actively exploit the vulnerability. To avoid attacks that can be carried out using vulnerabilities, it is advised to at once set up the published updates and prevent the specified consensus indicators (IoC) from the security tools in use.
Security News – Week 49
Published:
Critical XSS Alert Affecting Zyxel’s Specific Firewall Models
Zyxel has released updates for a critical XSS (Cross Site Scripting) vulnerability that affects specific models of firewalls.
The vulnerability, tracked as CVE-2022-40603, affects the CGI program of firewall versions and is caused by insufficient sanitization of user-supplied data. A remote threat actor can direct targeted users to visit an XSS-loaded URL and run a harmful script in the user’s browser. A threat actor who exploited the vulnerability could access private browser-based data.
The firewall models and versions affected by the security vulnerability are as follows.
Zyxel has fixed the said vulnerability with the current versions mentioned above. It is advised to set up the published updates at once in order not to be the target of targeted attacks that can be carried out using the vulnerability.
Critical RCE Alarm in FreeBSD Ping
A critical security vulnerability has been found in the ping module of the open-source FreeBSD operating system that threat actors could possibly exploit to gain remote code execution.
The Stack Buffer Overflow vulnerability, tracked as CVE-2022-23093, is caused by a boundary error in the ping module’s pr_pack() function and affects all supported versions of FreeBSD. The ping module allows testing the accessibility of a remote host using ICMP messages and reads raw IP packets to process responses in the pr_pack() function.
The pr_pack() function copies the received IP and ICMP headers to the stack buffers for further processing. A remote threat actor could exploit this vulnerability to trigger a boundary fault, crash the ping program, and run code remotely on the affected system.
There has yet to be an update that fixes the vulnerability. To avoid attacks that can be carried out using the vulnerability, it is advised that the updates to be published should be put in place at once if they are followed and published.
LastPass Suffers A Data Breach
LastPass, a popular password management service, suffered a data breach that resulted in threat actors gaining access without permission to a certain number of customer data.
The data breach targeting LastPass and its subsidiary, GoTo, is known to have been carried out using data gained in the August 2022 security breach. There are no details about the breach. But the statement made by LastPass officials stated that the unauthorized parties only gained access to some aspects of the customers with the said data breach attempt.
LastPass has launched a full investigation into the breach through the well-known security firm Mandiant and law enforcement. LastPass reported that its Zero-Knowledge architecture securely encrypts and stores customers’ passwords and that LastPass products and services continue to be available. So, there is no action for customers to take.
November 2022
Security News – Week 48
Published:
WhatsApp Suffered from a Data Breach – 487 Million Users’ Data in Danger
In a well-known hacking forum, it was detected that on November 16, 2022, a threat actor claimed that a database of 487 million WhatsApp users’ mobile phone numbers was hacked.
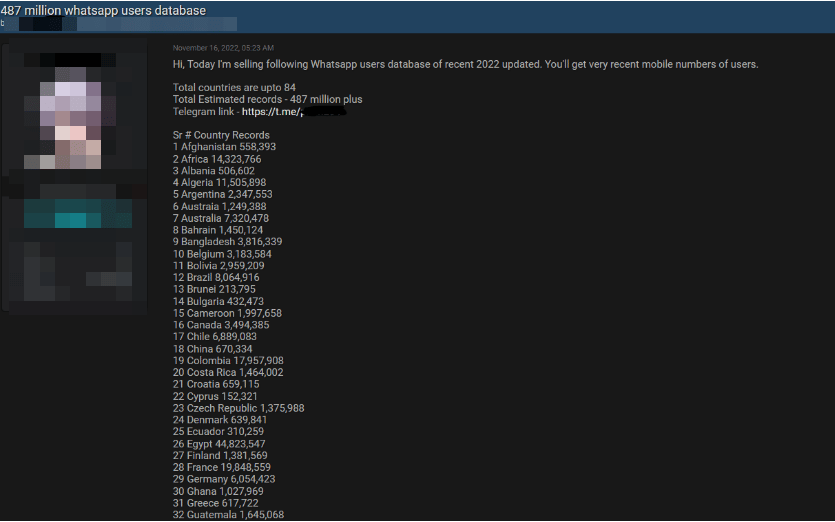
It is claimed that the database seized in the post contains the personal data of WhatsApp users from 84 countries. The distribution of the hacked data by country is given below.
- 45 Million User Data of Egyptian Citizens.
- 32 Million User Data of US citizens.
- 35 Million User Data of Italian citizens.
- 29 Million User Data of Saudi Arabian Citizens.
- 20 Million User Data of French Citizens.
- 20 Million User Data of Turkish Citizens.
- 10 Million User Data of Russian Citizens.
- Over 11 Million User Data of UK Citizens.
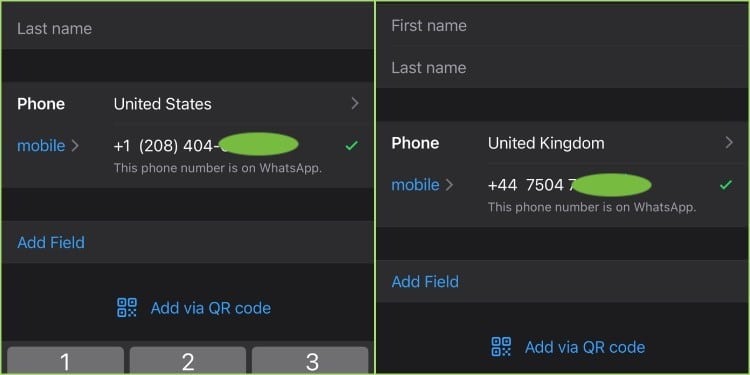
Cybernews experts contacted the threat actor who shared the post and requested a data set sample as evidence to confirm the relevant leak. In the shared example, there are phone numbers of 1097 UK and 817 US users.
But the threat actor did not provide details on how the database was gained, suggesting that they used their plans to collect the data. Upon this, the analysis of the sample data set by Cybernews experts confirmed that all numbers belong to active WhatsApp users.
The intercepted data is mostly used in phishing, smashing, and vishing attacks by threat actors. So, WhatsApp users are advised to be wary of incoming calls and message contents from unknown numbers. Meta, the parent company of WhatsApp, was contacted about the related data leak, but a response has yet to be received. WhatsApp users and parties will be informed of developments on the subject.
Amazon Fixes a Security Vulnerability Affecting AWS AppSync
A security vulnerability called “cross-tenant” has been detected by Datadog experts in AppSync, a popular Amazon Web Services (AWS) tool. AppSync is a popular AWS service that allows developers to quickly create GraphQL and Pub/Sub APIs.
The vulnerability is due to a case-sensitivity parsing issue of the AppSync service. It could possibly be used to bypass cross-account role usage validations and act as a service on customer accounts. Successful vulnerability exploitation allows threat actors to assume Identity and Access Management (IAM) roles in other AWS accounts.
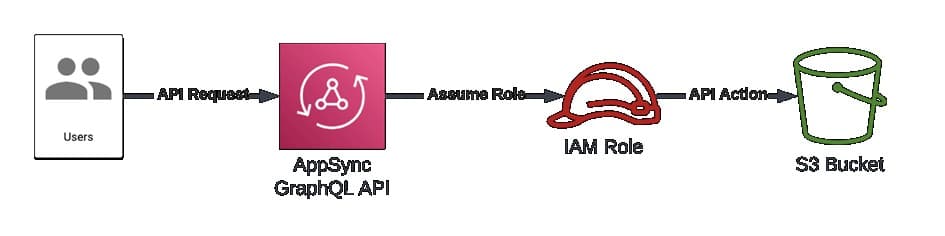
The vulnerability detected on September 1, 2022, was at once reported to AWS. AWS, which rescheduled the attack, verified the impact of the vulnerability and released a fix that fixed it. Also, Amazon released a statement on Monday, November 21, confirming the details of the vulnerability and stating that no customers were affected by it. There is no action for Amazon customers to take due to the vulnerability.
Multiple Vulnerabilities Detected in IT Management Solution GLPI
Many security vulnerabilities have been found in GLPI, an open-source web application that helps institutions/firms and firms manage their IT infrastructure and inventories. These vulnerabilities allow threat actors to run SQL queries against the application database and to carry out Cross-Site Scripting (XSS) and Server-Side Request Forgery (SSRF) attacks.
The details of the detected security vulnerabilities are as follows.
- The security vulnerability tracked as CVE-2022-39375 is due to insufficient cleaning of user-supplied entries in the RSS Feed function. A remote threat actor can run arbitrary HTML code and script in the user’s browser in the context of the vulnerable website via a harmful link. Successful exploitation of this vulnerability allows remote threat actors to get private data, alter the web page’s appearance, and carry out phishing attacks.
- The security vulnerability tracked as CVE-2022-39234 is due to an insufficient session expiration time. This vulnerability allows threat actors to access users’ accounts by reusing users’ old session credentials (Cookies) and thus may lead to the capture of users’ private data.
- The security vulnerability tracked as CVE-2022-39323 is due to insufficient sanitization of user-supplied data in the API REST user_token part. A remote threat actor can run arbitrary SQL commands in the application database by sending a crafted request to the affected application.
- The security vulnerability, tracked as CVE-2022-39276, is due to insufficient validation of user-supplied inputs in RSS feeds. A remote threat actor can direct the application to initiate requests to arbitrary systems (SSRF) via a crafted HTTP request.
- The vulnerability security tracked as CVE-2022-39277, is due to insufficient sanitization of user-supplied data on outside connections. A remote threat actor can run arbitrary HTML code and script in the user’s browser in the context of the vulnerable website via a crafted link.
These vulnerabilities affect specific versions of GLPI. Security updates have been released that fix the vulnerabilities. It is advised to at once upgrade vulnerable installations to the current versions published in order not to be the target of attacks that can be carried out using vulnerabilities.
Security News – Week 47
Published:
Critical RCE Vulnerabilities Affecting F5 Products Detected
Application service provider F5 has issued a security notice for two critical security vulnerabilities that allow an unauthenticated threat actor with network access to remote code execution in BIG-IP systems, a combination of software and hardware. It is designed around access control, application availability, and security tools.
In the statement made by F5, it was stated that the security vulnerabilities detected were found in the representative state transfer (REST) interface for the iControl framework used to communicate between F5 devices and users.
The found security vulnerabilities are:
The vulnerability, code CVE-2022-41622, is caused by cross-site request forgery (CSRF) that affects BIG-IP and BIG-IQ products. This allows threat actors to gain root access to a device’s management interface.
The vulnerability code CVE-2022-41800 allows a threat actor with administrative privileges to run code remotely on vulnerable systems via an RPM file.
BIG-IP product versions affected by these security vulnerabilities are as follows.
- 1.0 – 16.1.2.
- 1.0 – 15.1.5.
- 1.0 – 14.1.4.
- 1.0 – 13.1.4.
- 1.0 – 12.1.6.
- 6.1 – 11.6.5.
Stating that they will not release updates for 11. x (11.6.1 – 11.6.5) and 12. x (12.1.0 – 12.1.6) versions, F5 said that there is no data that security vulnerabilities have been exploited yet and that existing updates will be included in future versions as soon as possible and announced that it will.
To avoid target-oriented attacks that can be carried out by using the vulnerability of the users, it is advised that the published updates be put in place at once.
Reflected XSS Alarm in ProfileGrid WordPress Plugin
A security vulnerability has been detected. This allows threat actors to carry out Reflected XSS attacks in the ProfileGrid WordPress plugin, which offers features such as creating and managing user groups on WordPress websites. A Reflected XSS attack is carried out by injecting harmful scripts directly into an HTTP request by threat actors and executing them in the target user’s browser.
The vulnerability, tracked as CVE-2022-3578, is caused by the ProfileGrid WordPress plugin insufficiently clearing parameters sent to the page in versions before 5.1.1. As a result, a remote threat actor can direct users to open a harmful link. They can run arbitrary HTML code and script in the user’s browser in the context of the vulnerable website.
To avoid attacks that can be carried out using the security vulnerability in question, it is advised to at once upgrade the vulnerable ProfileGrid versions to the current versions (5.1.1) that fix the vulnerability.
Multiple Vulnerabilities Detected in IT Management Solution GLPI
Many security vulnerabilities have been found in GLPI, an open-source web application that helps institutions/firms and firms manage their IT infrastructure and inventories. These vulnerabilities allow threat actors to run SQL queries against the application database and to carry out Cross-Site Scripting (XSS) and Server-Side Request Forgery (SSRF) attacks.
The details of the detected security vulnerabilities are as follows.
- The security vulnerability tracked as CVE-2022-39375 is due to insufficient cleaning of user-supplied entries in the RSS Feed function. A remote threat actor can run arbitrary HTML code and script in the user’s browser in the context of the vulnerable website via a harmful link. Successful exploitation of this vulnerability allows remote threat actors to get private data, alter the web page’s appearance, and carry out phishing attacks.
- The security vulnerability tracked as CVE-2022-39234 is due to insufficient session expiry time. This vulnerability allows threat actors to access users’ accounts by reusing users’ old session credentials (Cookies) and thus may lead to the capture of users’ private data.
- The security vulnerability tracked as CVE-2022-39323 is due to insufficient sanitization of user-supplied data in the API REST user_token part. A remote threat actor can run arbitrary SQL commands in the application database by sending a crafted request to the affected application.
- The security vulnerability, tracked as CVE-2022-39276, is due to insufficient validation of user-supplied inputs in RSS feeds. A remote threat actor can direct the application to initiate requests to arbitrary systems (SSRF) via a crafted HTTP request.
- The vulnerability security, tracked as CVE-2022-39277, is due to insufficient sanitization of user-supplied data on outside connections. A remote threat actor can run arbitrary HTML code and script in the user’s browser in the context of the vulnerable website via a crafted link.
These vulnerabilities affect specific versions of GLPI. Security updates have been released that fix the vulnerabilities. It is advised to at once upgrade vulnerable installations to the current versions published in order not to be the target of attacks that can be carried out using vulnerabilities.
Security News – Week 46
Published:
Critical UEFI Firmware Vulnerabilities Detected in Specific Lenovo Notebook Models
Lenovo has released updates about vulnerabilities detected in the UEFI Firmware component hitting Yoga, IdeaPad, and ThinkBook devices. UEFI refers to software that acts as an interface between the operating system and the firmware embedded in the device’s hardware. It is responsible for starting the operating system when a device is powered on.
So, UEFI offers a highly attractive attack surface for threat actors who want to release hard-to-detect and remove malware.
Here are the details of the vulnerabilities that could be used by threat actors to disable Secure Boot, a security method designed to prevent harmful programs from loading during the boot process.
- The vulnerability, tracked as CVE-2022-3430, affects the WMI Setup driver on certain Lenovo Notebook PC devices and allows a threat actor with elevated privileges to modify Secure Boot settings by modifying an NVRAM variable.
- The vulnerability, tracked as CVE-2022-3431, affects a driver used in certain Lenovo Notebook PC devices that is not accidentally disabled during the manufacturing process. It could allow a threat actor with elevated privileges to change the Secure Boot setting by changing an NVRAM variable.
- The vulnerability, tracked as CVE-2022-3432, affects a driver used during the manufacturing process on the IdeaPad Y700-14ISK that was not accidentally disabled. It could allow a threat actor with elevated privileges to alter the Secure Boot setting by changing an NVRAM variable.
After the vulnerabilities were detected by the Eset security researcher, Lenovo announced that they took action to fix the vulnerabilities. But Lenovo has stated that they do not plan to release fixes for CVE-2022-3432 as the affected model has reached the end of life (EoL).
It is advised that users of other affected devices update their firmware to the latest version in order not to be the target of attacks that can be carried out using vulnerabilities.
Threat Group Named Worok Performs Espionage Activities With Backdoors Hidden Inside Image Files
A recently discovered cyber spy group called Worok has been found to hide malware in image files. PNG files’ purpose is to hide a harmful payload used to help data theft.
Avast discovered that Worok used a C++-based Payload called CLRLoad to pave the way for a PowerShell script embedded in PNG images, using a cloaking technique known as steganography. The findings show that the threat actor applied DLL Injection after gaining first access to run the CLRLoad malware.
Used in the attack chain, Malware called DropboxControl uses a Dropbox account for command and control (C&C) and captures data by allowing the threat actor to download/upload/run files to specific folders. Private firms and government agencies operating in locations such as Cambodia, Vietnam, and Mexico are among the countries affected by DropboxControl.
Avast confirmed the Worok findings of ESET experts and contributed to the expansion of the attack chain.
The tools used by Worok, which capture data through Dropbox accounts registered in active Google e-mails, are not very common. It is considered to be an APT project focused on high-profile firms in the private and public sectors in Asia, Africa and North America.
As a precaution against targeted cyber attacks, take the steps below.
- E-Mails, attachments, and links from suspicious parties should not be respected.
- Files or programs should be downloaded from reliable sources.
- The most up-to-date versions of existing systems/programs should be used.
- It is advised to block IoC findings related to the attack campaign by security tools.
New KmsdBot Malware Detected for Crypto Mining Activities and DDoS Attacks
Cyber security experts have detected malware called KmsdBot, which carries out DDoS attacks and cryptocurrency mining actions by accessing targeted systems using the SSH cryptographic network protocol.
KmsdBot malware is spread on systems with weak SSH credentials by downloading the “kmsd.exe” file from a server (C2) controlled by threat actors.
KmsdBot malware has the ability to carry out scanning actions on targeted systems, spread to different systems through username and password combinations, control cryptocurrency mining processes and update itself. Also, the malware has been found to organize DDoS attacks. Layer 4 TCP/UDP or Layer 7 HTTP/GET requests are sent to strain the targeted server resources. This hinders the server’s ability to process and respond.
It is known that the number of malware that carries out cryptocurrency mining actions is increasing day by day. In the recently detected cryptocurrency mining malware campaign called KmsdBot, threat actors target gaming, automobile, and security firms. In order not to be targeted by the related malware campaign, take the steps below.
- Use public key authentication for SSH connections.
- Not using weak or default credentials for servers or deployed apps.
- Do not open attachments/links from suspicious-looking sender e-mail addresses.
- Beware of unreliable content.
- Use of up-to-date and full security tools.
- Keeping systems and apps up to date.
It is strongly advised that IoC findings related to the attack campaign are blocked by security tools.
Security News – Week 45
Published:
WordPress reCAPTCHA Plugin has an XSS Vulnerability
A vulnerability has been found in the WordPress reCAPTCHA plugin, which protects WordPress website forms from spam/robot logins, that could allow threat actors to carry out XSS (Cross-Site Scripting) attacks on affected installations.
The security vulnerability with code CVE-2022-3831 affects the “unfiltered_html” part and is caused by insufficient cleaning of user-supplied data. Exploiting the vulnerability requires administrative privileges.
The vulnerability, assessed as medium critical, affects all versions of WordPress reCAPTCHA 1.6 and earlier. The plugin has been removed from the WordPress market since November 2, 2022, and no current version fixes the vulnerability. It is advised that users using the plugin in WordPress installations at once disable or remove it to avoid being affected by the vulnerability.
Medibank Confirms Security Breach Affecting 9.7 Million Customers’ Data
Australian-based insurance firm Medibank has confirmed that they were exposed to a security breach by BlogXX threat actors. This results in access without permission to 9.7 Million customer data. BlogXX is a structure of the Revil Ransomware group that was shut down by law enforcement in 2021.
9.7 million customer data captured by threat actors in this Ransomware attack includes personal data such as name, surname, date of birth, full address, phone number, and email address. Also, the captured data also includes the Medicare numbers of customers, passport numbers, and visa details of international student customers.
After the data breach, the Medibank security team announced that they detected Ransomware on their systems on October 12, 2022, and the affected systems were isolated. It is known that BlogXX threat actors threatened Medibank with leaking the captured data if the ransom payment was not made, but Medibank refused to pay the ransom.
With more than 3.9 million customers and 4,000 staff, Medibank is among Australia’s largest private health insurance providers. Every day, many institutions and firms, regardless of large or small scale, are targeted by Ransomware attacks. It is advised to consider the following suggestions in order not to be the target of similar attacks.
- Emails, Attachments, Files/Links From Suspicious/Unknown Parties Should Not Be Relied on.
- File, Software, and Program Downloads Must Be Performed From Real And Official Sources.
- Current and Full Security Solutions should be used.
- System And Apps Should Be Keep At The Latest Version.
Dynamics 365 Customer Voice Service Detected To Be Manipulated In Phishing Attacks
Avanan security experts have determined that the Dynamics 365 Customer Voice service, a Microsoft product that institutions/firms use to get customer feedback, is manipulated in phishing attacks by threat actors. Threat actors behind this phishing campaign are planning to seize the Microsoft account data of customers by sending phishing links that appear real to customers via Dynamics 365 Customer Voice.
The campaign starts with the delivery of a phishing e-mail to the recipients via the old name of the service, “Forms Pro,” stating that they have a new voicemail. When the Play Voicemail button is clicked, targets are directed to a phishing page that mimics the Microsoft login page.
But the URL of that phishing page has no connection with Microsoft. So, Microsoft login credentials entered by targets are captured by threat actors.
The campaign is an attack that requires careful detection by targets, as the phishing link is not visible until the last step. Also, destinations are redirected from the e-mail body to a real page first, so hovering over the URL in the e-mail body does not provide protection.
In order not to be the target of phishing attacks that can be carried out using similar methods, attention is paid to the following security recommendations.
- Users should check all URL addresses, including links in the e-mail body.
- E-mails, attachments, and links from unknown parties should not be trusted.
- Login credentials thought to have been hacked should be promptly replaced by enforcing strong password policies.
Security News – Week 44
Published:
Critical Zero-Day Alarm on iOS and iPadOS
Apple has released updates to 20 security vulnerabilities hitting iOS and iPadOS operating systems, including a 0-day vulnerability known to be actively exploited by threat actors.
The 0-day vulnerability, tracked as CVE-2022-42827, exists due to a boundary error hitting the “Kernel“ part of the operating system. Threat actors can run with root privileges on the vulnerable system by triggering an out-of-bounds write error through a crafted application.
Apart from the vulnerability mentioned above, Apple has also fixed two high-severity vulnerabilities with the released iOS 16.1 and iPadOS 16 updates. In order not to be the target of attacks that can be carried out using vulnerabilities, Apple users using vulnerable versions are advised to apply the published updates at once.
Preliminary Information Released for OpenSSL Vulnerability
The OpenSSL library has put in place HTTPS secure networking in many apps. Its developers have stated that a critical security vulnerability will be fixed in version 3.0.7, released on November 1, 2022 (Reference Link). But the project developers made public announcements that did not include all details of the vulnerability, as more data was kept confidential until the update for the found vulnerability was released.
It has been announced that the critical security vulnerability detected is affected by the versions between OpenSSL 3.0 and version 3.0.6, released on September 7, 2021. Therefore the affected versions were not widely known until OpenSSL 1.x, which has been available for 12 years.
OpenSSL security vulnerabilities have a widespread impact. The HeartBleed vulnerability, discovered in April 2014, has been observed on Apache and Nginx web servers, which have a usage rate of over 66% among all active websites on the internet. But it is unknown whether the detected and declared critical vulnerability would lead to a mass exploit like HeartBleed.
To limit the risk of being affected by the relevant security vulnerability as much as possible. Until the release of the measures by OpenSSL developers, it is advised to master the “Software Supply Chain” processes. This helps to determine which apps the old version OpenSSL libraries are running. It is also advised to make preliminary preparations.
Air New Zealand Suffered A Security Breach
New Zealand’s flag carrier, a national airline in Oceania, has suffered a security breach that resulted in threat actors gaining access to customer accounts.
In the security breach, threat actors performed credential-stuffing attacks to gain access without permission to customer accounts. A credential stuffing attack is performed by trying hacked credentials until the targeted system is logged in.
Following the detection of the security breach, the airline’s officials stated that the breach did not affect any of the company’s systems, but only individual customer accounts were affected. Upon the relevant explanation, customer accounts were blocked. Customers were contacted to change their login data before using the Airpoints system again.
Logging in to more than one platform with the same login data and not enabling MFA/2FA authentication methods on the platforms cause such attacks to be seen often. It is advised to consider the following security recommendations not to be the target of similar attacks.
- The same username and password should not be used in more than one online session.
- The login data should be created by applying unique and strong password policies.
- The airline’s customers should be aware of the data that could be leaked to the internet in this breach and used in some phishing/social engineering attacks.
October 2022
Security News – Week 43
Published:
Critical Zero-Day Alarm on iOS and iPadOS
Apple has released updates to 20 security vulnerabilities hitting iOS and iPadOS operating systems, including a 0-day vulnerability known to be actively exploited by threat actors.
The 0-day vulnerability, tracked as CVE-2022-42827, exists due to a boundary error hitting the “Kernel“ part of the operating system. Threat actors can run with root privileges on the vulnerable system by triggering an out-of-bounds write error through a crafted application.
Apart from the vulnerability mentioned above, Apple has also fixed two high-severity vulnerabilities with the released iOS 16.1 and iPadOS 16 updates. In order not to be the target of attacks that can be carried out using vulnerabilities, Apple users using vulnerable versions are advised to apply the published updates at once.
Iran Atomic Energy Agency Suffered from a Breach
The Atomic Energy Agency of Iran was exposed to a security breach that resulted in the threat actors gaining access without permission to their e-mail servers, compromising their data security.
The security breach came to light when threat actors known as “Black Reward” claimed to have gained private data on their Telegram channel, including contract files, business plans, and data about other facilities. Besides the sharing, the threat actors made a threat. They said the captured data would be shared publicly if the political prisoners arrested during the recent protests against the Iranian government on October 21 were not released within 24 hours.
The Iranian Atomic Energy Agency officials confirmed the security breach by targeting e-mail servers, but it was emphasized that the captured data was unimportant. Also, it was stated that the intercepted e-mails contained technical and casual messages.
It is advised that institutions and firms take into account the following security practices in order not to be the target of targeted attacks that can be carried out in a similar way to protest and attract attention.
- Internal inventories such as e-mail servers used within the institution/firm should be used in the most up-to-date versions where the vulnerabilities are fixed.
- Institution/firm staff should not rely on spam e-mails, attachments, and links from unknown parties.
- Full security tools should be deployed to the company/company network.
Magniber Ransomware Targets Windows Users with Fake Software Updates
HP Wolf Security experts have detected that the operators of Magniber Ransomware are running a new malware distribution campaign targeting Windows home users with advanced features.
The chain of infection begins when users download a ZIP file that allegedly contains anti-virus software or a Windows 10 update from a threat actor-controlled website. But contrary to what was promised, the ZIP archive contains compressed Javascript files containing malware. JavaScript files use a variation of the DotNetToJScript technique to load a .NET executable into memory.
So the ransomware does not need to be saved to disk. Using this technique, detection and prevention methods that monitor files written to disk are bypassed, and traces left on the vulnerable system are minimized. The .NET code decodes the shell code and injects it into another process.
On the other hand, the ransomware code disables Windows’s backup and recovery features by deleting the copy files before encrypting the user files. But Magniber requires administrator privileges to disable its data recovery feature. So the malware bypasses User Account Control (UAC) control to run commands without the user’s knowledge.
But the logged-in user must be part of the Administrators group for this process to work. Magniber enumerates the files and checks the file extension against a list during the encryption process. If the file extension is in the list, the file is encrypted.
In the final stage, Magniber places a ransom note in each directory and displays the message to the user by opening it in a web browser.
While it was observed that the malware spread through MSI and EXE files in the past attacks using Magniber, it was observed that it started to be spread via JavaScript files. This happened in the said attacks carried out in September 2022.
The threat actors behind the Magniber malware are known to demand a $2500 ransom payment from infected users. It is advised to consider the following security steps in order not to be the target of this and similar ransomware campaigns.
- Administrator accounts used in line with the need should be created by considering the principle of least privilege.
- Software updates or programs should be gained from reliable and official sources.
- The data stored in the systems should be backed up at routine intervals.
- Full Anti-Virus / Anti-Malware tools should be used.
- IOC findings related to the campaign should be blocked from security tools in use.
Security News – Week 42
Published:
Magniber Ransomware Targets Windows Users with Fake Software Updates
HP Wolf Security experts have detected that the operators of Magniber Ransomware are running a new malware distribution campaign targeting Windows home users with advanced features.
The chain of infection begins when users download a ZIP file that allegedly contains anti-virus software or a Windows 10 update from a threat actor-controlled website. But contrary to what was promised, the ZIP archive contains compressed Javascript files containing malware. JavaScript files use a variation of the DotNetToJScript technique to load a .NET executable into memory.
So the ransomware does not need to be saved to disk. Using this technique, detection and prevention methods that monitor files written to disk are bypassed, and traces left on the vulnerable system are minimized. The .NET code decodes the shell code and injects it into another process.
On the other hand, the ransomware code disables Windows’s backup and recovery features by deleting the copy files before encrypting the user files. But Magniber requires administrator privileges to disable its data recovery feature. So the malware bypasses User Account Control (UAC) control to run commands without the user’s knowledge.
But the logged-in user must be part of the Administrators group for this process to work. Magniber enumerates the files and checks the file extension against a list during the encryption process. If the file extension is in the list, the file is encrypted.
In the final stage, Magniber places a ransom note in each directory and displays the message to the user by opening it in a web browser.
While it was observed that the malware spread through MSI and EXE files in the past attacks using Magniber, it was observed that it started to be spread via JavaScript files. This happened in the said attacks carried out in September 2022.
The threat actors behind the Magniber malware are known to demand a $2500 ransom payment from infected users. It is advised to consider the following security steps in order not to be the target of this and similar ransomware campaigns.
- Administrator accounts used in line with the need should be created by considering the principle of least privilege.
- Software updates or programs should be gained from reliable and official sources.
- The data stored in the systems should be backed up at routine intervals.
- Full Anti-Virus / Anti-Malware tools should be used.
- IOC findings related to the campaign should be blocked from security tools in use.
Multiple Vulnerabilities Detected in Juniper Networks Junos OS
Many critical security vulnerabilities have been found in Junos OS, a network operating system used in security and network devices built by Juniper Networks. The vulnerabilities allow threat actors to carry out unauthorized file access, cross-site scripting (XSS), and directory traversal attacks.
Some of the detected security vulnerabilities are as follows.
- The security vulnerability, tracked as CVE-2022-22241, is due to incorrect login validation hitting the J-Web part of Juniper Networks Junos OS. As a result, an unauthenticated threat actor that exploits the vulnerability can gain access to data through a crafted POST request without proper authorization.
- The vulnerability, tracked as CVE-2022-22246, is a PHP Local File Inclusion (LFI) vulnerability that affects the J-Web part of Juniper Networks Junos OS . It could allow a low-privileged authenticated threat actor to run a harmful PHP file on the vulnerable system.
- The vulnerability tracked as CVE-2022-22242 is a Cross-Site Scripting (XSS) vulnerability that affects the J-Web part of Juniper Networks Junos OS . It could allow an unauthenticated threat actor to run harmful scripts in the user’s browser in the context of a J-Web session.
- The vulnerability tracked as CVE-2022-22244 is an XPath Injection vulnerability that affects the J-Web part of Juniper Networks Junos OS. An unauthenticated threat actor can exploit the vulnerability through a crafted POST request.
These vulnerabilities, which affect all versions of the Junos operating system, are critically rated as high and have been fixed with the updates released by Juniper Networks. To avoid attacks that can be carried out using vulnerabilities, it is advised that vulnerable Junos OS users upgrade at once to released updates. As a workaround, disable J-Web or restrict access to trusted hosts only.
Timing Attacks Via Npm API Discloses Custom Package Names
An attack method that reveals the names of special packages has been found by Aqua Security experts. Firms create internal projects and custom packages of certain software products to keep their code and features private. This limits the risk of their development teams and inventories being exposed to targeted attacks.
The detected attack method includes a timing attack using the npm API. The npm Register API allows users to download existing packages and check for the existence of packages. When using the npm registry to download a package that does not exist or is set as private, the website returns a 404 HTTP error code stating that the package could not be found.
Aqua Security experts used this feature to compare the response time of 404 HTTP errors with non-existent packets to check for the presence of custom packets they created in npm.
The results showed that the response time to the request containing the name of an existing package was longer than the response time to the request made for the non-existent package.
So, threat actors can learn whether the package exists in the system through dictionary attacks by creating a list of possible package names for special packages used by institutions/firms.
After spotting the private packages of the firms, the threat actors can create fake harmful packages with the same name and trick the public/company staff into downloading them. It is predicted that such an attack could be linked to wider supply chain attacks. It is advised to take the following security measures to reduce the risk of attacks that can be carried out using the said method.
- Firms should take preventive measures by often searching npm for suspicious packages that spoof their custom packages with similar names.
- Because npm doesn’t allow same-named packages to be installed in public repositories, firms should create public packages that emulate their private packages as placeholders.
- If similar packages are found, it should be ensured that they do not contain malware, and relevant stakeholders should be informed.
Security News – Week 41
Published:
Microsoft Released Critical Security Updates
As part of the October security updates, Microsoft has released updates for 85 security vulnerabilities, including 0-day vulnerabilities known to be actively exploited by threat actors. The criticality ratings of the vulnerabilities are 15 critical, 69 high, and one medium. Also, it is stated that the published updates do not cover the “ProxyNotShell” vulnerabilities (CVE-2022-41040, CVE-2022-41082) recently detected in Microsoft Exchange Server.
Some of the critical vulnerabilities fixed by the updates are as follows.
- The vulnerability, tracked as CVE-2022-41033, is caused by a buffer overflow hitting the Windows COM+ Event System Service. The vulnerability, which affects all versions of Windows starting with Windows 7 and Windows Server 2008, allows a local user to run code with SYSTEM privileges on a vulnerable system.
- The security vulnerability, tracked as CVE-2022-37979, is caused by a Race Condition bug in Windows Hyper-V. A local user can exploit the vulnerability to gain access without permission to private data and elevate their privileges in the system.
- The security vulnerability, tracked as CVE-2022-37976, is caused by improper enforcement of security restrictions in Active Directory Certificate Services.
- The vulnerability, tracked as CVE-2022-37978, exists because the security features in Active Directory Certificate Services are bypassed. As a result, a remote user can exploit the vulnerability to carry out man-in-the-middle (MitM) attacks and gain access to network communications.
- The vulnerability, tracked as CVE-2022-41043, exists due to excessive data output by Microsoft Office apps. As a result, a local user can gain access without permission to private data in the system by abusing the vulnerability.
Updates that fix vulnerabilities affect the following Microsoft products and versions.
It is advised that users using the products and versions mentioned above at once apply the published updates in order not to be the target of attacks that can be carried out using vulnerabilities.
Toyota Confirms a Security Vulnerability Affecting Customer Data
Toyota has stated that a security vulnerability has been found that compromises the 296,019 email addresses and customer management numbers of registered persons on the T-Connect help platform. T-Connect is a support platform for unlocking Toyota vehicles that offers features such as smartphone-based digital keys, navigation services, and remote start.
The vulnerability is due to a developer tasked with building the T-Connect platform uploading the site’s source code to a GitHub public repository in December 2017. Upon inspection of the publicly available source code by Toyota officials, it was discovered that the source code contained an access key to a server that stores customer data.
Right away after the vulnerable GitHub repository was discovered, Toyota officials made it private, and the exposed access key was replaced.
Toyota has launched an investigation into the vulnerability. But there is no evidence yet whether threat actors used the vulnerability to capture data from the server.
It is advised that T-Connect users with the potential to be affected by the breach be aware of the data that may be leaked to the internet about spear-phishing/Social engineering attacks and change the login data registered to the platform by applying strong password policies.
More than 400 Mobile Apps Detected to Hijack Facebook Login Credentials
More than 400 harmful Android and iOS apps have been found by meta security experts on the official Apple and Google app stores, aiming to hijack Facebook users’ login data. It has been observed that these harmful apps are disguised as photo editors, games, VPN services, business apps, and other utilities.
The campaign chain starts with malware developers creating harmful mobile apps disguised as apps with fun or useful functions. Threat actors have begun publishing built harmful apps on official application stores. They may publish fake reviews and comments to cover up the negative comments of people who detect that the apps are harmful.
With the installation of any of these apps, users are faced with a “Facebook Login” request before using the promised features. If users log in with their login data, the harmful application captures the entered user name, e-mail, and password data.
Threat actors can use the login data they gain for some actions. These include giving full access to people’s Facebook accounts and sending fake/spam messages to one’s friends. They also include accessing private data and fraud.
There are also many real apps that offer the features listed above and require you to securely log into Facebook. To distinguish harmful apps from real apps, there are a few important things to consider before logging into a mobile app with your Facebook account.
- If social media credentials are requested to use the application, it is important for users to check whether the application can be used without giving their Facebook data. For example, a photo editing app that requires your Facebook login and password before allowing you to use it has the potential to be harmful.
- App reputation, though imprecise, provides insight into whether the app is harmful before it is downloaded. So, app reviews, downloads, and ratings, including negative ones, should be checked.
- It should be checked whether the application provides the promised features before or after login.
Considering these issues, users who suspect they have been affected by a harmful mobile application with the above features should take the following steps at once.
- The app should uninstall from the device.
- Login data of social media accounts used in the application should be changed by applying strong password policies.
- Two-factor authentication methods must be enabled.
- Login alerts should be enabled to detect access without permission attempts by unknown parties.
Security News – Week 40
Published:
$566 Million worth of Binance Coins from Binance Bridge Seized
Binance Bridge has suffered a massive cyber-attack that resulted in the seizure by threat actors of 2 million Binance Coins (BNB) worth $566 Million.
The attack was launched at 14:30 on October 6, 2022. The threat actors transferred the seized funds to their wallets through two transactions of 1,000,000 BNB each. Spotting the security breach at 18:19, Binance paused BNB Smartchain transactions.
In the statements made by Binance officials on social media, the attack was confirmed. It was announced that the security weakness that caused the attack was under control. It was also stated that a large part of the seized funds remained and secured on BNB Smartchain.
As a result of the attack, it is predicted that $70 Million to $80 Million worth of crypto money was withdrawn from Binance BNB Smartchain by threat actors. Suspended BNC Smartchain transactions have been resumed as of October 7, 2022. Investigations are about the violation continue.
Critical XSS Alarm in Canon Medical Vitrea View Software
A critical XSS vulnerability has been found in Canon Vitrea View medical image imaging software provided by Canon Medikal, which, if exploited, could allow access without permission to patient data.
The security vulnerability with code CVE-2022-37461 is caused by insufficient cleaning of the data provided by the user in the error message in the “/vitrea-view/error/” directory. As a result, a remote threat actor can exploit the vulnerability to access patient data or stored images and change the data depending on the privileges used during the session.
The vulnerability affects versions before Vitrea View 7.7.6 and has been fixed with Vitrea View 7.7.6. All Vitrea View users using 7. x versions are advised to apply the published updates at once to avoid being exposed to data breaches that can be carried out using the vulnerability.
Critical 0-Day Alarm in Microsoft Exchange Server
Two new 0-day vulnerabilities have been found hitting Microsoft Exchange Server 2013, 2016, and 2019 products.
The details of the found vulnerabilities are as follows.
- The first critical security vulnerability (SSRF), tracked as CVE-2022-41040, is due to insufficient validation of user-supplied input in the Exchange OWA interface. A remote threat actor can direct the application to initiate requests to arbitrary systems via a crafted HTTP request.
- Another security vulnerability, tracked as CVE-2022-41082, is due to incorrect login validation in Exchange Server. A remote user who has access to PowerShell Remoting on Exchange systems affected by security vulnerability can run arbitrary code on the system.
It is observed that threat actors in targeted attacks exploit these vulnerabilities. The attacks detailed by Microsoft show that the two vulnerabilities are used together in an exploit chain. The SSRF vulnerability allows an authenticated threat actor to run arbitrary code. But abusing the vulnerabilities requires authenticated access to vulnerable Exchange Servers.
Microsoft has announced that Exchange Online users are not affected by these vulnerabilities and has released a set of workarounds they should set up to reduce possible threats to their affected customers. To avoid targeted attacks that can be carried out using vulnerabilities, it is advised to at once set up the following workaround suggestions published by Microsoft and to monitor the updates to be released often.
- IIS Manager should open.
- The Default Web Site bar should be expanded.
- The Autodiscover tab should open.
- The URL Rewrite feature within the IIS framework should be clicked.
- In the Actions pane on the right, the Add Rule(s) option should open.
- Select the Request Blocking option and click OK.
- In the Add Request Rule window that opens, add the string “.*autodiscover\.json.*\@.*Powershell.*” to the URL Pattern section and click OK.
- The added rule should be selected, and the Edit feature in the Conditions frame on the side tab should be opened.
- Should change the condition entry from {URL} to {REQUEST_URI}.
Multiple Vulnerabilities Detected in Solarwinds Orion
In the Solarwinds Orion platform, which is an IT management and monitoring solution, two critical security vulnerabilities have been found. They may cause threat actors to access private/critical data and run code on the vulnerable system.
- The SQL Injection vulnerability with code CVE-2022-36961 is caused by insufficient cleaning of user-supplied data. As a result, a remote user can run arbitrary SQL commands in the application database by sending a crafted request to the affected application. Successful exploitation of this vulnerability allows remote threat actors to read, delete, modify data in the database and gain full control over the affected application.
- The security vulnerability code CVE-2022-36965 is also caused by insufficient cleaning of user-supplied data and allows a remote threat actor to carry out cross-site scripting (XSS) attacks. A remote threat actor can exploit the vulnerability to inject arbitrary HTML and script code into the user’s browser in the context of the vulnerable website. Successful exploitation of the vulnerability allows remote threat actors to gain access to private data, alter the appearance of the affected web page, and carry out phishing and malware attacks.
These vulnerabilities affect all versions of Solarwind Orion Platform 2022.2 and earlier and have been fixed with the latest SolarWinds Platform 2022.3 release. It is advised to set up the security updates published at once in order not to be the target of possible attacks that can be carried out using vulnerabilities.
Other periods: 2023 | 2022 Q4 | 2022 Q3 | 2022 Q2 | 2022 Q1 | Overview
Know What Is Exposed. Before Attackers Do.
Book a demo of the platform.
- 4.7Gartner Peer Insights
- 24hEarly warning time
- 190+Countries covered
What you see in the demo
- Your exposureAssets and services seen from the outside, starting from your own domain.
- Threats aimed at youLeaked credentials, look-alike domains and brand abuse in one view.
- From alert to actionHow findings reach your team and what to do next.