Introduction
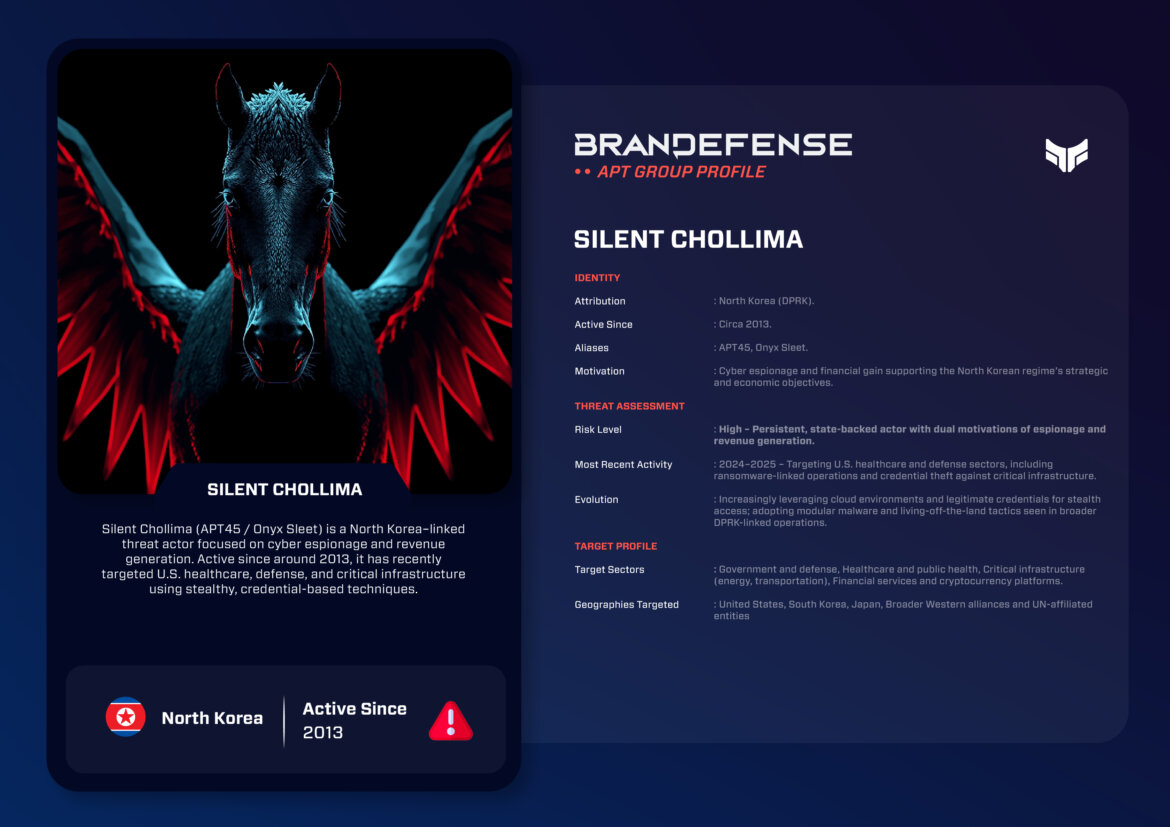
Silent Chollima, or APT45, also called Onyx Sleet, is one of North Korea’s most sophisticated and adaptable advanced persistent threat actors. The group fuses espionage with operations for money. It shows how state-sponsored cyber activity has shifted. Intelligence collection, financial theft, and disruption are now all tools of power.
The group emerged around 2013. It has targeted governmental entities, critical infrastructure, and the global financial system. This makes it a strategic asset to Pyongyang’s cyber capabilities. During 2024 and 2025, the group stepped up attacks against the healthcare sector, the defense sector, and cryptocurrency entities. It used both custom malware and legitimate tools to stay stealthy.
Silent Chollima fits into North Korea’s larger cyber strategy of easing the impact of sanctions. It does this by raising revenue for sanctioned programs, or by gaining intelligence on its adversaries.
Identity & Motivation
The term Silent Chollima is associated with the Democratic People’s Republic of Korea (DPRK). Chollima comes from Korean myth. It is a horse that flies over 1,000 li in a day (Korean mile). This is a fitting name for a team known for speed, adaptability, and a far reach in cyberspace.
The group’s main objectives fall into two categories:
1. Espionage: Collecting strategic intelligence from nations’ governments, defense contractors, and think tank organizations.
2. Financial Gain: Thievery (stealing money and cryptocurrencies). This helps North Korea escape sanctions and supports national programs, including nuclear weapons and missile programs.
Other DPRK-affiliated teams mostly focus only on financial theft. Silent Chollima is different, because it acts as a hybrid. It switches between espionage jobs and money-making efforts. It does so based on the government’s political lines, needs, and economic needs.
TTPs: Methods, Tools, and Access Strategies
Silent Chollima combines traditional APT techniques with unique approaches to target high-value victims.
– Initial Access: The group runs spear-phishing campaigns with malicious links or fake job offers. These look like recruitment messages, for example from a recruiter or reputable organizations. The group also exploits vulnerabilities in VPNs and web applications.
– Persistence: Once inside a network, Silent Chollima stays in with scheduled tasks, register changes, and custom malware families.
– Command and Control (C2): The group avoids questionable traffic and C2 over typical protocols and connections. Instead, it tunnels C2 communications over HTTPS or through legitimate cloud services, including Dropbox or OneDrive.
– Malware Arsenal: Silent Chollima uses tools including DTrack, Maui ransomware, and KEYMARBLE. They harvest credentials, conduct reconnaissance and encrypt files. These tools may also be connected to DPRK-linked operations, especially those tied to the well-known Lazarus group.
– Techniques: Silent Chollima relies heavily on living-off-the-land tactics. It uses PowerShell, CertUtil, and Windows Management Instrumentation (WMI) to avoid detection. It also moves laterally with SMB and RDP. This lets it escalate privileges and exfiltrate data.
Overall, this change in techniques shows a much more sophisticated trend in attacks. They have moved from traditional phishing to more complex, layered attacks that combine ransomware with intrusion and espionage.
Notable Operations
Silent Chollima’s operations reflect North Korea’s shifting focus and the impact of global events.
– 2018: DTrack Campaign – The group ran a major infiltration campaign against Indian financial institutions, aimed at ATMs. It showed some technical overlap with Lazarus. It also established Silent Chollima’s presence in the North Korean cyber threat landscape.
DTrack also appeared in 2019 at India’s Kudankulam nuclear plant, where the Indian government named no actor, as our incident page explains.
– 2021: Healthcare Sector Infiltrations – During the COVID-19 pandemic, Silent Chollima went after hospitals and vaccine research laboratories. It stole sensitive biomedical information and exploited healthcare networks for profit.
– 2023: Maui Ransomware – In 2023, the U.S. Department of Justice linked ransomware attacks on the healthcare sector to APT45, marking a notable pivot toward disruptive cybercrime.
– 2024: Credential Theft Campaigns – Using spear-phishing campaigns and known VPN vulnerabilities, it breached many defense and technology contractors in the United States and South Korea.
– 2025: Cryptocurrency – Continuing its model of finance-driven cybercrime, Silent Chollima ran large-scale thefts from cryptocurrency exchanges. It laundered the stolen funds through mixers and decentralized platforms to hide them.
In every case shown, the group’s criminal intent is clear. The cases also show the dual nature of its operations. Similar technical methods served both espionage and cybercrime.
Recent Developments (2024–2025)
At the same time, the use of ransomware has also evolved. The group no longer seeks mass infection. It now targets organizations that will give either high financial gain or intelligence value. This reflects a wider North Korean trend. APT actors increasingly combine espionage with ransomware techniques.
Silent Chollima has also shown interest in supply chain manipulation. In late 2024, the group compromised software updates meant to install malware on downstream clients. This is similar to Russian and Chinese APT actions. These hybrids suggest possible knowledge sharing and/or efforts to develop similar hybrid capabilities among state actors.
In October 2026, Microsoft reported that Onyx Sleet created over 100 target-specific PDF lures in August and September, dozens at a time within minutes. It also said the group has used the agentic AI framework ARTEX. Our analysis of North Korean AI adoption covers both findings.
Strategic Impact and Implications
Silent Chollima is a snapshot of contemporary state-sponsored threats that combine cybercrime and cyber espionage. This dual-purpose method makes it harder for policymakers to settle on attribution and a response. For example, a ransomware attack for money may result in intelligence gains or even fund a national imperative.
From a defense perspective, Silent Chollima’s effectiveness exposes weaknesses in organizations that rely on unpatched systems, poor credential management, and limited monitoring of cloud services. The mix of espionage and crime requires defenders to treat financially oriented intrusions as possible state-sponsored attacks. This complicates traditional responses.
In addition, the group’s sustained attacks on healthcare and financing are a systemic risk. By incapacitating hospital networks or exploiting financial platforms, additional disruptions may achieve greater consequences for the DPRK.
Conclusion & Defensive Takeaways
Silent Chollima (APT45/Onyx Sleet) is now one of North Korea’s most effective cyber teams. It combines stealth, versatility, and dual, if not mixed, objectives. This makes it a notable threat to both public and private industries. The past ten years of activity show a clear trend. North Korea is skillfully evolving its cyber capabilities to advance strategic and financial objectives while keeping plausible deniability.
Defensive Assessment:
– Use zero-trust architecture, ongoing, and privilege management.
– Update supporting technologies such as VPN, remote access solutions, and externally-exposed applications.
– Stay aware of suspicious behavior in cloud environments and legitimate file-sharing sites.
– Threat hunt against DPRK malware signatures such as Maui, DTrack, and KEYMARBLE.
– Run more user awareness campaigns to make phishing and social engineering less effective.
Silent Chollima succeeds because it adapts faster than its targets. Learning how it operates is the first step in reducing the impact of one of the most adaptive and aggressive groups on the world stage.
You can download and review the sheet for all the details!