Introduction
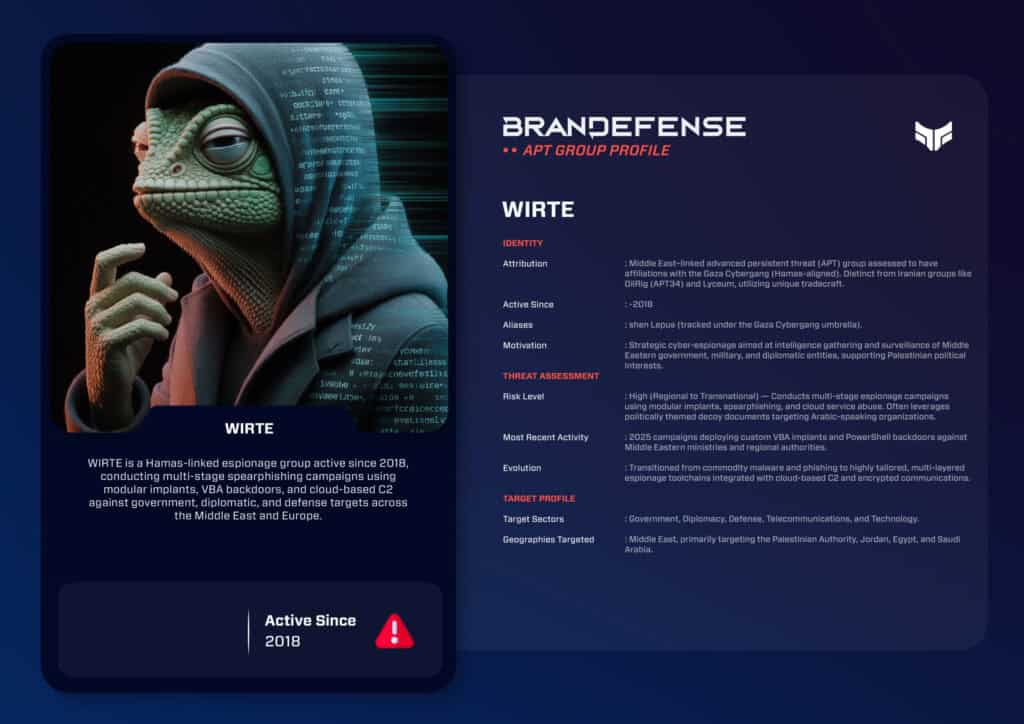
WIRTE is a cyber espionage group, also known as Ashen Lepus, active since at least 2018. It is attributed by MITRE ATT&CK as a believed subgroup of the Hamas-affiliated Gaza Cybergang. It mainly uses spearphishing emails, PowerShell scripts and cloud services to spy on governments and diplomats in the Middle East.
The WIRTE APT group has been conducting regional espionage for several years, dating back to at least 2018. The cybersecurity community has not always attributed WIRTE as a separate APT due to widespread misattribution as an Iranian state-sponsored actor. In reality, MITRE ATT&CK believes WIRTE (also known by the codename “Ashen Lepus”) to be a subgroup of the Hamas-affiliated Gaza Cybergang.
Despite having limited resources, WIRTE has conducted successful, highly estimated, operations through precision execution. The WIRTE actor successfully weaponizes basic technology (e.g., Microsoft Office macros, PowerShell, and cloud services). With it, the group keeps a persistent presence on networks and collects sensitive information. WIRTE flies under the radar and avoids the flashy techniques, such as zero-day exploits, that are traditional for top-tier APTs. In this way it has built a very prolific and discreet espionage capability within the Middle East.
- Also known as.
- Ashen Lepus.
- Active since.
- At least 2018.
- Attribution.
- Believed to be a subgroup of the Hamas-affiliated Gaza Cybergang, attributed by MITRE ATT&CK.
- Region.
- Middle East.
- Tools.
- LitePower, Ferocious, SurveyScript, VBS implants.
Who is WIRTE and what drives the group?
WIRTE (a separate entity from the Iranian IRGC) has its own specific tradecraft. It aligns with the group’s Palestinian political objectives. WIRTE acts as the highly active intelligence-gathering branch of the greater Gaza cybergang network.
Motivations:
- Regional Espionage: Collecting information on national defense, external relationships, and internal political developments within Middle Eastern states. The targets are government agencies, military entities, and diplomats in the Palestinian Authority, Jordan, Egypt and Saudi Arabia.
- Strategic Intelligence Support: The group’s second motivation is to provide actionable strategic intelligence. This supports the geopolitical/military objectives of Hamas and other Palestinian factions that primarily focus on monitoring realignment.
- Counterintelligence Operations: The monitoring of dissidents and communication regarding diplomacy that impact Palestinian-related political activity in the Gaza Strip.
What tactics, techniques and procedures does WIRTE use?
WIRTE uses both a cost effective and efficient method to operate. The organization utilizes smaller payload modular implants and uses social engineering to develop numerous campaigns.
1. Initial Access
WIRTE primarily gains access via spearphishing emails; these emails contain malicious document attachments and are written in Arabic or English. The poisoned documents tend to be related to political events and diplomatic meetings. When the poisoned documents are opened, the files execute embedded VBA macros (Visual Basic for Applications) or PowerShell commands. These deploy the first stage payloads.
In a small number of cases, WIRTE has used a method called remote template injection. The malicious document then downloads a payload stored on a server controlled by WIRTE. This gives WIRTE the ability to deploy a payload that is dynamically updated.
- Spearphishing emailArabic or English document sent as an attachmentTechnique T1566.001 (MITRE ATT&CK, opens in a new tab)
- Document openedEmbedded VBA macro or PowerShell command runsTechnique T1059.001 (MITRE ATT&CK, opens in a new tab)
- First stage payloadDeployed, sometimes pulled by remote template injection
- Cloud C2HTTPS channels through cloud platforms hide the traffic
2. Persistence and Privilege Escalation
WIRTE maintains its persistence using registry changes, scheduled tasks, and hidden directories. The group’s custom malware families, such as LitePower and Ferocious, were designed for stealth and persistence on compromised systems. The group is reported to have collected credentials for use in escalating privileges by leveraging PowerShell scripts and Windows Management Instrumentation (WMI) queries. The credentials that WIRTE collects are subsequently stored for lateral movement.
3. Command and Control (C2)
To avoid traditional perimeter defenses, WIRTE uses HTTPS-based command-and-control (C2) channels through cloud platforms (e.g., Google Drive, Dropbox, OneDrive). These conceal the communication within regular traffic. That makes it more challenging to take down their infrastructure. Additionally, WIRTE has started using alternative channels of communication, like DNS tunneling, to allow for communication when their primary C2 domains are blocked.
4. Malware and Tools
WIRTE has just under a dozen tools and malware families. Some examples include:
- LitePower: A lightweight PowerShell-based “backdoor” that allows for executing remote commands, downloading secondary payloads and collecting information about the system.
- Ferocious: A modular implant that was designed for persistence using obfuscated PowerShell code and had data exfiltration capabilities.
- SurveyScript: A reconnaissance tool for gathering system metadata and building out a map of the network topology.
- VBS Implants: Served as simple script-based payloads to be used at the initial stages of infection.
WIRTE mainly uses script-based malware, which is part of an ongoing trend of rising script-based malware use. Script-based malware tends to be more flexible, harder to detect, and easier to customize.
5. Exfiltration and Evasion
Data exfiltration occurred through encrypted HTTPS channels and through cloud storage systems. These hid at least part of WIRTE’s malicious actions among all the other legitimate users. WIRTE compressed data before encrypting it and uploading it to cloud storage. It frequently deleted the temporary files created during this period to reduce its potential tracking sources.
When possible, WIRTE exfiltrated data using Living-Off-the-Land (LOLBin) tools. These are built-in Windows tools (e.g., PowerShell, CertUtil, CMD). This minimized WIRTE’s digital forensics footprint.
Notable Operations
WIRTE has completed numerous targeted espionage operations over the past few years. Each one increased both its stealth and its precision and chance of success.
- 2019 – Government Espionage Campaigns: The groups’ early operations targeted ministries in Jordan and Lebanon. They used spearphishing documents with themes related to regional cooperation and energy policy.
- 2021 – Ferocious Campaign: WIRTE initiated the Ferocious campaign. It deployed a PowerShell payload through malicious Office macros to compromise Saudi Arabian and Emirati diplomatic networks. This campaign signified the groups’ movement toward modular PowerShell-based Frameworks through the use of Ferocious malware.
- 2023 – Cloud C2 Expansion: The group began to use Google Drive and OneDrive as C2 communication channels. It also integrated cloud APIs to manage infected hosts. This campaign reflects a trend toward operational maturity.
- 2025 – Strategic Espionage Wave: The group has also updated and refined its operations in the changing threat landscape. They now focus only on the Middle East, with an emphasis on the Palestinian Authority and adjacent countries. Their goal is to assess changes in alliances and security policies, as well as domestic developments that affect the Gaza Strip.
These operations illustrate WIRTE’s commitment to intelligence-related objectives while maintaining plausible deniability in shared infrastructure with other groups.
Evolution and Tradecraft
WIRTE’s evolution underlines an approach based on resilience, cost efficiency, and persistence all characteristics that prioritize these factors over sophistication. Unlike top-tier actors who utilize custom zero days, WIRTE decided to maximize existing, substantive tools to conduct longer-term intelligence collection efforts.
Evolutionary Highlights:
- 2018–2020:Early phishing campaigns that leveraged uncomplicated VBS scripts and remote templates.
- 2021–2023: Modular implants (Ferocious, LitePower) were used and C2 was being cloud-based.
- 2024–2025: Sharper operational tempo, improved infrastructural reach, and increased efficiency in Arabic-language lures.
These marks of evolution show how regional cyber units have become more professional. Smaller entities, like WIRTE, help collect intelligence towards larger strategic goals.
How can defenders counter WIRTE?
WIRTE is critical to the regional efforts of Gaza-based cybercriminal groups. Its campaigns have provided compelling data on how mid-level APTs can succeed. They use social engineering tactics and skills, scripted attacks and cloud-based technologies as part of their strategy.
- Control VBA execution macros at the macro level (macro disablement) in any Office products.
- Provide advanced email security with stronger phishing protections in addition to performing a sandboxed analysis of inbound Microsoft Office email attachments.
- Audit PowerShell execution logs for unusual activity correlated between the LitePower implant and the Ferocious implant.
- Inspect any outbound connections to cloud services and correlate unauthorized uploads of sensitive data with the identity of the internal user.
- Collaborate with local CERT to share indicators of compromise (IOCs) from their incidents in order to identify any structure that might be reused.
Conclusion
WIRTE (Ashen Lepus) is a robust, stable, and professional cyber-espionage operation that provides support to intelligence needs within the Hamas-aligned Gaza Cybergang ecosystem. They employ the combination of low-tech but effective cyber instruments and culture-based, manipulative lures as a long-term cyber threat in the Middle East. WIRTE’s continued use of established technology at low visibility will let regional advanced persistent threats extract substantial intelligence value from operations that are inexpensive to run. To counter this threat actor, defenders must thoroughly understand the geopolitical intelligence and flexible tradecraft that motivate WIRTE.
You can download and review the sheet for all the details!