


1. Executive Summary
In short
In a two-week observation window ending 18 November 2026, Odin by Brandefense mapped 238 mobile and desktop RAT listeners on 160 hosts, plus one open directory holding 40 botnet-themed files. Three separate ecosystems appear: HookBot Android banking panels, multi-port Windows RAT servers and Telegram-themed flood kits. Only six hosts carry enough signals to block. Block those six, hunt default RAT certificates and ports 56001 to 56003, and limit Telegram Bot API traffic to approved hosts.
Commodity cybercrime runs separate markets for mobile banking panels, desktop remote access trojans (RATs) and distributed denial-of-service (DDoS) kits. All three rent cheap virtual private servers (VPS) and use public messaging APIs. This report maps where these tools listen, which fingerprints give them away, and which hosts are safe to block.
Twelve HookBot feed entries hold one corroborated panel and eleven older entries.
A server in Germany, 152.70.24[.]49, shows a dedicated HookBot panel certificate and JARM fingerprint in November 2026. The other 11 entries carry first-seen dates from 2025 and no fresh panel markers. They belong on watchlists. Public research documents HookBot's Accessibility abuse, overlays and VNC screen control; we saw no victim devices.
Desktop RAT operators pack up to 22 listener ports onto one VPS.
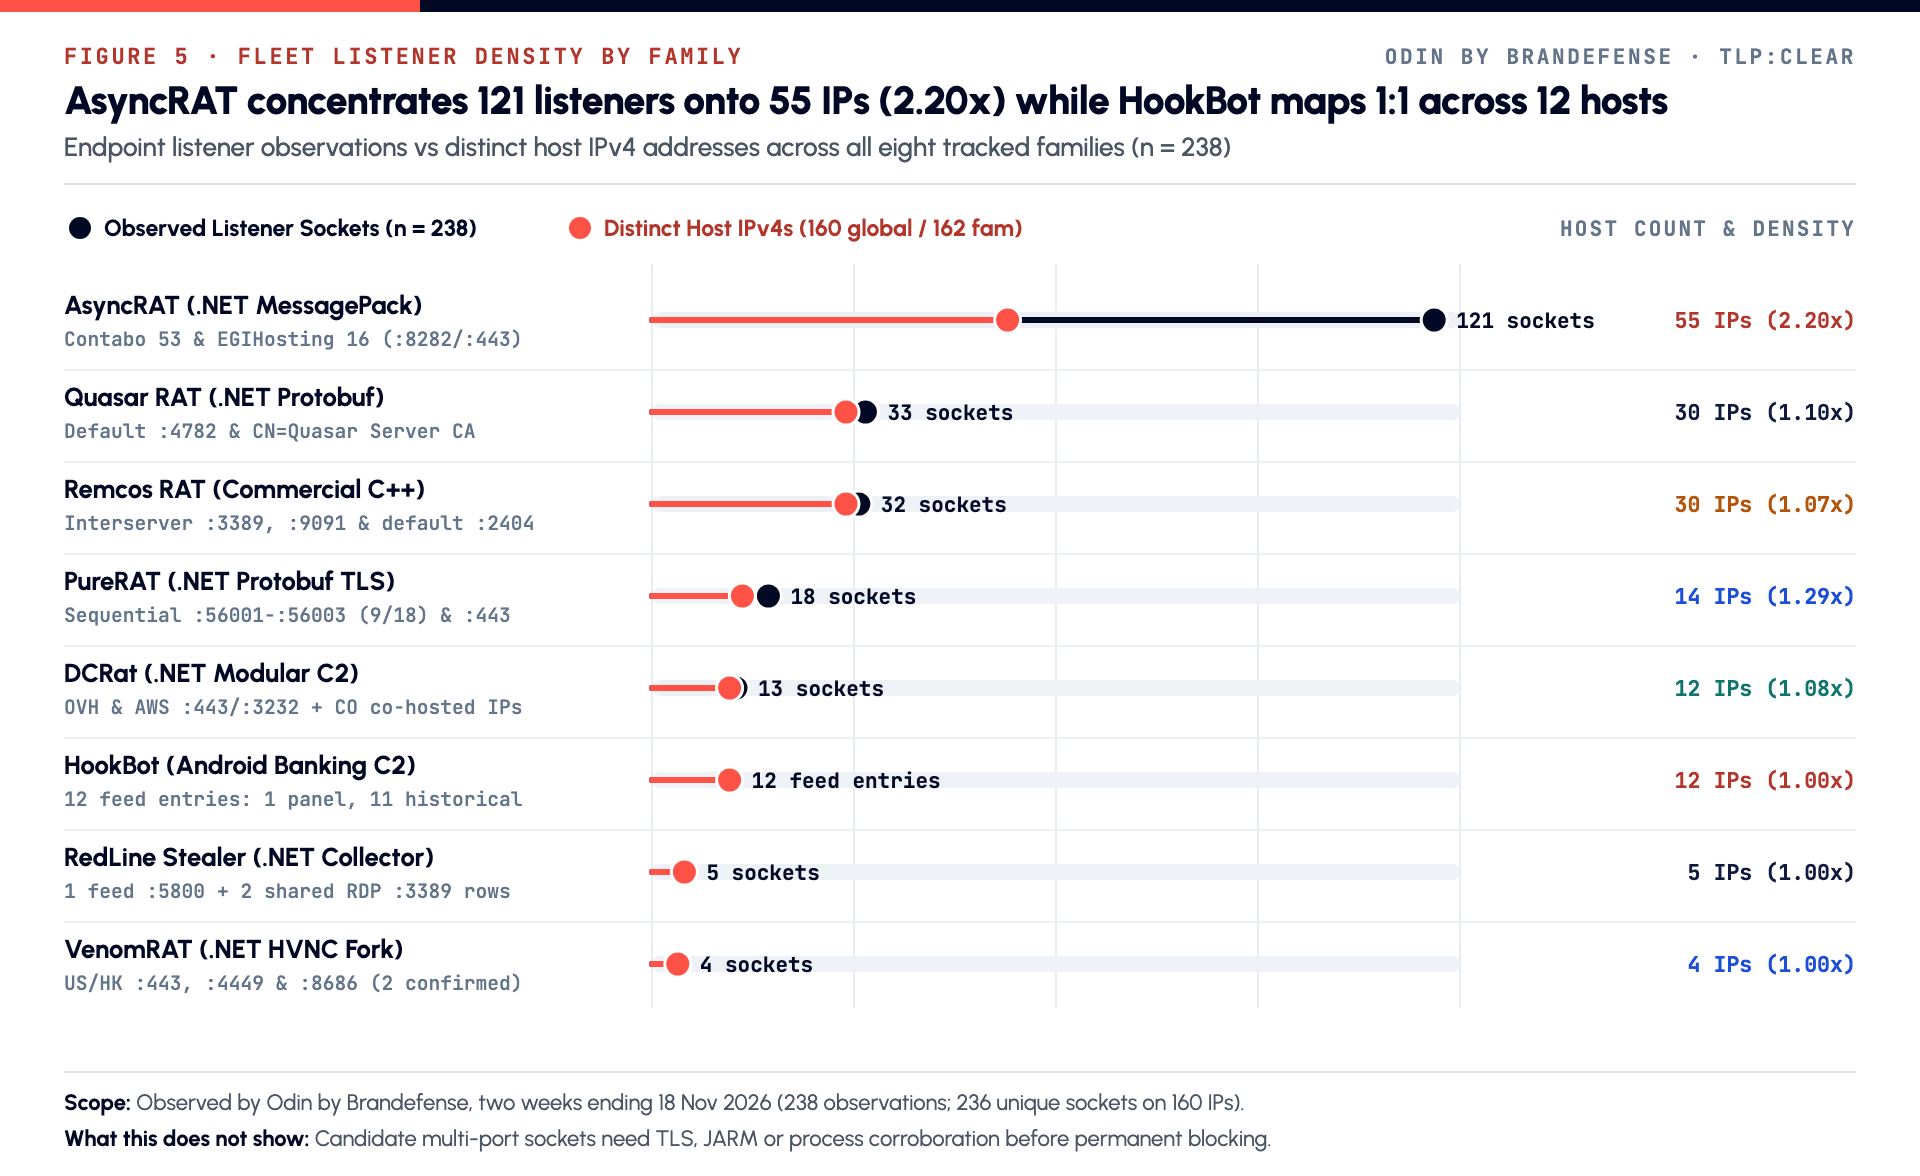
Across 226 desktop listeners in seven families, AsyncRAT averages 2.20 listeners per host. One Contabo server binds 22 ports. PureRAT places 9 of its 18 candidate listeners on the sequential ports 56001 to 56003.
An open directory on port 755 lists 40 botnet-themed files.
The files total 14.91 MB, including 7 ZIP archives and 31 JavaScript files. Their 39 stored files yield 33 unique SHA-256 hashes in five duplicate groups. File contents and server ownership are unverified, so the host stays on a watchlist.
Three Decisions for Leaders
- Treat Android Accessibility grants on banking devices as a fraud signal. Require Google Play Integrity attestation, and detect active Accessibility services and screen projection during transfers. Block the corroborated panel 152.70.24[.]49 and keep the 2025 HookBot entries on watchlists.
- Detect RATs by certificate, JARM and port density, not single ports. Block only the six multi-signal hosts. Hunt the default AsyncRAT and Quasar certificates and TLS handshakes on ports 56001 to 56003. Keep candidate hosts on watchlists.
- Allow Telegram Bot API traffic only from approved automation hosts. Alert when script interpreters, abused .NET framework binaries or programs in user-writable folders connect to Telegram API domains or
/botpaths.
The Study in Numbers
| Number | What it is |
|---|---|
| 238 | Mobile and desktop RAT listener observations (236 unique family, IP and port combinations) on 160 hosts |
| 12 | HookBot feed entries: 1 corroborated panel and 11 older entries for watchlists |
| 121 | AsyncRAT listeners on 55 IPs (2.20 per host), up to 22 ports on one Contabo VPS |
| 18 | PureRAT candidate listeners on 14 IPs; 9 of them on ports 56001 to 56003 |
| 40 | Files (14.91 MB) indexed on the open directory on port 755 |
| 33 | Unique SHA-256 hashes across the 39 stored files, in 5 duplicate groups |
| 6 | Hosts with enough independent signals to block |
How to use this report.
Security and fraud leaders can read Chapter 1, Chapter 6 and Chapter 7. SOC and detection engineers should start with Chapters 7 to 9. CTI analysts will find the HookBot, RAT and open-directory detail in Chapters 2 to 5.
2. Three Separate Ecosystems
In short
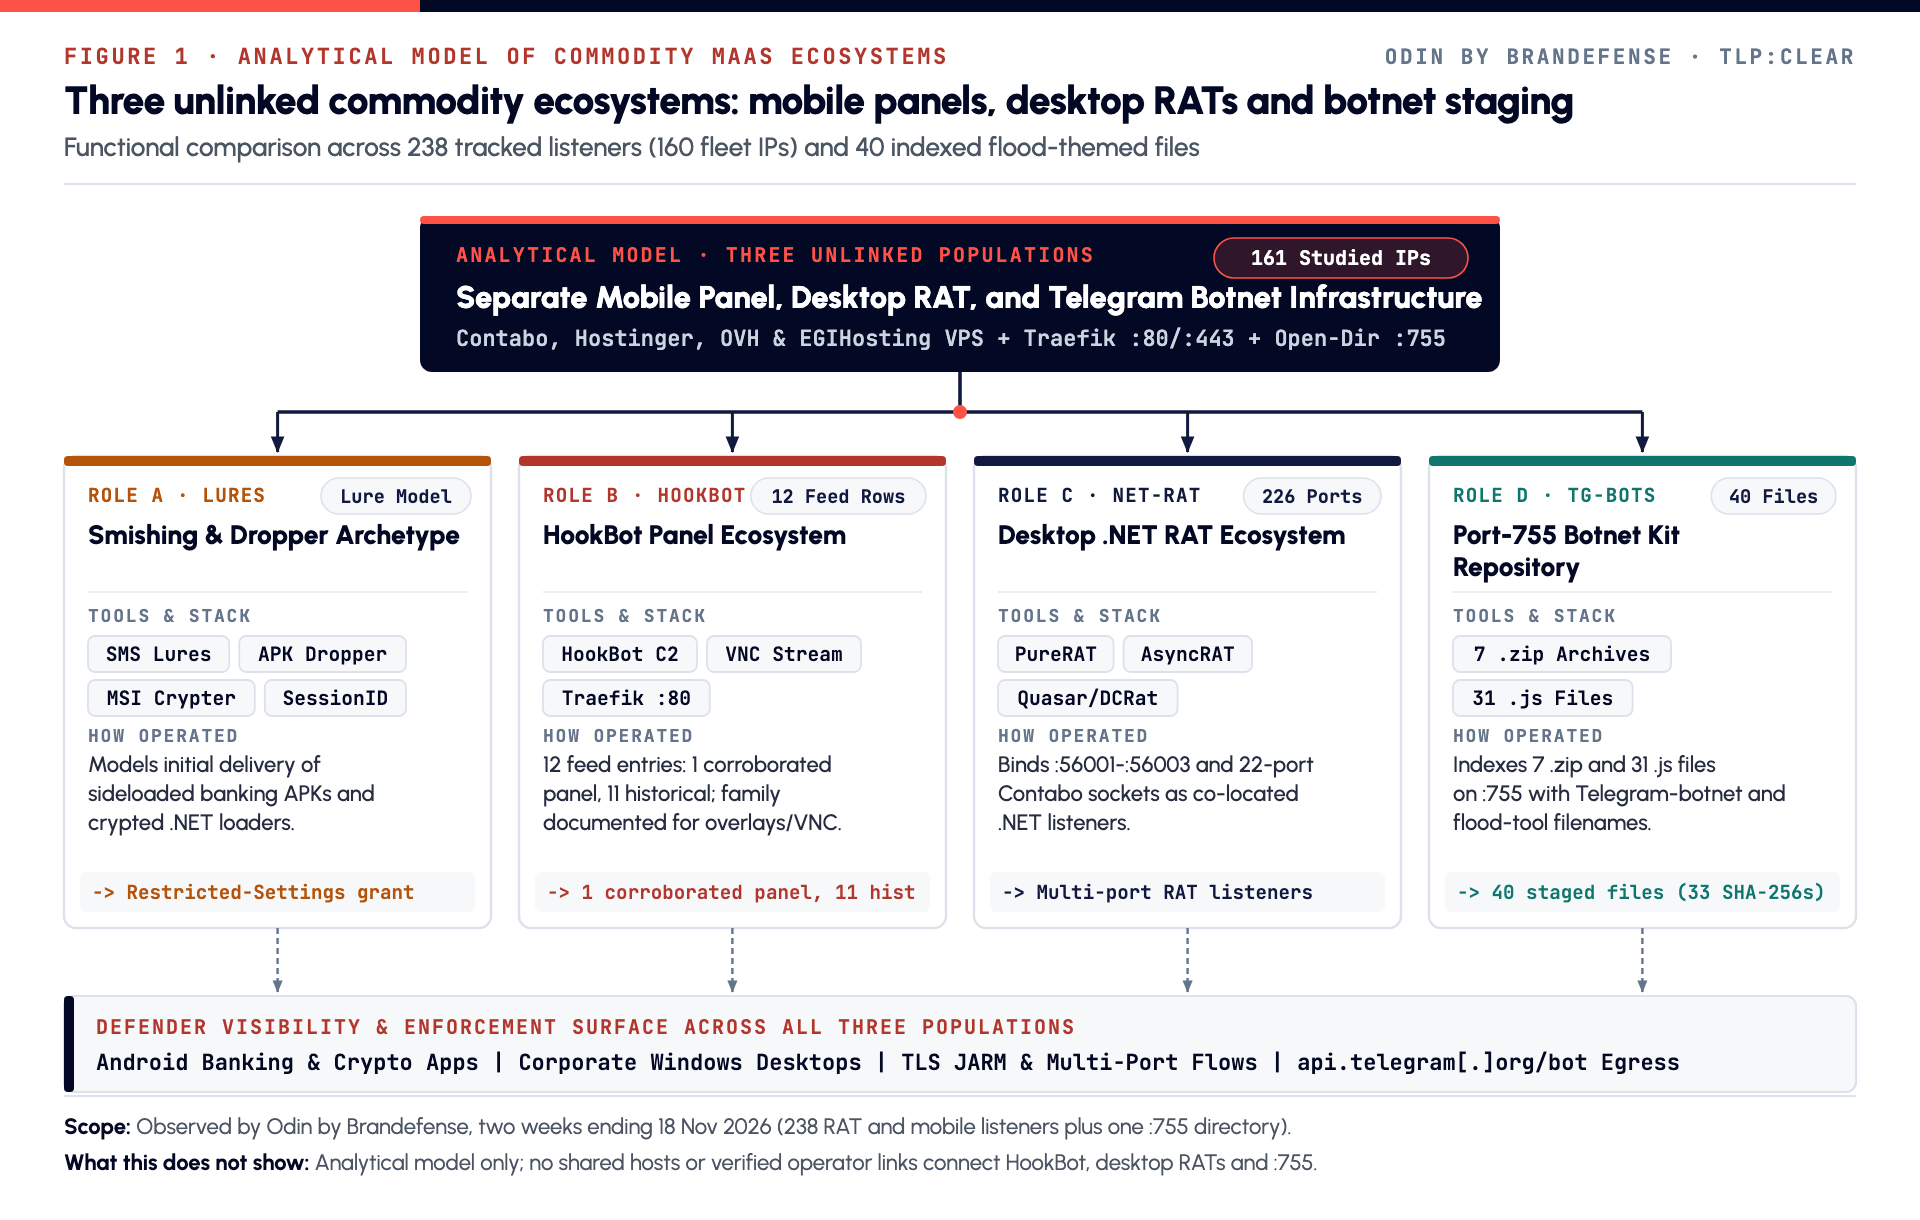
The data shows three populations that share no IP address, certificate or verified operator link. We compare them with an analytical model of four roles, not as one coordinated group.
What was observed
In the window, Odin by Brandefense recorded 238 listener observations. They cover one Android banking framework, HookBot, and seven Windows RAT or stealer families: AsyncRAT, Quasar, Remcos, PureRAT, DCRat, RedLine Stealer and VenomRAT. Separately, one open HTTP directory on port 755 listed 40 botnet-themed files.
The 12 HookBot hosts, the 148 desktop RAT hosts and the port-755 server share no IPv4 address. Together they make 161 studied hosts. Timestamps in this report are observation times, not infection times.
Families at a glance
Density is listeners per host. A value above 1.00 means operators stack several ports on one server.
| Family | Platform and protocol | Listeners | Distinct IPs | Density | Status |
|---|---|---|---|---|---|
| AsyncRAT | Windows .NET, MessagePack over TLS | 121 | 55 | 2.20x | 1 confirmed, 11 suspected, 109 candidate |
| Quasar | Windows .NET, Protobuf over TLS | 33 | 30 | 1.10x | 2 confirmed (1 to block, 1 on a dynamic ISP), 4 suspected, 27 candidate |
| Remcos | Windows C++, RC4 or TLS | 32 | 30 | 1.07x | 25 suspected, 7 candidate |
| PureRAT | Windows .NET, Protobuf over TLS | 18 | 14 | 1.29x | 18 candidate (9 on ports 56001 to 56003) |
| DCRat | Windows .NET, modular C2 | 13 | 12 | 1.08x | 1 confirmed, 3 suspected, 9 candidate |
| HookBot | Android, HTTP and VNC behind Traefik | 12 | 12 | 1.00x | 12 feed-confirmed (1 corroborated, 11 older) |
| RedLine Stealer | Windows .NET, HTTP or TCP stealer | 5 | 5 | 1.00x | 3 feed-confirmed (all watchlist), 1 suspected, 1 candidate |
| VenomRAT | Windows .NET, HVNC fork | 4 | 4 | 1.00x | 2 confirmed, 2 candidate |
Adding the per-family hosts gives 162 addresses. The true count is 160, because two Colombian telecom addresses host more than one family. One binds AsyncRAT on ports 5010 and 5011 plus DCRat on 5020. The other, a dynamic ISP address, binds Remcos on 3000 and 3001 plus DCRat on 30001.
The 238 observations reduce to 236 unique sockets. Two sockets were recorded twice: 102.220.163[.]109:443 (AsyncRAT) and 141.98.157[.]101:2288 (Quasar).
The four-role model
This is an analytical model. It compares how commodity malware-as-a-service (MaaS) markets specialize. It does not claim handoffs between groups.
| Role | What it covers | Evidence base |
|---|---|---|
| A. Delivery | Sideloaded Android .apk droppers that use session-based installers to get past Android 13 to 15 Restricted Settings, plus crypted Windows .msi and .zip loaders | Public reporting only |
| B. HookBot panels | Web panels built to control Android implants with overlays, PIN and 2FA capture, and VNC screen control | 12 feed entries; no victim handsets seen |
| C. Multi-port desktop RATs | VPS on Contabo, OVH, HostPapa and EGIHosting binding several ports per host | 226 desktop listeners; any split by affiliate or build is unverified |
| D. Botnet kit directory | Open directory with ZIP and JavaScript files whose names suggest Telegram botnets and flood tools | 40 indexed files; contents not inspected |
3. HookBot Android Banking Panels
In short
Of 12 HookBot feed entries, only 152.70.24[.]49 in Germany shows November 2026 panel markers. The other 11 carry first-seen dates from 2025 and go to watchlists.
HookBot descends from the leaked Ermac and Hook Android banking trojans. CSIRT KNF, the Polish financial supervisor's CSIRT, documents it as an on-device fraud (ODF) trojan. On-device fraud means the attacker starts transfers from the victim's own phone and logged-in banking session. Our view is the panel side only. We saw no victim handsets.
The corroborated panel
| Field | Value |
|---|---|
| Address | 152.70.24[.]49, port 80 (also port 8443) |
| Hosting | Oracle Corporation, Germany |
| TLS certificate | CN=panel.pecufos[.]com |
| JARM | 1dd40d40d00040d00042d43d000000831b6af40378e2dd35eeac4e9311926e |
| Page title | HOOKBOT PANEL (reported on port 8443) |
| Observed | 13 November 2026 |
The certificate and JARM on port 80 are directly observed. Feed records add the HOOKBOT PANEL title on port 8443 and eight separate HookBot fingerprint matches. These cover the panel title, HTTP body hashes, certificate subject and SAN, a fork's panel title, and two host-rotation hashes. Together, these signals support blocking.
The eleven older entries
The other 11 entries carry earliest first-seen dates between July and November 2025. None shows a panel body hash or fresh November 2026 panel marker. Their addresses are withheld.
| Country | Hosting | Port | TLS and JARM | Earliest first-seen |
|---|---|---|---|---|
| ID | Amazon.com, Inc. | 443 | CN=TRAEFIK DEFAULT CERT, JARM 29d29d...5a77db | 11 Nov 2025 |
| CL | The Constant Company | 443 | CN=TRAEFIK DEFAULT CERT, JARM 26d26d...9cdc13 | 26 Nov 2025 |
| DE | Contabo GmbH | 80 | CN=TRAEFIK DEFAULT CERT, JARM 3fd3fd...51d0e6 | 3 Oct 2025 |
| DE | Contabo GmbH | 80 | CN=TRAEFIK DEFAULT CERT, JARM 3fd3fd...51d0e6 | 4 Oct 2025 |
| US | RouterHosting LLC | 80 | CN=TRAEFIK DEFAULT CERT, JARM 3fd3fd...7899fb | 23 Sep 2025 |
| GB | EE Limited | 443 | Feed tag only | 11 Jul 2025 |
| ID | Hostinger International | 443 | Feed tag only | 23 Oct 2025 |
| LT | Hostinger International | 80 | JARM 0003fd...1f6145 | 18 Aug 2025 |
| LT | Hostinger or unattributed | 80 | Feed tag only | 16 Oct 2025 |
| NL | Ultahost, Inc. | 80 | Feed tag only | 13 Oct 2025 |
| Unattributed | VPS | 80 | Feed tag only | 14 Sep 2025 |
Five of these hosts present the default certificate of the Traefik reverse proxy. The two German Contabo servers share the exact JARM 3fd3fd00000000000043d3fd3fd43d79451d8c63b099acafdbabb24551d0e6. Their first-seen dates are 18 hours apart. That fits a standard Docker reverse-proxy template.
A first-seen date marks when a record entered the feed, not how long the panel stayed up. Addresses may have been reassigned since. One entry sits in EE Limited telecom space. Keep all 11 on watchlists until a live HOOKBOT PANEL banner is seen again.
What HookBot is built to do
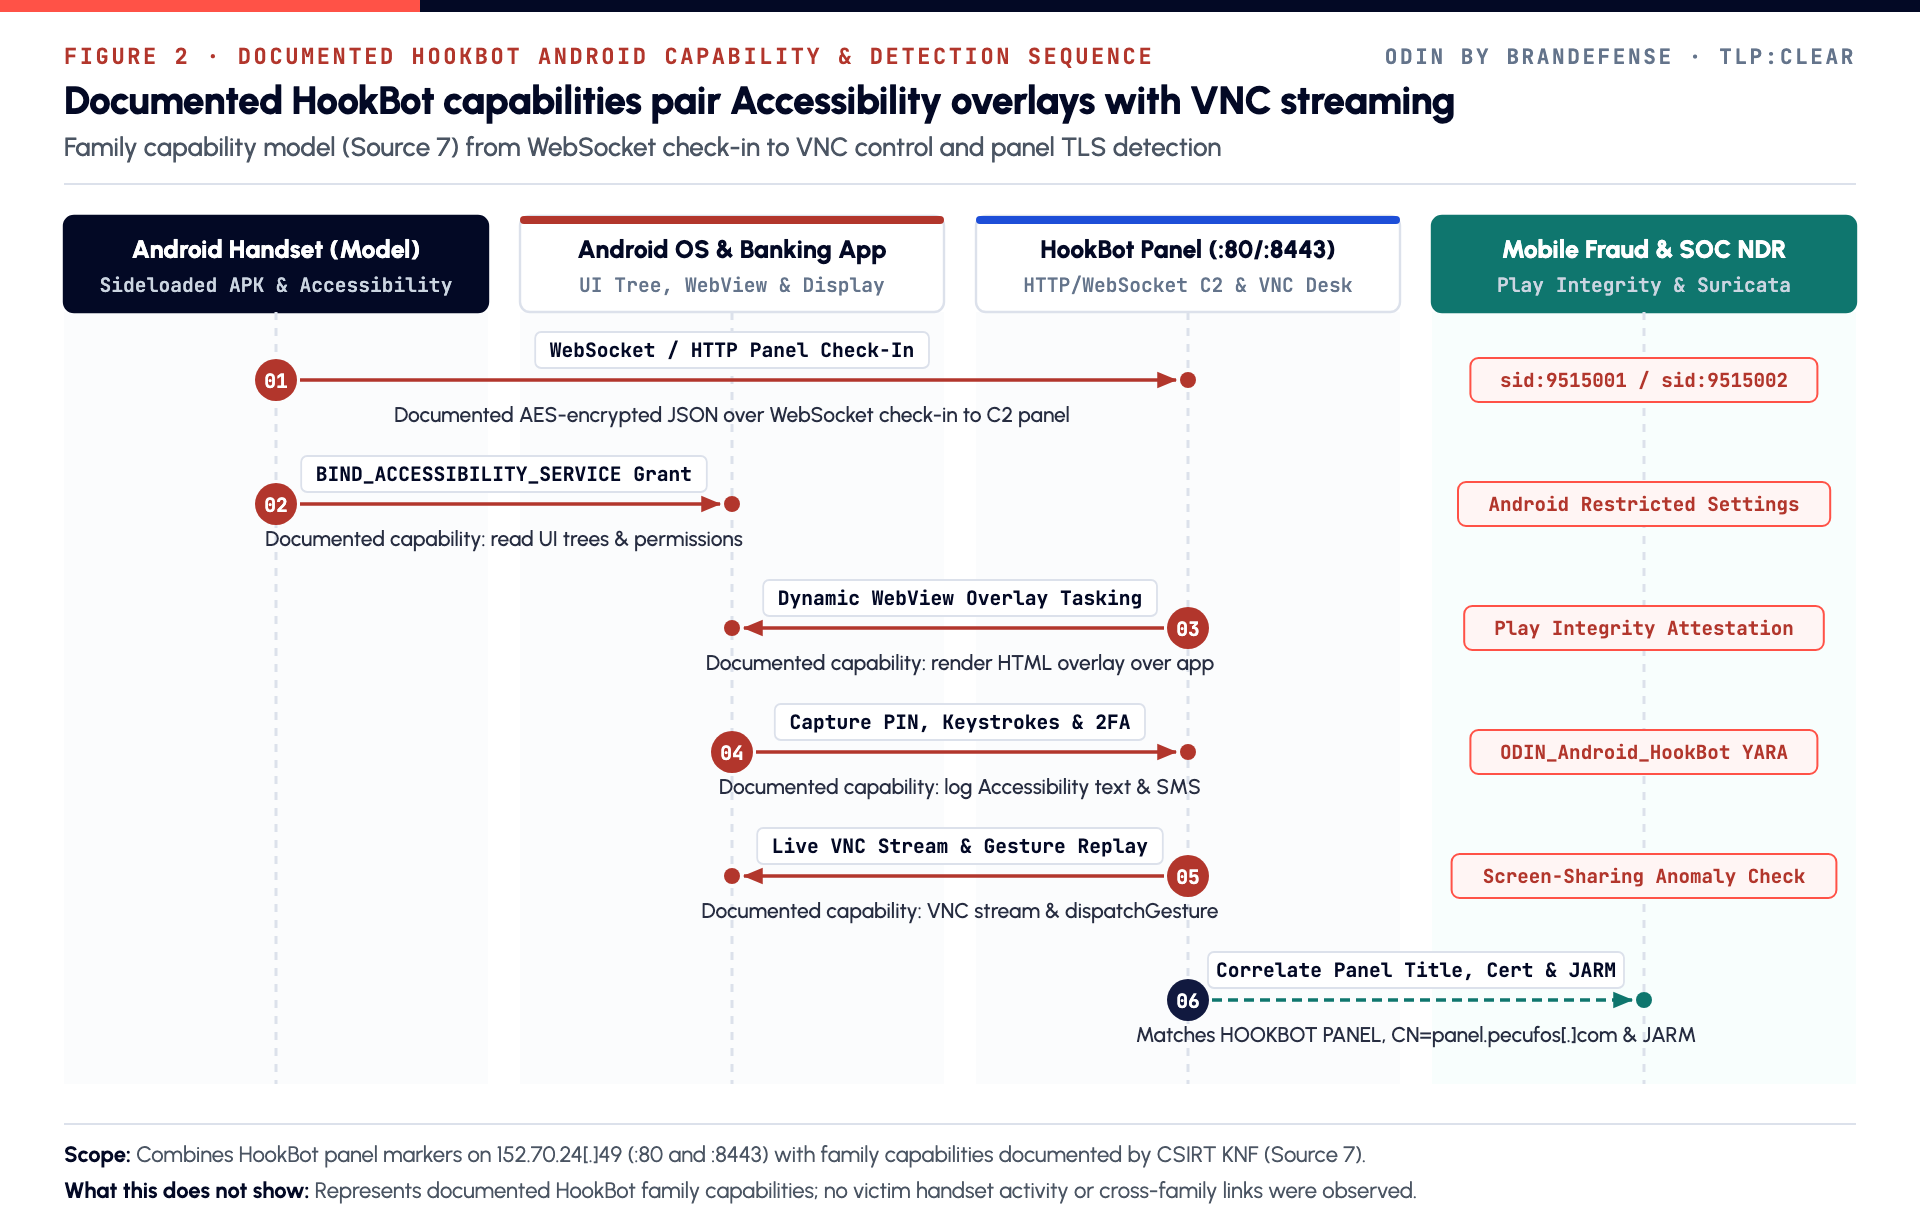
CSIRT KNF's reverse engineering, with MITRE ATT&CK Mobile and the Android reference, documents four capabilities. None was seen on a victim device in this study.
| Capability | How it works | ATT&CK |
|---|---|---|
| Accessibility abuse | Requests BIND_ACCESSIBILITY_SERVICE to read UI trees (AccessibilityNodeInfo), auto-approve MediaProjection and SMS permissions, and block Settings or uninstall | T1516 |
| WebView overlays | Watches the foreground app and draws a C2-supplied HTML login form over banking apps; talks to the panel with AES-encrypted JSON over WebSocket | T1417.002 |
| Keylogging and 2FA capture | Logs text-change events such as lock-screen PINs, seed phrases and one-time codes; intercepts SMS and bank push notifications | T1417.002 |
| VNC control | Streams the screen to the panel behind a black overlay, so an operator can replay taps with dispatchGesture inside a logged-in session | T1516 |
Because the implant encrypts its WebSocket traffic with AES, network rules match the panel's HTTP title and TLS certificate, not implant payloads.
4. Multi-Port Desktop RAT Servers
In short
Desktop RAT operators stack many listeners on one rented server. AsyncRAT reaches 22 ports on one Contabo host, and half of PureRAT's candidates sit on ports 56001 to 56003.
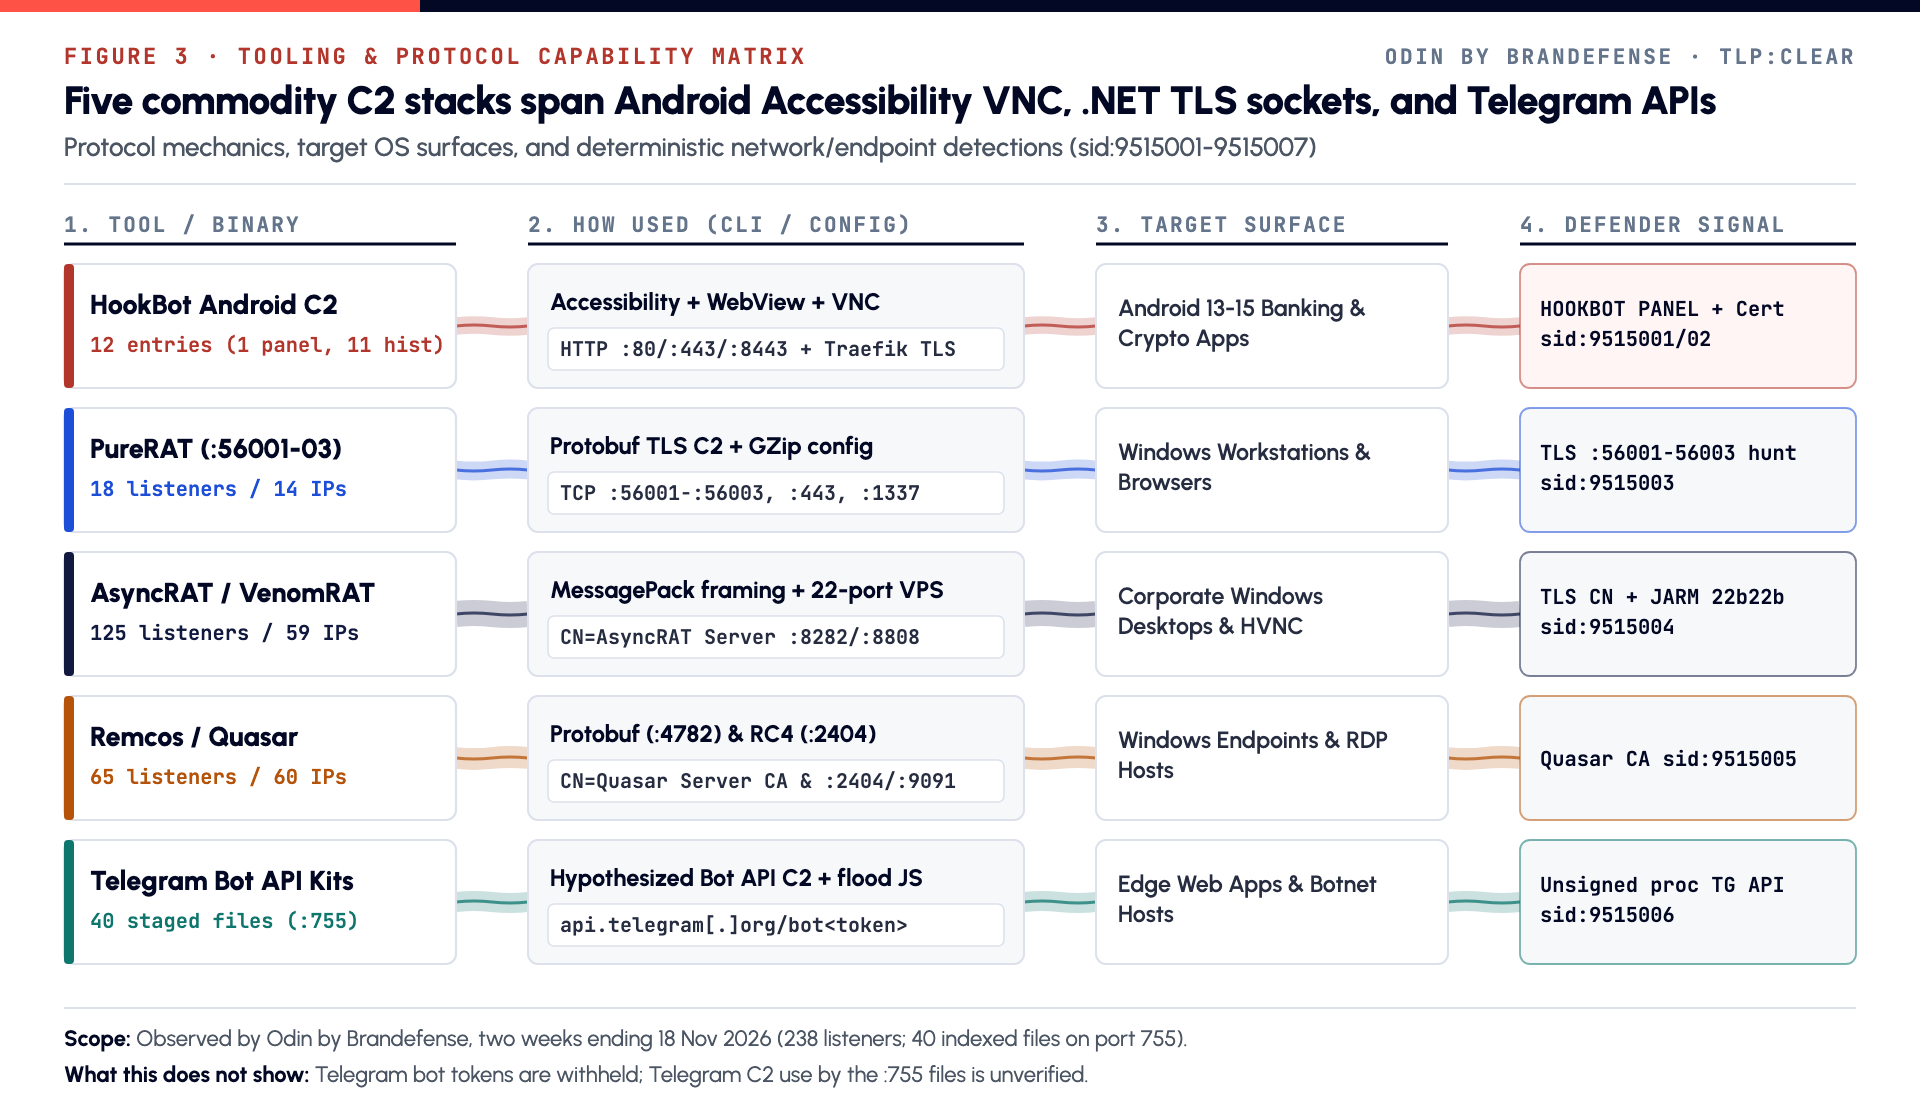
PureRAT on sequential high ports
PureRAT, also tracked as PureHVNC, is a commercial modular .NET RAT. Public analyses document Hidden VNC, a reverse SOCKS5 proxy and credential-stealing plugins. On 17 November 2026 we saw 18 PureRAT candidate listeners on 14 hosts.
Half of them (9 of 18, 50.0%) use a three-port window. Port 56001 has 2 sockets, 56002 has 3 and 56003 has 4. The other nine use 443 (3), 442, 1337, 4443, 6767, 7500 and 7777 (one each).
Four candidate hosts bind two ports each. Their addresses are withheld, as are the custom certificate names.
| Hosting | Country | Ports | What it shows |
|---|---|---|---|
| OVH SAS | SG | 56002, 56003 | Custom domain certificate on both sockets (name withheld), JARM 15d3fd...ccbc0b6b |
| Tier.Net Technologies LLC | US | 56002, 56003 | Sequential pair, no certificate name recorded |
| ReliableSite.Net LLC | US | 56002, 56003 | Sequential pair, no certificate name recorded |
| Antbox Networks Limited | SG | 442, 443 | Adjacent HTTPS-like pair, no certificate name recorded |
Huntress and Cyderes describe three layers in PureRAT builds:
- The .NET loader unpacks its payload with AES decryption and GZip decompression.
- The final configuration is stored as Base64-encoded, GZip-compressed protobuf.
- C2 traffic uses length-prefixed
protobuf-netmessages inside a .NETSslStreamTLS session.
TLS hides the protobuf messages on the wire. So the Suricata rule for ports 56001 to 56003 is a hunt for TLS server handshakes, not a verdict. Pair it with endpoint and YARA hunting for SslStream, protobuf-net and GZipStream loader traits.
AsyncRAT: vertical stacking and horizontal sprawl
AsyncRAT shows two opposite patterns.
Vertical stacking on Contabo.
Contabo hosts 53 of the 121 AsyncRAT listeners (43.8%): 30 on Contabo Inc. and 23 on Contabo GmbH. Three Contabo candidate hosts bind 52 ports between them. Their addresses are withheld.
| Host | Country | Ports | Pattern |
|---|---|---|---|
| Contabo candidate 1 | FR | 22 | 6006 plus 21 ports between 10100 and 30900 |
| Contabo candidate 2 | US | 16 | Ports 80 to 50100 |
| Contabo candidate 3 | US | 14 | Ports 70 to 20700 |
| 102.220.163[.]109 (confirmed) | SI, VPS Dedicated LLC | 11 | 443 with CN=AsyncRAT Server, plus 10 high ports from 2502 to 8808 |
The confirmed host's JARM on port 443 is 22b22b07b22b22b22b22b22b22b22bfd9c9d14e4f4f67f94f0359f8b28f532.
Horizontal sprawl on EGIHosting.
Sixteen candidate hosts in one EGIHosting /24 subnet each run a single AsyncRAT listener. All 16 use TCP 8282 and the generic certificate CN=Server. The subnet is withheld.
Sister families: default certificates, spoofing and cloned templates
The other desktop families reuse default RAT certificates, spoof software brands or clone Windows RDP templates. All seven custom domain certificates seen on candidate or suspected hosts are withheld.
| Family | Host and port | Hosting | What it shows | Action |
|---|---|---|---|---|
| Quasar | 141.98.157[.]101:2288 | GB, EUGAMEHOST LTD | Stock CN=Quasar Server CA, JARM 2ad2ad...3585be, seen twice | Block |
| Quasar | Withheld, port 5000 | CA, Shaw Communications | Stock CN=Quasar Server CA on a cable subscriber ISP | Short watchlist |
| DCRat | 148.113.214[.]176:443 (and 80) | CA, OVH SAS | Wildcard certificate spoofing a download-manager brand (name withheld) | Block |
| DCRat | Withheld, port 3232 | ES, IONOS SE | Default CN=DcRat | Watchlist |
| VenomRAT | 5.161.43[.]175:443 | US, Hetzner | CN=akashicsymbiosis[.]ai, JARM 27d40d... | Block |
| VenomRAT | 154.12.90[.]49:443 | HK, cognetcloud INC | CN=dgtwxj[.]com, JARM 3fd3fd... | Block |
| RedLine Stealer | Withheld, port 5800 | FI, Hetzner Online GmbH | Feed tag and port only; no certificate, JARM or banner | Watchlist |
| RedLine Stealer | Two hosts withheld, port 3389 | NL, RootLayer Web Services | Feed tag plus a shared Windows RDP hostname certificate | Watchlist |
| Remcos | 9 hosts withheld; ports 3389, 2404 (4) and 9091 (5) | US, Interserver, Inc | Port 3389 rows share one Windows RDP hostname certificate | Watchlist |
A shared RDP hostname certificate points to a cloned Windows VPS image, not to RAT software. That is why those RedLine and Remcos rows stay on watchlists.
5. The Port-755 Open Directory
In short
One open HTTP directory on port 755 lists 40 files with Telegram-botnet and flood-tool names. We hashed the files but did not open them, so the host stays on a watchlist.
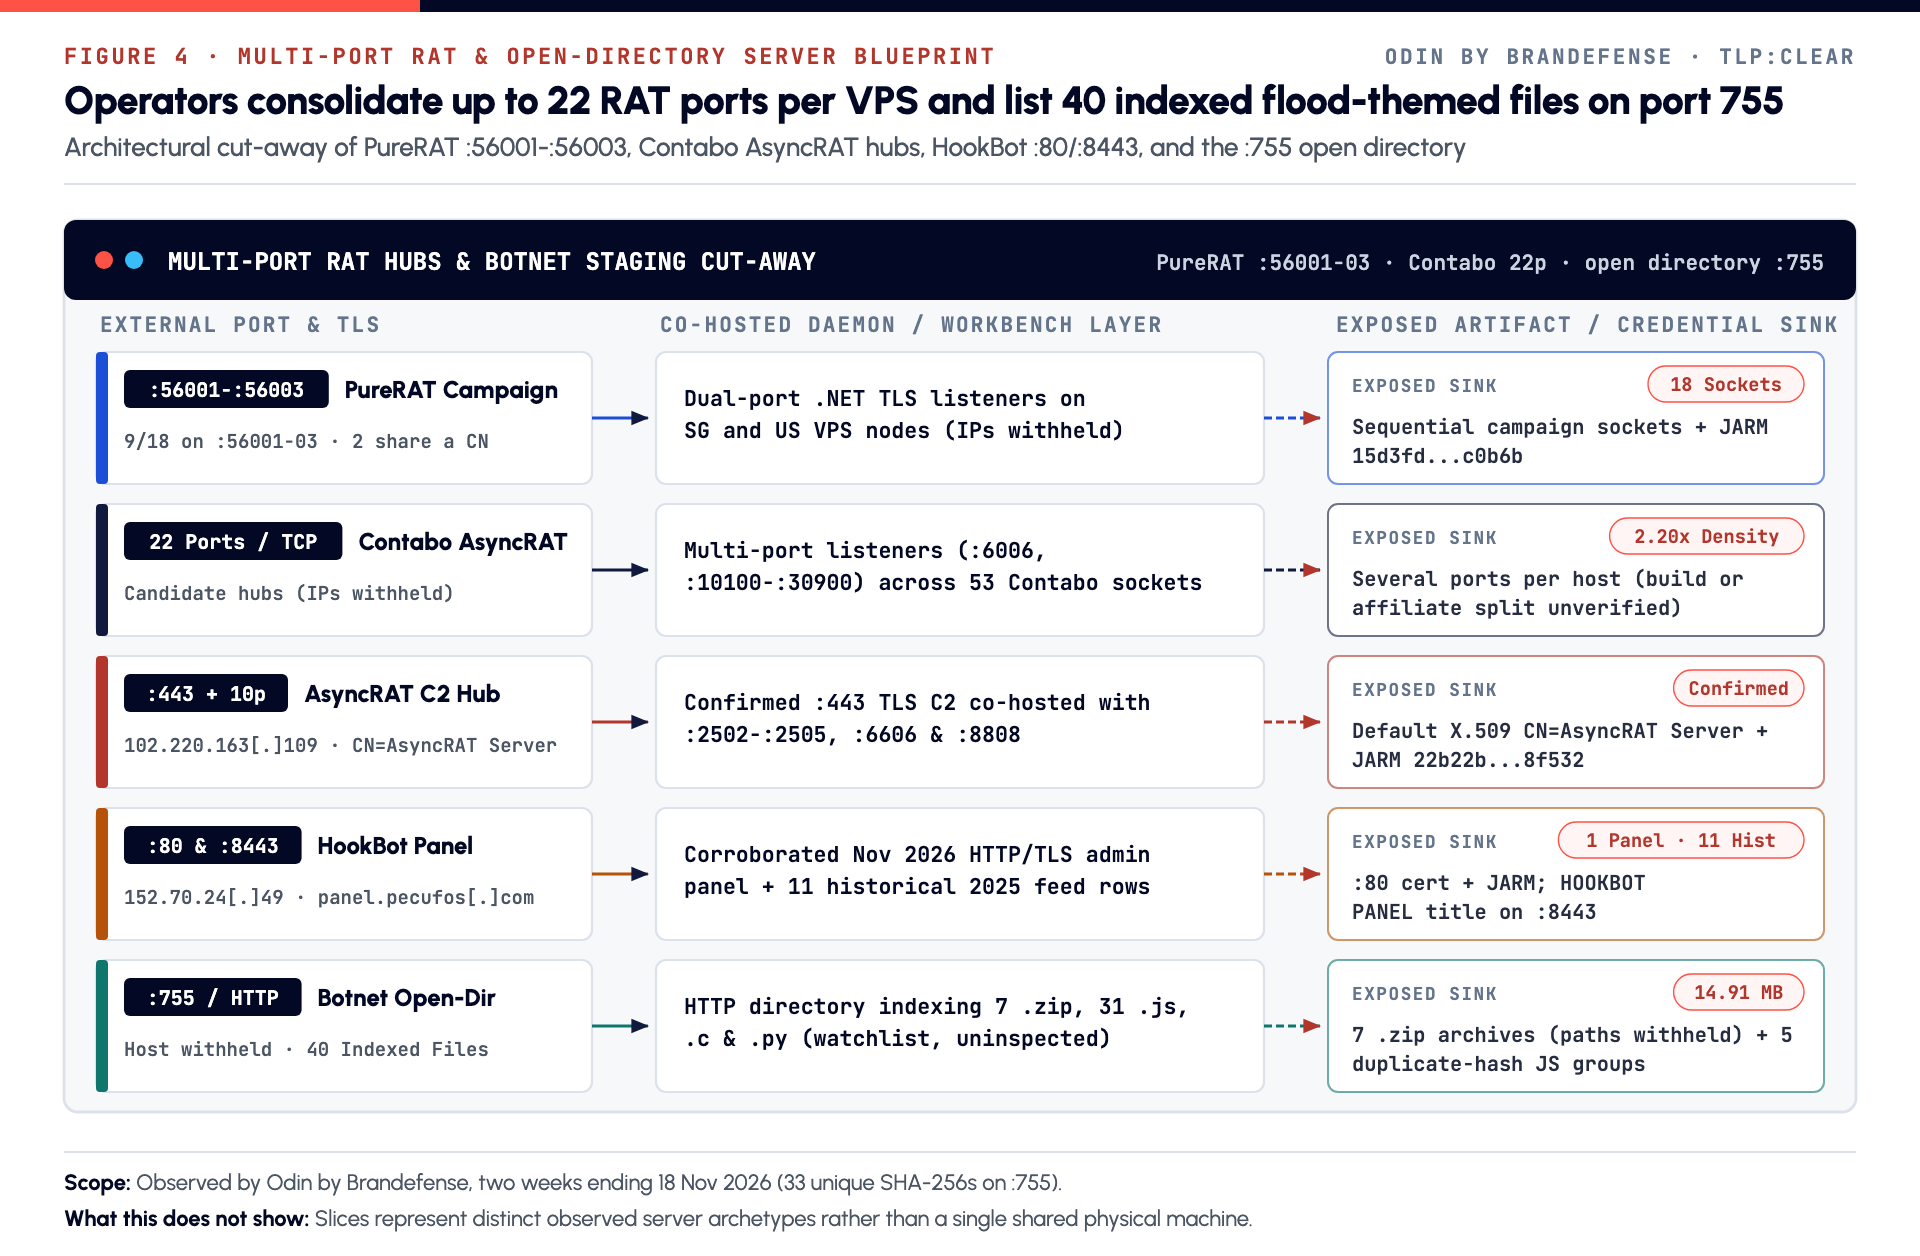
What the directory held
The directory listed 40 files totaling 14.91 MB: 7 .zip archives, 31 .js files, 1 .c file and 1 .py file. Thirty-nine were stored and hashed. One 158,720-byte entry was listed but not stored.
We recorded names, sizes and whole-file SHA-256 hashes. We did not unpack the archives or read the scripts. Hashes alone cannot show whether the server belongs to an attacker, a third-party mirror, a lab or a honeypot. So the host address and all 40 paths are withheld.
| File (described by its name) | Size (bytes) | Note |
|---|---|---|
Telegram DDoS-named archive (.zip) | 616,510 | Not unpacked |
Telegram botnet-named archive (.zip) | 2,198 | Not unpacked |
Bot-counter-named archive (.zip) | 2,533 | Not unpacked |
File-host stresser-named archive (.zip) | 1,091,073 | Not unpacked |
Encoded layer-7 DDoS-named archive (.zip) | 965,898 | Not unpacked; two related archives also present |
Two dstat-named scripts (.js) | 83,968 and 34,816 | Names suggest a flood meter |
Two HTTP flood-named scripts (.js) | 46,080 and 34,816 | Names suggest HTTP flooders |
Flood-named .c and .py sources | 6,011 and 5,256 | Names suggest layer-4 or game-server flooders |
None of the 40 paths contained a literal api.telegram[.]org string.
Hypothesis: Telegram Bot API as C2
Four of the seven archives have bot or Telegram names. The other three have DDoS stresser names. The 31 .js files carry flood and bypass themes.
Public reporting on Telegram-controlled kits describes a two-way pattern (ATT&CK T1102.002, bidirectional communication). A bot polls GET /bot<token>/getUpdates on api.telegram[.]org and returns output with POST /bot<token>/sendMessage. This differs from a dead-drop resolver (T1102.001).
For this directory, Telegram polling, a Node.js runtime and HTTP/2 flood behavior are hypotheses drawn from file names. Defenders should still watch which processes talk to api.telegram[.]org.
Fact: five groups of identical files
Comparing hashes across the 39 stored files shows five groups of byte-identical .js files saved under different names. The groups contain 11 files in total.
| Group | Files | Size (bytes) each | Name pattern |
|---|---|---|---|
| 1 | 2 | 1,363,148 | Base name and a copy with a (100$) price suffix; identical content, hash withheld |
| 2 | 2 | 873,472 | AI-themed labels |
| 3 | 2 | 34,816 | HTTP and HTTP/2 fast-flood labels |
| 4 | 2 | 34,816 | Same script in two directories |
| 5 | 3 | 204,800 | HTTP and HTTPS raw-flood labels |
The identical hashes show duplication under price-tagged and AI-themed names. Whether anyone sold the script, or paid USD 100 for it, is an inference from file names only.
6. What to Block and What to Watch
In short
Internet-wide RAT data mixes real panels with proxy defaults, cloned Windows templates, old feed tags and home broadband addresses. Only six hosts carry enough independent signals to block.
The six hosts to block
Each of these shows a RAT or panel certificate plus a JARM fingerprint, or a panel certificate plus feed-reported panel markers.
| Host | Family | Main signals |
|---|---|---|
| 152.70.24[.]49 | HookBot | CN=panel.pecufos[.]com, JARM 1dd40d...11926e, HOOKBOT PANEL title |
| 102.220.163[.]109 | AsyncRAT | CN=AsyncRAT Server, JARM 22b22b...8f532, 10 more high ports |
| 141.98.157[.]101 | Quasar | CN=Quasar Server CA, JARM 2ad2ad...3585be, seen twice |
| 148.113.214[.]176 | DCRat | Spoofed download-manager wildcard certificate, ports 443 and 80 |
| 5.161.43[.]175 | VenomRAT | CN=akashicsymbiosis[.]ai, JARM 27d40d... |
| 154.12.90[.]49 | VenomRAT | CN=dgtwxj[.]com, JARM 3fd3fd... |
What not to block
| Group | Why it is not a block | Action |
|---|---|---|
| 11 older HookBot entries | First-seen dates from 2025 and no fresh panel marker; addresses may have changed hands | Watchlist until the panel is seen again |
| Port 22 on five HookBot hosts | Ordinary OpenSSH administration on rented Linux VPS | Ignore |
| Uncorroborated feed rows, such as RedLine on port 5800 | Feed tag only | Watchlist |
| RDP-template rows (RedLine and Remcos on 3389) | Shared Windows hostname certificate from a cloned VPS image | Watchlist |
| Several suspected AsyncRAT rows on Alibaba Cloud | A commercial cloud AI gateway certificate on port 443 collides with the pattern | Watchlist |
| Dynamic or cable ISP addresses (Colombia, Canada) | Addresses rotate between customers | Short watchlist |
| Contabo, EGIHosting and PureRAT candidates | Port and JARM only, with no application handshake | Watchlist |
| The port-755 directory | Contents and ownership unverified | Watchlist |
Other explanations we could not rule out
The three populations share no address, certificate or operator link. So evidence from one cannot clear or condemn another. We weighed each one on its own.
- Multi-port RAT candidates. For the five desktop hosts to block, RAT certificates and JARM values support a C2 listener. The 14 to 22 port Contabo hosts, the 16 EGIHosting hosts and the 18 PureRAT sockets lack an application-layer handshake. A researcher honeypot, vendor sinkhole or lab could look the same.
- The port-755 directory. Without content or operator data, it could be a third-party repository, an academic malware mirror or a deception honeypot. Hunt by its file-name themes instead of blocking the host; its file hashes are withheld.
- Older HookBot entries. Their first-seen dates show when they entered the feed, not that panels ran in November 2026. VPS reassignment or harmless reuse of a Traefik proxy stays possible. Five of the 11 show the Traefik default certificate.
Telegram detections need scope
Many DevOps and SOC teams send real webhook alerts to api.telegram[.]org/bot.... Staff may also run the Telegram desktop client from C:Program Files. The KQL and Sigma rules therefore exclude named approved automation hosts and the official client in C:Program Files.
They fire when a script interpreter, or a binary in %APPDATA%, %TEMP% or %PROGRAMDATA%, connects to api.telegram[.]org. The interpreters are powershell.exe, pwsh.exe, wscript.exe, cscript.exe, mshta.exe, curl.exe, node.exe and python.exe. Only the KQL query also covers RegAsm.exe, InstallUtil.exe, MSBuild.exe and /bot command lines.
7. What Defenders Should Do
Within 24 hours
- Block the six hosts in Chapter 6 on perimeter firewalls, mobile VPN gateways, DNS and proxy logs.
- Put the 10 withheld watchlist entries and other candidate hosts on SIEM watchlists that need a certificate, JARM or endpoint signal before action.
- Re-check certificate or banner state before keeping any VPS block past 90 days, since addresses get reassigned.
Within 72 hours
- Enforce Google Play Integrity attestation. Block banking transfers while an untrusted
AccessibilityServiceorMediaProjectionstream is active. Disable APK sideloading on managed Android devices. - Restrict outbound
api.telegram[.]orgtraffic, through proxy or EDR policy, to designated webhook servers and the official Telegram client. - Review any host where a script or a user-writable binary calls
/bot. Isolate it if its owner and purpose cannot be confirmed, or if other malicious behavior appears.
Within 7 to 30 days
- Deploy Suricata SIDs 9515001 to 9515007, keeping 9515003 and 9515007 as hunts.
- Enable Attack Surface Reduction rules and the Sigma rules for
%APPDATA%or%TEMP%loaders that startRegAsm.exe,InstallUtil.exe,MSBuild.exeorvbc.exe, or createschtasks.exetasks. - Turn on HTTP/2 Rapid Reset rate limits, TLS or JA4-based bot challenges and upstream DDoS scrubbing against commodity layer-7 flood tools.
- Hunt for Telegram DDoS, botnet and stresser archive names in EDR file-write data and mail and web gateway archive scanners.
8. Detection Rules
The full rules are in the Detection rules tab. Each file targets a signal that survives a change of IP address.
| Rule file | What it catches |
|---|---|
odin_hookbot_purerat_asyncrat_telegram.rules | Suricata 7: seven signatures for the HookBot panel, PureRAT high-port handshakes, AsyncRAT and Quasar default certificates, and non-browser Telegram Bot API calls |
sentinel_rat_beacons_and_telegram_c2_egress.kql | Microsoft Sentinel and Defender XDR: egress to the six blocked hosts, RAT-port sockets from suspicious processes, unapproved Telegram API calls, and scheduled-task persistence |
sigma_windows_dotnet_rat_and_telegram_bot_c2.yml | Sigma (3 rules): .NET framework utilities started from user-writable folders, unapproved Telegram API connections, and a Linux flood-tool hunt |
odin_hookbot_purerat_and_telegram_botnet_kits.yar | YARA (4 rules): HookBot DEX and panel artifacts, AsyncRAT and VenomRAT stubs, PureRAT loaders, and Telegram botnet kits |
How the Suricata signatures work
| SID | Looks for | Why |
|---|---|---|
| 9515001 | <title>HOOKBOT PANEL</title> in an HTTP response | Catches the HookBot panel page (T1417.002) |
| 9515002 | TLS certificate subject CN=panel.pecufos[.]com from the server | Catches the corroborated panel's certificate |
| 9515003 | Any TLS server certificate from ports 56001 to 56003, once per source every 300 seconds | Hunt for PureRAT sequential ports; pair with endpoint process data (T1219) |
| 9515004 | Certificate subject CN=AsyncRAT Server on any port | Catches the AsyncRAT default certificate |
| 9515005 | Certificate subject CN=Quasar Server CA on any port | Catches the Quasar default certificate |
| 9515006 | Outbound request to api.telegram[.]org with a /bot<token>/sendMessage, sendDocument or getUpdates path and a script user agent | Catches non-browser Telegram C2 calls (T1102.002) |
| 9515007 | Outbound request to api.telegram[.]org/file/bot<token>/ with a script user agent | Hunt for payloads pulled through the Bot API file endpoint |
The script user agents are python-requests, Go-http-client, curl, node-fetch, axios, PowerShell and Mozilla/4.0.
Two limits apply. First, certificate rules 9515002 to 9515005 read the certificate in clear only in TLS 1.2 and earlier. TLS 1.3 encrypts the server certificate (RFC 8446), so TLS 1.3 needs TLS inspection, active JARM checks or endpoint data. Second, 9515006 and 9515007 read HTTPS URIs and need TLS inspection too. Exempt only named webhook gateway addresses from them, never whole workstation subnets.
How the KQL query works
The query looks back 14 days over DeviceNetworkEvents and DeviceProcessEvents and has four branches.
| Branch | Fires when |
|---|---|
| 1. Blocked-host egress | A device connects to one of the six hosts in Chapter 6 |
| 2. RAT-port sockets | A .NET framework binary (RegAsm.exe, InstallUtil.exe, MSBuild.exe, vbc.exe, AppLaunch.exe, cvtres.exe) or a user-writable binary connects to a public IP on a commodity RAT port; ports 56001 to 56003 get their own label |
| 3. Telegram API | An unapproved process calls api.telegram[.]org, judged by interpreter name, .NET binary, user-writable path or a /bot command line |
| 4. Scheduled tasks | schtasks.exe /create points at AppData, ProgramData, wscript or powershell |
The port list holds 17 values, including 2404, 4782, 8282, 8808, 10100 and 56001 to 56003. Watchlist hosts are withheld, so branch 2 finds them by behavior rather than by IP. Fill in your own approved Telegram hosts before use.
These events show a suspicious launch or socket. They do not show in-memory process hollowing; that needs EDR injection data. If developers run portable tools from %LOCALAPPDATA%Programs, add host-plus-path exclusions or check file signatures, rather than excluding the whole folder.
How the Sigma and YARA rules work
| Rule | Fires when |
|---|---|
| Sigma 1 | A binary in %APPDATA%, %TEMP% or %PROGRAMDATA% starts a .NET framework utility, or creates schtasks.exe /create persistence |
| Sigma 2 | A script or user-writable process connects to api.telegram[.]org, outside approved hosts and the official client |
| Sigma 3 (hunt) | A Linux node, python or curl process calls api.telegram[.]org/bot, or runs from /tmp/, /var/tmp/ or /dev/shm/ with HTTP/2 flood and proxy-list arguments |
ODIN_Android_HookBot_Overlay_And_VNC_Dropper | Strings in an extracted Android classes.dex file or captured panel HTML; unpack the .apk first |
ODIN_DotNet_AsyncRAT_VenomRAT_MessagePack_Stub | .NET MessagePack RAT stub strings |
ODIN_DotNet_PureRAT_Sequential_Port_Loader (hunt) | SslStream with ProtoContract or ProtoMember markers, plus GZipStream config code or the 56001 to 56003 port strings |
ODIN_Telegram_BotAPI_DDoS_And_Botnet_Builder_Kit (hunt) | api.telegram[.]org/bot methods with Node.js http2.connect or tls.connect calls |
The YARA kit rule does not cover the uninspected port-755 files.
How to sort a host
The triage logic never blocks on uncorroborated evidence.
| What the host shows | Action |
|---|---|
| Confirmed AsyncRAT, or HookBot with two or more independent panel signals | Block |
| HookBot feed entry with only one panel marker | Analyst review |
| Older HookBot feed entry | Watchlist |
| Multi-port RAT candidate cluster | Watchlist |
| Feed-tagged desktop RAT row with only a port, or only a certificate | Watchlist |
| Suspected RAT on a dynamic ISP | Short watchlist |
| Uninspected open directory | Watch only |
Telegram Bot API call from an unlisted %APPDATA% script, nothing else | Review before isolating |
| The same call plus another malicious behavior | Treat as a Telegram C2 beacon |
| Port-only SSH match | Ignore |
| Approved Telegram webhook server | Allow |
9. Indicators
The Indicators tab holds the 6 published hosts. The 10 watchlist hosts and 12 file hashes are withheld.
| Type | Count |
|---|---|
| Hosts to block (IPv4) | 6 |
| Watchlist hosts (withheld) | 10 |
| Withheld file hashes from the port-755 directory (12 of 33 unique) | 12 |
Supporting fingerprints: the JARM values and certificate subjects named in Chapters 3, 4 and 6.
Hosts to block
| Host | Port | Family | Country, hosting | Key fingerprint |
|---|---|---|---|---|
| 152.70.24[.]49 | 80 | HookBot | DE, Oracle | CN=panel.pecufos[.]com, JARM 1dd40d...11926e |
| 102.220.163[.]109 | 443 | AsyncRAT | SI, VPS Dedicated LLC | CN=AsyncRAT Server, 10 more high ports |
| 141.98.157[.]101 | 2288 | Quasar | GB, EUGAMEHOST | CN=Quasar Server CA, seen twice |
| 154.12.90[.]49 | 443 | VenomRAT | HK, cognetcloud INC | CN=dgtwxj[.]com, JARM 3fd3fd... |
| 148.113.214[.]176 | 443 | DCRat | CA, OVH | Spoofed download-manager certificate, also port 80 |
| 5.161.43[.]175 | 443 | VenomRAT | US, Hetzner | CN=akashicsymbiosis[.]ai, JARM 27d40d... |
Watchlist hosts
The 10 watchlist entries are withheld. They cover five of the 11 older HookBot entries, the RedLine port-5800 feed row, the port-755 directory, a PureRAT dual-port candidate, the 22-port Contabo AsyncRAT hub and a Colombian dynamic ISP host. The two RedLine RDP-template hosts on port 3389 are also watched but are not among the 28 indicators in this chapter (6 hosts, 10 watchlist entries and 12 hashes).
File names for hunting
Twelve of the directory's 33 unique file hashes were selected as hunting indicators, and all 12 are withheld. The files were not opened and the host's owner is not established. Hunt by the file-name themes in Chapter 5 instead: Telegram DDoS and botnet archives, stresser and layer-4 or layer-7 flood scripts, and dstat meters.
Withheld: the 10 watchlist addresses, the two RDP-template hosts, all candidate and suspected addresses, custom certificate names on non-confirmed hosts, the EGIHosting subnet, the port-755 host and its paths, and all Telegram bot tokens.
MITRE ATT&CK mapping
| Tactic | Technique | How it appears | Detection |
|---|---|---|---|
| Credential Access (Mobile) | T1417.002 Input Capture: GUI Input Capture | HookBot WebView overlays and PIN or 2FA capture | SID 9515001, 9515002; HookBot YARA rule |
| Impact / Defense Evasion (Mobile) | T1516 Input Injection | HookBot Accessibility abuse and dispatchGesture replay over VNC | Play Integrity and Accessibility monitoring |
| Command and Control | T1219 Remote Access Tools | AsyncRAT, Quasar, Remcos, PureRAT, DCRat and VenomRAT listeners | SID 9515003 to 9515005; KQL branches 1 and 2 |
| Command and Control | T1095 Non-Application Layer Protocol | MessagePack and protobuf framing over raw TLS sockets | SID 9515003; PureRAT and AsyncRAT YARA rules |
| Command and Control | T1102.002 Web Service: Bidirectional Communication | Telegram Bot API polling and replies, as hypothesized for the kits | SID 9515006, 9515007; KQL branch 3; Sigma 2 and 3 |
10. Scope and Limits
- Window. The findings cover a two-week observation window ending 18 November 2026. Some records carry earlier first-seen dates, as far back as 2023 for a few candidates and 2025 for the older HookBot entries. These are earliest first-seen dates, not a tracking start.
- Panels, not victims. We saw servers, certificates and listings. We saw no victim device, no infection and no financial loss.
- Feed records. The HookBot feed entries, the port 8443 title and the eight fingerprint matches on 152.70.24[.]49 come from feed records. The certificate and JARM on port 80 were observed directly.
- Candidates are leads. Multi-port candidate hosts rest on port and JARM data alone. Do not block them without a second signal.
- The open directory is unread. File names suggest Telegram botnets and flood tools. We did not open the files, and we do not know who runs the server.
- The role model is a model. Nothing links the three populations to each other.
- Rule testing. Every published rule file loads without errors in its engine (Suricata 7.0.12, YARA-X, pySigma and Microsoft's Kusto.Language analyzer, checked on 20 November 2026). The rules were not replayed against live traffic, so test and tune them in your own environment before production use.
11. Sources
- MITRE ATT&CK Mobile. T1417.002 GUI Input Capture and T1516 Input Injection. https://attack.mitre.org/techniques/T1417/002/ (verified 19 November 2026)
- Android Developers.
AccessibilityServicereference. https://developer.android.com/reference/android/accessibilityservice/AccessibilityService (verified 19 November 2026) - MITRE ATT&CK Enterprise. T1219 Remote Access Tools and T1095 Non-Application Layer Protocol. https://attack.mitre.org/techniques/T1219/ (verified 19 November 2026)
- MITRE ATT&CK Enterprise. T1102.002 Web Service: Bidirectional Communication. https://attack.mitre.org/techniques/T1102/002/ (verified 19 November 2026)
- Telegram. Bot API documentation. https://core.telegram.org/bots/api (verified 19 November 2026)
- Salesforce Engineering. Easily identify malicious servers on the internet with JARM. https://engineering.salesforce.com/easily-identify-malicious-servers-on-the-internet-with-jarm-e095edac525a/ (verified 19 November 2026)
- CSIRT KNF. HookBot, a new Android banking trojan. https://cebrf.knf.gov.pl/images/HOOKBOT_CSIRT_KNF_ENG.pdf (verified 19 November 2026)
- Huntress. PureRAT threat actor evolution. https://www.huntress.com/blog/purerat-threat-actor-evolution (verified 19 November 2026)
- Cyderes Howler Cell. Job offer attack chains analysis. https://www.cyderes.com/howler-cell/job-offer-attack-chains-analysis (verified 19 November 2026)
What is…?
Short explanations of the tools and families named in this study.
What is HookBot?
HookBot is an Android banking trojan that uses overlay screens and Accessibility abuse to steal credentials and control the device.
More about HookBotTechniqueWhat is JARM?
JARM is an open TLS server fingerprinting method from Salesforce. It hashes how a server answers a set of crafted TLS handshakes.
More about JARMRemote access trojanWhat is AsyncRAT?
AsyncRAT is an open-source .NET remote access trojan widely used in commodity malware campaigns.
More about AsyncRATRemote access trojanWhat is PureRAT?
PureRAT, also tracked as PureHVNC, is a commercial modular .NET remote access trojan with hidden-desktop control.
More about PureRATRemote access trojanWhat is Quasar?
Quasar is an open-source .NET remote access tool for Windows that criminals and some state actors use as a RAT.
More about QuasarRemote access trojanWhat is VenomRAT?
VenomRAT is a commodity remote access trojan descended from the Quasar and AsyncRAT code bases.
More about VenomRATFrequently asked questions
What did we find?
The data splits into three populations. They share no IP address, certificate or known operator. Of all these hosts, only six are block-ready today. Everything else belongs on a watchlist until it is corroborated.
Why should banks care about HookBot?
HookBot is an Android banking trojan descended from the leaked Ermac and Hook code. Public research by CSIRT KNF shows what it is built to do. It abuses Android Accessibility to read the screen and approve its own permissions. It draws fake login forms over banking apps. It captures PINs and one-time codes. It streams the screen to the attacker over VNC, so the attacker can tap through a transfer inside the victim's own session.
How do RAT operators set up their servers?
Desktop RAT operators rent one cheap server and open many listener ports on it. AsyncRAT averages 2.20 listeners per host across 55 addresses. One Contabo server binds 22 ports. Another hosting network shows the opposite pattern: 16 separate hosts in one subnet, each with a single AsyncRAT listener on port 8282.
What was in the open directory?
The port-755 directory listed 7 ZIP archives, 31 JavaScript files, one C file and one Python file. Their names suggest Telegram-controlled botnets and website flood tools. We recorded names, sizes and hashes, but did not open the files.