


1. Executive Summary
In short
In a two-week observation window ending 18 November 2026, Odin by Brandefense mapped 718 endpoints on 537 hosts running ten team command-and-control (C2) and adversary-emulation frameworks. Only 34 endpoints, on 25 addresses, are confirmed C2: SuperShell, ToShellC2, Metasploit and Meterpreter. Caldera, AdaptixC2 and the rest stay on watchlists, because labs, appliances and mail servers look alike. Block the 18 published confirmed addresses, and pair port alerts with in-memory process signals.
Team C2 frameworks let several operators share one attack server. They bundle reverse shells, payload builders, a task database and a web or desktop console into one Docker stack. This report maps where these consoles run, how each framework works, and which listeners are safe to block.
Browser shell consoles hold all 34 confirmed C2 endpoints.
SuperShell (2), ToShellC2 (10), Metasploit (17) and Meterpreter (5) make up the confirmed set. Viper, a browser front end for Metasploit, sits on top of these. These consoles wrap reverse SSH and Metasploit sessions in shared web terminals.
Plugin teamservers move post-exploitation into memory.
AdaptixC2 runs on 101 endpoints, 35 of them on its default port 4321. It loads listener and agent plugins and runs Beacon Object Files (BOFs) in memory. PyramidC2 uses signed Python interpreters to load offensive packages without writing them to disk.
Emulation planners and look-alikes need watchlists, not blocks.
MITRE Caldera shows 257 endpoints, but 239 are banner look-alikes on a security vendor's address space. The other 18 sit on cloud hosts. Purple teams run the same Caldera agents, so no Caldera address is published.
Three Decisions for Leaders
- Block confirmed shell consoles, watch dual-use tools. Block the 18 published confirmed SuperShell, ToShellC2, Metasploit and Meterpreter addresses, and re-check them after 30 days. Route Caldera, Starkiller and unconfirmed AdaptixC2 listeners to analyst watchlists.
- Join network alerts with memory signals. Connect workstation traffic to teamserver ports (3001, 3232, 4321, 8888, 18081) with memory allocation, unbacked .NET module loads or signed Python network activity within ten minutes.
- Register and lock down your own emulation servers. List every sanctioned Caldera, Viper, Empire and Metasploit host in your SIEM allowlists. Put their consoles behind mutual TLS or a VPN, and turn off directory listing on staging servers.
The Study in Numbers
| Number | What it is |
|---|---|
| 718 / 537 | Endpoints and distinct hosts across ten team C2 and emulation frameworks |
| 34 / 25 | Confirmed C2 endpoints and the addresses they sit on (SuperShell, ToShellC2, Metasploit, Meterpreter) |
| 18 | Confirmed addresses published for blocking; 7 addresses in one German business-ISP cluster are withheld |
| 180 | SuperShell endpoints; 2 confirmed on port 8888, 169 suspected in one Hong Kong cluster |
| 101 / 89 | AdaptixC2 endpoints and hosts; 35 endpoints use default port 4321 |
| 257 / 239 | MITRE Caldera endpoints, and how many of them are vendor banner look-alikes |
| 569 | Entries in an exposed Metasploit installation directory on one unattributed server |
How to use this report.
Security leaders can read Chapter 1, Chapter 6 and Chapter 7. SOC and detection engineers should start with Chapters 7 to 9. CTI analysts will find framework and infrastructure detail in Chapters 2 to 5.
2. Ten Frameworks, Three Workflows
In short
The 718 endpoints fall into three working styles: browser shell consoles, plugin teamservers and automated emulation planners. Grouping them this way shows how a shared team splits shell handling, modular evasion and lateral planning.
Defenders often expect a reverse shell to look like a raw netcat stream. Modern team frameworks look different. They package shell multiplexers, compilers, a task database and role-based web consoles in Docker Compose stacks. Several operators then share the same stack at once. What the targets of these servers experienced is not visible from the server side.
Figure 1 is an analytical model. It groups the frameworks into three workflows that meet at the target's memory. It does not show one actor commanding all three.
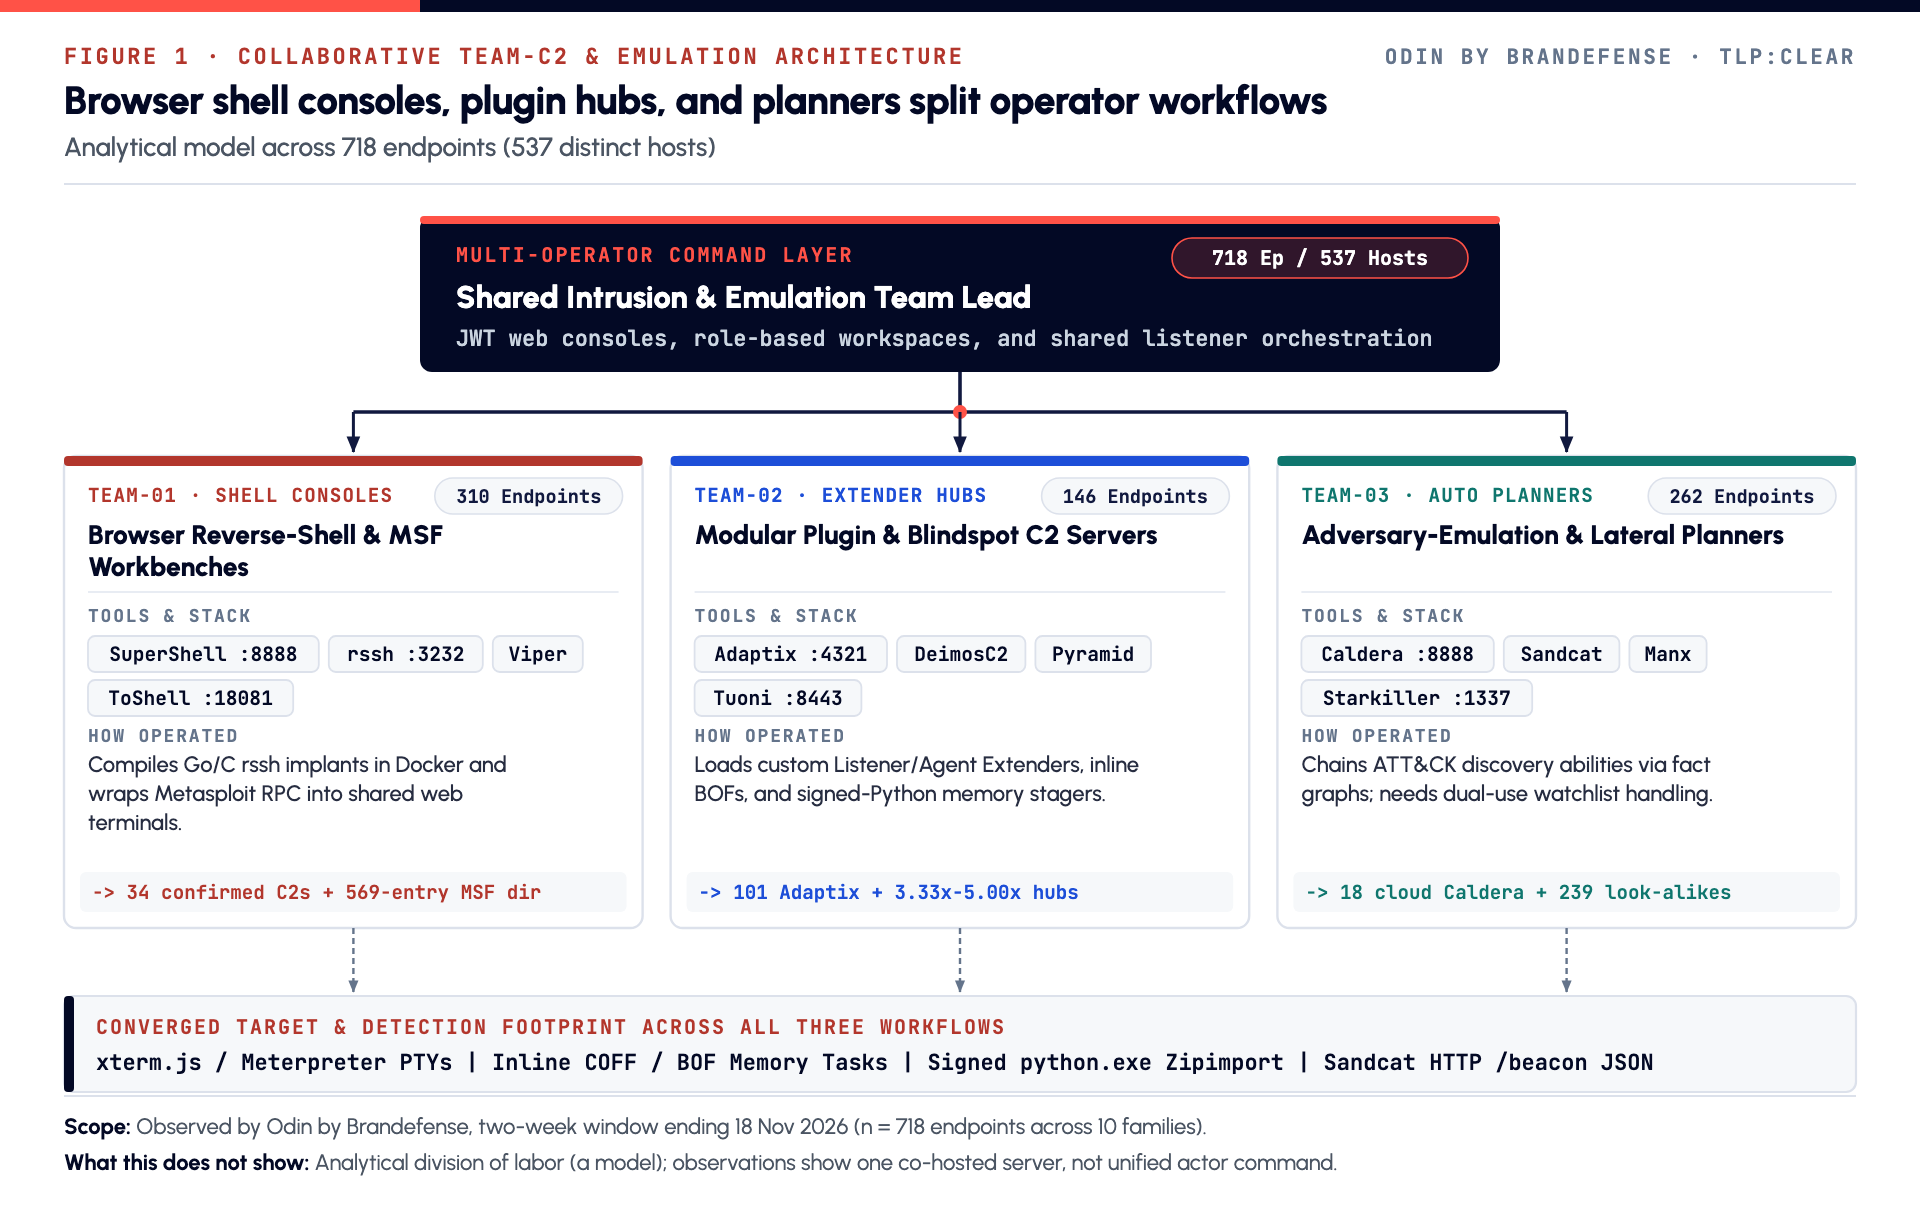
The ten frameworks
Endpoints count each distinct address and port once. Viper has no endpoints of its own, because it drives Metasploit and Meterpreter listeners rather than exposing its own implant protocol.
| Framework | What it is | Endpoints (hosts) | Ports per host | Confirmed |
|---|---|---|---|---|
| MITRE Caldera | Automated emulation planner | 257 (135) | 1.90x | 0 |
| SuperShell | Browser reverse-SSH console | 180 (180) | 1.00x | 2 |
| AdaptixC2 | Plugin-based teamserver | 101 (89) | 1.13x | 0 |
| Metasploit | Exploit and C2 framework | 75 (65) | 1.15x | 17 |
| ToShellC2 | Browser shell controller | 37 (33) | 1.12x | 10 |
| DeimosC2 | Go and Vue team C2 | 30 (6) | 5.00x | 0 |
| Meterpreter | Staged implant handler | 18 (18) | 1.00x | 5 |
| PyramidC2 | Signed-Python in-memory C2 | 10 (3) | 3.33x | 0 |
| TuoniC2 | Containerized plugin C2 | 5 (4) | 1.25x | 0 |
| Starkiller | Multi-operator Empire console | 5 (5) | 1.00x | 0 |
The per-framework host counts add up to 538, not 537. One Alibaba Cloud server in China runs both AdaptixC2 and ToShellC2.
Status across all endpoints
| Status | Endpoints | Share |
|---|---|---|
| Confirmed C2 | 34 | 4.7% |
| Suspected C2 | 541 | 75.3% |
| Candidate | 138 | 19.2% |
| Dynamic consumer ISP, short watchlist | 4 | 0.6% |
| Dual-use emulation tooling | 1 | 0.1% |
Where they run
Browser shell consoles cluster in East and Southeast Asia. SuperShell places 171 of 180 endpoints (95.0%) in Hong Kong and 6 in China. ToShellC2 places 26 of 37 (70.3%) in China (14) and Hong Kong (12).
AdaptixC2 and Metasploit spread across Western and Asian VPS providers alike.
| Framework | Top countries (endpoints) |
|---|---|
| AdaptixC2 | US 19, HK 15, CN 13, SG 10, RU 7, DE 5 |
| Metasploit | DE 19, HK 11, MA 8, SG 7, FR 5, US 5, AU 5 |
3. Browser Shell Consoles and Metasploit Workbenches
In short
Browser shell platforms account for all 34 confirmed C2 endpoints. They wrap reverse-SSH tunnels and Metasploit RPC sessions in shared web dashboards, so one server serves a whole team.
Browser consoles remove manual listener work. A single Docker command brings up a web terminal (xterm.js), payload cross-compilers, SOCKS5 pivots and a file browser. Operators log in through a JWT-protected portal and share live shells with each other.
Figure 2 maps each framework from server port to implant behaviour, target surface and the matching detection rule.
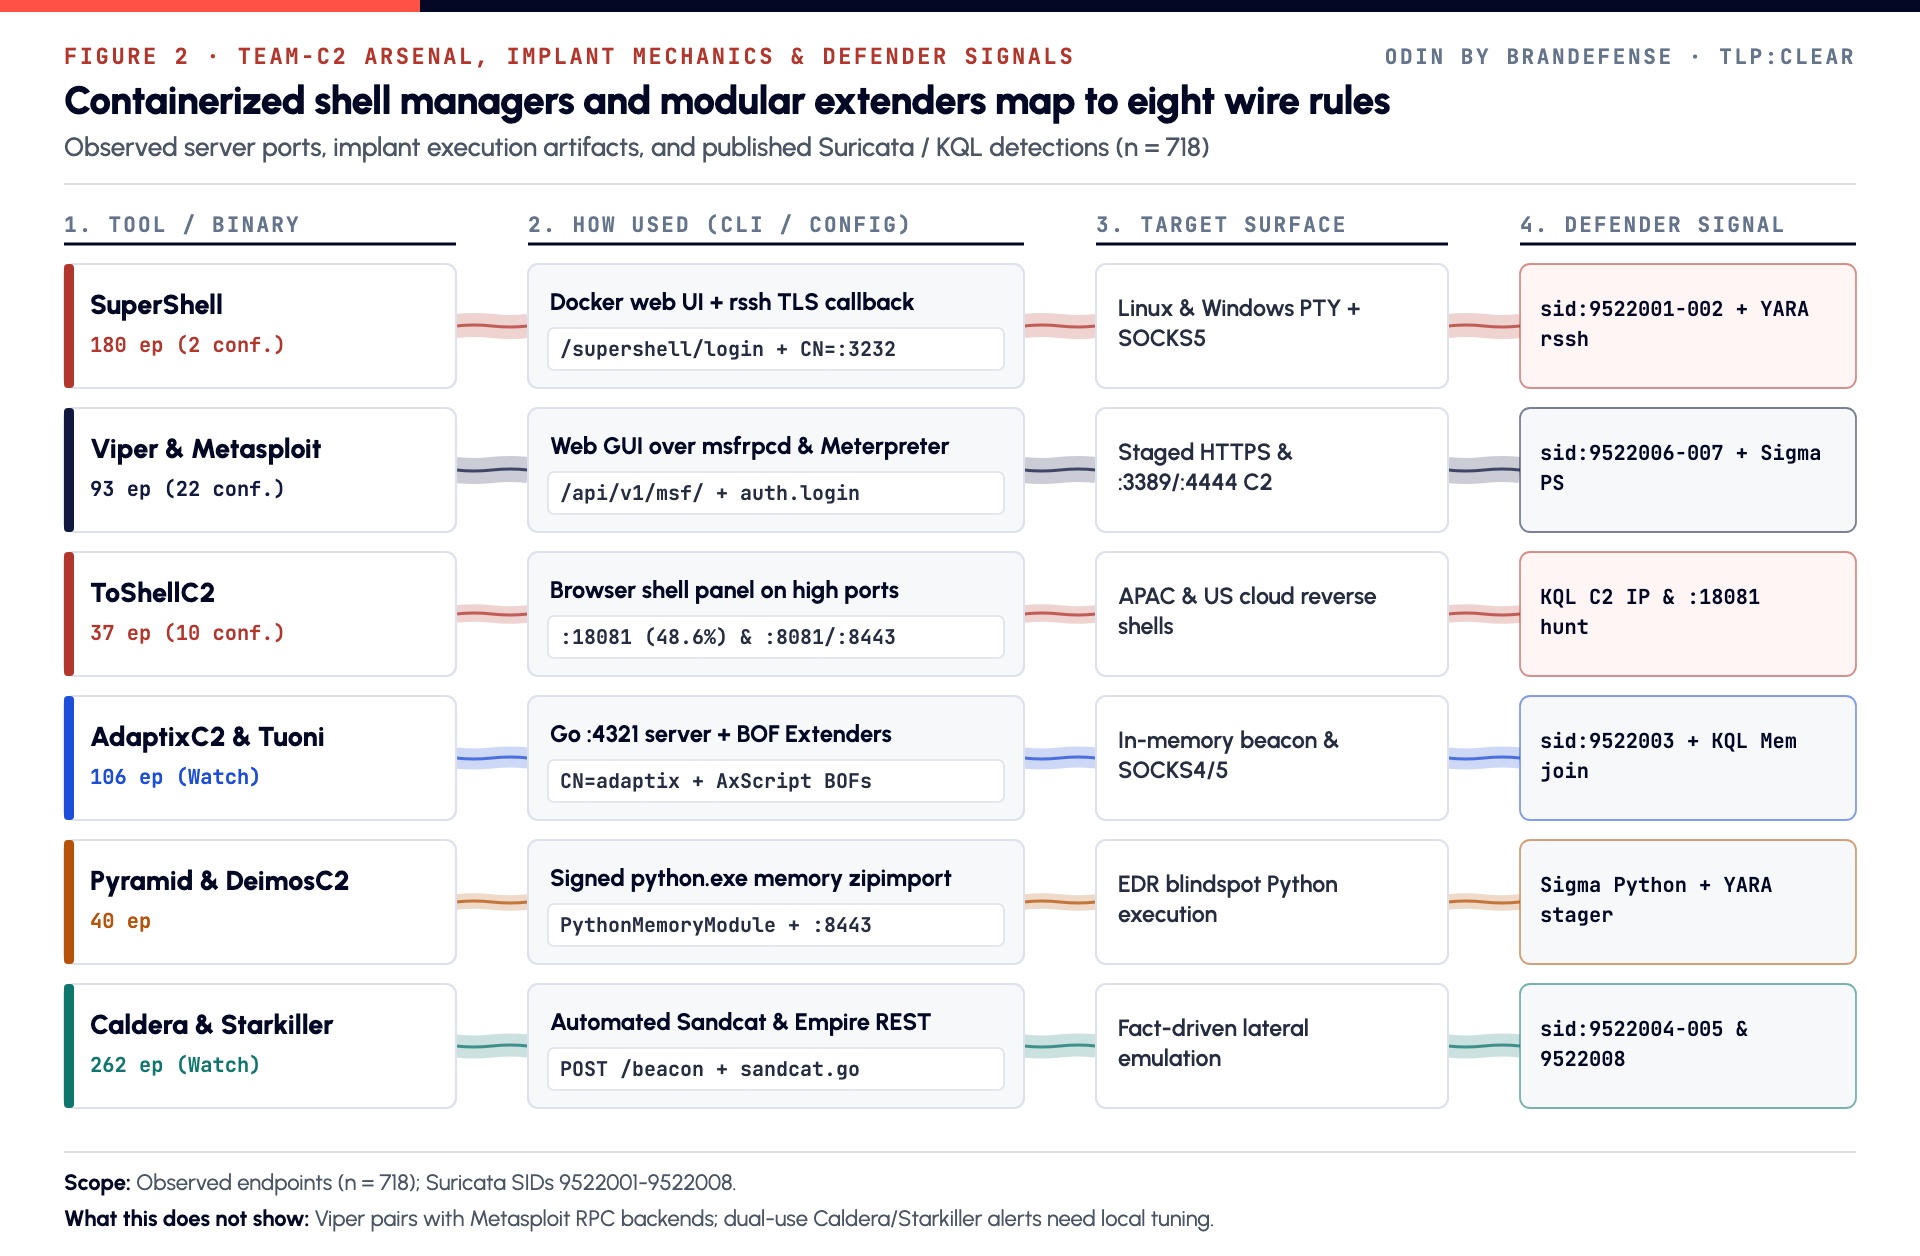
SuperShell and its embedded rssh listener
SuperShell (tdragon6/supershell) bundles a Flask and Nginx management portal with a reverse SSH (rssh) multiplexer.
| Component | Default | Detail |
|---|---|---|
| Web portal | Port 8888 | JWT login under /supershell/login |
rssh listener | Port 3232 | TLS-wrapped SSH with a self-signed certificate CN=:3232 |
| Implant builder | In the browser | Statically linked Go or C implants for Windows and Linux |
The implant dials out over TLS-wrapped SSH. The operator gets a browser terminal, file transfer, SOCKS5 tunnelling and shellcode injection. No inbound port needs to be open on the target.
The 180 SuperShell endpoints fall into three groups.
| Group | Endpoints | Ports and TLS | Hosting | Status |
|---|---|---|---|---|
| Confirmed consoles | 2 | 8888 | Shenzhen Tencent (CN), Cloudie Limited (HK) | Block |
| Hong Kong 443 cluster | 169 | 443, JARM prefixes 21d14d.. and 3fd3fd.. | LUOGELANG (FRANCE) LIMITED (HK) | Suspected, watchlist |
| Other candidates | 8 candidate + 1 suspected | 8888 (7), 18888 (1), 8443 (1); CN=:3232 on 2 | Alibaba, Tencent, Huawei, Cloudie | Watchlist |
The two confirmed consoles are 111.229.193[.]40:8888 and 103.115.57[.]95:8888.
Two candidate consoles in China present SuperShell's default rssh certificate CN=:3232. They share JARM 3fd3fd20d3fd3fd00043d3fd3fd43d5ecfbe778b06e32b538bd51f24eb7398. A third candidate uses a Chinese-language certificate name meaning "inventory management system". Their addresses are withheld.
ToShellC2
ToShellC2 is a lightweight web reverse-shell panel. It shows 37 endpoints on 33 hosts. Port 18081 carries 18 candidates (48.6%), and port 8081 carries 4 confirmed endpoints.
Ten ToShellC2 endpoints on 8 addresses are confirmed. Two of these servers listen on two ports each.
| Endpoint | Hosting | Note |
|---|---|---|
| 186.244.231[.]115:80 and :8080 | CLOUDVALLEY SDN. BHD. (US) | Dual-port controller |
| 185.207.154[.]238:8081 and :8443 | Cloudie Limited (HK) | Dual-port, third-party certificate subject withheld |
| 186.244.215[.]55:443 | Uscloud Inc (US) | CN=fileserver |
The full list of confirmed ToShellC2 addresses is in Chapter 9.
Viper, Metasploit and Meterpreter
Viper (FunnyWolf/Viper) puts a React and Ant Design multi-operator interface and an ATT&CK module runner on top of Metasploit. It talks to the Metasploit RPC daemon msfrpcd, which accepts auth.login calls over MessagePack.
Across 75 Metasploit endpoints (65 hosts) and 18 Meterpreter endpoints (18 hosts), 22 are confirmed C2. They form three groups.
| Group | Confirmed endpoints | Addresses | Detail |
|---|---|---|---|
| German dual-port cluster on a business ISP | 14 (7 addresses) | Withheld | Each binds Metasploit listeners on 443 and 80 and shares one third-party company certificate |
| Metasploit team listeners on 3001 | 3 | 77.83.36[.]163 (Layer7 Networks, SC), 185.254.199[.]160 (SOLLUTIUM EU, NL), 77.91.71[.]99 (hosting network, IL) | Standalone 3001 listeners |
| Meterpreter handlers | 5 | See table below | Includes one handler on the RDP port |
| Meterpreter handler | Hosting | Note |
|---|---|---|
| 65.38.121[.]42:3389 | BL Networks (RO) | TLS Meterpreter on the RDP port, CN=6a47718162def1c |
| 181.215.18[.]135:8443 | Datacamp (HK) | Reverse-HTTPS handler |
| 190.2.184[.]47:4444 | MASTER DA WEB (BR) | Default Meterpreter port |
| 8.148.31[.]135:4446 | Alibaba Cloud (CN) | Non-default TCP port |
| 154.89.152[.]104:10003 | CLOUDVALLEY (HK) | High-port handler |
Binding Meterpreter to 3389 makes the traffic look like Remote Desktop at a glance. Four more suspected Meterpreter hosts on Tencent Cloud port 443 share the default cloud image certificate CN=VM-0-4-centos. They stay on the watchlist.
4. Plugin Teamservers and Emulation Planners
In short
AdaptixC2, DeimosC2, PyramidC2 and TuoniC2 (146 endpoints) favour loadable plugins, in-memory BOFs and signed-Python loaders. Caldera and Starkiller (262 endpoints) automate ATT&CK-style lateral planning. All 408 stay on watchlists.
Plugin teamservers separate the core server from its transport and implant modules. An operator can swap HTTP, SMB, DNS or TCP listeners without rebuilding the backend. This also makes static signatures age quickly.
Figure 3 is a synthesized model built from the public documentation of each tool. It shows six protocol and memory steps and the defender signal for each. No single intrusion log links all six steps.
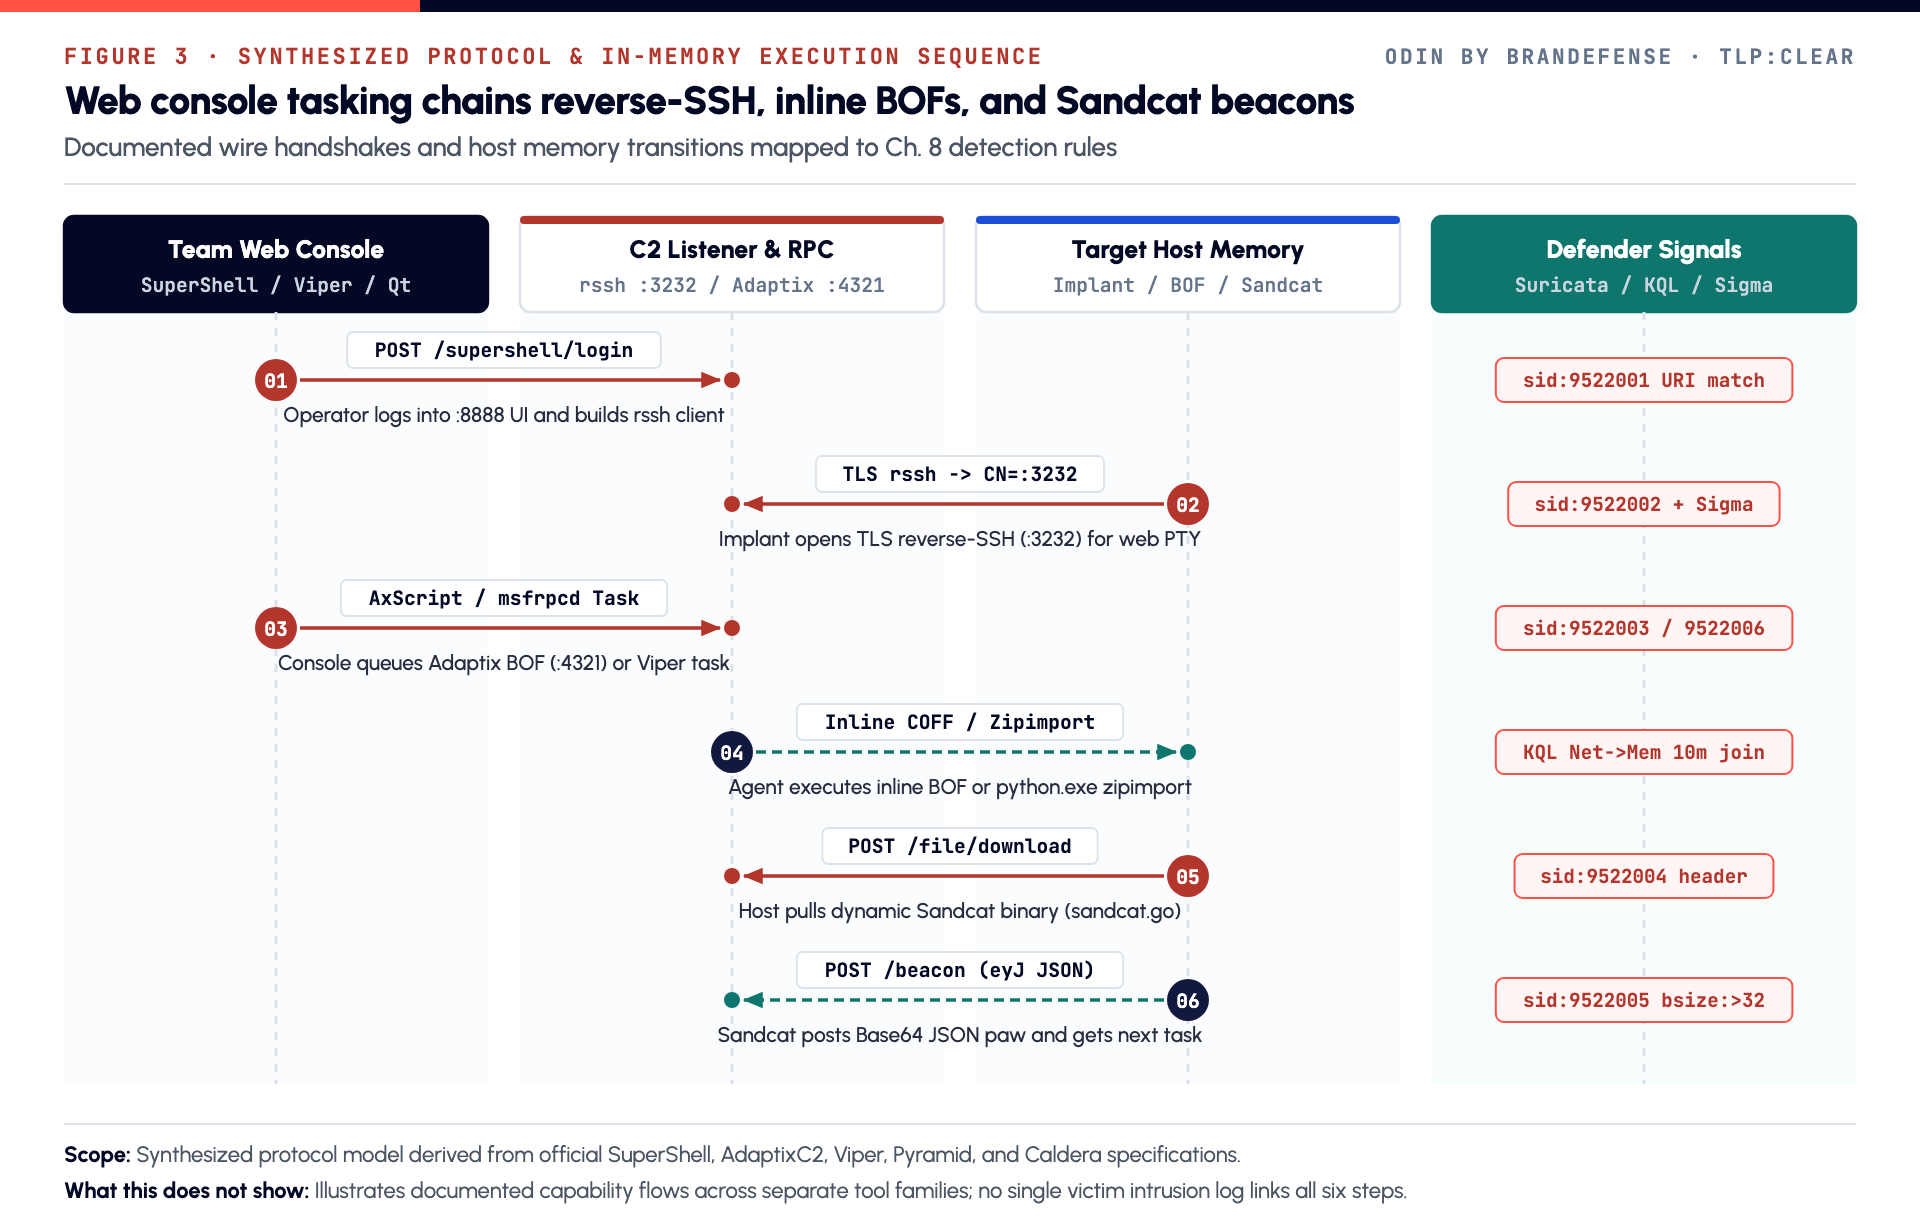
AdaptixC2
AdaptixC2 pairs a Go teamserver with a C++ and Qt operator client. It loads protocols and implants as "Extenders" (ExtenderListener and ExtenderAgent), scripted in AxScript. Operators can run BOFs inline (execute bof) and pivot through SOCKS4 or SOCKS5.
The 101 AdaptixC2 endpoints on 89 hosts break down as 32 suspected, 68 candidates and 1 node on a dynamic Chinanet line. None is confirmed.
| Signal | Endpoints |
|---|---|
| Default port 4321 | 35 (34.7%) |
| Port 443 / 4444 / 8443 / 4443 / 43211 | 7 / 6 / 4 / 3 / 3 |
Go TLS JARM 29d29d00000000000043d43d00043dc3b2afa8a5ec09b510a8559aff7899fb | 21 |
CN=localhost | 11 |
CN=adaptix / CN=adaptix.local / CN=adaptix-server | 4 / 2 / 1 |
Spoofed CN=AnyDesk Client (US) | 1 |
Default certificates give many deployments away. Some servers also bind several ports: one host in India uses 4444, 4445 and 50003, and one in Switzerland uses 4322 and 4323. A DigitalOcean host in Singapore pairs the 4321 management port with a 4444 beacon port. These addresses are withheld.
PyramidC2, TuoniC2 and DeimosC2
| Framework | Endpoints (hosts) | How it works | What we saw |
|---|---|---|---|
| PyramidC2 | 10 (3), 3.33x | Uses signed python.exe or pythonw.exe to fetch and import offensive packages (such as BloodHound and secretsdump) in memory through zipimport and PythonMemoryModule, with no .pyd DLL on disk | An Akamai US listener on 8080; a three-port host on a German consumer ISP; a six-port OVH host in France whose other five ports are mail ports |
| TuoniC2 | 5 (4), 1.25x | Dockerized red-team suite with plugins | All 4 TLS instances on 8443 (RU, DE, TR) share CN=localhost and JARM 07d3fd16d21d21d00042d43d00041ddb04deffa1705e2edc44cae1ed24a4da; the Russian host also exposes 12702 |
| DeimosC2 | 30 (6), 5.00x | Go and Vue team C2 | 1 German candidate on 8443; the other 29 are mail and FTP ports on 5 OVH hosts in Canada and Chile (see Chapter 6) |
PyramidC2 is built to work inside endpoint detection blind spots. A signed Python interpreter is often trusted, so the loaded code inherits that trust.
MITRE Caldera and Starkiller
MITRE Caldera automates post-compromise decisions. It pairs a Go HTTP agent, Sandcat (also written 54ndc47), and a TCP reverse-shell agent, Manx, with planners driven by collected facts.
- The target sends
POST /file/downloadwith the headerfile: sandcat.go. - The server compiles a fresh Go binary that embeds the
serverandgroupvalues, so the agent's command line can stay clean. - The agent then exchanges Base64-encoded JSON (starting with
eyJ) overPOST /beaconand receives its next task.
Caldera shows 257 endpoints on 135 hosts. Chapter 6 explains why 239 of them are look-alikes.
Five Starkiller nodes run multi-user consoles for PowerShell Empire (MITRE S0363), which logs operators in through /api/v2/users/login. Two use the Empire REST port 1337 (US and FI). Three use port 80 on OVH in France.
5. Container Stacks and an Exposed Metasploit Directory
In short
Port layouts and one open directory show how team C2 backends are packaged on cloud servers. An unattributed server in India exposed the full internal Metasploit installation tree.
A port banner shows which listener answers. A directory tree or a multi-port layout shows how the server was built. Figure 4 is a composite view across separate servers. It combines the SuperShell, rssh, AdaptixC2 and Caldera layers with the exposed Metasploit tree.
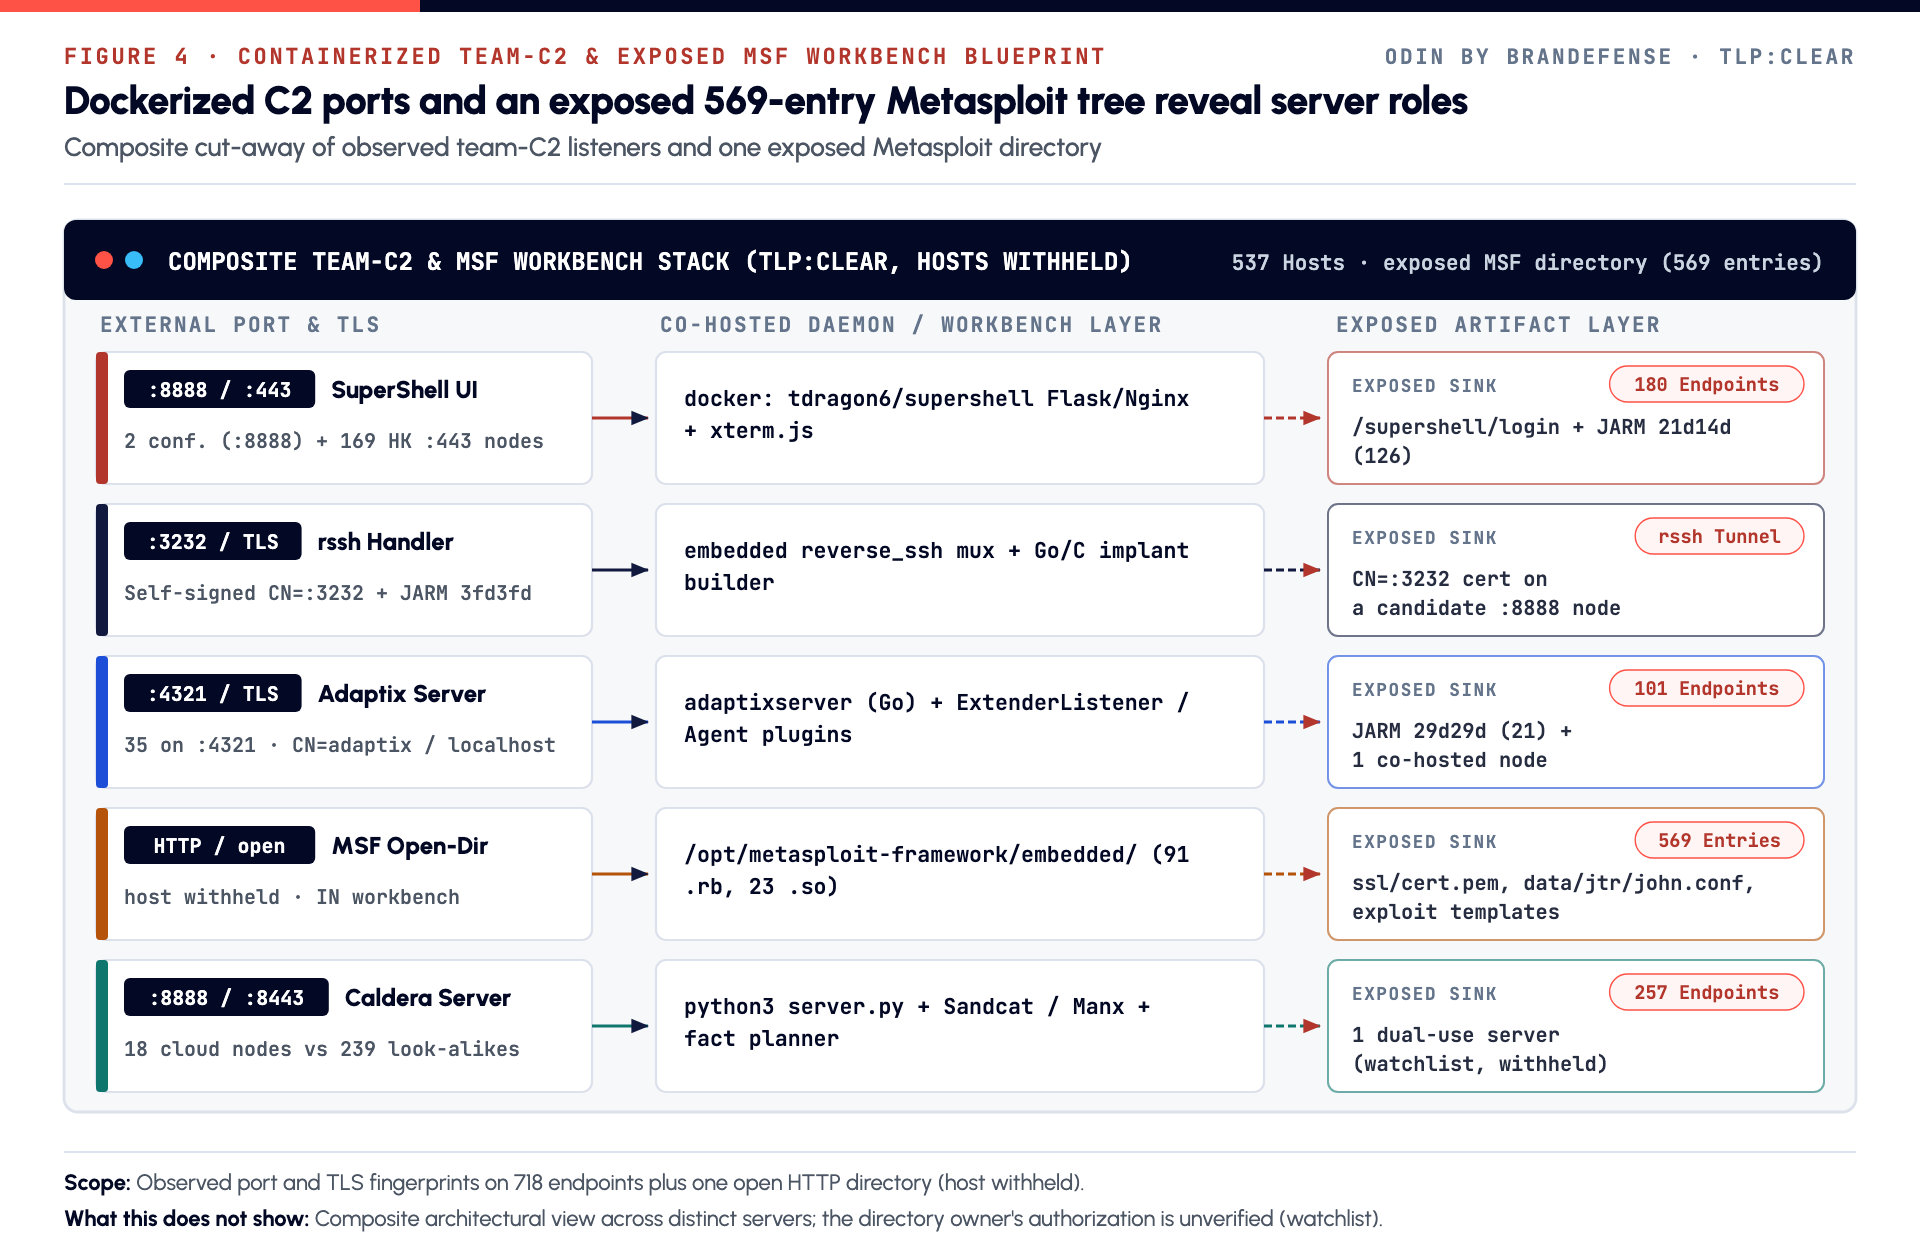
The exposed Metasploit installation
A server on an Indian hosting network ran an unauthenticated HTTP directory listing on a non-standard port. It exposed the internal Omnibus installation directory of the Rapid7 Metasploit Framework, /opt/metasploit-framework/embedded/. The listing reports 58 directory sites holding 7,064 files. This report describes 569 of those entries. The table shows the largest file types among them; smaller groups are not broken out.
An exposed framework installation could belong to an unhardened security lab, a scanner or an attack staging server. The owner's authorization is unknown, so the address, port and file hashes are withheld.
| File type | Entries | Share | What it is |
|---|---|---|---|
| No extension (ELF binaries) | 237 | 41.7% | Embedded PostgreSQL and terminal tools, such as bin/pg_restore, bin/pgbench, bin/pg_waldump and bin/tic |
.rb | 91 | 16.0% | Ruby framework libraries, exploit support code and msfrpcd runtime modules |
.so and versioned libraries | 43 | 7.6% | 23 .so files plus 20 versioned links, such as plpgsql.so, liblzma.so and libncurses.so |
.txt, .md, .rdoc | 38 | 6.7% | Framework documentation (20, 12 and 6) |
.h and .a | 35 | 6.2% | OpenSSL and ncurses headers, plus 10 static libraries such as lib/libpgtypes.a |
.pem, .conf and exploit data | 15+ | 2.6%+ | TLS root bundles, John the Ripper rule files and exploit templates |
The tree tells defenders three things.
- A database-backed install. Files such as
pg_restore,pg_receivewalandlib/postgresql/plpgsql.sobelong to a full Metasploit workspace. Such a workspace can hold shared host tables, captured credentials and Viper session state. - Cracking rules next to exploits. The John the Ripper rule files
john.conf(117,142 bytes) anddumb32.conf(100,781 bytes) sit beside the framework's exploit templates. - A common exposure mistake. The most likely explanation is a quick Python HTTP server started from a parent directory during a file transfer. That publishes the whole framework tree by accident.
Co-hosting and multi-port layouts
Across all 718 endpoints, one server runs two different frameworks. It sits on Hangzhou Alibaba Advertising (CN) and binds AdaptixC2 on 60001 beside ToShellC2 on 18081. Its address is withheld.
Another 14 servers run one framework on several ports, not counting vendor and mail look-alikes.
| Layout | Servers | Detail |
|---|---|---|
| Confirmed dual-port Metasploit | 7 | The German business-ISP cluster, each with 443 and 80 (withheld) |
| Confirmed dual-port ToShellC2 | 2 | 186.244.231[.]115 (80 and 8080) and 185.207.154[.]238 (8081 and 8443) |
| Candidate ToShellC2 | 1 | Singapore host on 80, 8080 and 28443 (withheld) |
| AdaptixC2 and TuoniC2 teamservers | 4 | India (4444, 4445, 50003), Switzerland (4322, 4323), Singapore DigitalOcean (4321 with 4444), Russia TuoniC2 (8443 web admin with 12702 implant delivery); all withheld |
6. Look-Alikes: What Not to Block
In short
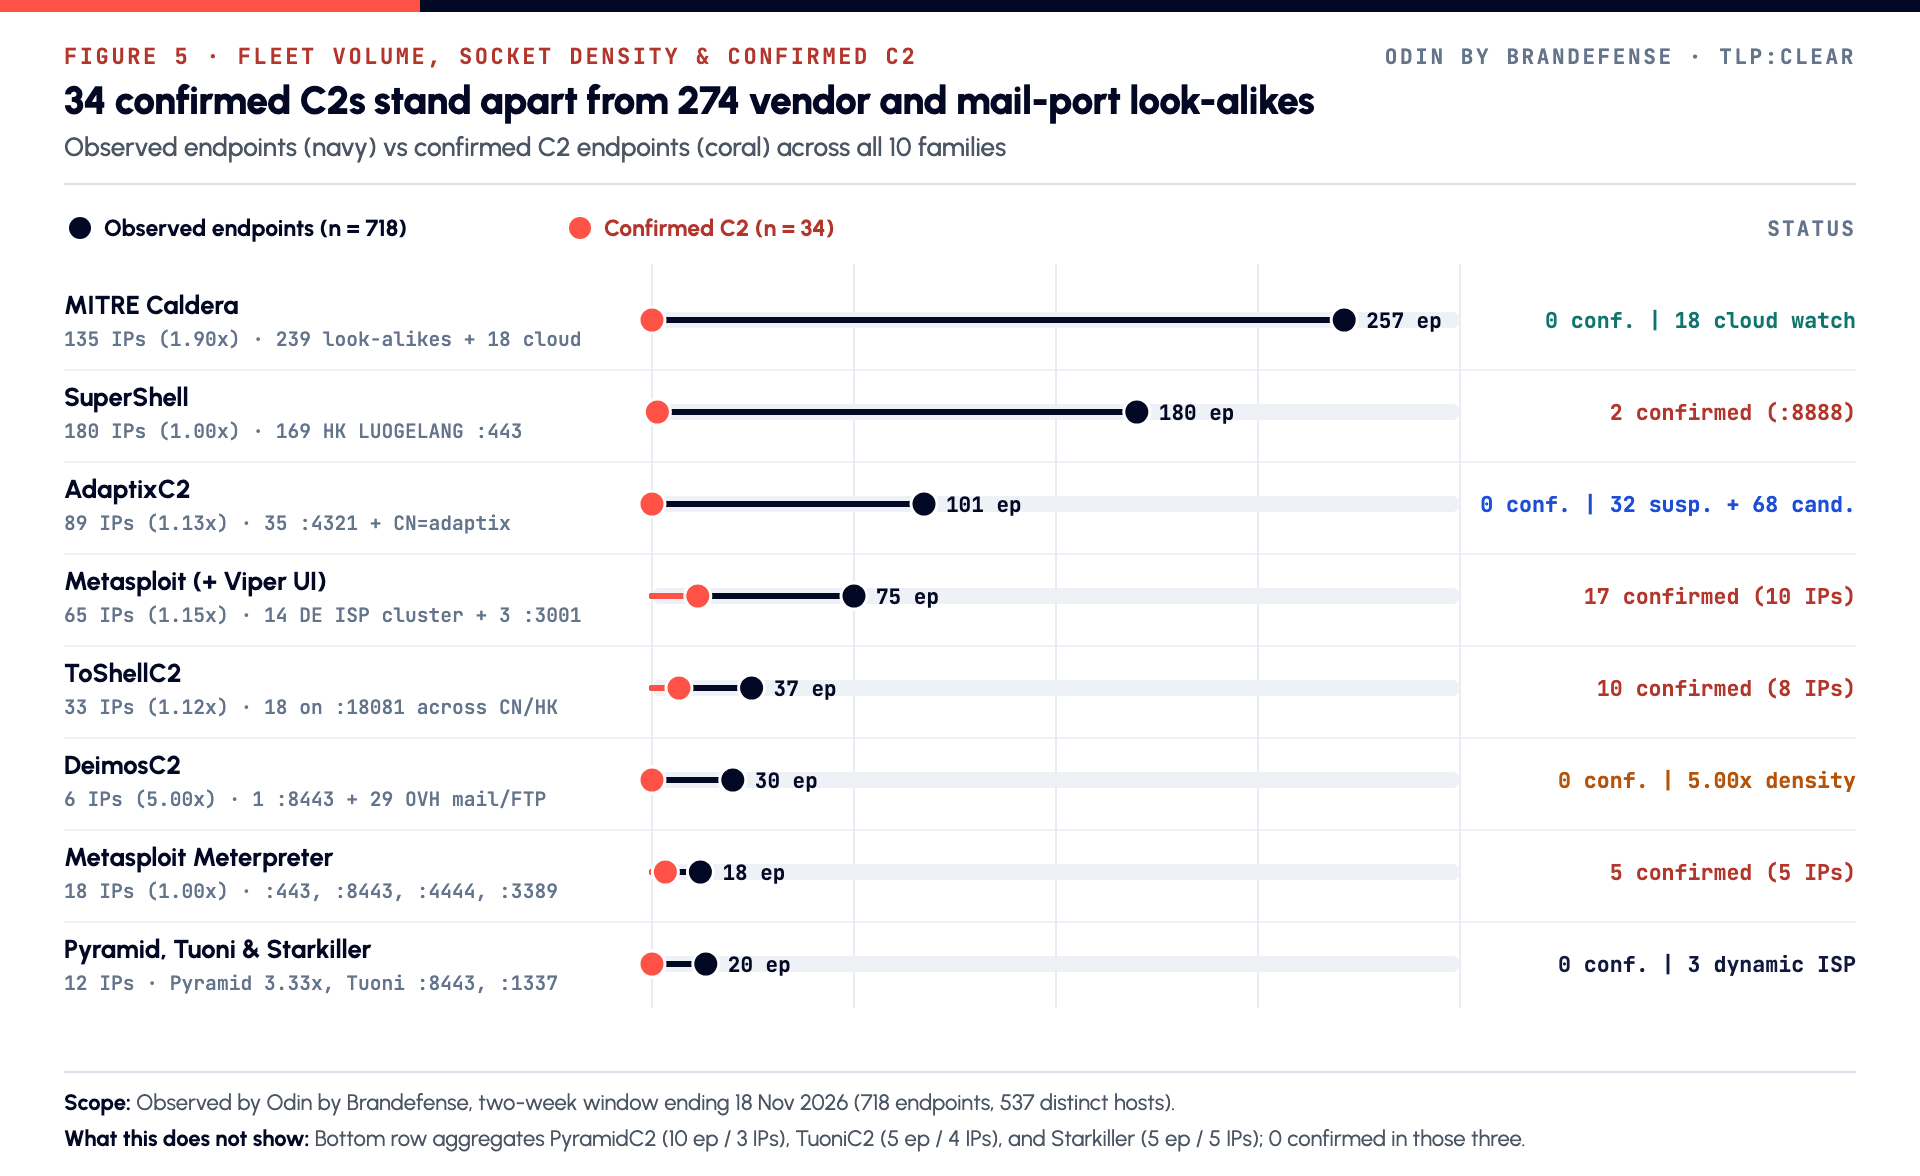
Raw C2 lists mix real listeners with security appliances, mail servers, scanner consoles and sanctioned purple-team labs. Only 34 of 718 endpoints are confirmed; the other 684 (95.3%) belong on watchlists.
Feeding raw Caldera, DeimosC2 or Metasploit lists into an automatic firewall block creates real business risk. Figure 5 compares each framework's endpoint count with its confirmed count.
Six sources of false positives
| Source | Endpoints | Why it is not a C2 | What to do |
|---|---|---|---|
| Security-vendor banner look-alikes in the Caldera list | 239 | Upstream HTTP and TLS fingerprints collide with the vendor's own cloud and appliance services | Do not block |
| Sanctioned purple-team Caldera and Starkiller servers | 18 cloud Caldera + 5 Starkiller | Purple teams and attack-simulation vendors run the same unmodified Sandcat and Empire servers | Watchlist |
| Mail and FTP ports | 35 | Standard mail and FTP services match Go and OpenSSL JARM patterns | Do not block |
| Vulnerability-management and Metasploit Pro consoles | 1 + 19 on port 3790 | A scanner console certificate, or the Metasploit Pro admin interface, is not a hostile handler | Watchlist unless paired with stager delivery |
| One-provider SuperShell cluster | 169 | Shared JARMs on one Hong Kong network, with nothing beyond port and JARM tying them to SuperShell | Watchlist |
| Dynamic consumer ISP lines | 4 | Addresses rotate between unrelated customers | 24-hour watchlist |
Vendor look-alikes. The 239 Caldera look-alikes sit on 117 US hosts in Fortinet corporate address space, which is a fingerprint collision and not Caldera activity. Their ports are 443 (117), 80 (114), 16018 (5) and 8080 (3). One certificate subject repeats on 236 of them.
The 18 cloud Caldera servers.
Removing the look-alikes leaves 18 Caldera endpoints on 18 hosts: 13 on AWS, 2 on DigitalOcean, 2 on Alibaba and 1 on TT DOTCOM. Fourteen use the default port 8888, and one uses 8443. One DigitalOcean server in Germany matches the Caldera protocol and is held as dual-use tooling.
Mail and FTP ports.
The 35 rows split as 29 DeimosC2 rows on 5 OVH hosts in Canada and Chile, 5 PyramidC2 rows on one OVH host in France, and 1 Caldera row on Alibaba. The ports are 21, 110, 143, 465, 587, 993 and 995. Removing them leaves the DeimosC2 candidate on 8443 and the five PyramidC2 web listeners on four ports: 443 (two hosts), 8080, 61380 and 80.
Dynamic ISP lines. The four rows are 1 AdaptixC2 node on Chinanet, 2 PyramidC2 rows on Deutsche Telekom and 1 TuoniC2 node on Turk Telekom. Their addresses are withheld.
7. What Defenders Should Do
Within 24 hours
- Block traffic to the 18 published confirmed addresses in Chapter 9. Re-check each one after 30 days, since cloud addresses get reassigned.
- Send any match on the German business-ISP Metasploit cluster pattern (dual 443 and 80 listeners behind one company certificate) to analyst review, not the block list.
- Keep Caldera, Starkiller, AdaptixC2, DeimosC2, PyramidC2 and TuoniC2 listeners on watchlists, not block lists.
- Put dynamic consumer ISP addresses on a 24-hour watchlist.
Within 72 hours
- Deploy the eight Suricata signatures behind TLS inspection and at perimeter TLS monitoring points. Add
passrules for your documented purple-team addresses first. - Schedule the Sentinel query and the three Sigma rules to catch inline BOFs, Sandcat,
rsshand Pyramid loaders. - Turn off HTTP directory listing on every staging and build server.
Within 7 to 30 days
- Restrict signed
python.exeandpythonw.exewith WDAC or AppLocker on non-developer workstations. Alert on interpreter connections to ports 3001, 3232, 4321, 8888 and 18081. - Keep a formal register of sanctioned Caldera, Viper, Empire and Metasploit hosts. Put their consoles behind mutual TLS or a VPN.
- Before you auto-block any external C2 list, filter out vendor appliance banners, mail and FTP ports (21, 110, 143, 465, 587, 993, 995), scanner console certificates and dynamic ISP lines.
8. Detection Rules
The full rules are in the Detection rules tab. Together they cover wire, certificate, process and file signals.
| Rule file | What it catches |
|---|---|
odin_supershell_adaptix_caldera_metasploit.rules | Suricata 7: eight signatures for SuperShell, AdaptixC2, Caldera Sandcat, Viper, Metasploit RPC and Starkiller traffic |
sentinel_supershell_caldera_sandcat_and_bof_hunt.kql | Microsoft Sentinel and Defender XDR: contact with confirmed C2 addresses, console URIs, interpreter egress, and egress followed by in-memory activity |
sigma_sandcat_supershell_and_meterpreter_execution.yml | Sigma (3 rules): Caldera agents, SuperShell rssh callbacks, and Meterpreter or Pyramid in-memory stagers |
odin_supershell_adaptix_caldera_pyramid_implants.yar | YARA (4 rules): SuperShell, AdaptixC2, Caldera agent and PyramidC2 stager files |
How the Suricata signatures work
| SID | Looks for | Why |
|---|---|---|
| 9522001 | Outbound URI starting /supershell/ followed by login, client, shell, compile or mem | Catches use of a SuperShell web console |
| 9522002 | TLS certificate subject CN=:3232 from an external server | Catches the default SuperShell rssh listener |
| 9522003 | TLS certificate subject CN=adaptix, CN=adaptix.local or CN=adaptix-server | Catches default AdaptixC2 teamservers |
| 9522004 | Outbound POST /file/download with sandcat.go in the headers | Catches a Caldera Sandcat agent download (dual-use, policy alert) |
| 9522005 | Outbound POST /beacon with a body starting eyJ | Catches Sandcat Base64 JSON check-ins (dual-use, policy alert) |
| 9522006 | URI starting /api/v1/msf/ | Catches Viper workbench API use |
| 9522007 | auth.login in a request to /api/ on ports 55552, 55553, 60000 or 3790 | Catches Metasploit RPC logins |
| 9522008 | Outbound POST /api/v2/users/login | Catches Starkiller and Empire v2 operator logins (dual-use, policy alert) |
The URI and body rules need TLS inspection to see HTTPS traffic. The certificate rules work on passive perimeter monitoring. Operators who replace the default CN=:3232 or CN=adaptix certificates evade SIDs 9522002 and 9522003, so pair them with the Sentinel query.
How the other rules work
The KQL query looks back 14 days. It has three branches.
- Network. It flags devices that contact the 18 confirmed C2 addresses in the Indicators tab. It also flags console URIs such as
/supershell/and/api/v1/msf/, and script interpreters (python.exe,powershell.exe,rundll32.exe) connecting to team C2 ports. - Process. It flags command lines with both
-serverand-group, or with markers such assandcat.go,54ndc47,PythonMemoryModuleorExtenderAgent. - Network then memory. It joins a network hit with remote thread creation, memory allocation, AMSI script content or an unbacked .NET module load on the same device within 10 minutes.
An exact-hostname allowlist excludes sanctioned purple-team machines, but never hides contact with a confirmed C2 address. Treat Caldera and Starkiller hits as hunting leads.
| Sigma rule | Fires when |
|---|---|
| Caldera Sandcat and Manx execution (Windows) | A command line has -server http with -group, or names sandcat.go, 54ndc47 or manx.go |
SuperShell rssh callback (Linux) | A command line names tdragon6/supershell, /supershell/login or SSH-2.0-rssh, or an rssh client dials -d host:3232, 8888 or 18888 |
| Meterpreter and Pyramid stagers (Windows) | PowerShell decodes Base64 with VirtualAlloc, CreateThread or a named pipe; or signed Python combines a memory loader with urllib.request or http.client |
Each Sigma rule carries an exact-hostname allowlist for sanctioned lab machines.
| YARA rule | Fires when |
|---|---|
ODIN_SuperShell_RSSH_Implant_And_Console | Two SuperShell strings appear together (such as tdragon6/supershell, /supershell/login, SSH-2.0-rssh); files under 25 MB |
ODIN_AdaptixC2_Extender_And_Beacon_Config | Three of AdaptixC2, ExtenderListener, ExtenderAgent, AxScript and execute bof; files under 15 MB |
ODIN_Caldera_Sandcat_And_Manx_Agent | Three of sandcat.go, 54ndc47, /file/download, contact_http and listenP2P; files under 20 MB |
ODIN_PyramidC2_Python_InMemory_Stager | PythonMemoryModule or BG_LOAD with two of zipimport, urllib.request and VirtualAlloc; files under 5 MB |
MITRE ATT&CK mapping
| Technique | How these tools use it | Detection |
|---|---|---|
| T1071.001 Application Layer Protocol: Web Protocols | Sandcat HTTP beacons, Viper and Starkiller REST APIs | SIDs 9522004 to 9522008; Sigma Caldera rule |
| T1572 Protocol Tunneling | SuperShell reverse SSH over TLS with SOCKS5 pivots | SID 9522002; Sigma rssh rule |
| T1055 Process Injection | Inline BOFs, Meterpreter stagers and shellcode injection | KQL network-then-memory branch; Sigma stager rule |
| T1059.006 Command and Scripting Interpreter: Python | PyramidC2 in-memory loading through signed Python | Sigma stager rule; YARA PyramidC2 rule |
9. Indicators
The Indicators tab holds 18 published indicators: 18 confirmed C2 addresses to block. The 2 JARM values appear in this report only, for TLS hunting. The JARM values belong to suspected and candidate nodes and are not block indicators. The seven addresses of the German business-ISP cluster, six watchlist entries and all file hashes are withheld.
| Type | Count |
|---|---|
| Confirmed C2 addresses in the Indicators tab (block) | 18 |
| Confirmed addresses withheld (German business-ISP cluster) | 7 |
| JARM values for TLS hunting only (not block indicators) | 2 |
| Watchlist entries (addresses withheld) | 6 |
| File hashes (SHA-256) | 0 published; 8 withheld |
The six withheld watchlist entries are the exposed Metasploit directory, the dual-use Caldera server, a default AdaptixC2 teamserver, the co-hosted AdaptixC2 and ToShellC2 server, a SuperShell candidate with CN=:3232, and the dual-port TuoniC2 server. The eight SHA-256 values come from stock Metasploit files on the unattributed server, so they are withheld.
Confirmed C2 addresses
| Endpoint | Framework | Hosting (country) | Key fingerprint | Seen |
|---|---|---|---|---|
| 111.229.193[.]40:8888 | SuperShell | Shenzhen Tencent (CN) | SuperShell web console | 13 Nov 2026 |
| 103.115.57[.]95:8888 | SuperShell | Cloudie Limited (HK) | SuperShell web console | 13 Nov 2026 |
| 206.119.189[.]208:8081 | ToShellC2 | SonderCloud (US) | Shell console on 8081 | 13 Nov 2026 |
| 186.244.231[.]115:8080 | ToShellC2 | CLOUDVALLEY (US) | Also 80 | 13 Nov 2026 |
| 186.244.215[.]55:443 | ToShellC2 | Uscloud Inc (US) | CN=fileserver, JARM 3fd3fd0003fd3fd00043d43d00043d3bef2bf79cd6719851e8198c1e8f9a14 | 13 Nov 2026 |
| 45.192.109[.]17:80 | ToShellC2 | cognetcloud INC (HK) | HTTP console | 13 Nov 2026 |
| 8.138.248[.]246:8081 | ToShellC2 | Alibaba Cloud (CN) | Listener on 8081 | 13 Nov 2026 |
| 185.207.154[.]238:8443 | ToShellC2 | Cloudie Limited (HK) | Also 8081; same JARM as above | 13 Nov 2026 |
| 83.229.120[.]101:8081 | ToShellC2 | LUCIDACLOUD (HK) | Listener on 8081 | 13 Nov 2026 |
| 43.160.243[.]229:443 | ToShellC2 | Shenzhen Tencent (SG) | TLS listener | 13 Nov 2026 |
| 181.215.18[.]135:8443 | Meterpreter | Datacamp (HK) | Reverse-HTTPS handler, JARM 07d19d12d21d21d07c42d43d000000f50d155305214cf247147c43c0f1a823 | 13 Nov 2026 |
| 65.38.121[.]42:3389 | Meterpreter | BL Networks (RO) | CN=6a47718162def1c on the RDP port, JARM 14d14d16d14d14d08c14d14d14d14dfd9c9d14e4f4f67f94f0359f8b28f532 | 13 Nov 2026 |
| 190.2.184[.]47:4444 | Meterpreter | MASTER DA WEB (BR) | Default handler port | 14 Nov 2026 |
| 8.148.31[.]135:4446 | Meterpreter | Alibaba Cloud (CN) | TCP handler | 13 Nov 2026 |
| 154.89.152[.]104:10003 | Meterpreter | CLOUDVALLEY (HK) | High-port handler | 13 Nov 2026 |
| 77.83.36[.]163:3001 | Metasploit | Layer7 Networks (SC) | Team listener | 14 Nov 2026 |
| 185.254.199[.]160:3001 | Metasploit | SOLLUTIUM EU (NL) | Team listener | 13 Nov 2026 |
| 77.91.71[.]99:3001 | Metasploit | Hosting network (IL) | Team listener | 13 Nov 2026 |
The seven-address German cluster (14 endpoints, each address on 443 and 80) sits on a business ISP and shares one third-party company certificate. That pattern also fits an authorized testing firm or lab, so its addresses are withheld. With it and the second ports on 186.244.231[.]115 and 185.207.154[.]238, the table above accounts for all 34 confirmed endpoints.
JARM values for hunting
| JARM | Framework | Use |
|---|---|---|
29d29d00000000000043d43d00043dc3b2afa8a5ec09b510a8559aff7899fb | AdaptixC2 | Go teamserver TLS fingerprint on 21 listeners; hunt, do not block alone |
3fd3fd20d3fd3fd00043d3fd3fd43d5ecfbe778b06e32b538bd51f24eb7398 | SuperShell | Default rssh TLS fingerprint, seen with CN=:3232 on candidate consoles in China; hunt, do not block alone |
Supporting fingerprints: the certificate subjects CN=:3232, CN=adaptix, CN=adaptix.local, CN=adaptix-server, CN=fileserver and CN=6a47718162def1c.
10. Scope and Limits
- Window. The findings cover a two-week observation window ending 18 November 2026. Some records carry earlier first-seen dates from public sources; we do not treat those as a tracking start.
- Server side only. These observations show what runs on attacker-side servers. They do not show which targets were reached or what happened on them.
- Confirmed is a high bar. Only 34 of 718 endpoints are confirmed, and 18 of their addresses are published. One confirmed cluster is withheld because it may belong to an authorized tester. Suspected and candidate endpoints are leads, not block entries.
- Dual-use tools. Caldera, Starkiller, Empire, Metasploit and Viper are used legitimately by red and purple teams. A listener alone does not prove hostile intent.
- The workflow model is a model. The three-workflow grouping in Figure 1 and the six-step sequence in Figure 3 are analytical. Nothing here links the frameworks to one actor.
- The exposed directory. The Metasploit tree shows a full installation. It does not show who ran it or whether it was used against anyone.
- Rule testing. Every published rule file loads without errors in its engine (Suricata 7.0.12, YARA-X, pySigma and Microsoft's Kusto.Language analyzer, checked on 20 November 2026). The rules were not replayed against live traffic, so test and tune them in your own environment before production use.
11. Sources
- tdragon6. SuperShell repository. https://github.com/tdragon6/Supershell (verified 20 November 2026)
- Adaptix-Framework. AdaptixC2 repository. https://github.com/Adaptix-Framework/AdaptixC2 (verified 20 November 2026)
- MITRE Caldera documentation, plugin library (Sandcat and Manx agents). https://caldera.readthedocs.io/en/latest/Plugin-library.html (verified 20 November 2026)
- FunnyWolf. Viper repository. https://github.com/FunnyWolf/Viper (verified 20 November 2026)
- Rapid7. Metasploit documentation. https://docs.rapid7.com/metasploit/ (verified 20 November 2026)
- shell-dot. Tuoni repository. https://github.com/shell-dot/tuoni (verified 20 November 2026)
- naksyn. Pyramid repository. https://github.com/naksyn/Pyramid (verified 20 November 2026)
- MITRE ATT&CK. Empire, S0363. https://attack.mitre.org/software/S0363/ (verified 20 November 2026)
What is…?
Short explanations of the tools and families named in this study.
What is Metasploit?
Metasploit is an open-source penetration testing framework maintained by Rapid7. It bundles exploits, payloads and the Meterpreter post-exploitation agent.
More about MetasploitAdversary emulationWhat is Caldera?
Caldera is MITRE's open-source adversary emulation platform. It plans and runs ATT&CK techniques through agents such as Sandcat.
More about CalderaC2 frameworkWhat is SuperShell?
SuperShell is a web-based C2 platform, usually deployed with Docker, that builds reverse-SSH implants for Windows and Linux and manages them from a browser.
More about SuperShellC2 frameworkWhat is AdaptixC2?
AdaptixC2 is an open-source, extensible post-exploitation and adversary emulation framework with a multi-operator client.
More about AdaptixC2Adversary emulationWhat is Starkiller?
Starkiller is the web interface for the PowerShell Empire post-exploitation framework.
More about StarkillerOffensive frameworkWhat is Viper?
Viper is an open-source browser front end for Metasploit. It adds a multi-operator web interface and a module runner on top of the Metasploit RPC service.
More about ViperFrequently asked questions
What are team C2 platforms?
Older attack setups were a single listener in a terminal. Team C2 platforms package everything in a Docker stack instead: reverse shells, payload builders, a task database and a web or desktop console. Several operators log in and work side by side.
Which servers are confirmed attack infrastructure?
All 34 confirmed endpoints are browser shell consoles. They sit on 25 addresses. Viper, a browser workbench for Metasploit, wraps Metasploit's RPC service in a shared web interface. SuperShell also shows how much of a raw list is noise. Of its 180 endpoints, 169 sit in one Hong Kong hosting cluster. They share TLS fingerprints, but nothing else ties them to SuperShell, so they stay suspected.
Why not block every listener?
Because many of them are not attack servers. MITRE Caldera is the clearest example. It shows 257 endpoints, but 239 of them are banner look-alikes on a security vendor's own address space. Of the remaining 18 cloud servers, any could be a sanctioned purple-team lab, because purple teams run the same Caldera agents as attackers.
What makes the newer frameworks hard to see?
They move the work into memory. AdaptixC2 runs on 101 endpoints, 35 of them on its default port 4321. It loads listener and agent plugins on demand and runs small compiled modules, called Beacon Object Files, inside an existing process. Nothing new lands on disk.
How can defenders spot them?
Many operators never change the defaults. SuperShell's reverse-SSH listener presents a self-signed certificate named CN=:3232. AdaptixC2 servers often present CN=adaptix or CN=localhost, and 21 of them share one TLS fingerprint. Caldera agents download themselves from a /file/download path and check in on /beacon. Starkiller operators log in on /api/v2/users/login.