
fraud monitoring. Tagged Articles.
120 articles tagged fraud monitoring.
 APT Groups
Hazy Tiger: An Emerging Espionage Threat in South Asia
Hazy Tiger is a South Asia-linked APT group active since 2013, targeting government, defense, and energy sectors through sophisticated espionage campaigns involving phishing, malware, and custom…
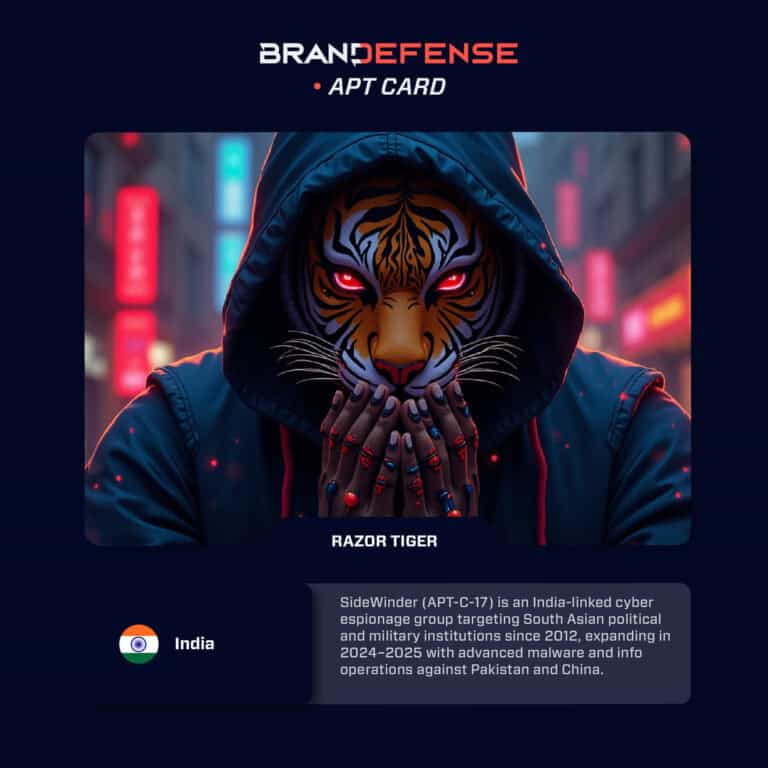 APT Groups
RAZOR TIGER: The Persistent South Asian Espionage Threat
Razor Tiger (APT-C-17), also known as SideWinder, is a long-standing India-linked APT group active since 2012. Its evolving espionage campaigns now target South Asian governments, defense,…
 APT Groups
UNC4841 / SLIME57: China-Linked Espionage Threat Expanding Global Operations
UNC4841, also known as SLIME57, is a China-linked APT group active since 2021, conducting cyber-espionage across government, defense, and tech sectors. Exploiting zero-day vulnerabilities and maintaining…
 APT Groups
Ghostwriter: Hybrid Influence and Espionage Operations in Eastern Europe
Ghostwriter, a Belarus/Russia-linked APT active since 2016, executes hybrid campaigns combining espionage, phishing, and disinformation against NATO and EU entities. Learn how these operations evolved into…
 APT Groups
GhostEmperor: Advanced China-Linked Espionage Campaigns
GhostEmperor is a China-linked APT active since 2019, leveraging stealthy rootkits like Demodex to conduct espionage across Asia, the Middle East, and Africa. Known for its…
 APT Groups
Earth Estries – Threat Actor Sheet
Earth Estries is a China-linked APT group active since the early 2020s, known for espionage campaigns targeting global governments, research institutions, and critical infrastructure. By 2025,…
 Blog
APT32 Targeting NGOs: A Perspective
APT32 (OceanLotus), a Vietnam-linked APT group, has intensified its cyber-espionage operations in 2025, targeting NGOs and cybersecurity professionals through sophisticated supply-chain tactics, stealthy persistence methods, and…
 Blog
Telegram Leaks and Dark Channels: How Criminals Use Telegram
How criminals share stolen data through Telegram channels and bots, what monitored groups show, and what to do about it.
 Blog
Top 10 Most Significant Data Breaches Publicly Listed on the Dark Web, 2023 to 2025
The 10 most significant data breaches listed on the dark web over the last two years, from Snowflake and MOVEit to Qantas, and the lessons each…
 Blog
Leaked Credentials from Ransomware Groups: Case Insights
Stolen credentials have become the new gateway for ransomware. This in-depth analysis explores how leaked identities circulate through dark web markets, empowering RaaS affiliates and bypassing…
 Blog
APT Groups in the MENA Region: Key Threat Actors in Cyber Espionage
The MENA region remains a hotbed for state-sponsored APT activities. This article explores key actors like MuddyWater, OilRig, APT33, and SideWinder, revealing how geopolitical conflicts shape…
 APT Groups
The Lazarus Group: Espionage, Sabotage, and Cybercrime Under One Umbrella
The Lazarus Group — a North Korea–linked APT — has executed some of the most disruptive cyberattacks in modern history. From Sony Pictures to billion-dollar crypto…
About The Blog.
Last updated June 9, 2026-
Articles on ransomware, APT groups, the dark web, digital risk protection, fraud, sector analysis and VIP security, written for security teams.
-
New articles are added several times a month. The newest come first, and every article shows its publish date.
-
Use the topic chips above the list to open one topic, or type a word in the search box. Each topic has its own page.
-
Articles draw on public sources such as CISA advisories, MITRE ATT&CK and ENISA reports. Sources are listed at the end of an article when it cites them.
-
The site feed at brandefense.io/feed/ lists new posts. The email sign-up box is on the All Resources and Reports pages.
-
Brandefense is an AI-driven threat intelligence company. Its platform covers cyber threat intelligence, digital risk protection and external attack surface management. You can request a demo on your own domain from the Request A Demo page.
-
The blog page shows 470 articles. You can open all of them or pick one topic, such as APT Groups, Dark Web, Ransomware or Fraud. Each article shows its publish date.
-
The blog describes its articles as explained by the analysts who track threats. They cover threat actors, dark web activity, ransomware and digital risk. The newest articles appear first.
-
Yes. APT Groups is one of the topic chips above the list, and it opens only the articles on that topic. The Knowledge Hub also holds profiles of threat groups.
-
The surface web is the part of the internet that search engines list. The deep web is content that search engines do not list, such as pages behind a login. The dark web needs special software to reach. The blog has an article that explains the three layers in plain words.