
Account Buyer Rate Sheets: What They Ask Suppliers For
Account buyer rate sheets treat a 2FA secret, a cookie and friend count as deliverables. Same-sheet pairs show which of them moves the stated rate.
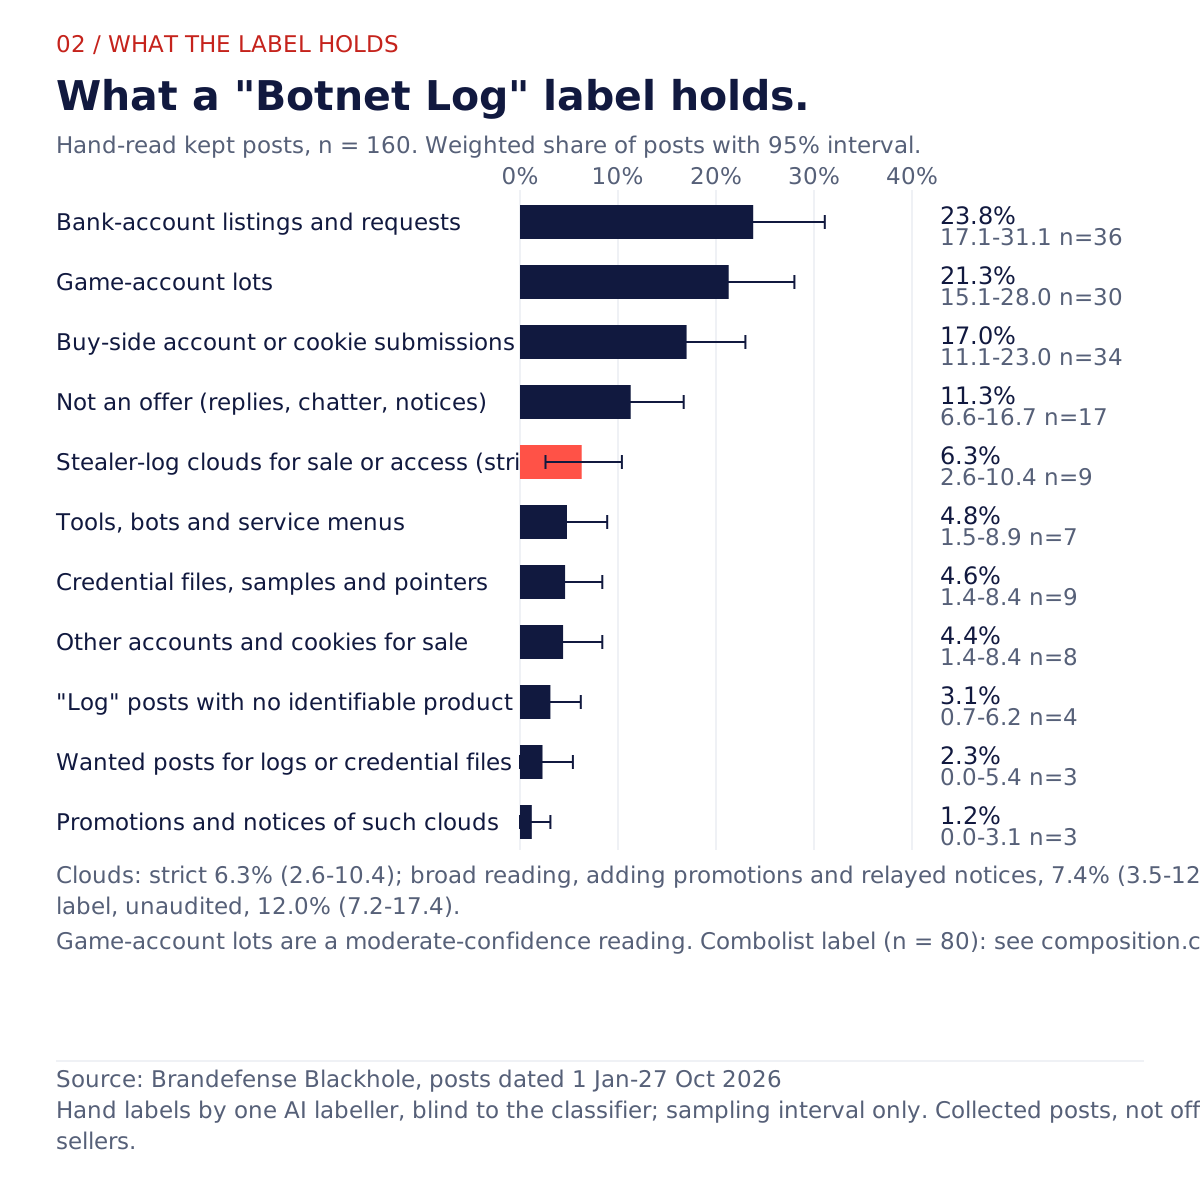
Read the investigation →We hand-read 160 Botnet Log posts and 80 Combolist posts. The labels do not name one product: under Botnet Log, bank-account listings (23.8%) and game-account lots (21.3%) outnumber strict stealer-log clouds (6.3%), all weighted estimates. Counts are collected posts in a Telegram-dominated collection, not offers, sellers, victims or a market total.
Each finding below is stated in its own unit, with the limit that comes with it. The investigations give the full reasoning and the evidence records.
Hand-read kept posts, n = 160. Weighted share of posts with 95% interval.
| Post type | Weighted share | 95% interval | Posts labelled |
|---|---|---|---|
| Bank-account listings and requests | 23.8% | 17.1–31.1% | 36 |
| Game-account lots | 21.3% | 15.1–28.0% | 30 |
| Buy-side account or cookie submissions | 17.0% | 11.1–23.0% | 34 |
| Not an offer (replies, chatter, notices) | 11.3% | 6.6–16.7% | 17 |
| Stealer-log clouds for sale or access (strict) | 6.3% | 2.6–10.4% | 9 |
| Tools, bots and service menus | 4.8% | 1.5–8.9% | 7 |
| Credential files, samples and pointers | 4.6% | 1.4–8.4% | 9 |
| Other accounts and cookies for sale | 4.4% | 1.4–8.4% | 8 |
| "Log" posts with no identifiable product | 3.1% | 0.7–6.2% | 4 |
| Wanted posts for logs or credential files | 2.3% | 0.0–5.4% | 3 |
| Promotions and notices of such clouds | 1.2% | 0.0–3.1% | 3 |
Each investigation answers a different question from the same collected posts. Start with the main one, then follow the question that matters to your team.
What "Botnet Log" and "Combolist" Posts Actually Sell
Hand-read Botnet Log and Combolist posts hold bank listings, game lots, rate sheets and subscriptions. Strict stealer-log clouds are 6.3% of Botnet Log, a weighted estimate.
Read the investigation →Account buyer rate sheets treat a 2FA secret, a cookie and friend count as deliverables. Same-sheet pairs show which of them moves the stated rate.
Read the investigation →Credential lists are advertised as time-limited plans, and in 144 of 174 eligible ladder segments the daily cost falls at every step. The adverts do not show what is delivered.
Read the investigation →Reposted Combolist texts say fresh, private and valid about twice as often as texts not seen twice. The words track advert copying, not exposure.
Read the investigation →Compare hosted services, worker accounts, access transfer and account-data requests in our cross-chapter analysis.
Explore the work and control analysis ↗These are implications of what the posts say, not measured control results. Each one points to a different decision.
Ask which product a "botnet log" mention is before you act: bank listings go to fraud, session and cookie material to identity operations, strict stealer clouds to endpoint response.
For a combolist mention, match your own domains and users once per distinct file, reset passwords and revoke sessions on a match. Claim words such as fresh, private and valid trigger nothing.
These advertised prices do not establish a risk ranking: denomination and product comparability across posts are not established. A subscription advert does not show what is delivered, so act on a verified match of your own accounts.
Watch enrolment and session behaviour: buyer rate sheets ask for 2FA-secret and cookie columns, which fits supplier-enrolled accounts better than accounts handed over as found.
See when your company's passwords, data or name show up on criminal forums and markets.
See how it works →Free exposure check. Enter your company domain and see what is visible from the outside, in about 30 seconds.
160 kept (cleaned) Blackhole posts carrying the Botnet Log class label, 1 Jan-27 Oct 2026, drawn with stratum weights (set x quarter). We labelled them from full text, blind to our classifier. Strict stealer-log clouds are priced or joinable feeds and log packs said to come from infected machines.
Weighted estimate: 6.3% (95% interval 2.6-10.4); 7.4% with unpriced promotions. Unweighted, 9 of the 160 posts (5.6%). The same sample holds bank-account listings and requests 23.8% (17.1-31.1), game-account lots 21.3% (15.1-28.0) and buy-side rate sheets 17.0% (11.1-23.0).
Read the report, open the evidence records and reuse the charts with their source and limits.
Original aggregate tables, charts and editorial paraphrases: CC BY 4.0. Keep the source, version, date range and measurement limits with reused figures.
30 October 2026 · Brandefense Research Team · Brandefense Blackhole data · Prepared by Claude Opus 5.5, checked by Codex Astra and approved by Brandefense analysts.
The Cybercrime Report 2026 reads eight kinds of activity in the same collection. Each chapter counts its own unit, so compare their limits before you compare their numbers.