
The affiliate gets the larger share.
Six programme ads state or imply a split. Entry charges, proof and deposits add conditions to the headline offer.
Read the partner terms →Ransomware has a public claim trail and an advertised service economy. We read the crews’ own ads beside 9,203 leak-site claims collected by Brandefense Blackhole, our cybercrime database.
177 groups appear in the collection. Qilin and The Gentlemen alone account for 23.4% of its claims. A changing list of names does not mean activity is evenly distributed.
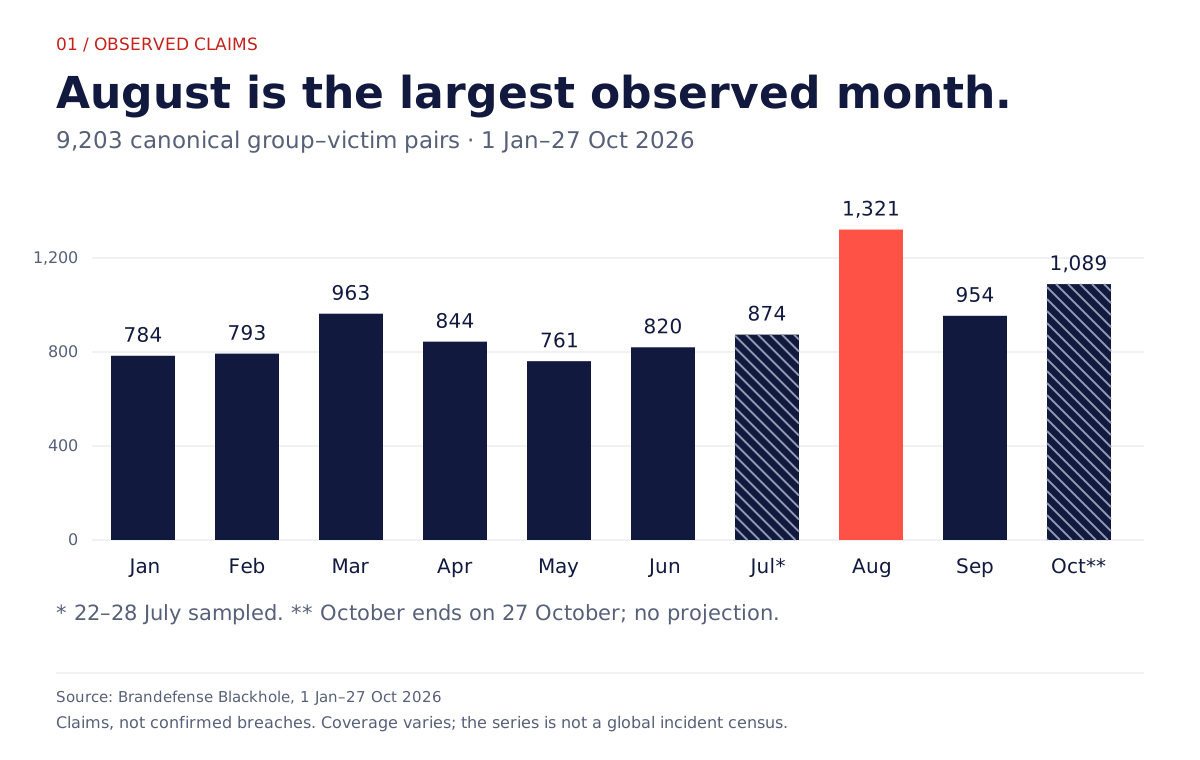
January–July range: 761–963 claims. August: 1,321. The series measures the collected relay posts; it is not a global incident trend.
| Month (2026) | Claims | Active groups | Note |
|---|---|---|---|
| Jan | 784 | 58 | |
| Feb | 793 | 60 | |
| Mar | 963 | 62 | |
| Apr | 844 | 60 | |
| May | 761 | 63 | |
| Jun | 820 | 69 | |
| Jul | 874 | 66 | sampled week |
| Aug | 1,321 | 92 | |
| Sep | 954 | 85 | |
| Oct | 1,089 | 85 | partial month |
The posts describe recruitment, tools, negotiation and publication as separate services. These are seller statements from selected posts, not verified purchases or estimates of the whole market.
The underground review uses 60 retained catalogue items from a keyword-led selection; some items combine multiple posts or threads.
Six programme ads state or imply a split. Entry charges, proof and deposits add conditions to the headline offer.
Read the partner terms →A hosted portal was offered for $100 setup and $30 a month. Other selected descriptions assign talks to the affiliate or crew staff.
Examine negotiation services →Six dated listings across 59 days change the builder package and access terms. Two June source-code offers name USD; other dollar denominations stay unspecified. These are asking prices, not verified sales.
Explore the builder offers →Five dated EDR-killer offers distinguish per-build pricing, custom work and limited access rights. Different products and unnamed dollar denominations do not form a common price range.
Compare the advertised terms →Vect promised an affiliate key to every forum member. The Gentlemen invited teams and access brokers as an official forum partner; neither announcement proves new intrusions.
Read the forum evidence →Selected catalogue descriptions distinguish unpriced publication, later reposting and sale offers. Composite catalogue items are not independently verified cases and cannot predict payment outcomes.
Compare the data routes →Read each profile alongside its observed claim count. These seven were selected for the research; they are not a ranking of all 177 groups.
Our interpretation follows the evidence. It does not promise a fixed warning window or establish when a compromise began.
Preserve the observation time, validate it against internal evidence, and involve incident response. Multiple relays can repeat the same allegation.
Prioritise relevant group activity, advertised access requirements and negotiation patterns. Keep observed activity separate from a seller’s claimed capability.
Pair vulnerability and exploitation notices with exposure checks and response ownership. A public advisory and a relayed claim need an event-level join before their dates can define an incident interval.
See when your company's passwords, data or name show up on criminal forums and markets.
See how it works →Free exposure check. Enter your company domain and see what is visible from the outside, in about 30 seconds.
One canonical group–victim pair, assigned to its first UTC appearance in the collected relay posts. Aliases are merged before de-duplication. We removed 171 duplicate pairs and excluded 190 claims attributed to 0APT.
Victim names, contact handles and illicit service links are omitted.
Original aggregate data and chart assets: CC BY 4.0. Retain the source, period and limitations when reusing them.
31 October 2026 · Brandefense Research Team · Brandefense Blackhole data · Prepared by Claude Opus 5.5, checked by Codex Astra and approved by Brandefense analysts.
The Cybercrime Report 2026 reads eight kinds of activity in the same collection. Each chapter counts its own unit, so compare their limits before you compare their numbers.