VanHelsing is a ransomware-as-a-service (RaaS) group whose malware targets Windows (x86 and ARM), Linux and VMware ESXi systems. Affiliates run their own intrusions, then encrypt files and steal data to pressure victims, a model known as double extortion. This profile covers its platforms, how affiliates operate and how to defend against it.
Over the last several years, the ransomware setting has kept changing. It has grown into a new ecosystem with more modular, subscription-based operations and market-based systems. These new RaaS groups mirror a traditional software developer. They have introduced business models with customer service, product updates and affiliate partnerships, among other things. The VanHelsing RaaS group has become one of the most prominent RaaS actors, both for its technical features and for its business model. It gained notoriety in a short time, and it grew from a very unusual and hard background. This blog gives a complete, original analysis of the VanHelsing RaaS Group’s rationale, methods, development and outlook through 2025.
What is the VanHelsing ransomware group?
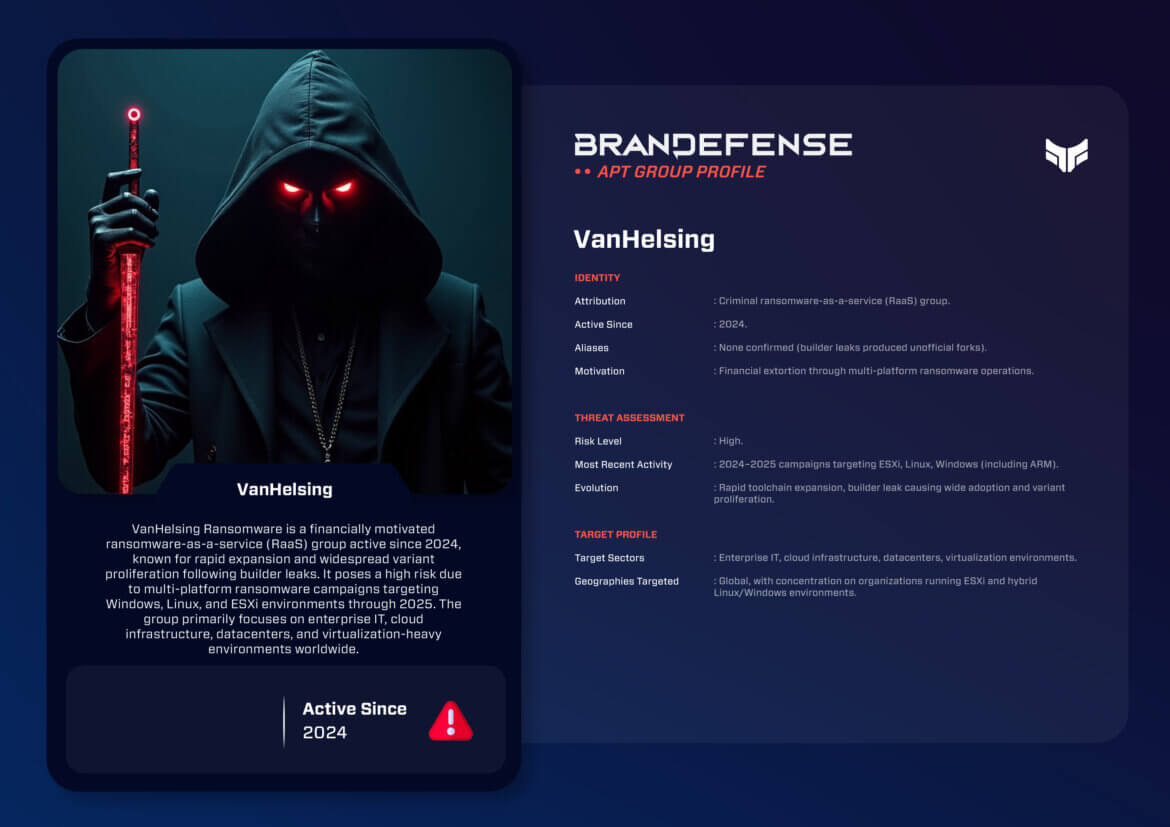
VanHelsing is a RaaS (Ransomware-as-a-Service) that was at first released with little to no info, but soon gained a lot of attention with its unique features. Many RaaS strains are developed for a single OS. VanHelsing is different. It has been written from the ground up to be compatible with Windows (x86 and ARM), Linux and VMware’s ESXi. This means that affiliates who use VanHelsing can possibly penetrate many different types of enterprise environments. This is especially true in virtualized datacenter settings, where ESXi deployments are very common.
The release of this ransomware did not happen in silence. VanHelsing quickly gained large attention soon after being released on the underground forums. The ransomware builder was also published, allegedly by an unhappy developer. This event greatly expanded the reach of VanHelsing. A much wider array of people could now create and deploy their own variation of the ransomware, even those with little knowledge or experience with ransomware attacks.
In contrast to existing ransomware families, VanHelsing shows an advanced level of engineering skill. This suggests that its engineering was influenced by, or developed in tandem with, a more advanced criminal grouping. It does not look like the result of growth from early amateur threat actors.
Identity & Motivation
Van Helsing is another criminal RaaS collective. Its motivations are similar to those of other financially motivated ransomware operations: speed to monetization, the ability to target on a global scale, and the ability to create maximum disruption. The developers behind Van Helsing have a keen focus on monetizing their affiliate relationships to generate revenue from ransom payments. They also have a well-defined set of characteristics that make up the Van Helsing operator. These include:
* Strong interest in targeting enterprise virtualization environments
* Major technical investment in ARM-native payloads
* Commercially oriented ambitions, such as selling access to and/or tools for use by other criminals
* Flexibility in giving support to affiliates, including customization and operational guidance
The leak of the builder is an odd and highly damaging incident for the Van Helsing operator. It suggests that either there are internal conflicts among the team, poor operational security or personal disputes within the developer team. Regardless, the leak has accelerated the proliferation of the malware to a wider network of cybercriminals.
- Model.
- Ransomware-as-a-Service (RaaS).
- Platforms.
- Windows x86, Windows ARM, Linux, VMware ESXi.
- Extortion.
- Double: encrypt systems and steal data.
- Intrusions.
- Run by affiliates, not the operators.
- Builder.
- Said to have been leaked by a former developer.

How does VanHelsing operate?
The multi-platform architecture of VanHelsing gives it the ability to use different types of intrusion workflows that affiliates can create.
1. Initial Access: Affiliate‑Driven Approaches
Because VanHelsing is a RaaS, the creators do not usually conduct intrusions directly. Rather, affiliates take the initiative to deploy their own access method(s), many of which will consist of:
– Credential theft/brute forcing – mainly done against VMware ESXi interfaces
– exploiting RDP, VPN, SSH, but with remote access services
– using public vulnerabilities in virtual management systems
– buying initial access from brokers on cybercrime forums.
This broad compatibility of architecture allows affiliates to deploy VanHelsing in a large number of infrastructures, using the compromise methods that work best for them.
2. Lateral Movement and Deployment
Once inside the target system, affiliates often move laterally with:
– RDP pivoting
– expanding via SSH from host to host across the entire Linux environment
– performing shell operations on ESXi servers to target the virtual machines
– and credential replaying for access to hypervisors.
The malware can execute either manually or automatically, allowing for rapid deployment of a large number of targets simultaneously.
3. Ransomware Behavior and Encryption Logic
VanHelsing has adopted modern ransomware methods of encryption:
– Using asymmetric encryption for file encryption
– Optimizing virtual machine disk file encryption routines
– Running many threads across platform variants, giving fast multi-threaded processing and giving easy access
– Specifically targeting the deletion of shadow copies and backup snapshots.
The unique Windows payload for ARM is noteworthy, as the use of ARM based laptops and servers is expected to grow steadily in many sectors.
4. Extortion & Communication
VanHelsing has used a familiar double-extortion model:
– Encrypting systems of the victim
– Exfiltrating sensitive data from the victim
– Bringing pressure on the victim through the use of leak sites and negotiation portals
Affiliates receive access to dedicated negotiation platforms, and some versions of the ransomware include automated scripts for the communication with the victims.
- Initial accessStolen credentials, exposed remote services, unpatched systems or bought access.
- Lateral movementRDP, SSH and ESXi shell used to reach more hosts.
- EncryptionFiles and virtual machine disks are encrypted.Technique T1486 (MITRE ATT&CK, opens in a new tab)
- ExtortionStolen data and leak sites are used to press for payment.
Notable Operations: A Brief Timeline
VanHelsing is still developing, but its short history already holds many major developments.
2025 – First Government Reporting
A May 2025 advisory from the UAE Cyber Security Council describes VanHelsing as a new ransomware strain. It says the group’s leak site listed seven victims as of April 2025, mainly in manufacturing and municipal government. Public sources do not confirm an earlier start or a date for the builder leak mentioned later in this post.
2025 – Increased Operational Activity
In 2025, threat analysts began to notice an increase in the use of VanHelsing amongst cybercriminals. Indicators of this increase in usage include:
1. More advanced versions being offered by affiliates
2. A major increase in attacks targeting ESXi and Linux servers (this correlates with the increased skill of the ransomware); and
3. Increased acceptance amongst access brokers and affiliates with intermediate-level technical competence.
Security advisories indicate the malware has been further improved through obfuscation, added runtime compatibility, added reliability when used in large virtualized environments.
Technical Change: How VanHelsing Continues to Refine Its Arsenal
The change of Van Helsing’s ransomware reflects quick development iteration cycles. It also reflects an ongoing willingness of the group to listen to its affiliates. It takes their suggestions into account when developing future iterations.
Platform Expansion
Van Helsing provides support for:
– Windows x86
– Windows ARM
– Linux Server
– VMware ESX Platforms.
Modular configuration files that allow for customization by affiliates; Improved logging suppression to help keep stealth mode.
Engineering Improvements
Up through the most recent release, several improvements were added to:
– Offer better fail safes, preventing the corruption of key system files as a result of ransomware attacks
– Add/improve encryption logic that is aware of Virtual Machine existence
– Allow for the development of affiliate-customizable configurable files using a modular architecture
– Decrease logging activity to provide improved stealth of the operation of the system.
Leak‑Driven Fragmentation
As a result of the leaked versions of the ransomware, affiliates began modifying the leaked build to suit their specific needs. Some of the incentives for these changes have resulted in both stable forks and more fully-featured improved versions. They have also led to a more diverse operator skill base.
Due to these divergencies, the number of circulating versions makes it hard to capture every circulating version with just one signature.
Why does VanHelsing matter in 2025?
Ransomware as a Service no longer relies solely on a small handful of major criminals operating as a syndicate. It has begun developing rapidly, using many technical methods to create new, agile ransomware platforms such as VanHelsing. This has occurred due to:
- Widespread availability of leaked technical tools that help misuse and promote the rapid development of ransomware
- Using these technical tools as a means for quick acceptance and on-boarding of potential affiliates who may lack operational discipline
- Finding of enterprise infrastructure vulnerabilities, which often result in much larger attack surfaces
- The unique ability of VanHelsing to connect highly-technical skilled advanced actors with lower-technical skilled (inexperienced) users.
The focus of VanHelsing on many platforms also reflects the shifting market of ransomware attack methods. It goes beyond Windows-based (OS-specific) systems. This points to more possible attack surfaces as hybrid systems become more common.
How can companies defend against VanHelsing?
Companies can help reduce possible damage from campaigns run by VanHelsing by:
- Using more controls over Shell access and multi-factor authentication for ESXi
- Isolating virtualization infrastructures through segmentation to limit potential blast radii
- Watch for suspicious ARM executable activity in their Windows environments
- Promptly apply patches to their hypervisor and remote-access vulnerabilities
- Limit access to credentials and service accounts to only required access
In addition, being proactive through network monitoring remains key. Companies also need to be ready to respond if an affiliate gains access to their environment. This minimizes damage in the event that VanHelsing affiliates get initial access.
Conclusion
The VanHelsing threat is an example of how the malware ecosystem evolves. It incorporates developed processes into a true multi-platform, commercial nature. Recent hardware/software leak(s) have made it available to an increasing number of people. VanHelsing has found more options for using Windows ARM, Linux and ESXi. This indicates that threat actors who use these platforms in their cybercriminal operations need to change their attack methods. Modern-day firms often depend on different types of platforms or architectures.
If these affiliates keep using VanHelsing the way they do now, its operational footprint will most likely grow during 2025. Learning about the features and techniques of VanHelsing and the RaaS (Ransomware as a Service) ecosystem helps defenders. They will be better equipped to face the next wave of cybercriminal attacks made possible by RaaS.
You can download and review the sheet for all the details!